Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 27 of 187

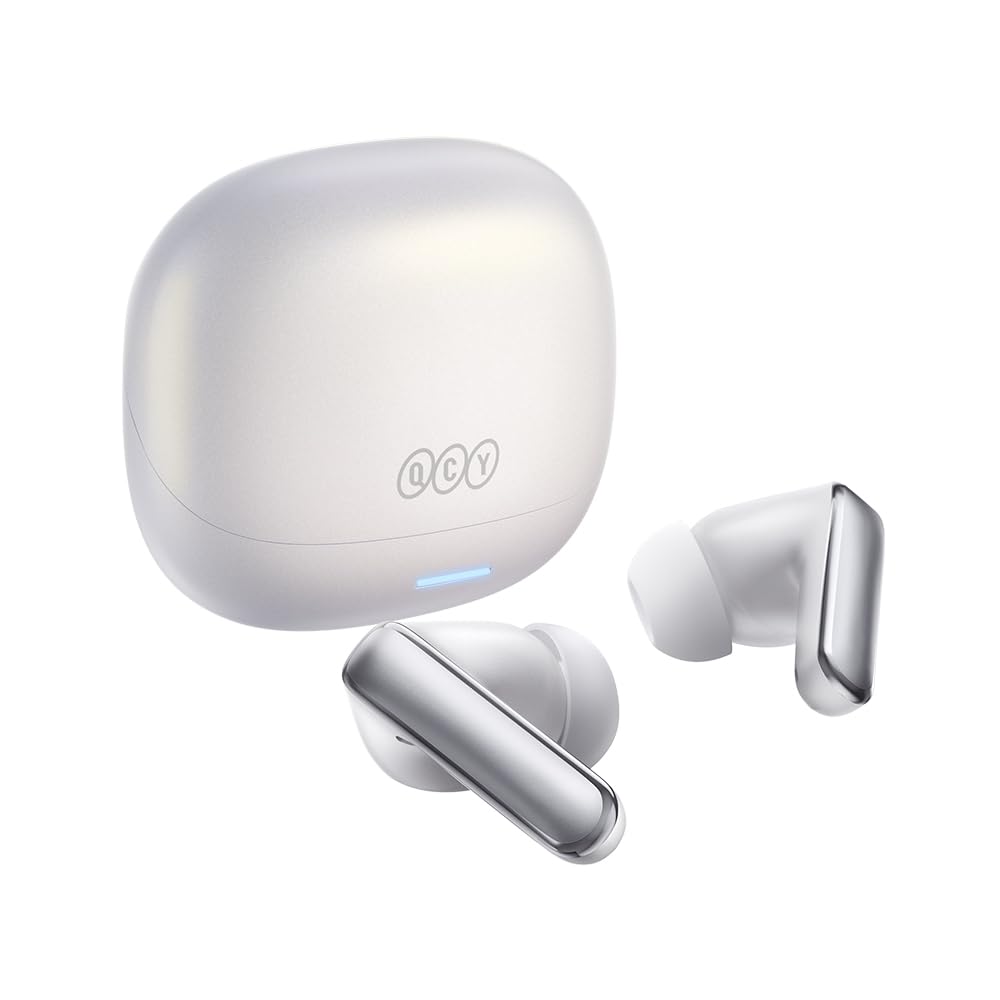
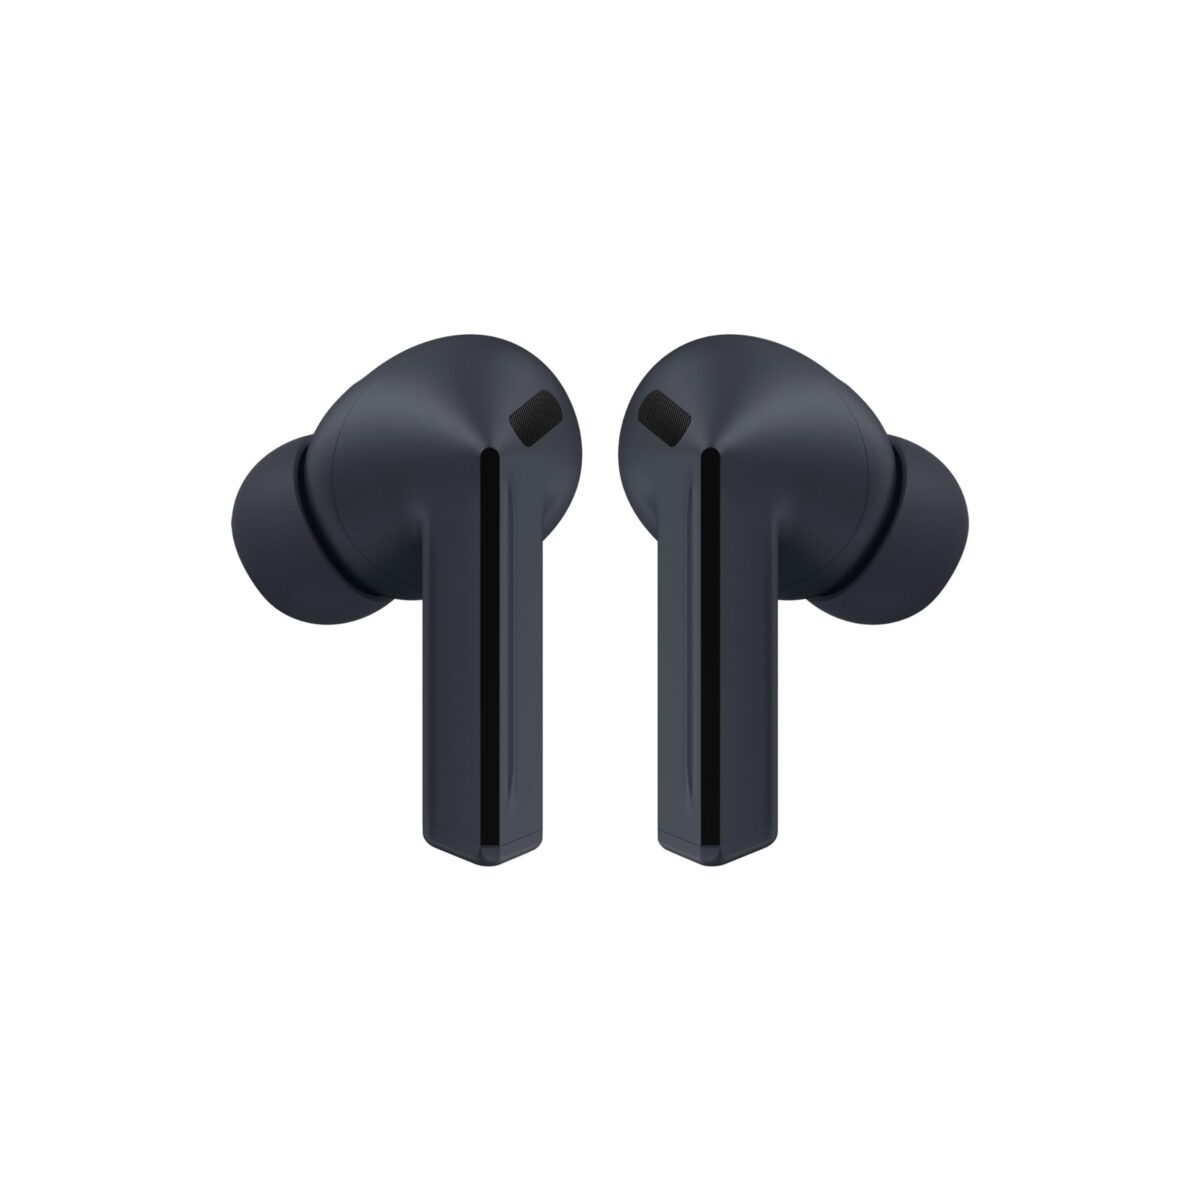
QCY MeloBuds N65 Wireless Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

QCY MeloBuds N65 Wireless Earbuds, AI Adaptive Noise Cancelling, 60dB ANC Ear Buds Hi-Res Sound, 50H Playtime, Spatial Sound, Triple Device Connection, IPX5 Waterproof

AWS clients astonished by exorbitant invoice projections


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

AWS Users Amazed by Surprising Bill Projections

Quick Read

  • Amazon Web Services users encountered unexpectedly large bill projections.
  • Estimated bills soared to billions or even trillions of US dollars.
  • The problem impacted AWS users globally.
  • A unit pricing glitch in the billing system was pinpointed as the culprit.
  • AWS made several attempts to rectify the situation but encountered obstacles.
  • Most accounts were adjusted by July 18 at 11pm Australian time.

Colossal Billing Projections Astonish AWS Users

Users of Amazon Web Services (AWS) were taken aback over the weekend when they received notifications showing outrageous bills, some estimated in the billions or even trillions of US dollars. This unforeseen error has had a global effect, resulting in widespread confusion and worry.

AWS users amazed by staggering bill projections

Worldwide Outrage Over Billing Mistakes

Numerous AWS users took to social media to post screenshots of their billing dashboards, displaying charges that greatly exceeded their typical monthly usage. Datadog staff engineer and AWS Hero AJ Stuyvenberg was one of the individuals who drew attention to these exaggerated billing projections.

AWS Discovers the Underlying Issue

AWS promptly recognized the mistake, explaining that the billed estimates did not accurately represent actual usage or charges. Engineers traced the problem back to a unit pricing error within the billing calculation subsystem. This mistake occurred after an update to the system that unintentionally triggered the inflated projections.

Actions Taken to Fix the Problem

In response, AWS halted all estimated billing calculations to avert additional increases in the erroneous figures. Engineers sought to revert to the last known accurate billing data and undo recent modifications to the calculation subsystem. However, the rollback did not rectify the problem, requiring further action.

By July 18, most of the impacted accounts were reportedly adjusted, although AWS acknowledged that the recovery process was slower than anticipated.

Previous Issues and Clarifications

Earlier this year, AWS addressed a different incident concerning Cost Explorer, which was initially reported by the Financial Times as being caused by artificial intelligence. AWS clarified that the service disruption was due to user error linked to a misconfigured role, not AI.

Summary

The unforeseen billing mistakes encountered by AWS customers underscore the complexities and possible pitfalls in cloud billing systems. AWS’s rapid response and ongoing efforts to remedy the situation highlight the significance of precise billing and effective customer communication in fostering trust.

Q&A

Q: What led to the inflated AWS billing projections?

A: A unit pricing glitch in the billing calculation subsystem was identified as the main issue.

Q: How did AWS react to the billing problem?

A: AWS suspended estimated billing calculations and tried to fix the error by reverting to previous data and undoing recent changes.

Q: Were all users impacted by the billing mistake?

A: The problem affected users globally, but AWS reported that most accounts were rectified by July 18.

Q: Has AWS experienced similar issues in the past?

A: Yes, AWS dealt with a previous incident concerning Cost Explorer, which was wrongly attributed to AI by some reports.

Q: How can users verify if their billing projections are accurate?

A: Users should regularly check their billing dashboards and reach out to AWS support if discrepancies are found.

Flight Centre Poised to Leverage AI Agents and Optimize Ecommerce


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Flight Centre’s Transformation in AI and Ecommerce

Brief Overview

  • Flight Centre has named Christopher Steiner as the chief AI officer and Rob New as the head of digital commerce.
  • AI is set to be integral in boosting online booking growth.
  • Steiner will spearhead an AI-driven productivity enhancement initiative.
  • New will integrate ecommerce platforms into a cohesive commercial framework.
  • Online bookings now represent nearly 50% of Flight Centre’s overall booking volume.

New Leadership at Flight Centre in AI and Digital Commerce

Flight Centre embracing AI agents, ecommerce unification

Flight Centre Travel Group is making impactful strides in its digital transformation by appointing Christopher Steiner as chief AI officer and Rob New as head of digital commerce. Charged with enhancing the firm’s online booking capabilities, both executives are expected to utilize artificial intelligence and digital platforms to improve customer interactions and operational efficiency.

Accelerating Growth through AI

Christopher Steiner, a seasoned veteran at Flight Centre with close to 24 years of experience, will lead a progressive “agentic accelerator program.” This initiative seeks to change Flight Centre’s global leisure operating framework into an AI-enhanced productivity powerhouse. By implementing AI agents, the organization plans to empower its workforce with better insights and quicker decision-making abilities.

Ecommerce Integration Approach

Rob New, who has a strong background within the Flight Centre system, is responsible for integrating the company’s ecommerce platforms. With an emphasis on crafting a seamless digital experience, New’s responsibilities involve leveraging Flight Centre’s broad brand portfolio to function as a single, cohesive commercial machine.

Customer Demands and Market Changes

James Kavanagh, Global Leisure CEO, emphasizes that the fusion of AI and digital commerce is essential as customer demands change and the travel market evolves. The strategic decisions to bring Steiner and New on board highlight Flight Centre’s dedication to remaining ahead of these transformations.

Conclusion

Flight Centre is on the brink of a significant transformation with the strategic placement of pivotal leaders in AI and digital commerce. By embedding AI in its processes and merging its ecommerce platforms, the organization seeks to bolster its competitive advantage and address the evolving needs of today’s travelers.

Q: What positions have Christopher Steiner and Rob New taken at Flight Centre?

A: Christopher Steiner is now the chief AI officer, and Rob New has taken on the role of head of digital commerce.

Q: What will be the impact of AI on Flight Centre’s operations?

A: AI will be essential for speeding up online booking growth and revamping the operating model into a productivity system.

Q: What is the objective of the agentic accelerator program?

A: The program aims to enhance employee productivity and decision-making through the use of AI agents across Flight Centre’s leisure brands.

Q: In what way will ecommerce be revamped under Rob New’s guidance?

A: New will concentrate on consolidating Flight Centre’s ecommerce platforms to establish a unified and effective digital commercial system.

Q: What makes these changes important for Flight Centre?

A: These changes are crucial for enabling Flight Centre to adapt to shifting customer expectations and remain competitive in the travel sector.

Samsung Galaxy Buds3 FE Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Samsung Galaxy Buds3 FE, Wireless Earbuds, Black, Blade Design, Balanced Sound, 360 Audio, Active Noise Cancelling & Clear Call (UAE Version)

AI Agents Stealthily Emerge as Leading Users in Companies, Leaving Organisations Unprepared


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

AI Agents: The Emerging Power User in Enterprises | TechBest

Brief Overview

  • AI agents are increasingly being adopted in organizations, frequently lacking appropriate governance.
  • These agents manage sensitive information and demand rigorous access controls.
  • Machine identities surpass human identities, complicating security management.
  • Organizations face security risks from AI agents with excessive permissions.
  • New standards such as MCP heighten the number of connections requiring secure oversight.
  • Contemporary identity security must progress to encompass AI agents.
  • Palo Alto Networks’ Idira aids in managing access across various identity types.

The Growth of AI Agents in Organizations

AI agents are swiftly becoming a fundamental part of the enterprise identity framework. However, numerous organizations are implementing them more quickly than they can regulate, leading to significant blind spots regarding the access capabilities of these agents, the systems they can connect to, and how that access is managed.

AI agents are becoming vital in organizations, with governance challenges.

As AI agents increasingly engage with sensitive information and automate operational workflows on behalf of users, they are being integrated into customer service, software development, and knowledge management. The primary security concern is not just what these agents are capable of, but whether organizations truly grasp and govern the privileges they have been assigned.

A New Category of Privileged Identity

Many organizations still wrongly interpret AI agents as simple software applications. In reality, they function as digital workers, capable of retrieving data, initiating workflows, and interfacing with critical business applications. Whether linked to internal knowledge repositories or customer-centric platforms, these agents frequently handle extremely sensitive data. Nevertheless, distinct ownership and visibility of how these permissions are utilized remain significantly inadequate.

This issue arises at a moment when the overall identity landscape already faces considerable pressure. Palo Alto Networks’ 2026 Identity Security Landscape Report revealed that machine identities now exceed human identities by a ratio of 109 to 1 in Australia, with both machine and AI agent identities anticipated to surge in the upcoming year. As organizations expand their AI initiatives, they are adding a vast, intricate layer of non-human users that necessitate the same visibility, governance, and accountability that have traditionally been applied to human employees.

The Broadening Attack Surface

AI agents are not intrinsically risky; the danger arises when organizations assign enterprise-level privileges before implementing enterprise-level controls. Our research shows that Australian organizations estimate around 40% of AI agents and 41% of machine identities already have access to organizational data, including vital business systems.

An AI agent with excessive permissions presents an attractive target for cybercriminals. If breached, manipulated, or misused, it turns into a trusted entryway into the organization, enabling malicious actors to navigate laterally through networks, remove data, or interrupt essential operations.

This issue is compounded by emerging standards like the Model Context Protocol (MCP). While MCP is beneficial for scaling agentic AI by establishing a consistent method for agents to communicate with databases and enterprise applications, it concurrently amplifies the number of credentials, permissions, and trust relations that are active throughout the network.

Each new link between an AI agent and a business system generates an access route that must be protected. As organizations develop these interconnected AI ecosystems, insight into who or what possesses access to critical systems becomes as critical as securing the AI models themselves.

Advancing Governance for the Agentic Age

To reduce these risks, contemporary identity security principles must be broadened to encompass all identity types, including human, machine, and agentic.

This necessitates a thorough strategy: identifying and cataloging all AI identities, implementing lifecycle management, enforcing stringent least-privilege access, and consistently monitoring for unusual activity. It additionally involves ensuring human oversight for compliance and guaranteeing that access can be immediately revoked if an agent is compromised or decommissioned.

As AI agents become deeply integrated into everyday operations, traditional identity tools will become insufficient. Organizations need advanced identity security platforms that extend governance beyond typical human users. The industry is experiencing a profound transformation: transitioning from managing only human access to governing every single identity operating within the enterprise from a centralized control framework.

To assist organizations in navigating this transition, Palo Alto Networks has recently introduced Idira. By merging privileged access management with capabilities for machine and agentic identity security, Idira offers a unified platform to discover, secure, and govern access across all identity types.

AI agents are swiftly becoming the most interconnected and privileged entities within the enterprise. As Australian organizations continue to expand agentic AI, strong governance will shift from being an obstacle to becoming the ultimate facilitator of security, trust, and innovation.

Conclusion

As AI agents become increasingly integrated into enterprise practices, they introduce new challenges for identity management and security. Organizations must tackle the governance of these agents to avert security incidents and maintain compliance. The emergence of AI agents requires a transformation in identity security strategies, with platforms like Palo Alto Networks’ Idira offering the essential tools for managing an array of identity types.

Q: What are AI agents and how are they utilized in organizations?

A: AI agents are software applications that carry out automated functions and interact with data and systems. In organizations, they are employed for customer service, software development, and knowledge management, among various other activities.

Q: Why do AI agents present a security concern?

A: AI agents create a security concern when they are given excessive privileges without adequate controls, rendering them potential targets for attackers aiming to exploit their access to confidential data and systems.

Q: What is the Model Context Protocol (MCP) and what impact does it have on AI agents?

A: The MCP is a protocol that streamlines interactions between AI agents and enterprise applications. While it aids in the scalability of AI deployment, it also complicates the management of credentials and access routes.

Q: How can organizations enhance governance for AI agents?

A: Organizations can strengthen governance by cataloging AI identities, managing their lifecycles, enforcing least-privilege access, and scrutinizing for anomalies, ensuring human oversight and quick response to security incidents.

Q: What is Palo Alto Networks’ Idira, and how does it assist with AI agent governance?

A: Idira is a solution from Palo Alto Networks that merges privileged access management with machine and agentic identity security features, providing a cohesive approach for discovering, securing, and managing access for all identity types.

New Cybersecurity Leader Named at JB Hi-Fi Group


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

New Cyber Security Leader at JB Hi-Fi Group

Quick Overview

  • Kanchana Devi has been appointed as the leader of group cyber security at JB Hi-Fi Group.
  • Devi has a robust background with the University of Melbourne and Accenture.
  • Devi’s goal is to improve cyber resilience and foster secure innovation.
  • JB Hi-Fi Group comprises JB Hi-Fi, The Good Guys, and e&s.
  • Former cyber security head Daniel Eastley is now the CISO at the Country Fire Authority in Victoria.

Overview

In a calculated initiative to strengthen its cybersecurity framework, JB Hi-Fi Group has revealed the appointment of Kanchana Devi as the leader of group cyber security. This follows the exit of Daniel Eastley in April, who has transitioned to a key position at the Country Fire Authority in Victoria.

Kanchana Devi’s Path

Kanchana Devi shared her excitement about joining JB Hi-Fi Group in her latest LinkedIn update. She is keen to partner with diverse teams within the group to boost cyber resilience and secure business functions, while also promoting safe innovation in the contemporary digital landscape.

Devi’s considerable experience encompasses her recent position at the University of Melbourne and a noteworthy 13-year tenure at Accenture, where she refined her skills in cyber security and digital transformation.

Retail Footprint of JB Hi-Fi Group

JB Hi-Fi Group is a prominent name in the retail domain, featuring well-known brands like JB Hi-Fi, The Good Guys, and e&s. The group’s dedication to enhancing its cybersecurity measures is underscored by Devi’s appointment, with the aim of safeguarding their extensive customer base and business operations.

New Position for Daniel Eastley

Daniel Eastley, who previously occupied a leadership role at JB Hi-Fi Group, now assumes the role of Chief Information Security Officer (CISO) at the Country Fire Authority in Victoria. His time at the Australian Red Cross Lifeblood equipped him with invaluable insights into infrastructure and security, which he now applies in the fire authority.

New cyber security leader announced by JB Hi-Fi Group

Conclusion

Kanchana Devi’s appointment as head of group cyber security at JB Hi-Fi Group signifies an important advancement in reinforcing the company’s cyber resilience. Her extensive background from earlier roles and her vision for secure innovation are in line with the group’s goals of protecting its operations and customer information.

Q: Who is the newly appointed head of group cyber security at JB Hi-Fi Group?

A: Kanchana Devi has taken on the role of the new head of group cyber security.

Q: What expertise does Kanchana Devi bring to JB Hi-Fi Group?

A: Devi brings extensive expertise stemming from her positions at the University of Melbourne and Accenture.

Q: Which brands are part of the JB Hi-Fi Group?

A: The JB Hi-Fi Group consists of JB Hi-Fi, The Good Guys, and e&s.

Q: What is Daniel Eastley’s new position following his departure from JB Hi-Fi Group?

A: Daniel Eastley is now the Chief Information Security Officer at the Country Fire Authority in Victoria.

Alinta Energy Implements State-of-the-Art AI for Improved Executive Insights


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Alinta Energy’s AI-Driven System for Executive Decision Support

Brief Overview

  • Alinta Energy has introduced AISE, a system using AI for executive insights.
  • AISE links executives to data and documents, improving decision processes.
  • The system was created in partnership with Databricks.
  • AISE analyzes 500 data metrics and more than 9000 documents.
  • Each insight features a confidence score for better guidance.
  • AISE is fully implemented and growing within Alinta Energy.

Overview of Alinta Energy’s AI Project

Alinta Energy, a prominent electricity generator and retailer, has rolled out an advanced AI system intended to aid its executive team in making well-informed choices. This initiative signifies a substantial leap in the firm’s application of technology to optimize and enhance strategic decision-making procedures.

The Alinta Intelligent Strategic Engine (AISE)

Launched at the Databricks’ Data + AI Summit in the U.S., the Alinta Intelligent Strategic Engine, known as AISE, is the result of a joint effort between Alinta’s CEO and CIO. As stated by Brad Walker, the general manager of data and AI, AISE was developed within a four-week timeframe, utilizing around 70 person-days of labor.

Capabilities of the System

AISE combines 500 structured data metrics and over 9000 documents, including board papers and strategic presentations. The system uses a supervising agent to interpret executive requests and present relevant insights, each paired with a confidence score to guide decision-making.

AISE’s Influence on Decision-Making

By offering a confidence score, AISE assists executives in assessing the reliability of the insights gathered. This functionality is vital in ensuring decisions are rooted in robust data, minimizing risks associated with strategic initiatives. The system is structured to help executives make decisions with varying degrees of certainty, from highly confident to more cautious insights.

Upcoming Developments

AISE is presently in active use, with ambitions to broaden its functionality across Alinta Energy’s diverse business divisions. This ongoing enhancement aims to deepen the integration of AI within the company’s operations, solidifying its commitment to utilizing technology for business advancements.

Conclusion

The implementation of the AISE system by Alinta Energy signifies a crucial stride towards embedding AI in executive decision-making. By leveraging data-driven insights, the organization positions itself at the forefront of technological progress in the energy industry.

Questions & Answers

Q: What does AISE stand for?

A: AISE refers to Alinta Intelligent Strategic Engine, an AI system tailored to provide data-driven insights for executive decision-making.

Q: In what way does AISE operate?

A: AISE employs a multi-agent framework to process data metrics and documents, delivering insights with a confidence score to assist executive decisions.

Q: What advantages does AISE offer Alinta Energy?

A: AISE advances decision-making by delivering trustworthy insights, mitigating risks, and enhancing the efficiency of strategic planning.

Q: Is AISE exclusive to Alinta Energy?

A: At present, AISE has been specifically designed for Alinta Energy, though similar systems might be investigated by other organizations in the future.

Q: How was AISE created?

A: AISE was developed in collaboration with Databricks over a four-week period, involving approximately 70 person-days of effort.

Q: What future enhancements are anticipated for AISE?

A: Alinta Energy intends to broaden AISE’s functionalities throughout its business units, further integrating AI into its operations.

Medical Clinic Consortium Partnered Health Experiences Data Breach


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Partnered Health Data Breach: Essential Information

Brief Overview

  • Data breach at Partnered Health impacts 21 clinics.
  • Confidential personal and medical information has been compromised.
  • Legal restraining order secured to avoid data exploitation.
  • Possible scam risks targeting those impacted.
  • Bupa intends to purchase Partnered Health for $450 million.

Details of the Breach

On June 23, Partnered Health, based in Adelaide, disclosed a major data breach involving 21 of its general practitioner clinics. The incident led to the unauthorized access of sensitive personal and medical details, including names, addresses, contact numbers, Medicare, private health insurance, and Veteran Card identifiers.

Incident of data breach at Partnered Health clinic

Medical data and treatment records were allegedly accessed during the breach. Nevertheless, Partnered Health has not provided technical details about the attack or the complete scope of the compromised data.

Legal Actions and Security Protocols

Following the breach, Partnered Health secured a court injunction from the Supreme Court of New South Wales to block the use or release of the stolen data. The organization has also cautioned its customers to remain alert to potential scams arising from the inappropriate use of their personal information.

Corporate News

In light of the data breach, health insurance and medical service operator Bupa has announced plans to acquire Partnered Health for $450 million. This acquisition is awaiting approval from the Australian Competition and Consumer Commission and the Foreign Investment Review Board.

Conclusion

Partnered Health has faced a significant data breach impacting 21 clinics, with personal and medical information being compromised. Legal measures are underway to deter the misuse of data, while Bupa is set to make a substantial acquisition of the organization.

Questions & Answers

Q: What type of information was compromised in the breach?

A: The breach involved names, addresses, contact numbers, Medicare, private health insurance, Veteran Card identifiers, and medical data.

Q: How many clinics were impacted by the data breach?

A: The breach affected a total of 21 clinics.

Q: What legal actions has Partnered Health implemented?

A: Partnered Health has secured an injunction from the Supreme Court of New South Wales to prevent the misuse of the stolen information.

Q: What should individuals affected be mindful of?

A: Affected individuals should be wary of scams that might leverage their compromised data.

Q: Who is in the process of acquiring Partnered Health?

A: Bupa is in the process of acquiring Partnered Health for $450 million, pending regulatory approvals.

Hard lines, wider nets: the Indo-Pacific week in seven moves


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Taiwan moved missiles, ASEAN reopened a door to Myanmar, Beijing built an AI institution, and the South China Sea argument turned ten without getting any safer.

Review: Razer Seiren V3 Pro – The Premier Hybrid Microphone for Streamers, Creators, and Presenters


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Concise Overview

  • Razer Seiren V3 Pro caters to creators, streamers, and presenters.
  • Features hybrid connectivity through USB-C and XLR ports.
  • Equipped with an integrated shock absorber and pop filter.
  • Showcases Razer Chroma RGB lighting for visual feedback.
  • Supports sophisticated audio processing via Razer Synapse software.
  • Retailing at AU$429.95, perfect for both novices and experts.

A Stunning, Practical Design

The Razer Seiren V3 Pro captivates immediately with its robust construction, made from premium zinc unibody. This weight guarantees stability when paired with a boom arm, preventing issues commonly seen with lighter microphones.

Unboxing Razer Seiren V3 Pro – The Complete Package

The package contains the microphone, a mini adjustable arm mount, a solid base, a cable, stickers, and an information booklet. The mic’s onboard bracket accommodates a standard thread for seamless transitions to a boom arm.

Subtle Features That Truly Perform

Razer’s aesthetics combine sleek professionalism with its distinctive flair. The built-in cover serves as a shock absorber and pop filter, removing the necessity for an external foam sock. The outer filter cover can be detached for a minimalist look.

Razer Seiren V3 Pro – Sleek and Subtle Design

The microphone incorporates Razer Chroma RGB lighting, featuring a discreet light ring at the base that changes color based on gain levels, providing real-time visual cues. It turns red when muted, clearly indicating the status.

Intelligent, Tactile Controls

The Razer Seiren V3 Pro shines in usability with a tap-to-mute sensor on top, removing the noise of physical button presses. A dedicated gain dial and headphone jack for zero-latency monitoring can be found at the bottom.

Smart Controls on Razer Seiren V3 Pro

Adaptability: The Power of Dual USB-C & XLR

The dual connectivity of USB-C and XLR enables the microphone to evolve with its user. The included USB cable comes with a USB-A to USB-C adapter for straightforward plug-and-play setup. For the best outcomes, the XLR connection is advisable.

Hybrid Connectivity of Razer Seiren V3 Pro

Utilizing both USB and XLR connections unlocks the microphone’s full capability, with USB powering the audio processing and RGB lighting. The setup requires two USB slots, one for the microphone and another for the mixer when using XLR.

Clear, Sharp, Studio-Quality Sound

The Razer Seiren V3 Pro provides outstanding audio quality with its 30mm dynamic capsule, delivering a warm, rich broadcast tone. It effectively isolates voice and diminishes background noise, reducing post-production work.

Razer Synapse Software with Razer Seiren V3 Pro

Razer Synapse software elevates the user experience with features like 32-Bit Float Support, AI noise reduction, and onboard DSP effects, further enhancing sound quality and performance.

Concluding Thoughts

The Razer Seiren V3 Pro stands as a versatile microphone suited for both beginners and professionals. With its USB and XLR functionalities, sturdy build, and advanced audio features, it presents remarkable value at AU$429.95.

Advanced Features of Razer Seiren V3 Pro in Synapse

Its elegant design, coupled with exceptional audio performance, makes it a worthwhile investment for anyone looking to elevate their audio setup.

Overview

The Razer Seiren V3 Pro is a remarkable addition to Razer’s offerings, tailored for creators, streamers, and presenters. Its hybrid connectivity, sturdy design, and superior sound quality render it ideal for a variety of professional uses. With advanced features available through Razer Synapse, it offers versatility and control, ensuring users can achieve broadcast-quality audio effortlessly.

Q: What makes the Razer Seiren V3 Pro appropriate for both novices and experts?

A: Its dual USB-C and XLR connectivity enables easy setup and scalability, making it perfect for beginners starting with USB and professionals moving to XLR setups.

Q: How does the Razer Seiren V3 Pro manage background noise?

A: The microphone boasts a dynamic capsule that efficiently isolates voice and minimizes background noise, supplemented by DSP features available through Razer Synapse.

Q: Is the Razer Seiren V3 Pro compatible with both PC and Mac?

A: Yes, it is compatible with both PC and Mac systems, due to its USB-C connection and the included USB-A to USB-C adapter.

Q: What advantages does using Razer Synapse with the microphone provide?

A: Razer Synapse grants access to advanced audio processing features including 32-Bit Float Support, AI noise reduction, and various DSP effects, enhancing audio quality and user control.

Q: Does the Razer Seiren V3 Pro come with an XLR cable?

A: No, the XLR cable is not included and must be purchased separately if you choose to use an XLR setup.

Q: How does the Razer Chroma RGB lighting improve the user experience?

A: The RGB lighting provides real-time visual indications of gain levels and mute status, offering an intuitive way to oversee audio settings during usage.