Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 28 of 185

US Cyber Agency Utilizes Mythos for Code Audits in Government


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Quick Overview

  • The US Cybersecurity and Infrastructure Security Agency (CISA) is utilizing Anthropic’s AI technology, Mythos, to assess government software for vulnerabilities.
  • Mythos has played a key role in pinpointing possible cybersecurity risks within government code repositories.
  • Anthropic’s association with the US government has been intricate, following a standoff regarding AI usage regulations.
  • In spite of earlier disputes, Mythos is now being employed by significant US security organizations like the NSA.
  • A public iteration of the AI, referred to as Fable, encountered limitations imposed by the White House but has recently been reinstated.

AI in Government Code Evaluations

The Cybersecurity and Infrastructure Security Agency (CISA) has adopted Anthropic’s AI model, Mythos, as part of its auditing initiatives for government software. This effort is designed to uncover and address errors that could potentially expose sensitive data to cybercriminals or foreign powers. The move illustrates the increasing integration of AI tools within government operations, strengthening protective measures against cyber threats.

US cyber agency utilizing Mythos for government code audits

CISA’s Attack Surface Evaluation Team

The evaluations are performed by CISA’s Attack Surface Evaluation team. This division specializes in assessments of digital security and conducts hacking tests across governmental agencies to validate the strength of their cyber defenses. While specific data on the quantity of vulnerabilities found is not disclosed, the process has reportedly uncovered multiple potential security risks.

Anthropic’s Intricate Relationship with the US Government

Anthropic, which has submitted for a US initial public offering, has had a rocky relationship with the government, mainly due to its protective measures against the misuse of its AI technology. In February, tensions reached a peak when the Pentagon designated the company as a supply-chain risk, alleging it could facilitate espionage. Nonetheless, this designation was lifted in March following a judicial decision.

Mythos and the NSA

Even with the earlier blacklisting, the National Security Agency (NSA) has been employing Mythos since April. The agency has been experimenting with the AI in classified environments, reportedly impressed by its ability to uncover and exploit cybersecurity vulnerabilities. This highlights the AI model’s importance in national security operations.

Public Version Fable and White House Action

Anthropic unveiled a public version of Mythos dubbed Fable, which included cybersecurity protections. However, the White House stepped in, requesting limitations on foreign access to the model. This resulted in a temporary global suspension of Fable, which was rescinded last week, restoring its accessibility.

Conclusion

Anthropic’s AI technology Mythos is playing an essential role in fortifying US government software by identifying possible vulnerabilities. Despite early disagreements with the US government, the AI’s abilities have been acknowledged and utilized by crucial security agencies. The public version, Fable, has also undergone challenges but remains a vital resource in the cybersecurity domain.
Q: What is Mythos?

A: Mythos is an AI model created by Anthropic, employed by CISA to evaluate government software and uncover cybersecurity vulnerabilities.

Q: What challenges did Anthropic encounter with the US government?

A: Anthropic faced a standoff with the US government due to its insistence on retaining AI safeguards, leading to a supply-chain risk classification, which was subsequently lifted.

Q: How is Mythos utilized by the NSA?

A: The NSA has been using Mythos since April, testing it in classified environments to identify and exploit cybersecurity vulnerabilities.

Q: What is Fable?

A: Fable is the public version of the Mythos AI model, featuring cybersecurity safeguards, which experienced temporary restrictions from the White House.

Q: What is CISA’s involvement with Mythos?

A: CISA employs Mythos to review government code repositories, aiming to protect sensitive government systems from potential cyber threats.

Huawei FreeBuds Pro 5 Wireless Bluetooth Headphones Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Huawei FreeBuds Pro 5 Wireless Bluetooth Headphones, in-Ear Headphones, AI Noise Cancelling for Business & Office, Stable Calls, IP57, for Sports, 38 Hours Battery, Black

Aegis Cybersecurity Founder Cautions About Increasing Examination of Tech Vendor Risks


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Increasing Attention on Tech Vendor Threats

Australian Entities Heighten Attention on Tech Vendor Threats

Heightened focus on tech vendor threats as outlined by Aegis Cybersecurity

Luke Irwin, Aegis Cybersecurity

Quick Overview

  • Heightened emphasis on vendor risk management within Australian entities.
  • Focus on the necessity for extensive cybersecurity evaluations.
  • Issues regarding SaaS data security and backup methodologies underscored.
  • Significance of synchronizing cybersecurity with business imperatives and leadership dialogue.

Vendor Risk Management: An Escalating Concern

Australian entities are increasingly turning their attention towards vendor risk management, spurred by recent notable breaches. The urgency to comprehend and navigate the risks tied to suppliers and their supply chains is becoming increasingly clear, as noted by Aegis Cybersecurity’s founder, Luke Irwin.

Beyond Checklists: A Thorough Exploration into Risk Evaluation

Irwin champions a more comprehensive methodology for cybersecurity risk evaluation, extending beyond mere questionnaires and checklists. Organisations ought to assess who has access to their systems and confirm that crucial SaaS platforms are properly backed up.

Obstacles in SaaS Data Security

A number of Managed Service Providers (MSPs) excel in backing up systems such as O365 and SharePoint. Nevertheless, the same level of attention is not consistently granted to other essential systems like Salesforce and Xero. Guaranteeing complete data security and verifying recovery abilities is vital for business continuity.

Integrating Cybersecurity with Business Leadership

There is a pressing need to weave cybersecurity into the fabric of business leadership and decision-making frameworks. Often viewed as an IT concern, cybersecurity demands a strategic orientation, harmonizing with corporate goals and organisational risk management methodologies.

Conclusion

As the focus on vendor risk management strengthens in Australia, organisations must embrace comprehensive cybersecurity frameworks. This encompasses evaluating risks throughout the supply chain, assuring robust SaaS data security, and synchronizing cybersecurity efforts with business aims.

Q&A

Q: What is fueling the emphasis on vendor risk management?

A: Recent notable breaches have heightened awareness of the vulnerabilities existing within supply chains, encouraging organisations to examine their vendor partnerships more critically.

Q: What are frequent oversights in cybersecurity agreements?

A: A significant oversight involves the absence of obligatory breach notification clauses, which should ideally stipulate notification within a 24 to 48-hour timeframe.

Q: How can organisations enhance their SaaS data security?

A: Organisations need to implement thorough backup methodologies for all critical SaaS applications and consistently evaluate their recovery processes.

Q: Why is cybersecurity frequently regarded as an IT issue?

A: Cybersecurity is often viewed as an IT challenge due to its technical aspects, but it requires a more extensive business strategy to effectively safeguard organisational assets.

OPPO Enco Buds3 True Wireless Headphones Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

OPPO Enco Buds3 True Wireless Headphones, 42 Hours Runtime, Dynamic Driver 12.4mm, BT 5.4, Touch Control, Passive Noise Cancellation, Android and iOS, IP55, [Italian Version] White

Tesla Cybercab Ready to Shuttle Workers at Giga Texas


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Read

  • Tesla is progressing with its Cybercab project at the Giga Texas plant.
  • These self-driving vehicles do not have standard controls such as steering wheels or pedals.
  • The current operation is limited to the factory and not on public routes.
  • Challenges consist of navigation, charging capabilities, and logistical cleaning.
  • The initiative aims to enhance employee transport within the large gigafactory.

Cybercab Launch at Giga Texas

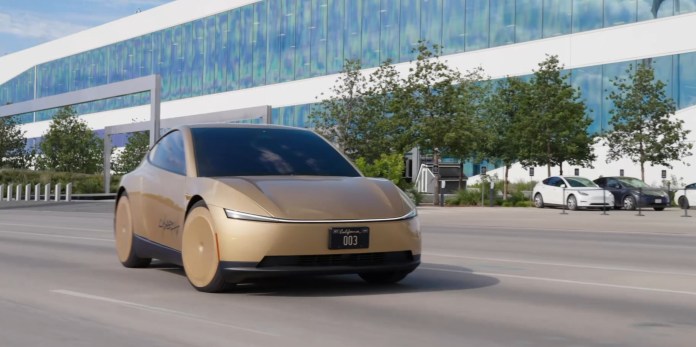
Tesla has made a major advancement toward self-driving transport with the rollout of its Cybercab at the Giga Texas site. These vehicles, intended as robotaxis, are planned to carry workers across the extensive location without conventional steering mechanisms or pedals, providing a preview of the future of autonomous transportation.

Tesla Cybercab autonomous vehicle at Giga Texas

Advancements in Autonomous Technology

Autonomous technology has been a subject of forward-looking debates, but Tesla’s Cybercab initiative makes it more tangible. These vehicles have been observed in drone videos and social media, signifying a concrete progression in the autonomous vehicle field.

Operation and Logistics Challenges

Navigation within the Factory

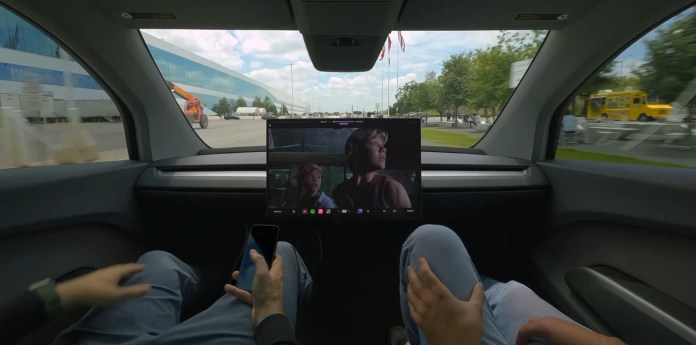
The functionality of these Cybercabs in the gigafactory raises inquiries about their navigation. Will Tesla implement a specific mapping system, or will workers input destinations via touchscreens?

Charging and Maintenance

The charging setup is another crucial aspect. While wireless charging may eventually be available, the early phases might depend on conventional supercharging. Regular maintenance and cleanliness will also be essential for efficient operation.

Tesla Cybercab ready for autonomous deployment at Giga Texas

Future Prospects for Autonomous Vehicles

Though currently restricted to the Giga Texas site, the Cybercab project represents an exciting progression in the field of autonomous vehicles. It reflects Tesla’s enduring dedication to innovation and its prospective influence on global mobility and transport economics.

Summary

The introduction of Tesla’s Cybercab at Giga Texas symbolizes a significant milestone in autonomous vehicle technology. By facilitating employee transport within the factory through self-driving robotaxis, Tesla propels its vision of a driverless future. Despite ongoing challenges regarding navigation, charging, and maintenance, this project highlights the transformative possibilities of autonomous vehicles.

Frequently Asked Questions

Q: What is the Tesla Cybercab?

A: The Tesla Cybercab is an autonomous vehicle initiative aimed at transporting employees within the Giga Texas facility without conventional driving controls.

Q: Where is the Cybercab currently being used?

A: The Cybercab is presently operational at Tesla’s Giga Texas factory, used solely for employee transport.

Q: How do the Cybercabs navigate the factory?

A: The method of navigation has not yet been confirmed, but it may involve a specialized mapping system or employees setting destinations through touchscreens.

Q: What are the main logistical challenges of the Cybercab project?

A: Significant challenges include establishing effective charging methods, ensuring consistent maintenance and cleaning, and optimizing navigation within the factory.

ACSC Releases Second Alert in Two Months as Unresolved CMS Vulnerabilities Persist in Being Abused


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

ACSC Releases New Alert Regarding CMS Vulnerabilities

Brief Overview

  • ACSC has issued a second warning within two months concerning CMS vulnerabilities.
  • 17 vulnerabilities are being exploited on a global scale, impacting Australian SMEs.
  • Updates are provided for all identified vulnerabilities.
  • Administrators should verify for signs of infection.
  • Users of managed hosting should ask about monitoring for breaches.

ACSC’s Second CMS Warning in a Two-Month Span

Second warning from ACSC in two months indicates ongoing exploitation of unpatched CMS vulnerabilities

Widespread Exploitation of Flaws

The Australian Signals Directorate’s Australian Cyber Security Centre (ACSC) has issued a second notification in a mere two months concerning flaws in content management systems (CMS). This warning highlights a global initiative exploiting 17 particular vulnerabilities, affecting websites run by small to medium-sized enterprises (SMEs) throughout Australia and beyond.

Vulnerabilities in Key CMS Systems

The vulnerabilities are present across various major CMS platforms, encompassing WordPress plugins, Craft CMS, MaxSite CMS, MetInfo CMS, and Joomla’s JCE editor. Several of these issues date back to 2024, demonstrating persistent security deficiencies that remain unresolved for numerous users.

Prior Notifications and Current Exploits

The recent alert follows an earlier warning from ACSC regarding the ClickFix campaign, which involved compromised WordPress sites that distributed the Vidar Stealer malware. In spite of available patches, the ACSC observes continued exploitation attempts on vulnerabilities such as CVE-2025-32432 in Craft CMS, which was initially exploited as a zero-day vulnerability.

Advice for Administrators and Hosting Companies

Administrators are encouraged to locate and address signs of compromise, such as webshells and harmful scripts, and to install all applicable security updates. The ACSC also recommends turning off vulnerable components if immediate patching is not achievable. Users of managed hosting services should engage with their providers to discuss how they monitor and handle exploitation efforts.

Conclusion

The latest alert from the ACSC emphasizes the ongoing risk presented by unpatched CMS vulnerabilities, impacting many Australian businesses. With updates readily available, prompt installations and proactive security strategies are crucial to protect against exploitation.

Q: Why did the ACSC send another alert in such a short time?

A: The ACSC identified persistent exploitation of existing vulnerabilities in CMS platforms, necessitating another alert to highlight the urgency of applying patches.

Q: Which CMS platforms are impacted by these flaws?

A: The vulnerabilities impact platforms that include WordPress, Craft CMS, MaxSite CMS, MetInfo CMS, and Joomla’s JCE editor.

Q: What actions should website administrators undertake?

A: Administrators should search for indicators of compromise, implement security updates, and disable vulnerable components if patches cannot be applied without delay.

Q: How can businesses utilizing managed hosting guarantee their security?

A: Businesses should consult with their hosting providers regarding their monitoring methods and responses to active exploit attempts.

Q: Are any vulnerabilities actively being exploited as zero-days?

A: Indeed, CVE-2025-32432 in Craft CMS was targeted as a zero-day prior to the patch release in April 2025.

ANZ Prepared to Trial Swift’s Blockchain Ledger


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

ANZ to Experiment with Swift’s Blockchain Ledger

Brief Overview

  • ANZ partners with 16 other banks to explore Swift’s blockchain ledger.
  • Swift’s technology seeks to allow fund transfers 24/7, even on weekends.
  • This initiative signifies a significant advancement for banks utilizing blockchain technology.
  • Swift manages cross-border transactions for 11,500 banks worldwide.
  • The project tackles the growth of tokenized payments and digital currencies.

Swift’s Blockchain Project

The global financial messaging network Swift has initiated a blockchain-centric shared ledger, with Australian bank ANZ among its 17 initial collaborators. This venture aspires to provide round-the-clock payment services and to create a competitive advantage in the expanding stablecoin sector.

ANZ to experiment with Swift's blockchain ledger

Consequences for the Banking Industry

Swift’s latest blockchain ledger permits the transfer of “tokenized” assets at any time, offering financial transactions the adaptability and programmability typically linked to digital currencies. This innovation represents one of the most ambitious attempts by mainstream banking to adopt blockchain technology while ensuring adherence to global regulatory frameworks.

Involved Banks and Worldwide Demand

In addition to ANZ, the initiative encompasses major banks such as UBS, BNP Paribas, BNY, Standard Chartered, MUFG, DBS, Lloyds, and Wells Fargo. The involvement of these institutions highlights the significant worldwide demand for a system that facilitates the interoperability of tokenized payment methods across different organizations.

Prospects for Digital Transactions

This initiative is set to foster future innovations like programmable money and agentic commerce, where automated systems can execute transactions on users’ behalf. Such developments could transform the manner in which digital transactions are performed within a regulated environment.

Swift’s Worldwide Presence

Swift is a cornerstone of international banking, managing cross-border transactions for more than 11,500 banks and financial service providers around the globe. The organization oversees payments equivalent to the global GDP every few days, across over 200 nations.

Conclusion

The partnership between Swift and 17 prominent banks, including ANZ, to pilot a blockchain-based shared ledger signifies a major step toward 24/7 payment solutions. This effort not only responds to the needs of the evolving financial landscape but also lays the groundwork for further advancements in digital transactions.

Q: What is the primary objective of Swift’s blockchain initiative?

A: The primary objective is to enable continuous fund transfers and compete within the stablecoin space.

Q: How many banks are taking part in this initiative?

A: Seventeen banks, including ANZ, are engaged in the project.

Q: What are the benefits of a blockchain-based shared ledger?

A: Benefits include the ability for tokenized funds to be programmable and transferrable at all times, enhancing flexibility and efficiency.

Q: How does Swift’s initiative affect the future of banking?

A: It sets the stage for innovations such as programmable money and agentic commerce, potentially reshaping digital transactions within the regulatory landscape.

Q: What is the extent of Swift’s existing payment network?

A: Swift enables cross-border payments for over 11,500 banks globally, processing transactions equivalent to the world GDP every few days.

HUAWEI FreeClip 2 Wireless Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

HUAWEI FreeClip 2, Wireless Earbuds, Airy C-bridge Design, Adaptive Open-ear Listening, Crystal-clear Calls, 38h Long Battery Life, Open-Ear Headphone, Compatible with iOS & Android, IP57 Berry Purple

Tesla’s FSD V14 Lite Early Access in Korea Brings Optimism for Global AI3 Owners


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • Tesla’s FSD V14 Lite has launched in South Korea, representing its inaugural rollout beyond the USA.
  • This launch is crucial for older AI3 hardware users who are eager for upgrades in autonomy.
  • South Korea’s intricate driving conditions offer a tough testing framework for Tesla’s technology.
  • Tesla owners in Australia are optimistic about a corresponding rollout, despite the complications of left-hand driving.

The hardware challenge and the smart adjustment of V14 Lite

Tesla’s choice to introduce the V14 Lite iteration of its Full Self-Driving (FSD) software in South Korea signifies an important accomplishment in the firm’s global expansion plans. This custom version aims to enhance AI3 hardware, allowing older models to take advantage of semi-autonomous functions without being hampered by the requirements of advanced neural networks. This strategy keeps millions of vehicles pertinent in the quest for complete autonomy.

Tesla's FSD V14 Lite deployment in South Korea inspires hope for global AI3 owners
Tesla’s thorough launch in South Korea may set the stage for upcoming worldwide releases.

Reasons South Korea was selected as the launch site

Choosing South Korea as the premier international market for the FSD V14 Lite is a deliberate strategy. The nation’s difficult urban environments, characterized by narrow roads and a diverse range of assertive traffic participants, create a demanding testing landscape. Moreover, the right-hand drive compatibility with the US negates the necessity for immediate software modifications, streamlining the rollout process.

Regional infrastructure and regulatory harmony

South Korea’s sophisticated cellular backbone and accommodating regulatory landscape further establish its fit as a testing ground for Tesla’s innovations. The nation’s dedication to smart city projects and forward-thinking policies enables Tesla to perform crucial public software tests with relative simplicity, gathering essential information for future upgrades.

Implications of staged validation for global rollout

The initial launch focuses on early access program members in South Korea, who are essential in pinpointing region-specific problems. This method allows Tesla to enhance the software ahead of a wider release. Once confirmed, Tesla’s adaptable end-to-end neural networks will make it easier to implement modifications for other overseas markets.

Rising expectations among Australian Tesla owners

Australian Tesla owners are particularly enthusiastic about the FSD V14 Lite launch. Despite owning vehicles with AI3 hardware, they have been constrained by outdated software versions. The imminent introduction of V14 Lite rekindles hope, although obstacles remain in adapting the platform for left-hand drive setups, which is essential for ensuring safety and effectiveness.

Local timeline and subsequent steps

It is likely that Australian roadways are already supplying important data to Tesla’s network, which will be vital for the eventual FSD V14 Lite launch. Following South Korea’s lead, a staged rollout featuring local beta testers is expected. Given the rapid advancements in Tesla AI, Australians may soon have access to the latest in autonomous driving capabilities.

Conclusion

The rollout of Tesla’s FSD V14 Lite in South Korea is a crucial move in its global growth strategy. By fine-tuning older AI3 hardware, Tesla ensures that a wider range of vehicles can access new technologies. The demanding driving scenarios in South Korea provide an ideal testing opportunity, and insights gained there will inform future launches in regions like Australia, where enthusiasm is strong.

Q: What is the significance of Tesla’s FSD V14 Lite rollout in South Korea?

A: It represents the initial release of this software version outside the USA, signifying a key milestone in Tesla’s international strategy.

Q: How does V14 Lite assist owners with AI3 hardware?

A: V14 Lite is optimized to provide advanced driving functionalities without overwhelming older AI3 hardware, prolonging the usefulness of these vehicles.

Q: Why was South Korea chosen for the inaugural international rollout?

A: South Korea’s intricate urban driving scenarios provide a rigorous testing environment, and its right-hand drive alignment with the US facilitated the deployment.

Q: What can Australian Tesla owners anticipate from this development?

A: Australian owners are hopeful for a similar launch, although left-hand drive challenges persist. Local testing and data gathering are likely already in progress.

State of Security 2026: Protecting Australia’s Data Future


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Protecting Australia’s Data Future: Toll Group’s Holistic Strategy

  • Cyber threats are changing, demanding a thorough security strategy.
  • Toll Group incorporates security into procurement and vendor oversight.
  • AI introduces new hurdles for data governance and security.
  • Critical infrastructure classification under the SOCI Act has national implications.
  • Enhanced due diligence and third-party risk management are primary focuses.

Comprehending the Cyber Threat Landscape

The international logistics and supply chain entity, Toll Group, is transforming its data security strategy in light of the rapidly shifting cyber threat landscape. Conventional security methods such as robust firewalls and access controls are increasingly inadequate for a globally operating supply chain, as pointed out by Vasant Prabhu, Toll Group’s global data protection chief.

Holistic security strategy for Australia's data future

Integrating Security into Business Procedures

Active in more than 50 countries, Toll Group has integrated security prerequisites into its procurement protocols, contracts, and third-party risk oversight. The aim is to handle security in a proactive manner rather than a reactive one, as emphasized by Prabhu. This methodology is essential considering the logistics industry’s heightened risk profile in the global economy.

National Significance and SOCI Act Compliance

Toll Group’s infrastructure is classified as critical under Australia’s Security of Critical Infrastructure (SOCI) Act, which imposes responsibilities beyond mere commercial risk management. Any failures may lead to national consequences, underscoring the necessity for robust security protocols.

Protecting Australia's data future and vital infrastructure

Tackling Third-Party and AI Challenges

The rise in risks from third-party vendors, together with complexities linked to AI, demands a flexible security perimeter. Toll Group has improved vendor due diligence, restricted third-party access, and assessed AI interactions with enterprise data. Solutions like ProcessUnity ensure that security is incorporated from the beginning.

Gaining Insights from Previous Cyber Incidents

In the aftermath of a major cyberattack in 2020, Toll Group acknowledges the significance of proactive security measures. The organization’s emphasis on supply chain and vendor security stems from previous experiences, regulatory demands, and emerging threats.

Comprehensive data security strategy for the future

AI and the Future of Data Protection

The incorporation of AI into projects brings about new challenges concerning data security and governance. Queries related to data input, model efficiency, and jurisdictional data handling are prompting a reevaluation of existing security frameworks. Prabhu underscores the importance of effective governance and safeguards as Agentic AI becomes increasingly widespread.

Conclusion

Toll Group’s holistic strategy for data security mirrors the shifting cyber threat landscape and the distinct challenges encountered by the logistics industry. By incorporating security into procurement and vendor management, addressing AI complexities, and adhering to the SOCI Act, Toll Group is establishing a standard for protecting Australia’s data future.

Q: Why is a holistic security strategy essential for Toll Group?

A: The changing cyber threat landscape and global operations render traditional security measures inadequate.

Q: How does Toll Group embed security into its business procedures?

A: Security requirements are integrated into procurement, contracts, and third-party risk management to proactively address threats.

Q: What relevance does the SOCI Act hold for Toll Group?

A: Being categorized as critical infrastructure under the SOCI Act implies that failures may have national consequences, necessitating strong security.

Q: In what way does AI influence data protection at Toll Group?

A: AI introduces new challenges in governance and security, requiring a reassessment of current strategies.

Q: What part do third-party risk platforms serve in Toll Group’s security strategy?

A: Solutions like ProcessUnity ensure that security is a prerequisite for entry, aiding in the effective management of third-party and vendor risks.

Q: How did the cyberattack in 2020 shape Toll Group’s security protocols?

A: The incident highlighted the necessity for proactive security strategies, focusing attention on supply chain and vendor security.

Q: What future challenges does Toll Group foresee with advancements in AI?

A: The emergence of Agentic AI and its associated complexities will necessitate increased focus on governance and security measures.