Security Specialist Cautions Against Installing Meta’s Muse AI Assistant

We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Brief Overview
- Security specialist Patrick Wardle advises against using Meta’s Muse AI assistant due to a zero-day vulnerability.
- The issue, termed “not-a-mused”, permits the redirection of dictated audio to an attacker’s domain.
- Muse AI’s significant access to system resources renders it a prime target for potential threats.

Security Risks Associated with Meta’s Muse AI Assistant
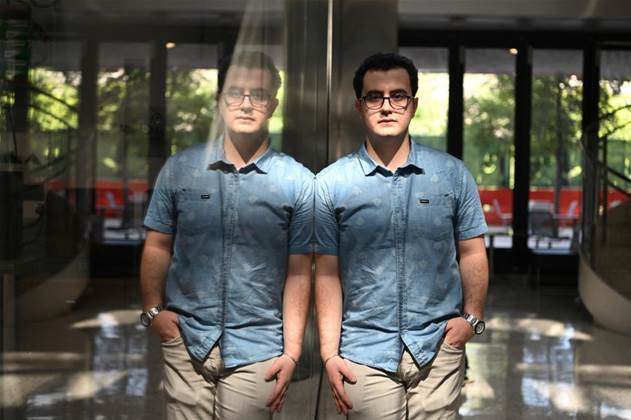
Renowned macOS security expert, Patrick Wardle, has alerted Mac users regarding Meta’s recently released Muse AI assistant. His warning follows the release of proof-of-concept code for a zero-day vulnerability, which he asserts can easily convert the app into a backdoor for cybercriminals.
Wardle, founder of the Objective-See Foundation and writer of The Art of Mac Malware, revealed the vulnerability, labeled “not-a-mused”, via an X thread and a functioning exploit on GitHub. He pointed out that this vulnerability enables any local process to modify an undocumented setting, endo_voyager_dictation_endpoint, without needing elevated permissions.
Risk Factors of Muse AI
The main danger involves rerouting the audio dictated to Muse to an attacker’s server instead of Meta’s. This redirection can facilitate capturing prompts, introducing harmful commands into the assistant, and stealing authentication data. The exploit only requires the user to click the microphone and dictate as they usually would.
Wardle noted that this proof of concept presumes an attacker can already execute code on the user’s machine. He stressed that Muse AI presents a uniquely attractive target due to its extensive access to system resources, which significantly exceeds the standard scope of malware.
Consequences for Connected Devices
Wardle’s discoveries also apply to devices connected to a compromised Mac using Muse. An attacker could potentially execute commands such as retrieving an iPhone’s location, scanning for nearby Bluetooth devices, and accessing personal data like contacts and calendars. Conversely, using the assistant for messaging would merely result in draft creation rather than covert message sending.
Meta’s Reaction and Security Protocols
Meta has been marketing Muse as a secure personal assistant, with Mark Zuckerberg emphasizing its round-the-clock capabilities. The company asserts that the system employs isolated execution, least-privilege access, and a dedicated security layer known as Sentinel to oversee connector actions and network egress.
Nevertheless, past incidents like the OpenClaw malware, previously referred to as Clawdbot, have raised alarms regarding AI agents having extensive access to user systems.
Conclusion
Patrick Wardle’s alert regarding Meta’s Muse AI assistant underscores critical security vulnerabilities that could be exploited by malicious actors. The zero-day flaw, “not-a-mused”, highlights the dangers associated with AI applications that enjoy extensive access to system resources. While Meta continues to endorse Muse’s security features, users must stay vigilant and aware of potential risks.