Australia Tech News - Page 12 of 231 - Techbest - Top Tech Reviews In Australia

Aussie Government Targets Social Media Algorithms


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
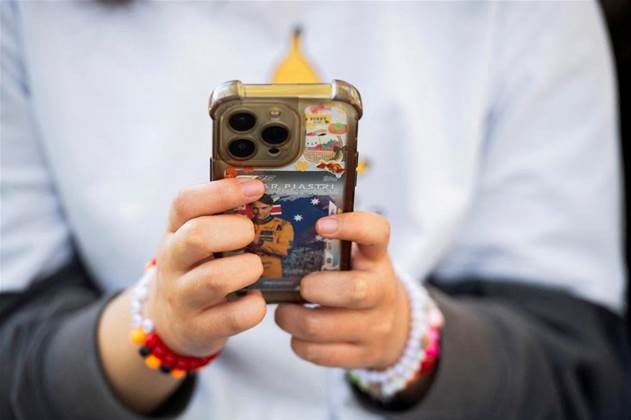
Australia’s Legislative Initiative on Social Media Algorithms

Australia’s Legislative Initiative on Social Media Algorithms

Australia's initiative on content control in social media

Overview

  • Australia will enable users to manage the visibility of content on social media timelines.
  • Proposed regulations would obligate platforms to inform users about content alternatives.
  • Fines could go up to $109.2 million for those not adhering to the rules.
  • This initiative follows the EU’s Digital Services Act but aims for better implementation.
  • Concerns have emerged regarding possible censorship dangers.

The Suggested Legislation

In a groundbreaking step, the Australian government has introduced fresh legislation designed to grant social media users increased authority over the content they encounter. As part of the government’s dedication to bolstering online safety, this initiative will mandate social media platforms to inform users and offer them the ability to customize their content feeds. Users may choose to permit algorithm-generated content or select to view posts solely from the accounts they follow.

Government Objectives and Industry Response

Prime Minister Anthony Albanese has termed the reform as “reasonable, practical, and sensible,” underlining that it empowers users while holding technology corporations accountable. Major companies like Meta Platforms and Google have yet to react, but the legislation mirrors a worldwide trend of enhanced scrutiny regarding algorithmic influence on user actions.

International Context and Comparisons

This legislative initiative parallels the European Union’s Digital Services Act, which allows users to disable content profiling. Despite the EU’s challenging implementation, Australia strives to simplify its method, ensuring user-friendly options for opting out of algorithm-based content.

Implementation and Compliance

The proposed “My Feed, My Way” initiative demands digital platforms to outline their strategies for mitigating risks for Australian users. Non-compliance may incur penalties of up to $109.2 million, mandated by eSafety, the national internet oversight body. eSafety will also possess the authority to demand the prompt removal of harmful materials.

Concerns About Censorship

Although the legislation is designed to empower users, advocates for free speech have raised alarms about potential censorship issues. Prime Minister Albanese assures that the primary focus is on user empowerment, not governmental control.

Future Actions

The government is actively soliciting feedback from stakeholders, including digital platforms, industry groups, and civil society organizations. The draft legislation is expected to be presented to Parliament later this year, representing a crucial advancement in Australia’s digital policy framework.

Conclusion

Australia is making significant strides to grant social media users authority over algorithm-driven content, inspired by European regulatory efforts. While this initiative aims to bolster online safety and user autonomy, it comes under scrutiny regarding potential censorship. The government is engaging in extensive consultations to ensure a fair and effective rollout.
Q&A Section

Q: What is the main objective of the proposed legislation?

A: The primary goal is to provide users control over the content they encounter on social media, enhancing online safety and holding tech companies accountable.

Q: How does this proposal compare to global regulations?

A: It is akin to the EU’s Digital Services Act, which requires platforms to give users the choice to disable content profiling.

Q: What are the potential penalties for non-compliance?

A: Companies could be fined up to $109.2 million, as enforced by the eSafety regulator.

Q: Are there concerns related to this legislation?

A: Advocates for free speech express concerns about possible censorship, but the government focuses on empowering users rather than enforcing control.

US Claims Chinese AI Firms Involved in ‘Nefarious’ Theft of Technology


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

US Claims Against Chinese AI Firms

Overview

  • The US has leveled charges against Chinese AI firms for technology infringement.
  • The distillation method is key to the claims.
  • Six Chinese entities, including Alibaba, are named.
  • These charges could influence future US-China relations.
  • Discussions on AI safety risks are anticipated soon.

Clarification of the Charges

The government of the United States has accused several Chinese AI companies of what it characterizes as ‘malevolent’ technology infringement from American AI entities. This allegation emerges as the leaders of the two major economies prepare to convene, possibly straining diplomatic relations.

US claims Chinese AI firms are replicating technology

Grasping Distillation

US officials claim that the Chinese companies have appropriated intellectual property using a method identified as distillation. This process entails training smaller AI systems with outputs from larger, more expensive models, thereby decreasing the expenses linked to creating new AI technologies.

Companies Involved

Among the six identified firms are DeepSeek, Moonshot AI, and Alibaba. They are charged with utilizing American AI models to hasten the training of their own AI offerings, reportedly with the knowledge of the Chinese government.

Geopolitical Repercussions

The allegations arise as the US administration readies for an encounter with Chinese President Xi Jinping. Both nations are also anticipated to tackle AI safety issues in forthcoming discussions.

Security Issues

US officials contend that these activities not only reduce research and development expenses for Chinese firms but also enhance China’s military and cyber capabilities, creating potential risks for the US and its allies.

Conclusion

The US has accused Chinese AI companies of improperly utilizing American technology, prompting worries regarding the impact on international relations and security. These allegations could influence discussions surrounding AI safety and further exacerbate US-China relations.

Q&A

Q: What does the distillation method entail?

A: Distillation consists of leveraging outputs from larger AI models to develop smaller ones, minimizing development expenses.

Q: Which companies have been accused?

A: Six Chinese firms, including DeepSeek, Moonshot AI, and Alibaba, are under scrutiny.

Q: What could be the consequences for US-China relations?

A: The accusations may complicate impending diplomatic discussions and AI safety talks.

Q: Are there security issues associated with this situation?

A: Yes, US officials indicate these actions may bolster China’s military and cyber capabilities.

Q: What topics will be discussed in the US-China dialogues?

A: The two nations are likely to address AI safety risks in an upcoming forum.

XPENG’s IRON Humanoid Emerges from New Production Line, Mass Production Targeted for 2026


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

XPENG’s Humanoid Innovation: An In-Depth Exploration of IRON

Quick Overview

  • XPENG introduces the first fully automated production line for humanoid robots worldwide.
  • IRON is tailored for use in XPENG stores and campuses, not for immediate sale to consumers.
  • More than 80% of the production process is automated, utilizing quality systems from electric vehicle manufacturing.
  • IRON features 76 degrees of freedom and sophisticated AI capabilities.
  • Mass production is projected for late 2026, with a global launch in 2027.
  • Considerable investment and market strategy position XPENG as a frontrunner in the robotics field.

Transitioning from Prototype to Production

The Chinese electric vehicle company XPENG has garnered attention with the launch of the world’s inaugural automated production line for advanced humanoid robots. Located in Guangzhou, this line signifies a significant transition from prototype lab models to actual manufacturing. During the event on 8 September, the first IRON robot emerged from the line, representing XPENG’s ambitious goal to incorporate these humanoids into their business operations.

XPENG's humanoid robot factory

What Exactly is IRON?

IRON embodies XPENG’s concept of a versatile humanoid robot, greatly exceeding the functions of single-task devices. With 76 degrees of freedom and an AI-centered platform, IRON is engineered to learn and adjust to real-life settings. Its sophisticated design guarantees safety and efficiency, while the incorporation of three Turing AI chips provides considerable computational strength for autonomous functioning.

Timeline and Financial Overview

XPENG has established an ambitious schedule with mass production expected by the end of 2026 and a global release planned for 2027. For Australia, this could mean possible integration into XPENG showrooms following the launch. On the financial front, XPENG has secured upwards of US$900 million in investments, highlighting its determination to lead in the robotics market.

XPENG humanoid robot assembly line

Consequences for Australia

Australia presents a crucial market for XPENG’s IRON, with plans to implement the robots in local showrooms by 2027. While considerations regarding regulations and safety persist, the advent of humanoid robots could transform customer interactions within the automotive industry.

Setting Realistic Expectations

Amidst the enthusiasm, it is important to maintain realistic expectations. Historically, humanoid robots have been known for high promises and lower delivery. XPENG, along with rivals like Tesla, is treading into new territory, and the progress from prototype to practical use will be closely monitored.

XPENG humanoid robot in action

Conclusion

XPENG’s initiation of the IRON robot production line signifies a notable point in the robotics sector. As the company gears up for mass production and global dissemination, attention turns to whether these humanoids can fulfill their promises. For Australia, the potential launch of IRON signifies progression toward the future of retail and customer engagement in the automotive realm.

Q&A

Q: What sets XPENG’s IRON robot apart?

A: IRON is crafted as a multifunctional humanoid robot featuring advanced AI capabilities and 76 degrees of freedom for diverse functionalities.

Q: When will IRON be launched in Australia?

A: XPENG intends to introduce IRON globally in 2027, with Australia being a key target market for incorporation in local showrooms.

Q: How does IRON stack up against Tesla’s robotics initiatives?

A: While both firms aspire to be leaders in humanoid robotics, XPENG prioritizes industrial scalability first, while Tesla focuses on enhancing AI capabilities.

Q: What hurdles does XPENG encounter in rolling out IRON?

A: Significant challenges encompass ensuring safety, navigating regulatory frameworks, and demonstrating the robot’s adaptability and practicality in real-world scenarios.

Sydney’s Mathspace Becomes Target of Delayed Metabase SQL Injection Vulnerability Fixing


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • Cyber adversaries took advantage of a severe Metabase flaw to infiltrate Mathspace after the firm neglected to update its self-hosted setup following an advisory issued on August 7.
  • Compromised information comprises user IDs, usernames, first and last names, email addresses, and additional login-related data for students, staff, parents, and guardians.
  • Only users from Australia and New Zealand were impacted, and Mathspace has reached out to authorities including the Office of the Australian Information Commissioner and the Australian Cyber Security Centre.
Late patching of Metabase SQLi bug claims Sydney's Mathspace

Exploring the Metabase Flaw

A significant vulnerability in the Metabase business intelligence (BI) tool was taken advantage of by unidentified attackers to breach the online mathematics learning service Mathspace. Despite Metabase issuing a security alert on August 7, prompting users to immediately upgrade their self-hosted versions, Mathspace’s founder and chief technology officer (CTO) Alvin Savoy stated that this action was not carried out.

Postponed Action and Its Ramifications

“Our vulnerability notification process failed to identify and escalate that alert for action,” Savoy mentioned. “We managed to update our instance on August 29 after a later Metabase communication drew our attention.” That lag in deploying patches was sufficient for hackers to access Mathspace’s Metabase instance and extract data. Savoy reported that a variety of data was taken, relating to students, staff, as well as parents and guardians. This encompasses user IDs, usernames, first and last names, email addresses, and other login-related details.

Simple to Exploit Critical SQLi Vulnerability

The Metabase vulnerability carries a peak severity rating of 10.0 out of a potential 10, and it is simple to exploit. It enables structured query language (SQL) command injection via the /api/session/reset_password endpoint, granting a remote attacker administrator-level access to the Metabase instance without any credential input. Various Metabase versions ranging from x.58.0 to x.63.0 are affected by this vulnerability.

Global Repercussions of the Vulnerability

Laptop manufacturer Framework, Python data science platform Anaconda, and form creation tool Tally have all acknowledged unauthorized data access stemming from the vulnerability, affecting the cloud-hosted Metabase instances of these three companies. Real-time threat and risk intelligence provider Dataminr reported that in the first week of August, slightly over 4300 publicly accessible hosts were running vulnerable versions of Metabase. It noted that many of these organizations belonged to the government, healthcare, energy, finance, telecom, aviation, and public sectors.

Mathspace’s Actions and Future Safeguards

Savoy stated that Mathspace has alerted affected schools and individuals, as well as authorities like the Office of the Australian Information Commissioner, the Australian Signals Directorate’s Australian Cyber Security Centre, and their counterparts in New Zealand. Founded in Sydney in 2010 by Savoy, Mohamad Jebara, and Chris Velis, Mathspace is used by educational institutions in Australia, New Zealand, the United States, Canada, the United Kingdom, Hong Kong, and India. However, this particular data breach solely impacted users from Australia and New Zealand. Savoy cautioned Mathspace users to be vigilant against messages impersonating the platform, schools, and other familiar organizations, utilizing the stolen data.

Conclusion

The infiltration of Mathspace due to a critical Metabase vulnerability highlights the necessity of prompt security updates and effective vulnerability management. This incident underscores the substantial risks related to delayed patching and the extensive consequences such vulnerabilities may have across various sectors.

Q: What led to the breach at Mathspace?

A: The breach was instigated by a serious Metabase vulnerability that Mathspace did not address in a timely fashion.

Q: What information was compromised in the breach?

A: The compromised information consists of user IDs, usernames, first and last names, email addresses, and other login-related details pertaining to students, staff, parents, and guardians.

Q: Who were the users affected by the breach?

A: The breach affected only users located in Australia and New Zealand.

Q: What actions has Mathspace taken in response to the breach?

A: Mathspace has informed the affected individuals and relevant authorities. They have also advised users to be watchful of messages that impersonate the platform or associated organizations.

Q: What is the severity rating of the Metabase vulnerability?

A: The Metabase vulnerability has a highest severity rating of 10.0 out of 10, signifying it is extremely critical and easy to exploit.

Q: How widespread is the impact of the Metabase vulnerability?

A: The vulnerability has affected a multitude of organizations globally, encompassing those in government, healthcare, energy, finance, telecommunications, aviation, and public sectors.

Hundreds of Obsolete, At-Risk Exchange Servers Remain Throughout Australia


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Main Highlights

  • As of August 31, 382 Exchange servers in Australia and 56 in New Zealand remain exposed to CVE-2026-62911, three weeks post Microsoft’s resolution.
  • Publicly accessible exploit code now exists, with NCSC-NL cautioning that an unauthenticated attacker might gain arbitrary code execution capabilities.
  • ASD is advising entities still operating outdated Exchange versions to take action, or segment their networks if they cannot replace them.
Outdated Exchange servers pose risks in Australia

Vulnerable Exchange Servers: An Increasing Issue

Unpatched and old Microsoft Exchange servers susceptible to a serious authentication bypass flaw are prevalent in Australian and New Zealand networks, endangering organizations’ mailboxes with potential total compromise. Compounding the issue, active exploit code is now available to the public for this vulnerability.

Scope of the Vulnerability

The ShadowsServer Foundation, a nonprofit focused on security monitoring, reported that as of August 31, there are 382 Exchange servers in Australia and 56 in New Zealand left vulnerable to CVE-2026-62911, three weeks after Microsoft provided a fix. The versions affected comprise older Exchange Server 2016, 2019, and Subscription Edition, which complicates the patching situation.

Extended Security Updates

Exchange 2016 and 2019 only receive security updates through Microsoft’s Extended Security Updates (ESU) program now. This indicates that organizations operating those versions are incurring costs for ongoing support on infrastructure they have yet to update or transition to cloud-hosted Exchange.

Exploitation Threats and Alerts

The National Cyber Security Centre of the Netherlands (NCSC-NL) announced on August 28 that exploit code proof-of-concept had surfaced online. NCSC-NL upgraded its alert and cautioned that an unauthenticated attacker might execute arbitrary code.

Microsoft’s Position

Microsoft has yet to validate active exploitation occurring in real-world settings, and the vulnerability does not currently show up in the United States Cybersecurity and Infrastructure Agency’s Known Exploited Vulnerabilities (CISA-KEV) database. The flaw is rated with a CVSS 3.1 score of 8 out of 10, permitting an attacker to capture authentication traffic and replay it to obtain elevated privileges on an Exchange server.

Recommendations from Authorities

The flaw was identified by Orange Tsai from the DEVCORE Research Team during the Pwn2Own Berlin 2026 competition. When queried regarding the vulnerability by TechBest, the Australian Signals Directorate (ASD) urged organizations still using legacy Exchange to respond promptly.

ASD’s Suggestions

“Outdated technology lacking critical security updates and patches is an appealing target for cybercriminals and is more susceptible to attacks,” stated an ASD representative. The directorate further recommended that if legacy systems cannot be updated, organizations should segment their networks to safeguard their most vital systems, according to ASD.

Worldwide Context

ASD continues to provide ongoing guidance on Exchange Server security hardening and end-of-support strategies. On a global scale, as of August 31, 2026, ShadowServer reported 21,899 vulnerable Exchange servers, indicating that slow patching and upgrading is not solely an issue localized to the Oceania region.

Conclusion

Outdated Microsoft Exchange servers throughout Australia and New Zealand still exhibit vulnerability to security threats, despite a fix being offered by Microsoft. The ongoing existence of these servers creates significant security challenges, leading authorities like ASD to issue urgent recommendations for organizations to either upgrade or secure their infrastructures.

Q: What is the issue affecting Exchange servers?

A: The issue is a severe authentication bypass vulnerability termed CVE-2026-62911, enabling unauthenticated attackers to potentially execute arbitrary code on the compromised servers.

Q: How many servers are impacted in Australia and New Zealand?

A: As of August 31, 382 servers are vulnerable in Australia, and 56 in New Zealand.

Q: Which Exchange versions are affected?

A: The versions at risk include Exchange Server 2016, 2019, and Subscription Edition.

Q: What measures should organizations with vulnerable servers take?

A: Organizations should either update or replace these servers or, if unable, segment their networks to safeguard critical systems.

Q: Has Microsoft acknowledged active exploitation of this vulnerability?

A: Currently, Microsoft has not verified any active exploitation in real-world scenarios.

Q: What is the position of the Australian Signals Directorate (ASD)?

A: ASD encourages organizations to promptly address the vulnerability and recommends network segmentation if upgrading is not an option.

Cathay Pacific and Google Partner to Enhance AI Experiments Focused on Minimizing Contrails


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

AI Trials in Aviation: The Partnership Between Cathay Pacific and Google

Quick Summary

  • Cathay Pacific and Google broaden AI trials to decrease contrails.
  • Initial trials achieved a 40% reduction in the warming effects of contrails on selected flights.
  • The second phase of trials will encompass Cathay’s Asian and trans-Pacific routes.
  • Contrails may play a role in one-third of the aviation sector’s climate impact.
  • AI technologies are essential for tackling the environmental issues in aviation.

Transforming Air Travel with AI: The Collaborative Effort of Cathay Pacific and Google

AI Trials in Aviation: The Partnership Between Cathay Pacific and Google

AI-Driven Contrail Mitigation

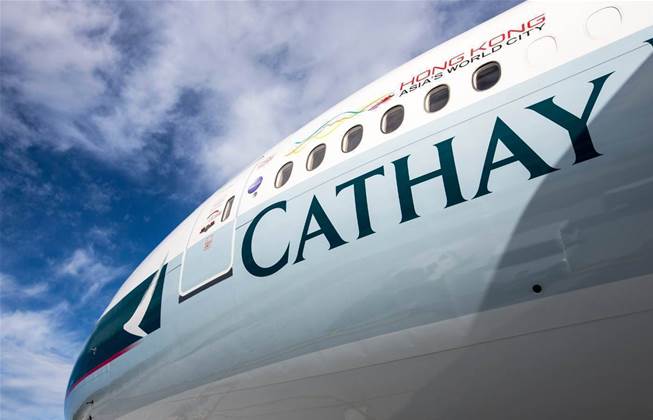
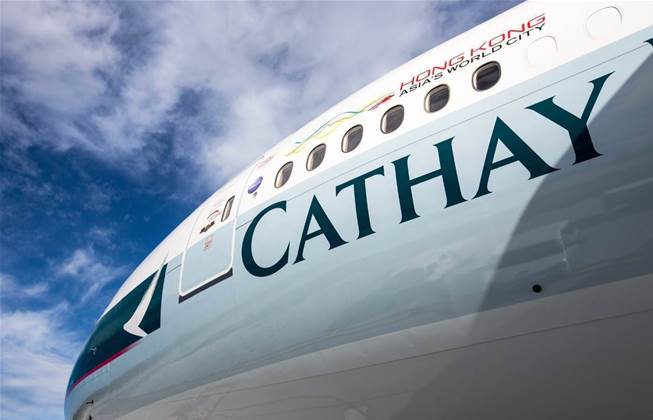
In a pivotal step towards promoting sustainable aviation, Cathay Pacific and Google are pushing forward with AI technology trials aimed at diminishing climate-warming contrails. Initiated in late 2025, these trials utilise Google’s AI-driven forecasting tools to identify areas prone to contrail formation, enabling pilots to modify flight altitudes and lessen their effects.

Notable Initial Outcomes

The first phase of testing saw over 80 Cathay flights achieve an impressive 40% decline in contrail warming effects, signifying a hopeful beginning for this forward-thinking strategy. As the first airline worldwide to test contrail avoidance on ultra-long-haul routes, Cathay Pacific is pioneering efforts in Asia-Pacific with Google’s backing.

Future Phases and Broader Implications

The forthcoming second phase of trials will extend throughout Cathay’s Asian and trans-Pacific network. With persistent contrails potentially making up to one-third of aviation’s climate impact, this partnership is a critical move towards mitigating the industry’s environmental footprint.

AI: A Driver for Change

Lawrence Fong, director of digital and IT at Cathay, highlights AI’s crucial role in hastening the aviation sector’s response to climate change. The collaboration with Google underscores the necessity of innovative approaches in confronting the urgent challenge of global warming.

Conclusion

The partnership between Cathay Pacific and Google focused on reducing contrails via AI technology represents a landmark initiative in sustainable aviation. Successfully lessening the impact of contrails and planning extensive trials illustrate the essential role of AI in tackling climate issues within the aviation sphere.

Q&A

Q: What are contrails and why are they important?

A: Contrails are the slender white lines created by aircraft in cold, moist conditions at high altitudes. Their significance lies in their potential contribution to climate warming, possibly representing up to one-third of the aviation sector’s climate impact.

Q: How does the AI technology work to decrease contrails?

A: The AI technology employs forecasting instruments to detect areas where contrails are likely to form, enabling pilots to alter flight altitudes to avoid these zones, thereby reducing their warming effects.

Q: What were the outcomes of the initial trials?

A: The initial trials resulted in a 40% reduction in contrail warming impact across more than 80 Cathay flights, showcasing the potential effectiveness of this technology.

Q: What will be covered in the second phase of trials?

A: The second phase will broaden to Cathay’s Asian and trans-Pacific routes, aiming to further evaluate and enhance the technology’s efficacy on a larger scale.

Q: Why is Cathay Pacific’s partnership with Google significant?

A: Cathay Pacific is the first airline in the Asia-Pacific region to collaborate with Google for this technology, and this initiative signifies a groundbreaking step in employing AI to confront the environmental challenges faced by aviation.

Europe’s Major Mobile Operators Talk About Satellite-to-Mobile Collaboration


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Deutsche Telekom, Orange, Vodafone, and Telefonica are considering a partnership for satellite-to-mobile services.
  • The group intends to bid for EU satellite spectrum to enable direct mobile services.
  • The EU is set to allocate a considerable amount of satellite spectrum to companies based in Europe.
  • The IRIS² project serves as Europe’s alternative to Starlink.

Formation of the Consortium

Reports indicate that Deutsche Telekom, Orange, Vodafone Group, and Telefonica are in preliminary talks to establish a consortium focused on bidding for satellite spectrum within the European Union. The aim is to provide direct mobile services, based on information from sources with knowledge of the situation. This prospective alliance would seek a portion of the 2GHz frequency range that the EU has suggested should be reserved for local providers. The project aims to enhance Europe’s independent satellite capabilities.

Major European mobile carriers consider a satellite-to-mobile collaboration

Strategic Allocation of Spectrum

In May, it was announced by the European Union that plans are underway to allocate a substantial part of valuable satellite spectrum to European firms, thereby decreasing the portion accessible to U.S. companies. This action is part of a comprehensive initiative to support local enterprises and lessen dependence on major tech companies. The European Commission has earmarked two-thirds of the spectrum within the IRIS² multi-orbit network of 290 satellites for commercial activities, with equal shares assigned to EU and non-EU operators. The envisioned consortium would compete for the EU operator segment.

The Initiative IRIS²

IRIS² is Europe’s tactical response to the SpaceX Starlink project. It is spearheaded by the European Commission and includes a consortium made up of SES SA, Eutelsat, and HispaSat. This initiative is aimed at strengthening Europe’s satellite capabilities and fostering a competitive landscape within the satellite communications industry.

Conclusion

The ongoing discussions among Europe’s leading mobile operators suggest a vigorous move towards enhancing regional satellite capabilities. Should the consortium materialize, it would enable these firms to bid for a segment of the EU satellite spectrum, aligning with the EU’s ambitions to enhance local satellite communication and minimize dependence on non-European technology providers. This development occurs under the broader context of the IRIS² initiative, which seeks to position Europe as a significant player in the global satellite communications sector.

Q: What is the main aim of the envisioned consortium?

A: Its primary aim is to bid for EU satellite spectrum to facilitate direct mobile services.

Q: What is the reason for the EU allocating more spectrum to European firms?

A: The EU intends to support local businesses and lessen reliance on major tech firms by granting more spectrum to European enterprises.

Q: What does IRIS² signify?

A: IRIS² is an initiative led by the European Commission, involving a consortium of SES SA, Eutelsat, and HispaSat, aimed at improving Europe’s satellite communication capabilities as a response to Starlink.

Q: Are any definitive decisions made regarding the consortium?

A: Currently, no final decisions regarding the establishment of the consortium or its bidding plans have been confirmed.

Q: How is the satellite spectrum allocated according to the EU’s strategy?

A: The satellite spectrum on the IRIS² array is distributed equally between EU and non-EU operators for commercial utilization.

Victoria Police introduces a digital platform for community-driven retrieval of stolen vehicles


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Victoria Police Unveils Stolen Vehicle Verification Portal

Quick Overview

  • Victoria Police introduces an online resource for verifying stolen vehicles in Victoria.
  • This resource permits searches by registration number, make, or model.
  • Real-time data from Victoria Police’s system guarantees accuracy.
  • Street parking constitutes a primary target for automotive thefts in Victoria.
  • The community can aid in vehicle recovery by reporting suspicious observations.
  • This resource should not replace a PPSR check when purchasing pre-owned vehicles.

Overview

Victoria Police has launched a groundbreaking online resource aimed at empowering the public in combating vehicle theft. The Stolen Vehicle Verification portal allows anyone with internet access to check if a vehicle is reported stolen in Victoria, using either the registration number or vehicle make and model.

How the Online Verification Tool Operates

The Stolen Vehicle Verification portal is designed for ease of use and does not require any registrations or app installations. Just input a vehicle’s registration number or search by make and model to discover if it has been reported as stolen. The information is derived from the Victoria Police Law Enforcement Assistance Program, VicRoads, and the National Exchange of Vehicle and Driver Information System, ensuring real-time information.

Smart Functionality: Search by Make and Model

The make and model search addresses a prevalent tactic employed by thieves who change licence plates. This functionality enables users to identify stolen vehicles even if the plates have been altered, providing crucial information that can be forwarded to the authorities.

Street Parking: A Major Target for Theft

Recent data indicates that a substantial number of vehicle thefts occur from street parking. Contemporary vehicles featuring keyless ignition systems are particularly susceptible to theft methods that evade electronic immobilisers. The goal of this tool is to lower these statistics by engaging the community in observing and reporting suspicious behavior.

Victoria Police's online resource for recovering stolen vehicles

Preventing Keyless Vehicle Thefts

With the majority of stolen vehicles ultimately being recovered, Victoria Police recommends implementing physical deterrents such as steering wheel locks, OBD port locks, and secure handling of key fobs. Regularly locking vehicles, even for brief stops, is also advisable.

Not a Substitute for a PPSR Check

Although the resource is efficient for recovery, it is not meant for verifying used vehicle purchases. Buyers should still conduct a PPSR check through the Personal Property Securities Register to confirm a vehicle’s history is free from theft, write-offs, and financial claims.

Reporting a Stolen Vehicle

If a vehicle is listed in the database as stolen, do not confront anyone. Instead, report the vehicle’s location to the Police Assistance Line or anonymously through Crime Stoppers. For ongoing thefts, contact emergency services immediately.

Conclusion

The Stolen Vehicle Verification portal from Victoria Police marks a significant initiative in engaging the public in crime prevention efforts. By providing straightforward access to stolen vehicle information, the resource promotes community safety and aids in recovering stolen automobiles. This initiative exemplifies the practical use of technology in public service, fostering collaboration between law enforcement and the public.

Q: How do I access the Stolen Vehicle Verification portal?

A: The portal is accessible via the Victoria Police website without necessitating an account or app download.

Q: What information do I need to determine if a vehicle is stolen?

A: You can perform a search using the vehicle’s registration number or by make and model.

Q: Can this tool serve as a replacement for a PPSR check when buying used vehicles?

A: No, the tool is not a replacement for a PPSR check, which offers detailed vehicle history.

Q: What should I do if I locate a stolen vehicle?

A: Avoid approaching the vehicle. Report its location to the Police Assistance Line or Crime Stoppers. In emergencies, dial Triple Zero (000).

Q: Are modern vehicles especially at risk for theft?

A: Yes, vehicles equipped with keyless ignition systems are frequently targeted using sophisticated theft methods.

Executive Retreat: Edition for Security Leaders – Victoria


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Executive Retreat: Security Leaders Edition – Victoria

Quick Overview

  • Exclusive gathering for top technology and security professionals.
  • The event features leadership dialogues and networking opportunities.
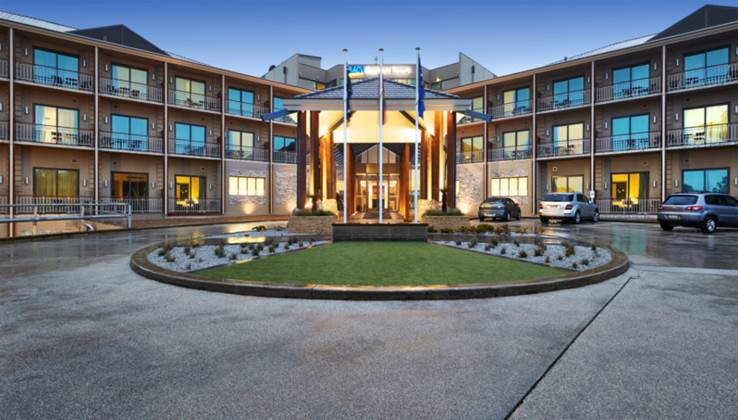
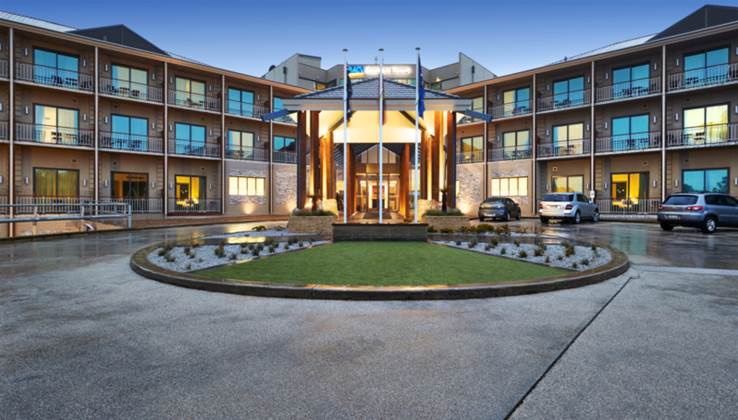
  • Conducted at RACV Goldfields Resort, Creswick, Victoria.
  • Emphasis on promoting executive wellness and preventing burnout.
  • Chance to cultivate enduring relationships in a comfortable atmosphere.
  • Participation is capped for a tailored experience.

Transformational Leadership Journey

Security leaders encounter distinct challenges in the current rapid technological environment. Juggling risk management, team guidance, and emerging threats leaves scant time for self-reflection. This November, the Executive Retreat offers a unique opportunity for leaders to retreat and connect with peers in a tranquil setting.

Tailored Agenda for Security Leaders

Aimed at surpassing conventional conferences, this retreat encourages genuine dialogue. Sessions will explore crucial topics such as leading intricate security teams, cultivating resilient cultures, and prioritizing executive wellness. Attendees will also exchange practical experiences and forge trustworthy, lasting relationships.

Executive Retreat for Security Leaders in Victoria

Beyond Simple Networking

The retreat offers more than just simple networking. Attendees will indulge in exquisite dining and local experiences, ranging from VIP luncheons to evening events. This laid-back environment fosters authentic interactions that are frequently absent in standard event formats.

Exclusive and Personal Environment

With a capped attendance, every participant can engage fully, contributing to discussions and building meaningful connections. This retreat is perfect for leaders who want to take a pause, gather fresh insights, and engage with peers encountering similar challenges in the security field.

Conclusion

The Executive Retreat: Security Leaders Edition at RACV Goldfields Resort provides a unique chance for senior executives to reflect, connect, and recharge. By merging leadership sessions with informal networking events, participants can look forward to departing with new insights and lasting connections.

FAQs

Q: Who is encouraged to attend the Executive Retreat?

A: Senior technology and security leaders aiming to network with peers and gain new leadership perspectives should consider joining.

Q: What is the primary focus of the retreat?

A: The retreat centers on leadership development, peer networking, and nurturing executive wellness in a relaxed atmosphere.

Q: When and where is the retreat scheduled?

A: The retreat is set for 26–27 November at the RACV Goldfields Resort in Creswick, Victoria.

Q: In what ways does this retreat differ from typical conferences?

A: Unlike typical conferences, this retreat offers a relaxed setting conducive to meaningful discussions and relationship development.

Q: Why is participant attendance limited?

A: Limiting attendance guarantees a customized experience, allowing each participant to engage and form valuable connections.

People First Bank Enhances Its Technology Infrastructure Upgrading Initiatives


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • People First Bank is progressing with its technology stack overhaul, aiming for completion by late 2027.
  • A core banking platform from Fiserv and a digital banking application powered by Backbase are crucial elements.
  • The transition of Heritage Bank accounts to the updated system is projected for late 2027.
  • A new comprehensive lending platform is set to launch soon, enhancing the customer experience.
  • The modernisation seeks a straightforward, cloud-driven, and sustainable tech stack.
People First Bank advances its technology stack modernisation

Updating the Tech Stack

People First Bank is on the verge of finalising a comprehensive upgrade of its technology stack, following the merger between People’s Choice and Heritage Bank. This undertaking, expected to be completed by late 2027, will involve the introduction of a Fiserv core banking platform, a fresh digital banking app powered by Backbase, and improved customer service systems integrated with Salesforce and Vonage.

Account Transition and New Solutions

The bank’s brand launched in May, representing a major achievement in its change initiative. Importantly, a new all-encompassing lending platform is about to go live, enhancing experiences for clients, brokers, and employees. The complete transition of Heritage Bank accounts to the new core banking system is projected for late 2027.

Comparisons with Larger Financial Institutions

Andy Weir, Chief Technology and Transformation Officer, sees similarities between the modernisation efforts at People First Bank and those of larger entities such as Westpac. He underscores a common aim of building a simple, modern, cloud-enabled, and sustainable technology stack.

Designing the New Stack

Weir’s responsibilities began just prior to the merger, and he played a crucial role in establishing the targeted technology state. He confirmed that 98% of the necessary tech decisions were secured before the merger. The strategy emphasizes simplicity, digital empowerment, and social accountability.

Pillars of Strategy and Clarity

The bank strives to provide a seamless customer experience by steering clear of unnecessarily complex features in its services. The recently launched digital banking platform, which has garnered high praise, illustrates this commitment to clarity.

Digital Empowerment and Safety

Security and robustness are paramount, with minimal customisation to ease upgrades and AI incorporation. The tech stack is crafted to lessen customer effort by reducing the need for phone calls and branch visits, while boosting safety through mechanisms like verified messaging and fraud prevention integration.

Conclusion

People First Bank is making notable progress in updating its technology stack, aiming for a 2027 completion date. This initiative encompasses a new core banking system, digital solutions, and advancements in customer service. The bank’s methodology aligns with those of larger counterparts, emphasizing simplicity, cloud functionalities, and safety.

Q: What are the key elements of People First Bank’s new technology stack?

A: The key elements consist of a Fiserv core banking platform, a Backbase-powered digital banking application, a new end-to-end lending platform, and upgraded customer service systems that utilize Salesforce and Vonage.

Q: When is the transition of Heritage Bank accounts anticipated to finish?

A: The transition of Heritage Bank accounts to the People First Bank core banking system is scheduled for completion by late 2027.

Q: How does People First Bank’s modernisation relate to larger banks?

A: The modernisation of People First Bank’s tech stack reflects the initiatives of larger banks like Westpac, striving for a straightforward, modern, cloud-based, and sustainable stack.

Q: What strategic principles guide the bank’s technology evolution?

A: The evolution is steered by three strategic principles: simplicity, digital empowerment, and social responsibility.

Q: How does People First Bank maintain the clarity of its digital banking application?

A: The bank refrains from complicating its services and is committed to delivering the most appreciated features for customers in a seamless fashion.

Q: What actions are being undertaken to improve security and reliability?

A: The bank is minimizing customisation to enable smoother upgrades and AI integration, with the goal of establishing a resilient, safe, and secure platform.