Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 23 of 187

Brookfield Maze Energizes: Fresh EV Charging Station for Travelers


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Quick Read

  • A new Delta AC Max EV charger has been installed at Brookfield Maze.
  • This charger facilitates up to 22 kW of AC charging via a Type 2 connector.
  • Charging is priced at A$0.40 per kWh, providing convenience for visitors.
  • The charger is featured on PlugShare, broadening EV charging options in the region.
  • Destination charging promotes regional tourism and enhances road trip adventures.

EV Charging Grows at Brookfield Maze

Weekend road trips are a classic Aussie pastime. Recently, Brookfield Maze has emerged as a prominent stop for EV drivers, thanks to its newly installed Delta AC Max charger, which provides a handy charging solution for those exploring the picturesque landscapes of Victoria.

Finding the Charger at the Maze

Situated next to the maze, the Delta AC Max is an elegant, wall-mounted model that integrates well with its surroundings. It supports both single-phase and three-phase power systems, delivering up to 22 kW of AC charging, depending on the electrical configuration of the site. The charger comes with a 5-metre Type 2 connector cable, making it a user-friendly choice for road trippers who wish to avoid carrying their own charging cords.

The Charging Session and Payment Dilemma

While their EVs charge, visitors can take in the attractions at Brookfield Maze. At A$0.40 per kWh, the price is slightly higher than the average for a Level 2 charger but justified by its convenience. However, determining the total charging cost was challenging due to insufficient information from the vehicle’s display and the charger’s interface.

Addressing the Calculation on Site

Without a simple method to assess the kWh consumed, an agreement was reached for a fee of A$10 for the charging session. Subsequent evaluations revealed the actual amount should have been A$8.04, underscoring the necessity for improved billing systems in future setups.

The Importance of Regional Destination Charging

The installation of the charger at Brookfield Maze enhances the regional EV charging landscape, providing an essential service for travelers venturing beyond city limits. As more tourism providers adopt this kind of infrastructure, EV drivers will gain the confidence to explore further, assured of dependable charging solutions during their travels.

Conclusion

The introduction of EV charging services at Brookfield Maze exemplifies the increasing trend of regional spots improving visitor experiences through sustainable infrastructure. Although some operational hurdles persist, the overall influence on regional tourism and the feasibility of EV road trips is considerable.
Q&A Section

Q: What type of charger is available at Brookfield Maze?

A: The charger installed is the Delta AC Max, providing up to 22 kW of AC charging.

Q: What is the cost of charging an EV at Brookfield Maze?

A: The charging fee is A$0.40 per kWh.

Q: Is the charger easy to locate and operate?

A: Yes, it is conveniently positioned near the maze and includes a 5-metre tethered Type 2 cable.

Q: How does this addition support regional tourism?

A: It incentivizes EV drivers to discover regional attractions while enhancing local tourism through critical charging infrastructure.

Q: Are there any issues associated with the current setup?

A: Yes, there can be complications in determining total kWh utilized and billing processes due to insufficient data, though improvements are anticipated with future updates.

Arch Linux Halts Package Adoptions Due to Increase in Malware Hijacking


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Arch Linux Suspends Package Adoption Due to Security Risks

Quick Overview

  • Arch Linux has halted package adoptions on AUR due to security issues.
  • More than 1500 packages were affected in a recent security event dubbed “Atomic Arch.”
  • The Australian Cyber Security Centre alerts to rising threats against code repositories.
  • Arch Linux is extensively utilized and serves as the groundwork for other platforms like Valve’s SteamOS.

Arch Linux Pauses Package Adoptions Due to Security Issues

Arch Linux has momentarily stopped package adoptions on the Arch User Repository (AUR) after a spike in harmful code injections. This decision came as a response to attackers leveraging the feature to insert malicious code via later commits.

Arch Linux halts AUR package adoptions in light of malware threats

Robin Candau, part of the Arch Linux DevOps team, has urged the community to stay alert and report any suspicious activities. This marks the third security incident impacting the AUR since June.

Recent Security Issues

The “Atomic Arch” initiative conducted by Sonatype researchers led to the compromise of over 1500 packages. Attackers took advantage of abandoned listings to insert a credential-stealing payload through a malicious npm dependency. Moreover, in mid-June, over 70 packages were modified to include Russian-language spam and inappropriate content in users’ shell configuration files.

Exploitation of Package Adoption Mechanism

In Arch Linux’s package framework, any registered AUR user can take over a package once its original maintainer has left it. This system was misused by attackers, impacting at least 27 packages. The affected packages included names such as “archutil,” “boringssl-git,” and “icloudpd,” hiding malicious ELF binaries under common names.

Alerts from the Australian Cyber Security Centre

The Australian Cyber Security Centre (ACSC) has issued alerts regarding the escalating threat to online code repositories. ACSC highlighted the significant and ongoing risks that the compromise of trusted software packages poses to institutions.

Arch Linux: A Favored Choice

Arch Linux is celebrated for its minimalist and open-source characteristics, serving as the backbone for systems such as Valve’s SteamOS. Its popularity positions it as a prime target for supply-chain attacks, highlighting the necessity for improved security measures.

Conclusion

The choice of Arch Linux to pause package adoptions on AUR underscores the persistent security challenges that open-source platforms face. With recent incidents impacting thousands of packages, the urgency for vigilance and robust security protocols has never been more significant. The alerts from the Australian Cyber Security Centre further emphasize the need to protect code repositories against ever-evolving threats.

Q&A Section

Q: What caused the halt of package adoptions on AUR?

A: The halt was prompted by a notable rise in harmful code injections through the package adoption feature, affecting AUR’s security.

Q: How did the “Atomic Arch” initiative compromise packages?

A: Attackers took over orphaned packages to insert a credential-stealing payload through a malicious npm dependency, compromising over 1500 packages.

Q: What precautions should developers take to ensure security on AUR?

A: Developers should maintain vigilance, report any suspicious activities, and adhere to best practices for securing code repositories to reduce risks.

Q: Why is Arch Linux susceptible to supply-chain attacks?

A: The popularity and open-source nature of Arch Linux render it a lucrative target for attackers intending to exploit its package adoption feature.

Q: How does the ACSC’s warning affect organizations utilizing Arch Linux?

A: The ACSC’s warning underscores the necessity for organizations to implement strict security measures to defend against the growing threat of supply-chain attacks.

Okta Introduces ‘Work Panel’, a Novel SaaS Solution Designed for Vishing Activities


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Transforming Vishing Operations: Okta’s Work Panel

Quick Read

  • Okta announces Work Panel, a SaaS platform aimed at voice-phishing activities.
  • Automates the processes of domain registration, brand duplication, and website hosting.
  • Employs AI for quick setup and upkeep.
  • Enables real-time surveillance of phishing targets.
  • Features include secret rotation and a “self-destruct” functionality.
  • Abused by groups such as Scattered Spider and Scattered Lapsus$ Hunters.

Enhancing Vishing with Work Panel

Identity provider Okta has launched an innovative SaaS platform, the Work Panel, tailored to optimize voice-phishing operations. This latest offering provides cybercriminals with an extensive dashboard that automates functions like domain registration, brand duplication, and website hosting. Aiming at customers from leading identity providers such as Okta, Microsoft 365, and Salesforce, the software improves the efficiency and effectiveness of executing vishing strategies.

The Functionality of Work Panel

Okta unveils Work Panel, a new SaaS for vishing tasks

The Work Panel, as described by Okta Threat Intelligence analyst Moussa Diallo, delivers a set of functionalities similar to a CRM system designed for vishing teams. The platform is thought to be significantly AI-driven, enabling rapid deployment and ongoing support by a single operator. It features three role access for team management, callers, and administrators, offering an exhaustive overview of phishing activities.

Key Features and Capabilities

Work Panel includes numerous advanced characteristics, such as specialized workflows, audit logging, and a “self-destruct” capability to swiftly conclude operations. It utilizes Cloudflare for DNS management, NiceNIC for domain acquisitions, and a Caddy web server functioning as a reverse proxy, while Bunny CDN handles email click tracking. Integration with RocketReach provides access to contact information, including names, phone numbers, and LinkedIn profiles of targeted companies.

Instantaneous Target Surveillance

A notable aspect of Work Panel is its ability to monitor targets in real-time. As targets enter passwords or approve MFA requests on phishing sites, the information is directed to a manager’s session queue. Administrators can monitor and assist targets through phishing transactions, capturing sensitive data such as usernames, passwords, and MFA tokens. This data is then quickly sent to managers via a Telegram bot.

Impact on the Industry and Reactions

Although Okta has not revealed how Work Panel was acquired, it has notified legitimate feature misuse to Cloudflare and other service providers. Vishing, employed by groups like Scattered Spider and Scattered Lapsus$ Hunters, has shown to be extremely effective, leading to substantial breaches, including a 2025 incident involving Qantas that exposed over five million customer records.

Conclusion

Okta’s Work Panel signifies a crucial advancement in the tools designed for executing voice-phishing operations, automating various manual tasks while providing real-time monitoring features. While its introduction raises security alarms, initiatives are being implemented to address its potential misuse.

Q: What is Okta’s Work Panel?

A: Work Panel is a SaaS platform engineered to optimize and automate processes essential for voice-phishing operations.

Q: How does Work Panel improve vishing operations?

A: It automates infrastructure tasks, provides real-time target monitoring, and features like secret rotation and a “self-destruct” button.

Q: Who can access Work Panel?

A: The platform is aimed at cybercriminals engaging in vishing operations, offering various access roles for management, callers, and administrators.

Q: How does Work Panel impact Australian businesses?

A: Australian companies may be targeted in vishing campaigns utilizing Work Panel, posing risks of data breaches and financial losses.

Q: What measures are in place to prevent the misuse of Work Panel?

A: Okta has reported the misuse to service providers like Cloudflare and is actively working to minimize the platform’s exploitation.

Q: Can Work Panel serve legitimate purposes?

A: No, Work Panel is strictly intended for unlawful vishing operations aimed at compromising sensitive data from businesses and individuals.

Runner World Redesign Review: A Better Daily Read for Active Runners


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Runner World’s redesigned site pairs source-labelled running news with evidence-aware guides, clearer navigation and an excellent mobile reading experience.

Musk’s X Argues Australia’s Social Media Ban Enforcement Breaches International Law


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Musk’s X Critiques Australia’s Social Media Legislation

Brief Overview

  • X contests Australia’s social media restrictions on teens, citing violations of international law.
  • The legislation intends to limit social media access for individuals under 16.
  • X asserts that the law compromises privacy and due process.
  • eSafety Commissioner requests enhanced enforcement authority to guarantee adherence.
  • A US congressional committee is worried about implications for free speech in America.

Innovative Social Media Legislation in Australia

In December, Australia implemented a pioneering law that bans social media accounts for users below 16 years old. This regulation has faced criticism mainly from American social media entities, including Elon Musk’s X.

Musk's X challenges Australia’s social media legislation, claiming it breaches international laws

X’s Opposition to Overreach

X, overseen by its parent organization SpaceX, argues that the suggested amendments are at odds with international legal standards by endowing the eSafety Commissioner with excessive rights to document discovery and potentially increasing penalties to $99 million.

The modifications could force foreign companies to yield information, raising issues regarding international comity—deference to the legal frameworks of other nations.

International Consequences and Free Speech Worries

A US congressional committee has indicated worries about the law’s effects on free speech in America, leading to a request for the eSafety Commissioner to provide testimony.

Musk labeled the legislation a possible “backdoor” approach for greater internet control within Australia, intensifying the geopolitical aspect of the conversation.

Enforcement Difficulties

Notwithstanding the law, a considerable number of Australian minors under 16 continue to use social media. The eSafety Commissioner is gearing up for enforcement actions against numerous platforms but faces restrictions due to limited authority.

The regulator emphasized the difficulties of depending on platforms’ self-disclosed compliance and the lack of ability to mandate documentation from third-party age verification services.

Industry Reactions and Next Steps

DIGI, a sector association, claimed that the powers of eSafety have not been fully utilized. Companies such as Google’s YouTube and TikTok admitted the complexities of accurately filtering out underage users.

The Australian Parliament has yet to reach a conclusion regarding the proposed enhancements to enforcement powers, with findings from the senate committee due by August 25.

Conclusion

Australia’s social media regulation targeting users under 16 is at the heart of an international discourse, with Musk’s X challenging the law’s consequences for privacy, international legality, and free expression. As the Australian government strives to enhance regulatory authority, global tech industry players and international lawmakers are closely monitoring the evolving situation.

Q: What position does Elon Musk’s X hold regarding the Australian social media law?

A: X asserts that the law bestows excessive authority to the eSafety Commissioner, violating international legal standards and privacy rights.

Q: What prompts the involvement of the US congressional committee?

A: The committee is worried about the law’s ramifications on free speech in America and has requested the eSafety Commissioner to provide testimony.

Q: What obstacles does the eSafety Commissioner encounter when enforcing the law?

A: The Commissioner faces challenges due to limited authority to enforce document production and must rely on self-reported compliance from platforms.

Q: What is the current situation regarding the enforcement of the law?

A: In spite of the law, numerous minors under 16 remain active on social media. The eSafety Commissioner is preparing enforcement actions but is pending enhanced powers from Parliament.

Q: How have industry organizations responded to the law?

A: DIGI and platforms such as Google’s YouTube and TikTok have recognized enforcement difficulties and requested clarity regarding the extent of eSafety’s authority.

Optus Appears in Court Once More Regarding 2025’s 13-Hour Service Disruption


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Optus Returns to Court Due to 2025’s 13-Hour Outage – TechBest

Quick Overview

  • Optus is in Federal Court concerning a 13-hour network disruption in 2025.
  • This disruption impacted emergency triple zero call services.
  • The Australian Communications and Media Authority (ACMA) is taking action in the matter.
  • If found at fault, Optus may incur financial penalties.
  • Past events have led to substantial fines for the telecommunications company.

Context of the 2025 Disruption Incident

The major Australian telecom company Optus is facing scrutiny once more due to a notable network outage in September 2025. This 13-hour interruption, caused by a firewall upgrade, severely impacted emergency triple zero call connectivity. The inability to connect these calls has been sadly linked to two fatalities, raising grave concerns regarding the dependability of emergency communication in Australia.

Optus' 13-hour outage in 2025 brings it back to court

ACMA’s Lawsuit Against Optus

The Australian Communications and Media Authority (ACMA) has filed a lawsuit against Optus in Federal Court. The regulatory body accuses the telecommunications provider of failing to fulfill its responsibilities to guarantee customer access to emergency call services. It is claimed that during the outage, emergency calls were not connected to their designated endpoints on 1005 occasions, raising serious public safety concerns.

Optus’ Reaction and Prior Incidents

Although Optus has recognized the legal action, they have chosen not to elaborate further on the ongoing proceedings. The company asserts its commitment to enhancing network robustness and has been investing resources to fortify its systems. This incident is not unprecedented, as a comparable outage in November 2023, stemming from a router preset issue, also compromised emergency services, resulting in a $12 million penalty for Optus.

Consequences and Possible Fines

ACMA has emphasized the frequent occurrence of these outages as a significant concern, particularly in light of the recent 2023 incident. The potential maximum fine in the current proceedings may reach $250,000 for each breach. This case highlights the critical importance of dependable emergency call services and the obligations of telecommunications companies to maintain public safety.

Conclusion

Optus is facing legal challenges following a major network outage in 2025 that impacted emergency call services. The ACMA is pursuing court proceedings, underlining worries over recurrent failures in Optus’ systems. As the legal process advances, the emphasis remains on securing the dependability and safety of the telecommunications infrastructure in Australia.

Q&A Section

Q: What led to the 2025 Optus outage?

A: The outage was triggered by a firewall upgrade affecting network services.

Q: How many emergency calls were compromised during the outage?

A: It is reported that 1005 emergency calls were unable to connect to their intended endpoints.

Q: What penalties might Optus face if found liable?

A: Optus could incur financial penalties up to $250,000 for each infringement.

Q: Has Optus had similar problems previously?

A: Yes, a comparable issue occurred in November 2023, resulting in a fine of $12 million.

Q: What actions has Optus taken to resolve these matters?

A: Optus claims to be investing in enhancing network resilience and reinforcing its systems and processes.

Q: Who is spearheading the legal action against Optus?

A: The Australian Communications and Media Authority (ACMA) is pursuing the case in Federal Court.

Unyielding Investigator Challenges Microsoft’s Efforts to Halt Copilot for Word Worm


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • A Norwegian data scientist unveils weaknesses in Microsoft’s AI tool, Copilot for Word.
  • Challenges from prompt injection attacks persist, with a self-replicating worm enduring through numerous patches.
  • Microsoft’s attempts to fix vulnerabilities have been undermined by altered prompts and model enhancements.
  • Researcher Håkon Måløy recommends considering all external documents as untrustworthy.
  • Earlier vulnerabilities identified in Copilot were linked to web pages and Outlook functionality.

Insights into the Copilot for Word Worm

Tenacious researcher reveals Copilot for Word worm

Håkon Måløy, a data scientist from Norway, has showcased how prompt injection attacks can be used against Microsoft’s Copilot for Word. Through cross-domain prompt injection, Måløy illustrated that a single Word document could trigger infection in others by embedding concealed commands within AI-generated text.

Techniques for Prompt Injection

By employing cross-domain prompt injection (XPIA), Måløy demonstrated that concealed natural language commands could transmit through Copilot’s AI systems. These commands, hidden from human perception, are recognized by the AI model, facilitating the infection’s spread without needing the original harmful document.

Spread and Consequences

Måløy’s proof-of-concept illustrated Copilot’s capability to disseminate prompt injections by transcribing concealed commands into fresh documents. This self-replicating process allows harmful commands to persist even after the original document is removed, presenting considerable security threats.

Microsoft’s Actions and Issues

Patch Trials and Evasion

Microsoft is actively engaged in remedying these vulnerabilities. Despite numerous updates and the launch of new AI models, Måløy has effectively navigated these patches using rephrased prompts, underscoring the enduring nature of the threat.

Additional Vulnerabilities

Alongside the Copilot for Word worm, Måløy has pinpointed issues in Copilot’s interactions with web pages and Outlook. These encompass unwanted memory retention and alteration of email content, highlighting the urgent necessity for solid security measures.

Tackling the Vulnerability

User Recommendations

As Microsoft continues to tackle these challenges, Måløy advises users to exercise caution with external documents. By validating source materials and examining AI-generated outputs, users can diminish some of the dangers linked to prompt injection vulnerabilities.

Microsoft’s Ongoing Initiatives

Microsoft’s partnership with researchers such as Måløy emphasizes their dedication to confronting AI security issues. Nevertheless, the complexity of prompt injection attacks means that effective solutions will require constant improvements in AI model capabilities.

Conclusion

The revelations by Håkon Måløy act as an important alert for both software developers and users dependent on AI assistants. With prompt injection attacks proving resistant to patches, it is evident that more advanced security measures are crucial to combat these developing threats.

Q&A Section

Q: What constitutes a prompt injection attack?

A: A prompt injection attack involves the insertion of concealed commands into natural language text, misleading AI models into performing unintended actions.

Q: How does the Copilot for Word worm spread?

A: The worm spreads by embedding hidden prompts in documents, which the AI then replicates into new documents, thus distributing the infection.

Q: What actions has Microsoft taken to address these vulnerabilities?

A: Microsoft has rolled out patches and updated AI models, but these efforts have been bypassed by reworded prompts and new model iterations.

Q: Are there additional vulnerabilities associated with Copilot?

A: Yes, other vulnerabilities include issues with memory retention and the manipulation of email content via Outlook Copilot integrations.

Q: How can users safeguard against prompt injection attacks?

A: Users should regard external documents as untrustworthy, verify source materials, and assess AI-generated content prior to usage.

Google Launches Gemini Spark in Australia to Oversee Your Digital Responsibilities at Night


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Gemini Spark: Revolutionizing Digital Task Management in Australia

Quick Overview

  • Google introduces Gemini Spark in Australia, shifting AI from reactive to proactive approaches.
  • Integrated smoothly with Google Workspace, removing the necessity for third-party applications.
  • Automates responsibilities such as planning travel itineraries and managing subscriptions.
  • Facilitates personalized AI skills adapted to individual writing preferences.
  • Incorporates robust privacy safeguards and human oversight.
  • Accessible to Google AI Pro and Ultra subscribers in Australia.

The Transition from Chatbots to Continuous Agents

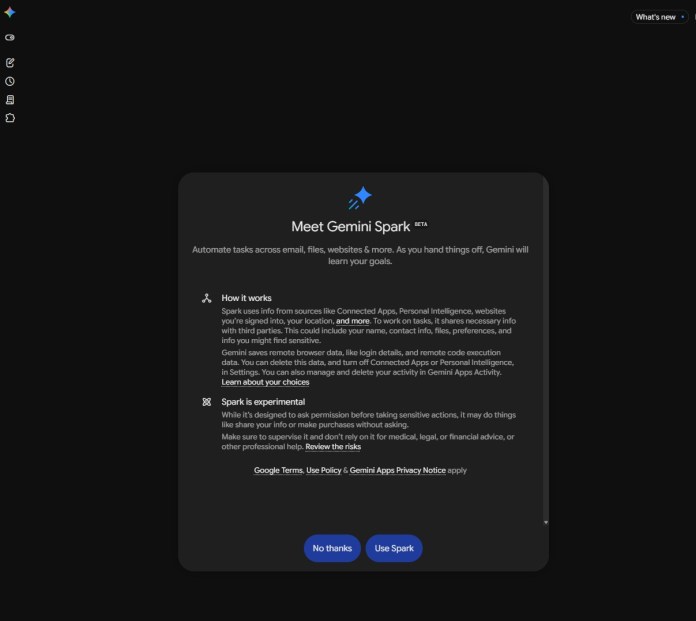
Google Australia is transforming digital task management with the launch of Gemini Spark. In contrast to conventional chatbots, Spark functions as a proactive digital assistant, effortlessly managing multi-step tasks in the background.

Google's Gemini Spark overseeing tasks in Australia

Integrated Workspace Without Complicated Setups

Gemini Spark connects directly with Google Workspace, utilizing Gmail, Google Docs, Google Sheets, and Google Calendar, thereby eliminating the need for third-party tools and ensuring the protection of data.

Automatically Compiling Travel Itineraries in the Background

Spark can compile travel itineraries automatically by scanning emails for confirmations and proposing activities based on your calendar openings.

Identifying Hidden Subscription Price Hikes

Spark’s financial auditing feature aids in detecting changes in subscription prices, notifying users of possible increases and allowing straightforward cancellations if necessary.

Gemini Spark tracking subscription prices in Australia

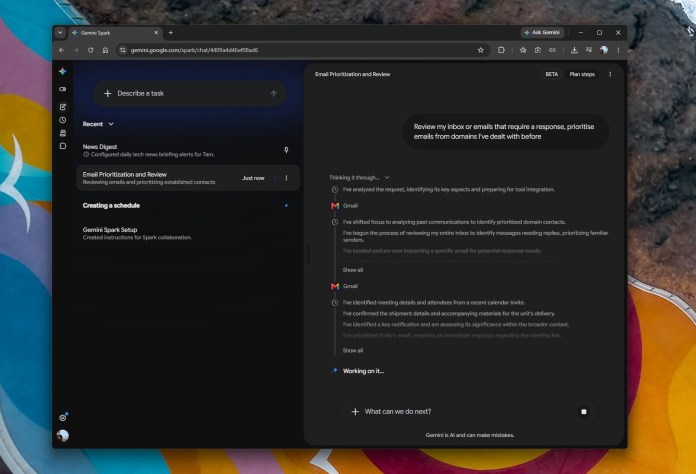
Automated Management of Inbox for Busy Professionals

For busy professionals, Spark automates the generation of responses to customer queries, aligning them with service options and preparing them as drafts for review.

Gemini Spark automating inbox management in Australia

Creating Custom AI Skills Reflective of Your Writing Style

Spark enables users to develop custom AI skills that mirror their personal communication style, ensuring the AI-generated material resonates with their distinct voice.

Security Measures and Human Control

Focusing on privacy and security, Spark incorporates user confirmation checkpoints for sensitive actions, empowering users to control their data.

The Impact of Background Execution on Productivity

Gemini Spark’s capability to operate asynchronously boosts productivity by managing routine tasks while users concentrate on more vital duties.

Details on Pricing and Availability in Australia

Gemini Spark is being rolled out to Google AI Pro and Ultra subscribers in Australia. Available in English on both desktop and mobile, users will find it seamlessly incorporated into their current accounts.

For additional details, visit Google Australia.

Conclusion

Gemini Spark signifies a major leap in AI technology, providing proactive task management through flawless integration with Google Workspace. From itinerary handling to subscription monitoring, Spark establishes a new benchmark for digital assistants in Australia.

Q: What is Gemini Spark?

A: Gemini Spark is Google’s latest AI tool designed to proactively manage digital tasks by integrating with Google Workspace.

Q: How does Gemini Spark integrate with Google Workspace?

A: It seamlessly integrates with Gmail, Google Docs, Google Sheets, and Google Calendar without the need for extra software or add-ons.

Q: Can Gemini Spark handle travel itineraries?

A: Yes, it can create travel itineraries and propose activities by reviewing emails for confirmations and checking calendar schedules.

Q: How does Spark ensure user privacy?

A: Spark includes confirmation checks for sensitive activities, requiring user consent before important actions are taken.

Q: Who is eligible to use Gemini Spark in Australia?

A: It is available to Google AI Pro and Ultra subscribers, with rollout taking place over the upcoming weeks.

NBN Co Utilizes AI to Generate Incident Reports and Provide Field Crews with Tools


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

NBN Co Adopts AI for Enhanced Infrastructure Management

Summary

  • NBN Co is utilizing AI to generate initial post-incident documentation.
  • AI is employed to refine infrastructure repair and connection methodologies.
  • ServiceNow’s Now Assist is a pivotal AI resource in operation.
  • AI initiatives are aimed at boosting service provision and operational efficiency.
  • A responsible AI policy ensures ethical and managed utilization.

AI in Incident Documentation

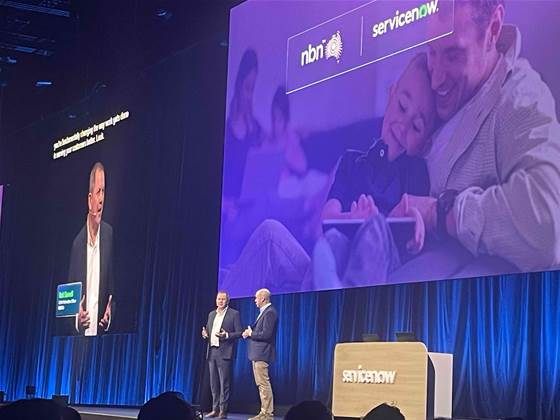
NBN Co is at the forefront of implementing AI to automate the preliminary draft of post-incident reports, greatly improving the speed and effectiveness of internal IT issue handling. This effort is part of a larger plan to incorporate AI into the company’s workflows.

ServiceNow’s Now Assist

ServiceNow’s Now Assist forms the foundation of NBN Co’s AI developments, offering generative and agentic AI capabilities. These tools assist in the drafting of post-incident reports, ensuring prompt and effective resolution of IT incidents.

AI-Powered Image Assessment

NBN Co is also harnessing AI for image assessment to ascertain when new constructions are suitable for NBN connection and to improve the repair process of compromised infrastructure. This application of AI is intended to streamline workflows and enhance customer service by speeding up repair durations.

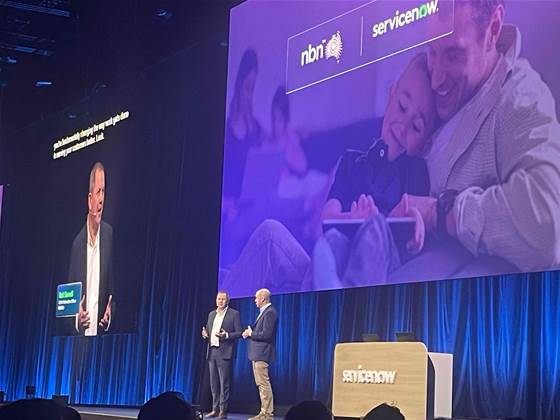
NBN Co using AI for infrastructure management

Future Prospects of AI

In the future, AI is anticipated to be vital in the evolution of autonomous networks that can better anticipate, identify, and react to network fluctuations in Australia. This proactive approach aims to support retail service providers further and enhance broadband offerings.

Commitment to Ethical AI

NBN Co is dedicated to executing AI in a responsible manner, guided by a thorough policy that assesses and regulates every AI application. The organization’s strategic AI integration is crafted to be straightforward, digital, and insight-focused, reinforcing its goal of delivering superior service and technology throughout Australia.

Conclusion

NBN Co’s strategic incorporation of AI is transforming its processes, from incident documentation to infrastructure management. By integrating AI technologies, the organization aims to boost efficiency, enhance service provision, and maintain a commitment to ethical AI practices.

Q: What is the main goal of employing AI in NBN Co’s operations?

A: The main goal is to automate and streamline functions, such as drafting post-incident reports and improving the efficiency of infrastructure repairs and connections.

Q: What role does ServiceNow’s Now Assist play in NBN Co’s AI implementation?

A: ServiceNow’s Now Assist offers the generative and agentic AI resources necessary to enable efficient incident reporting and management procedures.

Q: What advantages does AI-driven image assessment provide for NBN Co?

A: AI-driven image assessment aids in determining the readiness for new NBN connections and optimizes the repair of damaged infrastructure, resulting in quicker and more efficient service delivery.

Q: How is NBN Co ensuring ethical AI usage?

A: NBN Co adheres to a thorough responsible AI policy that evaluates and manages each AI application to guarantee ethical and controlled implementation.

Q: What future advancements does NBN Co anticipate with AI integration?

A: Future advancements include moving toward autonomous networks for better anticipation, detection, and response to network changes, thereby enhancing overall service delivery.

NZ Data Centre Constructor Obtains Agreement for Fresh Trans-Tasman Connection


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Tasman Ring Submarine Cable Network Achievement

Quick Overview

  • Datagrid NZ finalizes agreements with OMS Group and ASN for the Tasman Ring cable.
  • The cable will connect Invercargill, NZ with Melbourne, Australia.
  • Marine assessments will be carried out by OMS utilizing an unmanned vessel.
  • The initiative is projected to enhance latency by as much as 45% for users on the South Island.
  • Anticipated to be operational by 2029, featuring a design capacity of 160 terabits per second.
  • Mercury NZ purchases a 12.7% interest in Datagrid NZ.

Datagrid NZ’s Tactical Move in the Tasman Sea

Datagrid New Zealand has made a remarkable advancement in improving connectivity between Australia and New Zealand by signing contracts with Malaysia’s OMS Group and Alcatel Submarine Networks (ASN). This collaboration represents a crucial milestone in the construction of the Tasman Ring submarine cable network, a venture that is set to change data transmission across the Tasman Sea.

NZ data centre developer contracts for new trans-Tasman link

Advanced Survey Methods

The marine survey for the Tasman Ring cable will be carried out by OMS Group using an unmanned surface vessel (USV), a technology that offers effectiveness and accuracy in marine operations. This survey is a vital phase in the implementation of the cable, which will be later provided by ASN.

Linking Invercargill to Melbourne

The Tasman Ring Network will cover a distance of 2300 kilometres, connecting Invercargill on New Zealand’s South Island to Melbourne in Victoria, Australia. Datagrid NZ intends to set up an “AI factory” in Invercargill, utilizing the improved data connectivity provided by the submarine cable.

Technological Progress and Advantages

With a design capacity of 160 terabits per second and employing an Open Cable system, the project differentiates optical circuits from transmission equipment, enabling versatile and scalable data transfer capabilities. The cable is planned to be operational by 2029.

Effect on South Island’s Connectivity

Rémi Galasso, CEO of Datagrid, emphasized the advantages for universities, research institutions, and IT firms on New Zealand’s South Island. The new pathway is expected to enhance latency by as much as 45%, facilitating faster data transmission than current routes through the North Island.

Collaboration with Mercury NZ

Earlier this year, Mercury NZ acquired a 12.7% equity interest in Datagrid for NZ$53 million. This investment is in line with a power purchase agreement established in March 2026, which guarantees a supply of 140 megawatts for Datagrid’s proposed data centre facility.

Conclusion

The Tasman Ring submarine cable network is poised to revolutionize digital connectivity between Australia and New Zealand. With the participation of key players like OMS Group, ASN, and Mercury NZ, the initiative is set to provide substantial technological and economic advantages by 2029.

Q&A Session

Q: What is the goal of the Tasman Ring Network?

A: The Tasman Ring Network is designed to improve digital connectivity between the South Island of New Zealand and Australia, facilitating faster and more dependable data transmission.

Q: In what ways does the project address latency problems?

A: By providing a direct connection between Invercargill and Melbourne, the Tasman Ring Network decreases latency by up to 45% compared to current routes, increasing data speed and dependability.

Q: What technological advancements are utilized in the cable design?

A: The cable features an Open Cable system, which separates optical circuits from transmission equipment, ensuring improved scalability and flexibility in data management.

Q: When is the expected completion date for the project?

A: The Tasman Ring Network is forecasted to be operational by 2029.

Q: What role does Mercury NZ play in this project?

A: Mercury NZ holds a 12.7% stake in Datagrid and has entered into a power purchase agreement to provide 140 megawatts for the forthcoming data centre facility.

Q: Will the Tasman Ring Network replace current routes?

A: While it presents a quicker alternative, the network will complement existing routes, offering additional options for data transmission across the Tasman Sea.