
Apple-notarized CrashStealer Malware Pretends to be macOS Crash-Reporting Application

We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Brief Overview
- Apple macOS is being targeted by an advanced malware known as CrashStealer.
- This malware imitates authentic crash-reporting applications to evade detection.
- CrashStealer is propagated through a fraudulent collaboration app called Werkbit.
- Security firm Jamf uncovered the malware and alerted Apple.
- Apple has revoked the signing certificates for the harmful app.
The Rise of CrashStealer
Recently, researchers have discovered a new malware initiative aimed at Apple macOS users. Named CrashStealer, this complex malware poses as a legitimate crash-reporting software. The malware was initially detected by security firm Jamf, and further research has brought additional samples to light.
Veiled as a Collaboration App
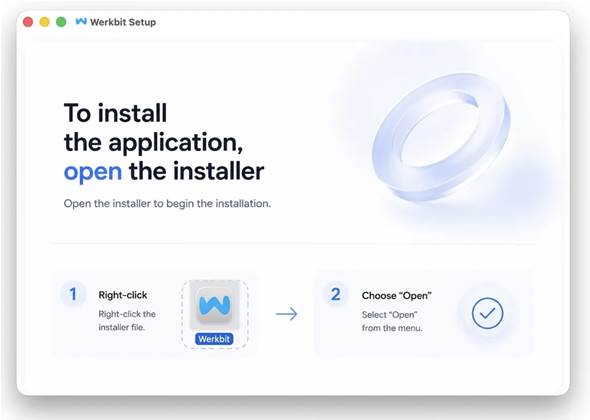
CrashStealer is disseminated through a misleading app referred to as Werkbit, which falsely purports to serve as a collaboration tool for reputable brands. The registration for the app’s website dates back to June, suggesting its recent establishment exclusively for malicious intent.
Mechanism of CrashStealer’s System Breach
The infection process starts with a PIN-protected Werkbit.dmg disk image. After downloading, it functions as a dropper, retrieving additional harmful payloads from GitHub repositories under the control of the attackers. The assailants have taken extensive measures to obtain an Apple developer account, using the name “Emil Grigorov” to notarize the malware and circumvent macOS Gatekeeper defenses.
Imitating Apple’s Crash-Reporting Utility
The payload of the malware closely mimics Apple’s crash-reporting component, using similar bundle identifiers and icons. When executed, it prompts users with a fraudulent macOS password request, designed to seem like a normal system upkeep task.
Harvesting Confidential Data
Once the correct password is acquired, CrashStealer retrieves and duplicates information from the Mac’s login keychain, focusing on browser passwords, cookies, cryptocurrency wallets, and more. The malware subsequently encrypts these credentials prior to exfiltration, adhering to a conventional attack methodology.
Professional Craftsmanship and Ongoing Risk
Jamf’s examination reflects a methodical approach in the creation of CrashStealer, employing native macOS binaries that are compatible with both Intel x86 and Apple Silicon systems. The attackers also impersonate reliable Apple components, illustrating advanced social engineering strategies.
Impending Campaigns and Expanded Targets
Researchers have noted several similar domains to Werkbit, indicating preparations for infrastructure tailored to ongoing operations. This hints at potential risks to Microsoft Windows systems as well.
Conclusion
CrashStealer poses a considerable danger to macOS users, utilizing advanced strategies to evade detection while pilfering sensitive information. Although Apple has intervened to revoke the malicious credentials, the enduring nature of such malware campaigns emphasizes the necessity for alertness and strong security protocols.
Reader questions
Frequently asked questions
Fast answers to the questions readers ask most about Apple-notarized CrashStealer Malware Pretends to be macOS Crash-Reporting Application.
What is the initial infection method for CrashStealer on macOS systems?
CrashStealer infiltrates systems via a counterfeit collaboration app known as Werkbit, which users download as a PIN-protected disk image.
What makes CrashStealer especially hazardous?
It mimics valid macOS crash-reporting tools, complicating detection, and it has the ability to steal sensitive information, including passwords and cryptocurrency wallet details.
How did Apple respond upon discovering CrashStealer's existence?
Apple revoked the signing credentials of the harmful application after being notified by the security firm Jamf.
What measures should macOS users take to safeguard against similar threats?
Users should be cautious when downloading unfamiliar applications, ensure their systems are up-to-date with the latest security updates, and contemplate employing additional security software.
Can CrashStealer impact other operating systems?
Currently targeting macOS, researchers propose that infrastructure is being set up for campaigns that might involve Microsoft Windows variants.
Is notarisation a definitive assurance of safety for macOS applications?
Notarisation does not serve as a comprehensive vetting process, prompting users to remain wary even with notarised applications.
