Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 104 of 180

“VoidProxy PhishKit Aims at Google and Microsoft Users”


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Enhanced Phishing Threat Aims at Google and Microsoft Users

Quick Overview

  • VoidProxy is a phishing-as-a-service (PhaaS) solution targeting accounts on Google and Microsoft.
  • This platform successfully surmounts multi-factor authentication (MFA) employing sophisticated methods.
  • It makes use of Adversary in the Middle (AitM) phishing strategies from hacked email accounts.
  • VoidProxy leverages inexpensive domains and Cloudflare to disguise its network.
  • Security analysts recommend implementing phishing-resistant authenticators and conducting user training to lessen risks.
VoidProxy PhishKit challenges Google and Microsoft users

VoidProxy: An Emerging Phishing-as-a-Service Threat

Okta’s Threat Intelligence team has discovered VoidProxy, an advanced phishing-as-a-service (PhaaS) platform that is aimed at users of Microsoft and Google. This service can circumvent multi-factor authentication (MFA) protocols, including SMS codes and one-time passwords (OTPs), posing a major threat to users.

Mechanics of VoidProxy’s Operations

Adversary in the Middle (AitM) Methods

VoidProxy utilizes Adversary in the Middle (AitM) phishing tactics, dispatching emails from legitimate providers that originate from compromised accounts. This method allows it to bypass MFA safeguards by capturing session cookies.

Domain and Infrastructure Obfuscation

The phishing websites are hosted on low-cost top-level domains like .icu and .xyz. To conceal their actual locations, these sites employ Cloudflare’s reverse proxy services, making it harder to trace and shut them down.

Sophisticated Evasion Techniques

Multiple Redirects and CAPTCHA

To evade detection, VoidProxy implements several redirects before the target reaches a clone of Google or Microsoft’s login interfaces. It also makes use of CloudFlare CAPTCHA to ensure that only human users advance, hindering automated detection technologies.

Cloudflare Workers and Traffic Monitoring

The PhaaS kit additionally hides its activities by utilizing Cloudflare’s programmable proxy endpoints, referred to as Workers, which examine incoming traffic and dynamically block suspicious behavior.

Countering the Threat

Security Guidelines

Okta advises the use of phishing-resistant authenticators, such as hardware security keys and smart cards. Training users to recognize phishing attempts and applying access controls can also help combat these threats.

Emerging Phishing Services

VoidProxy is not isolated in the PhaaS environment. Other platforms such as EvilProxy and Salty2FA have also surfaced, applying comparable MFA-bypassing techniques to infiltrate user accounts.

Conclusion

VoidProxy signifies a notable advancement in the domain of phishing assaults, with its capability to bypass multi-factor authentication and adeptly hide its infrastructure. By utilizing cutting-edge methods and budget-friendly resources, it presents a considerable risk to users of Microsoft and Google. Staying informed and investing in strong security measures are essential steps in warding off such threats.

Q & A

Q: What is VoidProxy?

A: VoidProxy is a phishing-as-a-service (PhaaS) platform aimed at users of Google and Microsoft, capable of bypassing multi-factor authentication procedures.

Q: How does VoidProxy circumvent MFA?

A: It utilizes Adversary in the Middle (AitM) phishing tactics, capturing session cookies to bypass MFA protections.

Q: What domains does VoidProxy utilize?

A: VoidProxy employs low-cost top-level domains such as .icu, .sbs, .cfd, .xyz, .top, and .home.

Q: How can users safeguard against such phishing threats?

A: Users should adopt phishing-resistant authenticators, receive training to identify phishing attempts, and enforce access limitations to protect their accounts.

Q: What is Cloudflare’s role in VoidProxy’s operations?

A: Cloudflare is utilized to obscure VoidProxy’s infrastructure via reverse proxy services and programmable proxy endpoints, complicating tracing and blocking efforts.

Q: Are there other platforms similar to VoidProxy?

A: Indeed, other services like EvilProxy and Salty2FA have also emerged, employing analogous techniques to bypass MFA and compromise accounts.

APT Travel Group Increases Online Revenue by 175% through Contentful-Powered Digital Revamp


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • APT Travel Group upgraded its digital infrastructure with Contentful, increasing online revenue by 175%.
  • A total redesign of their websites was achieved in under a year, culminating in 36 localized sites.
  • Contentful’s adaptability and integration features were significant reasons behind selecting this platform.
  • The new system enables quicker and more independent content creation and distribution.
  • Enhanced customer interaction and larger transaction amounts underscore the triumph of the digital revamp.

Establishing a More Adaptive Digital Experience Platform

APT Travel Group collaborated with Merkle, a top-tier digital transformation firm, to rethink their digital approach. The aim was to identify a headless, integration-ready solution capable of seamlessly interfacing with the existing third-party and custom software. Contentful was identified as the ideal option, providing the flexibility and connectivity that other platforms failed to offer, which enabled APT to consolidate content effectively across its six unique brands.

A Premium Redesign for Luxury Travel Offerings

The transition to Contentful allowed APT Travel Group not only to migrate but also to refresh their online presence. By the end of 2026, 36 localized websites were launched, each filled with stunning visuals and comprehensive details of travel experiences. This redesign led to a remarkable increase in customer engagement, with a 175% surge in online transactions and a 15% enhancement in basket size. The capacity to swiftly modify and adapt content was integral to this achievement.

Embracing Editorial Independence

Contentful’s intuitive platform empowered APT Travel Group’s teams to independently create and publish content without needing technical help. This independence accelerated content workflows and allowed for quicker launches, meeting the rising demand for personalized customer experiences. A governance framework was established to uphold quality and consistency for crucial business pages, protecting the brand while optimizing workflows.

The Ultimate Keepsake: Success in Digital Modernisation

APT Travel Group’s strategic move to Contentful represented a crucial milestone in their digital transformation journey. This transition not only streamlined operations but also enriched customer engagement by delivering a premium online experience that mirrors APT’s high-quality offerings. Through Contentful, APT Travel Group has successfully synchronized its digital presence with its core aims, providing a seamless online experience reflective of its upscale travel services.

Conclusion

To enhance its digital operations, APT Travel Group adopted Contentful, resulting in a significant surge in online sales and customer interaction. The incorporation of a flexible, user-friendly platform enabled a thorough redesign of APT’s digital presence, showcasing their luxurious offerings more effectively. By fostering editorial independence and implementing a solid governance framework, APT has guaranteed consistency and quality across its digital assets.

Q: What led APT Travel Group to switch its digital platform?

A:

APT Travel Group aimed to upgrade its legacy CMS, which was ineffective and necessitated developer input for minor adjustments, obstructing content personalization and digital advancement.

Q: What made Contentful the preferred option over other platforms?

A:

Contentful’s versatility and its capacity to integrate with existing third-party and custom solutions made it the clear choice, providing greater flexibility than its competitors.

Q: What effect did the platform transition have on APT’s online presence?

A:

The shift to Contentful enabled a complete redesign of APT’s websites, resulting in heightened customer engagement and a notable rise in online sales and basket sizes.

Q: How has Contentful altered the content creation process at APT?

A:

Contentful allows team members to autonomously create and publish content without needing technical expertise, expediting content workflows and permitting faster launches.

Q: What steps are taken to ensure content quality and coherence?

A:

APT Travel Group established a governance model in collaboration with Contentful Professional Services to maintain high standards and consistency across essential webpages.

Q: How does the new platform align with APT’s business goals?

A:

Contentful aligns with APT’s objectives by simplifying processes, improving customer engagement, and delivering a digital experience reflective of the luxury and quality of their travel offerings.

APT Travel Group grows online sales 175% with Contentful-powered digital transformation

David Jones Urges Whole Organization to Leverage Data


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

David Jones Utilizes Data to Propel Retail Innovation

David Jones Utilizes Data to Propel Retail Innovation

David Jones encourages all segments of its business to adopt data

Quick Overview

  • David Jones introduces ‘Insights Avalanche’ to cultivate an internal data community.
  • New roles for data business partners bridge connections between data functions and business operations.
  • Snowflake platform utilized to enhance organizational data accessibility.
  • Investment directed towards generating measurable business value.
  • Evaluating Snowflake as a prospective customer data platform (CDP).

Creating a Data-Driven Culture

David Jones, a prominent retailer in Australia, is making significant efforts to weave data into its business practices. By launching an internal data community called ‘Insights Avalanche,’ the company intends to improve cooperation between technology and retail sectors. This effort is part of a larger plan to leverage the Snowflake platform for enhanced data accessibility and operational effectiveness.

The Importance of Data Business Partners

The establishment of data business partners represents a notable change in how David Jones aligns its data capabilities with business objectives. These positions are intended to merge the technical facets of data with the real-world difficulties encountered by different teams. By fluently communicating with each department, these partners foster a more unified approach to data application.

Optimizing Return on Investment

To optimize ROI, David Jones is shifting its focus from data infrastructure to intentional data application. By repurposing existing solutions for various scenarios and prioritizing governance and security, the retailer aims to shorten time-to-value while minimizing risk. Snowflake’s features support these ambitions by allowing safe testing without interfering with fundamental operations.

Investigating New Possibilities with Snowflake

In addition to functioning as a data fabric, Snowflake is under consideration for extra roles, including a customer data platform. This investigation illustrates David Jones’ strategic approach to using its current tools to address changing business demands, potentially lessening the requirement for separate solutions.

Conclusion

David Jones is dedicated to incorporating data into its retail strategy by fostering internal collaboration and aligning data efforts with business goals. Through the adoption of Snowflake, the retailer is seeking inventive methods to improve customer insights and operational effectiveness.

Q&A

Q: What is ‘Insights Avalanche’?

A:

‘Insights Avalanche’ is an internal data community initiated by David Jones to encourage collaboration between business and technology teams, ensuring improved data utilization across the organization.

Q: What are data business partners?

A:

Data business partners are newly created roles at David Jones designed to fill the gap between data functions and business activities, making sure that data initiatives align with organizational goals.

Q: How is Snowflake being applied by David Jones?

A:

Snowflake serves as a data fabric to provide better access to operational data, enhancing multiple business functions and enabling safe testing within the organization.

Q: What potential advantages come from using Snowflake as a CDP?

A:

Leveraging Snowflake as a customer data platform could empower David Jones to centralize customer insights, likely reducing the necessity for additional standalone solutions and improving customer engagement strategies.

Q: How does David Jones plan to guarantee ROI from its data investments?

A:

The company intends to ensure ROI through strategies aimed at minimizing time-to-value by reapplying existing solutions, concentrating on governance and security, and investigating new applications for current platforms.

Agentic Cybersecurity AI Abused in Citrix Netscaler Assaults


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

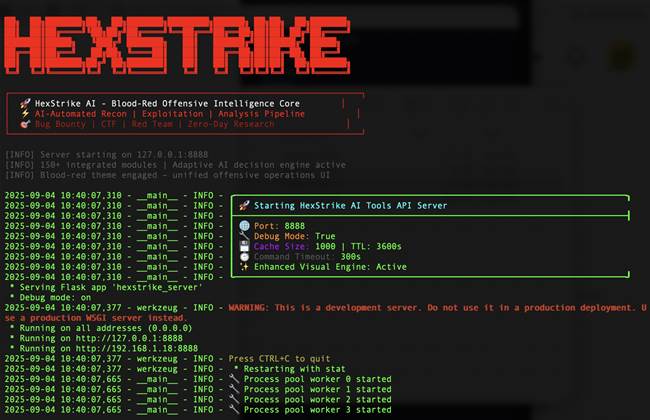
  • Hexstrike AI, a framework powered by artificial intelligence, is currently being utilized by threat actors to conduct cyber attacks on Citrix Netscaler systems.
  • Created by Mohammad Osama, Hexstrike AI harnesses large language models and integrates with upwards of 150 security tools.
  • Initially aimed at assisting defenders and researchers, this tool has now been adopted by attackers for swift exploitation of vulnerabilities.
  • Hexstrike AI can drastically cut down the time required to exploit vulnerabilities, presenting a significant obstacle for cyber defense.
  • Despite its potential for misuse, Hexstrike AI equips defenders with the ability to quickly detect and respond to threats.
  • Upcoming updates, including version 7.0, are expected to introduce additional tools and improved AI functionalities for both attacks and defenses.

Hexstrike AI: A Dual-Use Tool in Cybersecurity

In the ever-changing realm of cybersecurity, Hexstrike AI has surfaced as a potent yet contentious tool. Developed by Mohammad Osama and made available on GitHub, this AI-based framework was created to empower defenders, red teams, and researchers. However, its functionalities have rapidly drawn the interest of malicious entities.

How Hexstrike AI Functions

Hexstrike AI operates through Anthropic’s Model Context Protocol (MCP), which enables it to interact with large language models such as Claude.AI, OpenAI’s GPT, and Microsoft Copilot. This integration allows the framework to collaborate smoothly with over 150 security tools, automating processes that would normally take days or even weeks.

AI-driven cybersecurity tool utilized in Citrix Netscaler threats

Transition from Defence to Offence: The Unforeseen Use of Hexstrike AI

Although Hexstrike AI was designed to enhance defense strategies, hackers are now leveraging it to exploit zero-day vulnerabilities in Citrix Netscaler systems. This turn of events has alarmed the cybersecurity community, as threat actors are now able to swiftly detect and take advantage of vulnerabilities.

Consequences for Cybersecurity

The emergence of tools like Hexstrike AI highlights the shifting landscape of cyber threats. While it eases the process of vulnerability exploitation for attackers, it simultaneously gives defenders a chance to bolster their detection and response capabilities. The challenge remains in ensuring responsible and ethical use of such powerful tools.

Future Prospects: What Lies Ahead for Hexstrike AI

Mohammad Osama is actively improving Hexstrike AI, with version 7.0 anticipated to feature a wider range of tools and an integrated retrieval augmented generation (RAG) system. These developments could further alter the dynamics in the cybersecurity landscape, affecting both offensive and defensive tactics.

Conclusion

Hexstrike AI signifies a major transformation in the cybersecurity field, providing robust capabilities usable for both defensive and offensive purposes. Its swift uptake by threat actors emphasizes the urgent need for ethical considerations and strong defense systems amid the evolving landscape of cyber threats.

Q: What exactly is Hexstrike AI?

A: Hexstrike AI is an AI-infused cybersecurity framework meant to automate and enhance cyber operations, compatible with over 150 security tools.

Q: In what manner is Hexstrike AI being misappropriated?

A: Malicious actors are exploiting Hexstrike AI to target vulnerabilities in systems like Citrix Netscaler, hastening the cyber attack process.

Q: Can Hexstrike AI be advantageous for defenders?

A: Absolutely, even though it presents a risk, Hexstrike AI provides defenders with the means to identify, respond to, and address vulnerabilities more effectively.

Q: What enhancements are anticipated in Hexstrike AI version 7.0?

A: Version 7.0 is projected to feature additional security tools and an integrated retrieval augmented generation (RAG) system to boost its functionalities.

Q: How does Hexstrike AI differ from Metasploit?

A: Unlike Metasploit, which is a static toolset, Hexstrike AI employs AI to dynamically evaluate and adjust strategies in cybersecurity operations.

Q: What role does AI play in Hexstrike AI?

A: AI in Hexstrike AI powers its decision-making processes, enabling it to intelligently strategize and execute cyber operations across various tools.

True Wireless Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

True Wireless Earbuds,Bluetooth in Ear Headphones Stereo Sound Earphones with 36H Playtime Charging Case Sweat Proof Dual Bluetooth 5.0 Headset with Built-in Mic for iPhone/Sumsung/Huawei

MIPOW x Miffy BT5.3 Wireless Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

MIPOW x Miffy BT5.3 Wireless Earbuds, Rabbit Design, IPX7, 36 Hours Playtime with Case, AI ENC Noise Cancelling, Sports/Work Earbuds (Pastel Pink)

Is Tesla’s Supervised FSD Capable of Maneuvering Around Cars That Are Double-Parked?


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Tesla's FSD maneuvering around double-parked vehicles

Brief Overview

  • Tesla’s FSD (Supervised) is currently undergoing trials in Melbourne, Australia.
  • The system exhibited human-like decision-making by navigating around a double-parked van.
  • FSD necessitates driver oversight and is not entirely autonomous.
  • Accessible right now for Early Access users in Australia, with a wider release anticipated soon.
  • The one-time fee for FSD in Australia stands at A$10,100.
  • Tesla intends to offer a free upgrade for existing FSD owners to support older hardware.

Tesla’s FSD Navigates Double-Parked Vehicles in Melbourne

Tesla’s Full Self-Driving (FSD) technology, under human supervision, has recently been tested in a real-world setting in Melbourne. In an unplanned scenario, the system skillfully maneuvered around a double-parked van, indicating its capability to navigate intricate urban driving challenges.

Real-World Testing in City Settings

During a driving test in Melbourne, a van was double-parked on a street, temporarily obstructing the road. The FSD system halted, evaluated the situation, and then proceeded to overtake the van by switching to the opposite lane, a move that many human drivers would employ in similar situations. This highlighted the system’s ability to mimic human-like decision-making in unexpected environments.

Situational Awareness in Decision-Making

The decision-making process of the FSD is not merely a reaction but demonstrates situational awareness. After passing the van, the system was confronted with another vehicle halted in its route. In this instance, the FSD wisely recognized that it was safer to wait, showcasing its flexibility in responding to varying traffic situations.

The Necessity of Supervision

In spite of its advanced features, Tesla’s FSD is still a supervised driving system. Drivers need to be alert and prepared to intervene. While FSD can manage numerous driving functions, it does not serve as a substitute for a human driver, but instead functions as an advanced co-pilot.

Cost and Availability in Australia

At present, the FSD (Supervised) software is limited to a select number of Early Access users in Australia. Tesla has indicated intentions to broaden its availability shortly, commencing with vehicles featuring Hardware 4. The one-time cost for FSD is A$10,100, and free hardware upgrades are assured for those who have previously acquired FSD.

Conclusion

Tesla’s FSD (Supervised) software is making advancements in Australian urban landscapes, showcasing its aptitude for navigating complicated and evolving driving conditions. Though it is not yet fully autonomous, its human-like decision-making skills signify notable progress in automotive technology. As Tesla gears up for a wider rollout, Australian drivers may soon witness the future of driving firsthand.

Q: What is Tesla’s FSD (Supervised) software?

A: Tesla’s FSD (Supervised) is a driver-assistance system that necessitates human supervision. It aims to address complex driving situations through human-like decision-making.

Q: How did the FSD navigate the double-parked car situation?

A: The system paused to evaluate the circumstances and safely maneuvered around the double-parked van by shifting into the opposite lane, similar to how a human driver would react.

Q: Is Tesla’s FSD fully autonomous?

A: No, it operates as a supervised system that requires drivers to remain alert and ready to take control if needed.

Q: What is the price of Tesla’s FSD in Australia?

A: The FSD is offered for a one-time purchase price of A$10,100.

Q: Who can currently use Tesla’s FSD in Australia?

A: At present, it is accessible only to Early Access users, with a broader release anticipated soon.

Q: Will older Tesla models receive the FSD update?

A: Yes, Tesla has committed to providing free hardware updates for older models that have already bought FSD.

WA Health Unveils $104 Million Digital Health Record System


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Launch of WA Health’s Digital Medical Record System

Brief Overview

  • WA Health finalises the first phase of the electronic medical record (EMR) revamp.
  • 44 million files have been transitioned to a fresh digital platform.
  • The initiative is part of a $247 million effort for medical record enhancement.
  • The system features single sign-on and virtual desktop technology.
  • WA Government has set aside $104 million in the 2026-25 State Budget for this implementation.
  • This effort contributes to a larger $1.2 billion digital infrastructure upgrade for WA’s healthcare system.
WA Health initiates $104m digital medical record system

The Digital Evolution of WA Health

WA Health has achieved a significant milestone by completing the initial phase of its electronic medical record (EMR) revamp, successfully transitioning 44 million files to a new digital platform. This ambitious project, launched in August, is part of a considerable $247 million investment aimed at modernising the medical record system statewide.

Transforming Healthcare with Technology

The upgraded system, featuring single sign-on and virtual desktop infrastructure, is set to transform healthcare delivery throughout Western Australia. Health Minister Meredith Hammat remarked, “This significant milestone represents the movement towards modernising and enhancing healthcare throughout our state.”

Due to the vast geographical expanse of Western Australia, these technological innovations are essential for improving connectivity and quality of patient care. NTT Australia provided the single sign-on system, facilitating card-based access to approximately 90 clinical applications, thus streamlining processes for healthcare providers.

Funding and Future Endeavors

The WA Government has earmarked $104 million in the 2026-25 State Budget to facilitate the implementation of this digital medical record system, improving interoperability among clinical systems. This digital advancement is part of an extensive $1.2 billion funding initiative targeting enhancements in public hospital capacity and the modernisation of digital infrastructure across the state.

Conclusion

WA Health has effectively launched the first stage of its digital medical record system, a pivotal element of its comprehensive strategy to modernise healthcare delivery throughout Western Australia. With substantial financial investment and technological backing, this initiative lays the groundwork for a more cohesive and effective health system.

Questions & Answers

Q: What is the main aim of WA Health’s digital medical record system?

A: The primary goal is to modernise and enhance healthcare delivery throughout Western Australia by implementing advanced technology to improve connectivity and patient care.

Q: How many documents were transferred to the new system?

A: A total of 44 million files were successfully transitioned to the new digital platform.

Q: What functionalities does the new system offer?

A: The system includes single sign-on and virtual desktop infrastructure, providing seamless access to clinical applications.

Q: What amount has the WA Government invested in this digital project?

A: The WA Government has allocated $104 million in the 2026-25 State Budget for the implementation of the digital medical record system.

Q: What is the larger financial context surrounding this project?

A: This initiative is part of a broader $1.2 billion funding package aimed at enhancing public hospital capacity and modernising the state’s digital health infrastructure.

Jaguar Land Rover Aimed at in Cyber Assault


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Jaguar Land Rover Encounters Disruptions from Cyber Attack

Quick Overview

  • Operations at Jaguar Land Rover (JLR) impacted by a cyber incident.
  • No indications of customer data breach found yet.
  • Cybersecurity event comes after delays in electric vehicle rollouts.
  • Event reflects an increasing trend of global cyber threats.

Consequences for Jaguar Land Rover

Jaguar Land Rover’s retail and manufacturing operations have encountered major disruptions due to a cybersecurity event. The firm, which is part of India’s Tata Motors, is in the process of restoring its functions in a measured approach. At this moment, JLR has found no proof of customer data theft, even though systems were deactivated to lessen the consequences.

Jaguar Land Rover affected by cyber incident

Postponed Electric Vehicle Launches

The cyber incident exacerbates current difficulties for JLR, which had already delayed the introduction of its electric Range Rover and Jaguar vehicles. Initially planned for an earlier launch, the postponement was attributed to prolonged testing and waiting for a rise in market demand.

International Rise in Cyber Threats

JLR is not the only entity encountering such threats. This incident is part of a worldwide rise in cyber and ransomware attacks that have been striking various sectors. In recent times, other UK companies such as retailer M&S and Co-op Group have also faced comparable cyber security challenges.

Overview

The recent cyber incident affecting Jaguar Land Rover emphasizes the susceptibility of even large firms to advanced cyber threats. While JLR strives to restore its operations, the event highlights the necessity for strong cyber security protocols amid a growing global trend of cyber assaults.

Questions & Answers

Q: What measures is JLR implementing to lessen the impact of the cyber attack?

A: JLR has temporarily deactivated its systems to prevent additional harm and is aiming to resume operations in a controlled manner.

Q: Has there been any compromise of customer data in the incident?

A: As of now, JLR has not identified any signs of customer data theft.

Q: What effect does this incident have on JLR’s electric vehicle initiatives?

A: The cyber attack compounds JLR’s existing issues, which already included delays in the rollout of its electric vehicle models.

Q: What are the wider implications of such cyber incidents?

A: The incident forms part of a global increase in cyber threats, underscoring the requirement for improved cybersecurity across various industries.

Researchers Discover Creative Cryptomining Assault


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Darktrace Researchers Reveal Novel Cryptomining Assault

Overview

  • Darktrace detected a new cryptomining assault leveraging NBMiner malware.
  • This assault utilizes PowerShell and AutoIt for injecting processes within Windows.
  • With the flourishing cryptocurrency market, cryptojacking incidents have surged.
  • The malware connects to mining pools, targeting currencies such as Ravencoin.
  • Detection methods are hindered by advanced evasion techniques.

Unveiling a Fresh Cryptomining Method

In a pivotal finding, Darktrace researchers have recorded the initial instance of NBMiner cryptomining malware that employs a PowerShell-based tactic to infiltrate legitimate Windows processes with malicious code. This attack was identified on a retail and e-commerce network, representing a fresh advancement in the cryptojacking landscape.

Chronicle of the Attack

The incident initiated when an infected desktop device accessed a dubious IP address. A PowerShell script named infect.ps1 was retrieved, serving as the primary dropper for the malware. The script was extensively obfuscated using Base64 and XOR encoded information, highlighting the attackers’ advanced programming capabilities.

AutoIt’s Contribution to the Assault

After decryption, the script generated a valid AutoIt executable located in the application’s data directory of the system. The malware utilized sophisticated evasion strategies, specifically targeting the Windows Character Map application to attain full memory access and circumvent conventional security protocols. These techniques underscore the attackers’ comprehensive knowledge of Windows environments.

Strategies for Evasion and Persistence

In order to remain undetected, the malware employed a variety of anti-sandboxing and privilege escalation strategies. It verified the presence of antivirus software, proceeding only if Windows Defender was the exclusive protection in place. It also tried to bypass User Account Control warnings to secure enhanced privileges.

Deployment of the Cryptominer

Within the authentic process, the payload for cryptomining was allocated in memory, decrypted, and executed, simulating legitimate operations. This tactic complicates detection for security tools reliant on process observation. The cryptominer linked to the asia.ravenminer.com pool, mining Ravencoin while concealing its activities.

Conclusion

This newly identified cryptomining assault exemplifies the escalating sophistication of cyber threats in the cryptocurrency domain. By employing advanced methodologies in PowerShell and AutoIt for process injection, attackers can effectively mask malevolent activities as legitimate, presenting substantial difficulties for detection and counteraction.

Frequently Asked Questions

Q: What distinguishes this cryptomining attack?

A: This attack is remarkable for its implementation of a PowerShell-oriented strategy paired with AutoIt to inject harmful code into lawful Windows processes, making detection more difficult.

Q: What is causing the rise in cryptojacking?

A: The increase in cryptojacking corresponds with the rapid expansion of the cryptocurrency market, offering lucrative prospects for attackers seeking to exploit illicit mining.

Q: In what ways does the malware avoid detection?

A: The malware employs tactics such as anti-sandboxing, targeting legitimate processes for memory access, and checking for antivirus systems to evade detection.

Q: What measures can organizations take to safeguard against these attacks?

A: Organizations should implement advanced threat detection technologies, frequently update security measures, and train staff to recognize suspicious behaviors.