David Leane, Author at Techbest - Top Tech Reviews In Australia - Page 8 of 50

Fair Work Commission’s Rapid and Secure Implementation of Agentic AI in Weeks


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Rapid Implementation of AI by the Fair Work Commission

Brief Overview

  • The Fair Work Commission (FWC) swiftly utilized regulated AI agents, boosting efficiency and preserving public confidence.
  • The FWC’s AI implementation was finalized within weeks, emphasizing rigorous governance and operational transformation.
  • The AI applications include an IT Support Genie and License Optimization Genie, streamlining internal workflows.
  • FWC intends to broaden AI functionalities to include public-facing services, like a contact centre agent.
  • The initiative highlights the significance of governance, readiness, and strategic capacity utilization.
How the Fair Work Commission efficiently utilized Agentic AI in weeks, not years

Overview

The Robodebt controversy in Australia underscored the dangers of inadequately controlled automation. For the Fair Work Commission (FWC), maintaining governance while accepting AI was essential. Joshua Pope, FWC’s CTO, acknowledged the potential advantages and obstacles of using AI to manage workplace conflicts for many Australians.

Governance and Quick AI Implementation

The FWC’s strategy for AI implementation focused on rigorous governance and rapid execution. Given the Australian government’s strict security standards, FWC required a platform that enabled flexible development while ensuring data sovereignty.

AI Solutions for Internal Operations

FWC’s internal AI solutions comprise the IT Support Genie and License Optimization Genie. These agents optimize processes, decrease manual involvement, and improve operational efficiency. For instance, the IT Support Genie allows for multiple daily system status checks, proactively detecting issues.

Enhancing AI Capabilities

FWC intends to enhance AI functionalities in public-facing services, such as developing a contact centre agent for call management. This aims to minimize call wait times and enhance service delivery, reflecting an emphasis on alleviating operational friction points.

Insights from AI Implementation

The FWC’s AI deployment imparts critical insights: governance is vital, and freeing up capacity should be aligned with strategic reallocation. Joshua Pope recommends that organizations focus on identifying reusable solutions rather than creating custom systems for each instance.

Conclusion

The Fair Work Commission’s rapid AI agent implementation illustrates a paradigm of efficiency, governance, and strategic foresight. By concentrating on internal enhancements and preparing for public-facing upgrades, FWC is establishing a new benchmark in governmental AI application.
Q: What was the primary emphasis of FWC’s AI deployment?

A: The primary emphasis was on stringent governance and swift deployment, enhancing operational efficiency while sustaining public trust.

Q: What tools were introduced internally by FWC?

A: FWC introduced the IT Support Genie and License Optimization Genie, which streamline workflows and diminish manual input.

Q: What advantages does the IT Support Genie offer to FWC?

A: It facilitates multiple daily status evaluations across systems, proactively identifying and resolving issues before they affect users.

Q: What future initiatives does FWC have for AI?

A: FWC plans to create a contact centre agent for call triage, which aims to minimize wait times and enhance service delivery.

Q: Why is governance critical in AI deployment?

A: Governance guarantees that AI systems function within compliance frameworks, preserving public trust and operational legitimacy.

Q: What guidance does Joshua Pope provide regarding AI deployment?

A: He recommends that organizations identify and leverage existing solutions instead of crafting custom systems for every application.

ACMA Initiative Reduces Listings of Unreliable Devices


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

ACMA Program Results in Notable Decline in Dubious Device Listings

Quick Read

  • ACMA’s program has led to a 69% decrease in dubious device listings.
  • The initiative includes commitments from prominent online retailers such as eBay and Gumtree.
  • Two-way radios and mobile phone repeaters are the most frequently encountered non-compliant devices.
  • ACMA performed a five-week evaluation that uncovered the decline in listings.
  • The initiative aims to improve the reliability of emergency call services.

The Program and Its Effects

The Australian Communications and Media Authority (ACMA) indicated a significant drop in listings of unsafe mobile phones and various dubious radio devices. This follows the launch of a voluntary program aimed at online retailers amid heightened scrutiny of emergency call services.

ACMA pledge program assists in reducing dubious device listings

Online Retailers Contribute to the Cause

ACMA’s program, revealed last December, includes commitments from major online retailers like eBay, Gumtree, Temu, and Shein to prevent the sale of non-compliant devices. A recent five-week evaluation conducted from April to May showed a 69% decline in these listings, from 1162 last year to just 361.

Emphasis on Compliance

The evaluation examined seven online platforms: Amazon Australia, eBay, Facebook Marketplace, Gumtree, Kogan, Temu, and Shein. Five of these platforms still displayed some dubious device listings. Two-way radios were the most common, followed by unauthorized mobile phone repeaters and jamming devices.

Issues with Grey Market Mobiles

Although the evaluation did not uncover any non-compliant grey market mobile handsets, concerns linger, particularly following the Optus outage in September. These grey market mobiles have sparked discussions regarding the reliability of Samsung devices during emergencies, leading to calls for a centralized database of problematic devices.

Suggested Changes and Future Actions

ACMA intends to implement modifications to mobile testing regulations, ensuring more frequent compliance assessments in relation to emergency call access standards. This initiative seeks to fill gaps in the existing voluntary record-keeping system, which the Australian Telecommunications Alliance (ATA) argues may enable non-compliant grey market handsets to evade scrutiny.

Conclusion

ACMA’s program has resulted in a considerable decline in the number of dubious devices listed by online retailers in Australia. By securing commitments from major platforms and conducting comprehensive evaluations, ACMA is working to enhance the reliability of emergency call services and tackle compliance issues associated with grey market mobiles.

Q: What is the primary goal of ACMA’s program?

A: The primary goal is to decrease the listings of non-compliant and illegal devices sold online, thereby enhancing the reliability of emergency call services.

Q: Which online platforms participate in ACMA’s initiative?

A: The program involves platforms like eBay, Gumtree, Temu, Shein, Amazon Australia, Facebook Marketplace, and Kogan.

Q: What types of devices are predominantly found non-compliant?

A: Two-way radios and unauthorized mobile phone repeaters are the most frequently observed non-compliant devices.

Q: What concerns exist regarding grey market mobiles?

A: Grey market mobiles raise concerns due to potential issues with emergency call reliability, especially underscored by the Optus outage incident.

Q: How will ACMA’s proposed changes influence device compliance testing?

A: ACMA’s proposed changes are aimed at ensuring more frequent testing of handsets for compliance with emergency call access standards.

Unity Bank revamps IT leadership after successful merger conclusion


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Unity Bank Revamps IT Leadership Following Merger Completion

Unity Bank revamps IT leadership following merger completion

Quick Overview

  • Unity Bank completes merger with G&C Mutual Bank.
  • Chief Information Officer position removed; duties reassigned to COO.
  • New head of IT operations and security appointed.
  • Maintained emphasis on digital banking and cybersecurity.
  • Brands consolidated under the Unity Bank banner.
  • Along history of mergers and rebranding spanning decades.

Transformative IT Leadership Adjustment

Following its merger with G&C Mutual Bank, Unity Bank has transformed its IT leadership framework. The chief information officer position has been phased out, with responsibilities reassigned to chief operating officer Akhilesh Mehta. A new head of IT operations and security has been appointed to report directly to Mehta, though their name has not been disclosed.

Contributions of the Previous CIO

Former CIO Fergus Stevens, who left the role in March after more than a year, significantly contributed during the merger. Stevens oversaw the technical integration, guaranteeing system conformity and adherence to regulations. His initiatives ensured continuous service for 60,000 members.

Commitment to Digital Banking and Cybersecurity

Even with the changes in leadership, Unity Bank’s technological aims remain unwavering. The bank persists in its efforts to provide a smooth digital banking experience and to uphold strong cybersecurity protocols for safeguarding its members’ assets.

Unity Bank’s Growth Through Acquisitions

Unity Bank boasts a significant history of expansion through mergers. It has amalgamated G&C Mutual Bank and another brand, Reliance Bank, under the Unity Bank identity. This unification simplifies operations and bolsters the bank’s market position. The bank began its journey as the Waterside Workers of Australia Credit Union in 1970, progressing through various mergers and brand alterations across the years.

Conclusion

Unity Bank’s recent merger with G&C Mutual Bank has instigated a strategic overhaul of its IT leadership, prioritizing digital advancement and security. The bank’s historical mergers have influenced its existing framework, establishing it as a formidable force in the Australian finance sector.

Q&A

Q: Why was the CIO role removed at Unity Bank?

A: The CIO position was removed to enhance IT management efficiency under COO Akhilesh Mehta, fostering better integration.

Q: Who oversees IT operations currently?

A: IT operations are now overseen by a newly appointed head of IT operations and security, who reports to COO Akhilesh Mehta.

Q: What successes did Fergus Stevens achieve as CIO?

A: Fergus Stevens effectively integrated the technology platforms of the merging banks, achieved compliance with regulations, and ensured uninterrupted services.

Q: What is the main technological focus of Unity Bank after the merger?

A: Unity Bank’s primary focus is on providing efficient digital banking services and maintaining robust cybersecurity.

Q: In what way has Unity Bank developed over the years?

A: Unity Bank has progressed through numerous mergers and rebranding efforts, tracing its roots back to the Waterside Workers of Australia Credit Union in 1970.

US and Allies Blame Russian Hackers for Email Theft Without Utilizing Social Engineering


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Russian Hackers Capitalize on Zimbra Email Service in Worldwide Operation

Quick Overview

  • Russian hackers took advantage of a Zimbra email flaw by employing a “half-click exploit.”
  • The attack did not necessitate any social engineering methods.
  • The campaign initially focused on Ukraine before reaching NATO nations.
  • The hacking group Laundry Bear is suspected, with purported connections to Russian security agencies.
  • A US indictment associates Laundry Bear with the Russian entity Yutek-NN.
  • The Zimbra flaw has now been addressed with a patch.

Exploiting Zimbra

Recently, Russian hackers have targeted Zimbra email platform users, leveraging a significant vulnerability referred to as a “half-click exploit.” As noted by Proofpoint, the cybersecurity company that discovered the exploit, the attack demanded users to simply open an email, circumventing conventional social engineering techniques. This flaw has been patched, yet the incident emphasizes ongoing challenges in cybersecurity.

Global Consequences

The attack was not confined to a specific area. Initially centered on Ukraine, the campaign swiftly extended its reach to NATO member nations, including the United States, Canada, and various European countries. The coordinated initiative attracted the attention of law enforcement and intelligence organizations globally, resulting in a detailed 31-page alert regarding the threat.

Involvement of Laundry Bear

The hacking group known as Laundry Bear is believed to be leading this cyber espionage initiative. Allegedly backed by the Russian government, Laundry Bear is among various groups reportedly working on behalf of Russian security services. The US has established a connection between the group and Yutek-NN, a Russian cybersecurity firm facing legal issues in the United States.

Legal Consequences

A US indictment has been issued against Denis Obrezko, the deputy director of Yutek-NN, linking him to the hacking activities. Arrested in Thailand and facing charges in Boston, Obrezko has denied the accusations. The Russian embassy and Yutek-NN have not yet responded to these claims.

Zimbra’s Reaction

Zimbra and its parent organization, Synacor, have not released immediate statements regarding the breach. The event underscores the necessity of vigilance in cybersecurity practices, especially for services that are frequently targeted by state-sponsored cyber espionage.

Conclusion

The recent cyberattack taking advantage of Zimbra email software underlines the continual risk posed by state-sponsored hacking entities. The rapid patching of the vulnerability showcases the significance of proactive cybersecurity measures. As geopolitical tensions persist in shaping cyber operations, being informed and prepared remains essential for both individuals and organizations.

Q&A

Q: What does a “half-click exploit” mean?

A:

It’s a form of cyberattack that necessitates minimal interaction from the user. In this scenario, users needed only to open an email for the exploit to activate, avoiding standard social engineering approaches.

Q: Who are Laundry Bear?

A:

Laundry Bear is a hacking group reportedly backed by the Russian government, recognized for its cyber espionage operations targeting different nations.

Q: Is the Zimbra vulnerability resolved?

A:

Yes, the vulnerability has been fixed, lowering the likelihood of similar assaults through this particular method.

Q: What potential outcomes face Yutek-NN?

A:

Yutek-NN and its deputy director confront legal challenges in the US, including charges related to hacking, which could lead to significant legal and reputational fallout.

Q: Why are email services commonly targeted?

A:

Email services are often pursued as they can house sensitive information and grant access to larger networks, making them attractive targets for cyber espionage.

For additional technology news, visit TechBest.

In Images: Discovering the Future of Retail at Flipkart’s Melbourne Roundtable


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Delving into the Retail Future at Flipkart’s Melbourne Roundtable

Concise Overview

  • Retail executives assembled in Melbourne for a discussion on the future of retail.
  • Emphasis on AI-driven infrastructure and conversational AI.
  • Composable architecture for enhanced operational flexibility.
  • Consolidated retail media and adaptive pricing as novel revenue opportunities.

The Retail Landscape Ahead

Delving into the Retail Future at Flipkart's Melbourne Roundtable

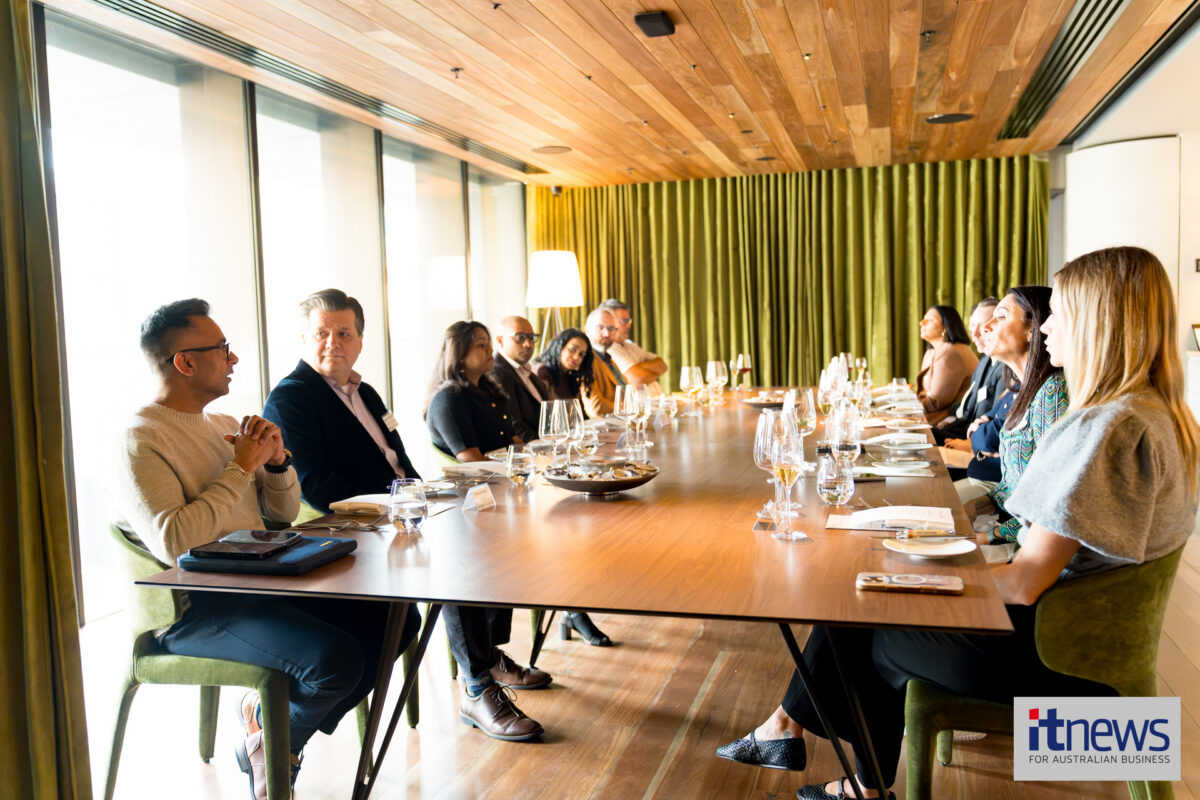
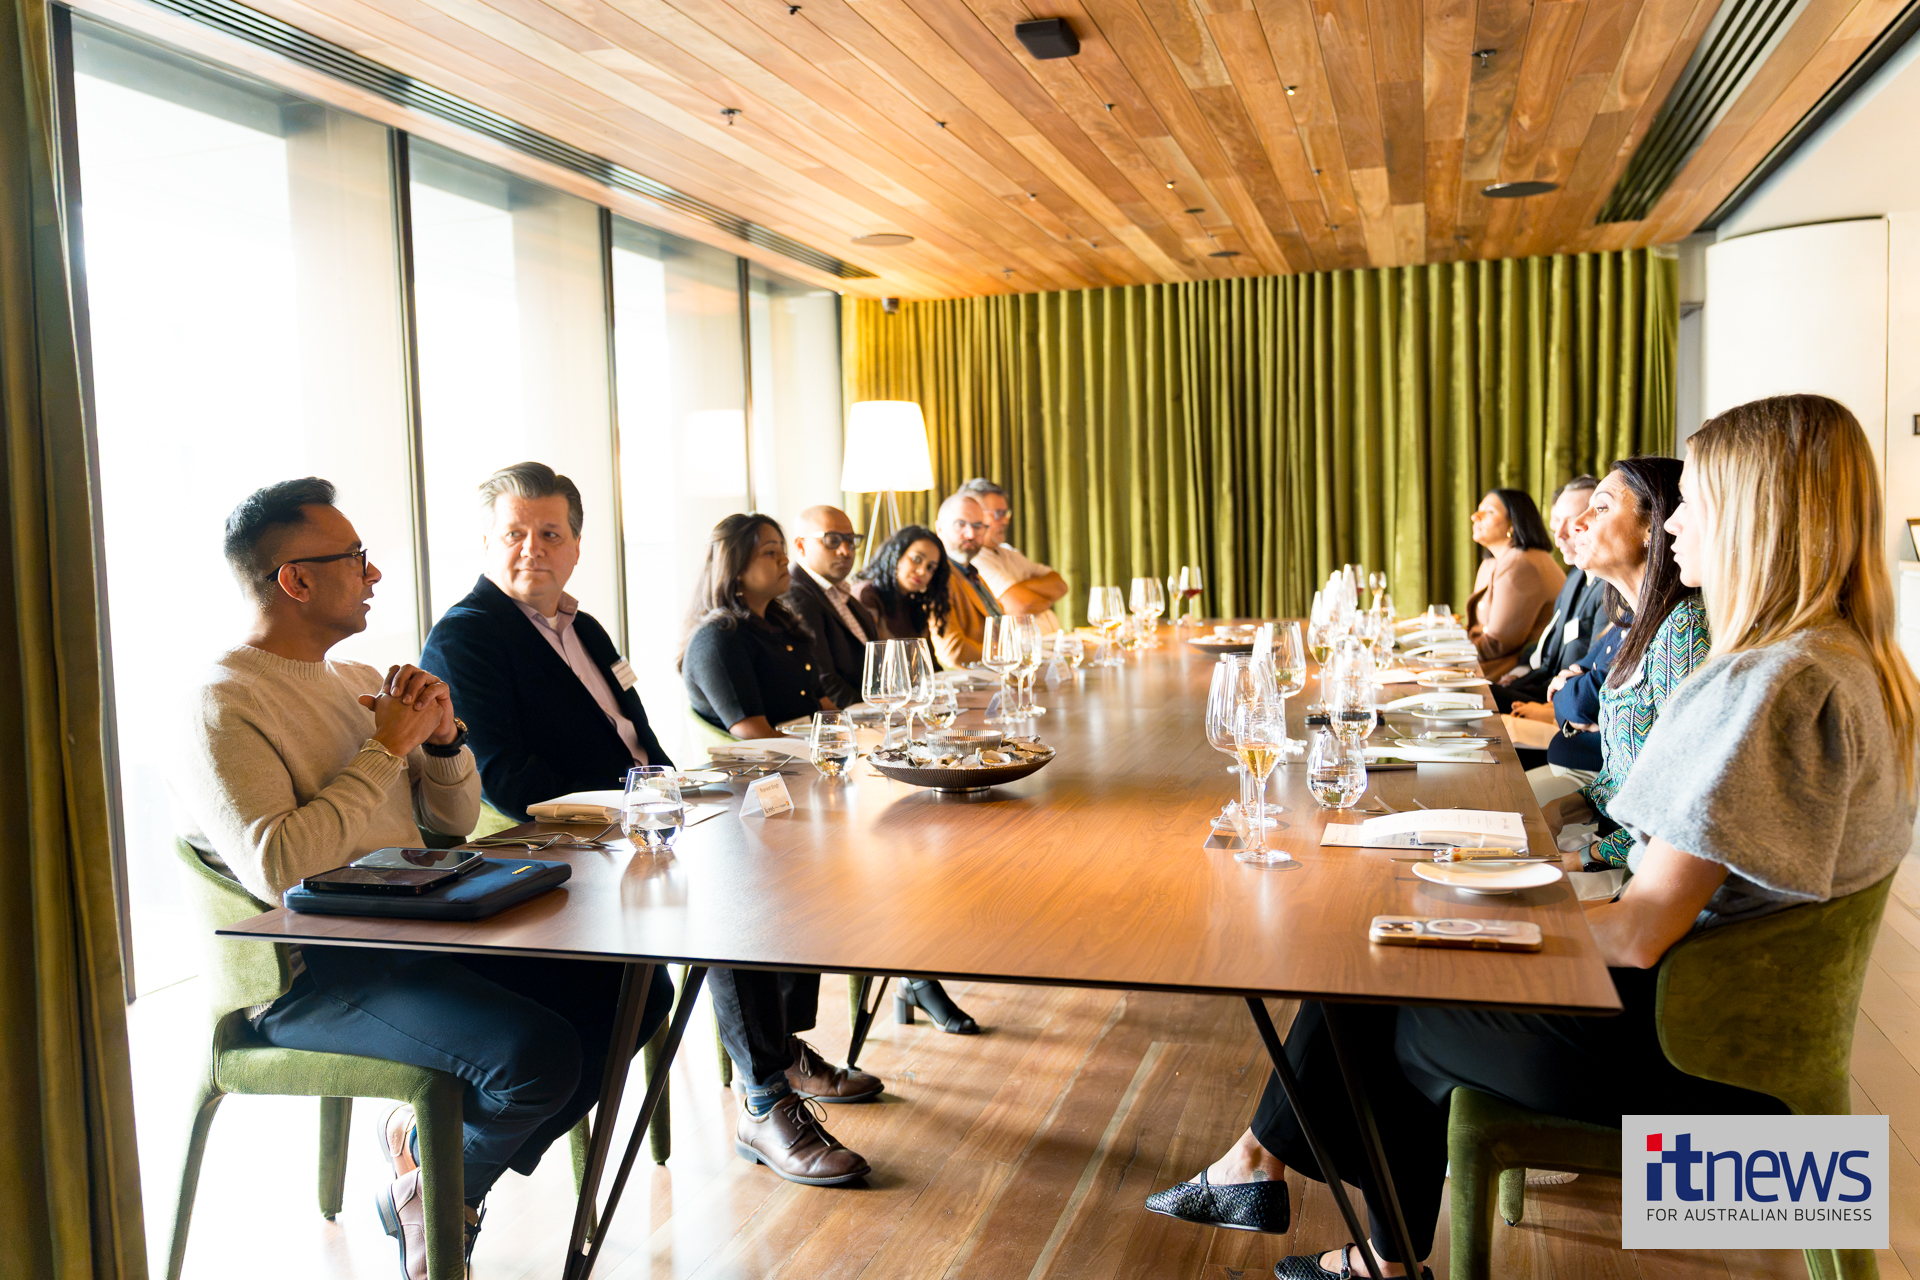
At a recent TechBest executive gathering in Melbourne, backed by Flipkart Commerce Cloud, prominent technology leaders came together to discuss the retail future, especially through the framework of AI-enhanced infrastructure. This meeting underscored the revolutionary possibilities of technology in transforming retail interactions, operational strategies, and income models.

Conversational AI and Smart Discovery

One significant subject was the deployment of conversational AI to elevate smart discovery. Byutilizing AI, retailers can enhance customer engagement, deliver tailored suggestions, and optimize the shopping journey. This approach not only cultivates customer loyalty but also elevates sales conversion ratios.

Composable Framework for Operational Flexibility

The conversation also explored the advantages of embracing composable frameworks. This flexible strategy enables retailers to rapidly respond to market fluctuations and consumer needs. By constructing and reconstructing various elements, companies can attain heightened adaptability and boost their operational efficacy.

Revenue Generation through Retail Media and Adaptive Pricing

Integrated retail media and adaptive pricing were emphasized as cutting-edge methods for generating new revenue streams. Retail media allows brands to connect directly with consumers on retail platforms, while adaptive pricing modifies prices instantaneously according to demand and supply dynamics, optimizing profitability.

Recap

The roundtable hosted by Flipkart in Melbourne yielded insightful perspectives on the changing retail environment. Key insights included the significance of AI-powered discovery, the flexibility provided by composable frameworks, and fresh revenue avenues through retail media and adaptive pricing.

Q&A

Q: How does conversational AI contribute to retail?

A: Conversational AI enhances customer interactions by providing tailored recommendations and streamlining the shopping process, potentially leading to increased sales and customer loyalty.

Q: What advantages does composable architecture offer to retailers?

A: Composable architecture grants flexibility and operational effectiveness by enabling retailers to swiftly respond to market changes using modular and adjustable systems.

Q: What do integrated retail media and adaptive pricing entail?

A: Integrated retail media permits brands to target consumers on retail platforms, whereas adaptive pricing modifies product pricing real-time based on market conditions, maximizing revenue opportunities.

Q: Why are these technological innovations crucial for the future of retail?

A: These innovations empower retailers to more effectively meet consumer expectations, enhance operational efficiency, and explore new revenue streams, positioning them for success in a fast-evolving market.

Court Services Victoria announces new Chief Digital and Innovation Officer


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Pauline Diano Takes on Role as New Technology Chief

Court Services Victoria names chief digital and innovation officer

Pauline Diano (Image credit: LinkedIn)

Quick Overview

  • Pauline Diano has been designated as Chief Digital and Innovation Officer at Court Services Victoria.
  • Diano possesses vast expertise in IT project management and digital transformation.
  • She has played a crucial role in the deployment of case management systems for Magistrates’ and Children’s Courts.
  • The CDIO position is a development from the former chief digital officer role.
  • Jorge Silveira was the most recent permanent chief digital officer, departing in March 2025.
  • Adam Todhunter held the interim digital leadership position before Diano’s official appointment.

Pauline Diano’s Rich Expertise

Pauline Diano has been an integral part of Court Services Victoria, leading essential IT initiatives and spearheading digital change. Her direction was particularly vital during the pandemic when digital systems became crucial for court functionality. Recently, she has been key in the introduction of a new case management system for Victoria’s Magistrates’ and Children’s Courts.

Shift to Chief Digital and Innovation Officer

Diano’s elevation to Chief Digital and Innovation Officer signifies a broadening of the prior digital leadership role at Court Services Victoria. This role is an advancement from the earlier chief digital officer position, which was last occupied by Jorge Silveira until March 2025. After Silveira’s exit, Adam Todhunter took on the acting digital director role until Diano’s recent appointment.

Path Ahead for Digital Innovation at Court Services Victoria

In her new capacity, Diano is set to guide the delivery of significant projects and manage strategic and operational efforts within the digital framework of Court Services Victoria. Her emphasis on technology and artificial intelligence is anticipated to propel the Courts into a groundbreaking phase of digital innovation.

Conclusion

Pauline Diano’s selection as Chief Digital and Innovation Officer at Court Services Victoria marks a strategic enhancement of the court’s digital leadership. With a solid foundation in IT projects and digital transformation, Diano is prepared to steer the courts through advancements in technology and innovative methodologies.

Q&A

Q: What is the importance of Pauline Diano’s appointment?

A: Diano’s appointment signifies a strategic enhancement and progression of the digital leadership role at Court Services Victoria, positioning the courts for improved technology integration and innovation.

Q: What qualifications does Pauline Diano have for her new role?

A: Diano brings significant experience in managing IT projects and digital transformation within Court Services Victoria, including pivotal online systems developed during the pandemic.

Q: How does the Chief Digital and Innovation Officer role differ from the prior role?

A: The CDIO role builds on the previous chief digital officer position by including a wider range of strategic and operational duties within Court Services Victoria’s digital sphere.

Q: Who held the position of the last permanent chief digital officer?

A: Jorge Silveira was the last permanent chief digital officer, leaving the post in March 2025.

Q: What significant initiatives has Pauline Diano led?

A: Diano has been at the forefront of major initiatives, including the rollout of a case management system for Victoria’s Magistrates’ and Children’s Courts.

Vic Labor Suggests Restrictions on AI and Biometric Monitoring in Employment Settings


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Victoria’s Labor Government Proposes to Regulate AI and Biometric Surveillance in Workplaces

Brief Overview

  • Victoria’s Labor government intends to limit AI and biometric surveillance in workplaces.
  • The suggested legislation aims to tackle AI bias and guarantee human involvement in hiring.
  • Biometric data collection will be confined to scenarios where there are no less intrusive alternatives.
  • Employees will be entitled to understand when they are being observed and what data is gathered.
  • Engagement between employers and staff is required before initiating any monitoring.
  • Under the proposed law, the sale of workplace surveillance data will be prohibited.

New Proposal for Workplace Surveillance from Victoria’s Labor Government

Vic Labor considers restrictions on workplace AI and biometric surveillance

Details of the Proposed Legislation

The Labor government of Victoria, under the leadership of Premier Jacinta Allan and Treasurer Jaclyn Symes, has revealed intentions to introduce a law aimed at regulating AI and biometric surveillance within workplaces. This initiative is part of a wider effort to promote ethical and equitable monitoring practices, contingent on Labor’s success in the upcoming state election in November 2026.

Tackling AI Bias in Hiring

A pivotal element of the proposed legislation is the aim to mitigate the risk of AI bias during recruitment. The law will mandate human participation in hiring choices to avert discrimination and ensure a fair recruitment process.

Restrictions on Biometric Data Gathering

While biometric technology is advantageous, it raises substantial privacy issues. The proposed law is set to constrain the collection of biometric data to cases where no less intrusive alternatives exist. Furthermore, using biometric data for emotional assessment will be barred, except for specific legitimate purposes, like monitoring driver fatigue.

Guaranteeing Employee Awareness and Approval

The legislation aims to empower workers by granting them the right to be informed when they are under surveillance and how the collected data will be utilized. Mandatory discussions between employers and employees will precede the implementation or modification of any monitoring techniques.

Ban on Selling Surveillance Data

To safeguard employee privacy, the proposed law will also prohibit the commercialization of workplace surveillance data. This initiative is designed to thwart the inappropriate use of personal information gathered through surveillance.

Comparison with Other Jurisdictions

The proposed law in Victoria will augment the existing workplace surveillance regulations in NSW and the ACT, providing slightly enhanced protections in specific areas. This alignment will ensure a unified strategy toward workplace surveillance across varying regions.

Conclusion

The legislation proposed by Victoria’s Labor government aims to oversee the application of AI and biometric surveillance in workplaces, addressing privacy concerns and ensuring equitable practices. By necessitating human involvement in hiring processes, restricting biometric data collection, and banning the sale of surveillance data, the government seeks to forge a balanced and ethical structure for workplace monitoring.

Frequently Asked Questions

Q: What is the primary objective of the proposed legislation?

A: The primary objective is to guarantee that workplace surveillance methods are ethical, fair, and conducted with employee agreement, addressing privacy issues and bias.

Q: How will AI bias in hiring be tackled?

A: The legislation mandates human inclusion in recruitment decisions to avert AI bias and ensure just hiring processes.

Q: Are there limitations on biometric data collection?

A: Yes, the collection of biometric data will be restricted to scenarios where no less intrusive options are available, and its use to interpret emotions will only be permitted for specific legitimate purposes.

Q: What entitlements will employees have under the proposed law?

A: Employees will possess the right to be aware when they are observed and what data is being collected, with required consultation prior to deploying any surveillance.

Q: Will the sale of surveillance data be permitted?

A: No, the proposed legislation will prohibit the sale of workplace surveillance data to ensure employee privacy is upheld.

Q: How does the proposed legislation stack up against laws in other states?

A: Victoria’s proposed law is crafted to enhance the existing laws in NSW and the ACT, providing slightly stronger protections in certain respects.

Microsoft Updates ‘RoguePlanet’ Defender for Zero-Day Issue, Fresh Vulnerabilities Identified by Researcher


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Microsoft Reinforces Windows Defender Against ‘RoguePlanet’ Zero-Day Vulnerability

Quick Overview

  • Microsoft resolves ‘RoguePlanet’, a significant zero-day flaw in Windows Defender.
  • Following the update, additional vulnerabilities have been identified by the researcher.
  • These include an information leak and a denial-of-service issue.
  • The newly found vulnerabilities have not yet been verified by Microsoft or assigned a CVE number.
  • The researcher, Nightmare Eclipse, has a track record of revealing various security vulnerabilities.

Tackling RoguePlanet Flaw

Microsoft has addressed a crucial zero-day vulnerability termed ‘RoguePlanet’ in its Windows Defender scanning engine. This flaw enabled local attackers to gain elevated privileges and potentially execute a SYSTEM-level shell. Rated 7.8 on the CVSS scale, this vulnerability was mitigated with an update to the Windows Defender Malware Protection Engine, currently at version 1.1.26060.3008.

Microsoft reinforces Windows Defender against 'RoguePlanet' zero-day vulnerability

New Worries: Additional Vulnerabilities

After the fix, the researcher known as Nightmare Eclipse brought attention to two more security concerns in Windows Defender. One issue involves an eight-byte information leak, reportedly originating from Microsoft’s defense-in-depth strategies. However, the leak appears not to impact standard user processes outside Windows kernel drivers.

The second problem includes a denial-of-service vulnerability. This flaw takes advantage of the Defender’s caching mechanism for Zone.Identifier, potentially causing disk exhaustion. The researcher illustrated this by establishing a rogue SMB server to manipulate Defender’s file handling, leading to crashes and excessive disk space usage.

Researcher Background and Prior Discoveries

Nightmare Eclipse, also referred to as Chaotic Eclipse, has a notable history of identifying vulnerabilities within Microsoft products. Past discoveries encompass the BlueHammer, RedSun, and UnDefend vulnerabilities, all of which were exploited in the wild prior to patch releases. These findings are included in CISA’s Known Exploited Vulnerabilities database.

Microsoft initially condemned the researcher’s disclosure tactics but later rescinded legal threats after facing criticism from the security community.

Conclusion

While Microsoft has effectively patched the RoguePlanet vulnerability, ongoing discoveries by researchers like Nightmare Eclipse underscore the dynamic nature of cybersecurity risks. Users are urged to keep their systems updated and remain alert to possible exploits.

Q: What is the RoguePlanet vulnerability?

A: RoguePlanet is a zero-day exploit present in Windows Defender that enables privilege escalation, which may lead to SYSTEM-level shell execution.

Q: How has Microsoft tackled the RoguePlanet issue?

A: Microsoft has mitigated the vulnerability by updating the Windows Defender Malware Protection Engine to version 1.1.26060.3008.

Q: Are there any additional vulnerabilities associated with the RoguePlanet patch?

A: Indeed, the researcher has identified an information leak and a denial-of-service vulnerability subsequent to the patch.

Q: Has Microsoft verified the new vulnerabilities?

A: At this moment, Microsoft has not confirmed these new discoveries or assigned CVE identifiers to them.

Q: Who is the researcher responsible for these findings?

A: The vulnerabilities were uncovered by a researcher known as Nightmare Eclipse or Chaotic Eclipse.

Q: How has the security community reacted to Microsoft’s actions?

A: The community expressed backlash after Microsoft initially threatened legal measures against the researcher, prompting a withdrawal of those threats.

Q: What actions should users take to ensure their safety?

A: Users should routinely update their systems and antivirus software to the latest versions to protect against known vulnerabilities.

Pentagon Suspends Cyber Audit Regulation Associated with Supplier Exits


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • The Pentagon pauses Phase 2 of the Cybersecurity Maturity Model Certification (CMMC) for defense contractors.
  • Smaller suppliers raised concerns regarding expensive compliance and lengthy audit processes.
  • The suspension is intended to keep innovative firms within the defense supply network.
  • A 60-day assessment along with a new CMMC Reform Task Force will offer recommendations.

Pentagon Suspends Cybersecurity Certification to Retain Suppliers

The United States Department of Defense has opted to suspend the next phase of its Cybersecurity Maturity Model Certification (CMMC) initiative, which has been a significant worry for defense contractors, especially smaller providers. This move comes in response to growing pressure from industry leaders who have claimed that the compliance mandates were overly burdensome, prompting some firms to rethink their participation in the defense supply network.

Pentagon pauses cyber audit rule blamed for supplier exits

Insight into the CMMC Program

Initiated in November 2025, the CMMC program is designed to protect controlled unclassified information within the defense industry. Initially, contractors were required to complete stringent third-party audits to gain certification, but the rollout of Phase 2, set for November 10, has been halted. The current emphasis will be on Level 1 or Level 2 self-assessments.

Concerns from Suppliers and Financial Strain

Small to medium-sized aerospace and defense suppliers have expressed dissatisfaction with compliance expenses, which can soar into the hundreds of thousands. These financial burdens, along with extended wait times for third-party assessments, have prompted some suppliers to rethink their involvement in defense contracting.

Feedback from the Industry and Legal Sector

Legal experts within the industry have raised alarms that strict regulations might inhibit participation from lower-tier suppliers and complicate matters for international firms navigating diverse data-privacy regulations. Pentagon CIO Kirsten Davies has recognized these challenges, highlighting the necessity for a reassessment of the program.

Pentagon’s Strategic Action

Pentagon Under Secretary of War for Acquisition and Sustainment Michael Duffey emphasized the department’s goal to expedite weapons production and sustain a competitive landscape within the defense supply network. The suspension is viewed as a strategy to reduce “crippling costs” and encourage innovation.

Establishment of the CMMC Reform Task Force

A new CMMC Reform Task Force has been set up to tackle these issues, drawing upon industry feedback collected via a public inquiry. The task force is expected to submit recommendations within a 60-day timeframe.

Conclusion

The Pentagon’s choice to halt the upcoming phase of the CMMC program signifies a strategic pivot to alleviate supplier concerns regarding high compliance expenses and protracted audit delays. By pausing the program, the Defense Department aims to attract innovative companies into the defense supply network and foster a competitive market atmosphere. The newly constituted CMMC Reform Task Force will be instrumental in defining the future of the certification process.

Q: What is the Cybersecurity Maturity Model Certification (CMMC)?

A: The CMMC is a program launched by the US Department of Defense to safeguard sensitive information within the defense sector by mandating contractors to adhere to specific cybersecurity standards.

Q: Why was the Phase 2 implementation of the CMMC program suspended?

A: The suspension was put in place following feedback from smaller suppliers who found the compliance expenses and audit wait periods to be a significant burden, jeopardizing their involvement in defense contracts.

Q: What is the role of the newly established CMMC Reform Task Force?

A: The task force is intended to collect industry input and present suggestions for enhancing the CMMC program within a 60-day timeframe.

Q: How do self-assessments differ from third-party audits in the CMMC program?

A: Self-assessments allow contractors to internally assess their adherence to cybersecurity standards, while third-party audits involve external validation, which often entails higher costs and extended wait times.

Q: What effect is the suspension of Phase 2 expected to have on the defense supply network?

A: The suspension is anticipated to ease financial pressures on suppliers, maintain innovative firms in the market, and uphold a competitive defense supply chain.

Pokémon GO City Safari Scheduled to Launch in Brisbane This September


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Read

  • Brisbane is set to host the Pokémon GO City Safari this September.
  • The event covers the entire city, emphasizing exploration and community interaction.
  • Special Pokémon, including shiny forms, will be featured throughout the weekend.
  • An exclusive event hub will be located at Queen Street Mall, offering physical merchandise.
  • Optional gameplay enhancements are available for a richer experience.
  • Tickets are on sale now, priced at $17 AUD for one day.

Brisbane Ready for Pokémon GO City Safari

Following the successful Pokémon GO anniversary in Melbourne, Queensland is preparing for a real-world experience with the Pokémon GO City Safari arriving in Brisbane. This September, the River City will be transformed into a large, interactive Pokémon environment, attracting trainers from all over Australia for a weekend event.

Discover Brisbane with City Safari

Contrary to typical events that are limited to parks, City Safari promotes exploration throughout Brisbane. Trainers will have the opportunity to roam the city’s riverfront areas, lively neighborhoods, and cultural attractions, all while catching Pokémon and connecting with other fans.

Event Hub and Special Merchandise

The centerpiece of the event will take place at Queen Street Mall. Here, trainers can gather exclusive items such as Pokémon GO City Safari Pikachu Visors and sticker packs, making it an ideal meeting spot for trades and launching your Pokémon journey.

Brisbane Pokémon GO City Safari adventure featuring unique Pokémon.
Unique Pokémon will be accessible during the event. (Image: Supplied)

Event Details: Dates and Times

Save the dates for the end of September:

  • Location: Queen Street Mall, Brisbane
  • Date: Saturday, September 26, and Sunday, September 27, 2026
  • Hours: 9:00 am to 6:00 pm AEST each day

Event Highlights: Gameplay, Stamp Rallies, and Spawns

Participants can look forward to a variety of exclusive in-game experiences. The main attraction is the GO Stamp Rally, where trainers visit PokéStops throughout Brisbane to gather stamps, providing a chance to encounter an exclusive Eevee wearing an explorer hat.

  • Special Research: Partner with Professor Willow for unique research encounters featuring Eevee and its evolutions.
  • Wild Spawns: Anticipate an influx of special Pokémon, including the globally featured Mudbray, with increased shiny chances.
  • Ticket Holder Benefits: Enjoy advantages such as 4-hour Lure Modules, up to five Special Trades daily, and a “Tiny Compass” keepsake.
Shiny Eevees accessible during Brisbane Pokémon event.
You may encounter unique shiny Eevees during the event. Evolutions can solely be achieved by evolving Eevee. (Screenshot by TechBest)

Enhance Your Weekend with Add-Ons

For those aiming to maximize their experience, Niantic provides gameplay add-ons:

  • Raid Lover: Enjoy up to 12 free Raid Passes daily with added XP, Candy, and Candy XL.
  • Egg-thusiast: Reduces Egg hatch distance and amplifies XP, Stardust, and Candy.
  • Extra Day Add-On: Upgrade for citywide gameplay and bonuses across both days.

Ticket Pricing and Purchase Information

Tickets are currently available on a first-come, first-served basis:

Single-Day Ticket: $17 AUD (including taxes and fees). Raid Lover and Egg-thusiast extras are $8 AUD each, while the Extra Day Add-On costs $12 AUD.

How to Reserve Your Spot:

Buy tickets through the official Pokémon GO City Safari Website or within the Pokémon GO app. Go to the Main Menu, select ‘Events’, choose the Brisbane City Safari, and select your date and add-ons. Tickets can also be purchased for in-game friends who have at least Great Friends status.

With a fantastic weekend ahead, Australian trainers should grab their badges early to ensure they don’t miss out. Visit the website for further information on other international events taking place in Boston, Lisbon, Marseille, Munich, and Rio de Janeiro.

Overview

The Pokémon GO City Safari in Brisbane is set to be an incredible experience for trainers across Australia. With citywide exploration, unique Pokémon encounters, and engaging community activities, it’s an event not to be missed by any Pokémon fan. Make sure to take advantage of this chance to catch them all in the heart of Brisbane!

Frequently Asked Questions

Q: What is Pokémon GO City Safari?

A: It’s a citywide Pokémon GO event in Brisbane, centering on exploration and community engagement activities.

Q: When and where will the event take place?

A: The event will occur on September 26-27, 2026, at Queen Street Mall, Brisbane, with gameplay covering the entire city.

Q: What exclusive Pokémon will be available?

A: Trainers will have opportunities to encounter special Pokémon such as Mudbray and Eevee in an explorer hat, featuring boosted shiny rates.

Q: Are there add-ons for the event?

A: Yes, optional add-ons like Raid Lover and Egg-thusiast are available to enhance your gaming experience.

Q: How can tickets be purchased?

A: Tickets can be obtained via the official Pokémon GO City Safari website or in the Pokémon GO app.

Q: What are the costs of tickets?

A: Single-day tickets cost $17 AUD, with add-ons such as Raid Lover and Egg-thusiast priced at $8 AUD each, and the Extra Day Add-On at $12 AUD.