Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 52 of 187

“ACSC Notifications: ‘ClickFix’ Fraud Tricks Users into Self-Hacking”


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Concise Overview

  • The Australian Cyber Security Centre (ACSC) alerts users about a new ClickFix scheme aimed at Windows users featuring Vidar Stealer malware.
  • ClickFix deceives users into jeopardizing their systems via counterfeit Cloudflare CAPTCHA cues.
  • Compromised WordPress websites are utilized to transmit harmful commands through injected JavaScript.
  • Apple and Microsoft are implementing measures to safeguard users from these attack methods.
  • ACSC advises updating WordPress sites and limiting the execution of untrusted applications.
ACSC alerts about 'ClickFix' scheme causing users to self-hack

What Exactly is ClickFix?

The ClickFix strategy is an advanced form of social manipulation that takes advantage of user trust by encouraging them to execute detrimental commands on their own machines. This tactic has become well-known as attackers deploy fake CAPTCHA verifications to spread malware such as Vidar Stealer.

Mechanism of the Attack

Perpetrators infiltrate legitimate Australian corporate websites operating on WordPress by embedding harmful JavaScript code. This code, triggered by user interaction with a fraudulent CAPTCHA, copies a malicious PowerShell command to the user’s clipboard. The attack subsequently prompts the victim to execute this command with administrative permissions, thus compromising their own device.

Consequences and Advice

The ACSC has stressed the importance for government bodies, businesses, and individuals to prevent untrusted scripts from executing. Administrators of WordPress should confirm that their sites are updated and devoid of outdated plugins to avert compromise.

Technological Defenses

Both Apple and Microsoft are proactively addressing ClickFix threats. Apple has improved its XProtect anti-malware tool and rolled out new security notifications in macOS. Microsoft has documented the progression of the attack and is enhancing its Defender software to provide stronger protection for users.

Overview

The ClickFix scam poses a considerable threat to users who inadvertently jeopardize their own systems. With the ACSC’s recommendations and the proactive initiatives from tech companies, users can enhance their defense against this escalating risk.
Q&A

Q: What exactly is Vidar Stealer?

A: Vidar Stealer refers to a type of malware that extracts confidential data from infected systems, including passwords and financial information.

Q: How can I safeguard my WordPress site from breach?

A: Ensure your site is consistently updated, eliminate any unused or obsolete themes and plugins, and adopt robust security protocols.

Q: What steps should I take if I suspect a ClickFix breach?

A: Disconnect from the internet immediately, perform a comprehensive antivirus scan, and obtain professional cybersecurity help.

Q: How does the deceptive CAPTCHA trick function?

A: Users encounter a counterfeit CAPTCHA that looks authentic, but upon interaction, it transmits harmful commands to the clipboard.

Q: Why is ClickFix especially perilous?

A: It manipulates user trust and uses social engineering to compel users to run harmful commands themselves, evading numerous security safeguards.

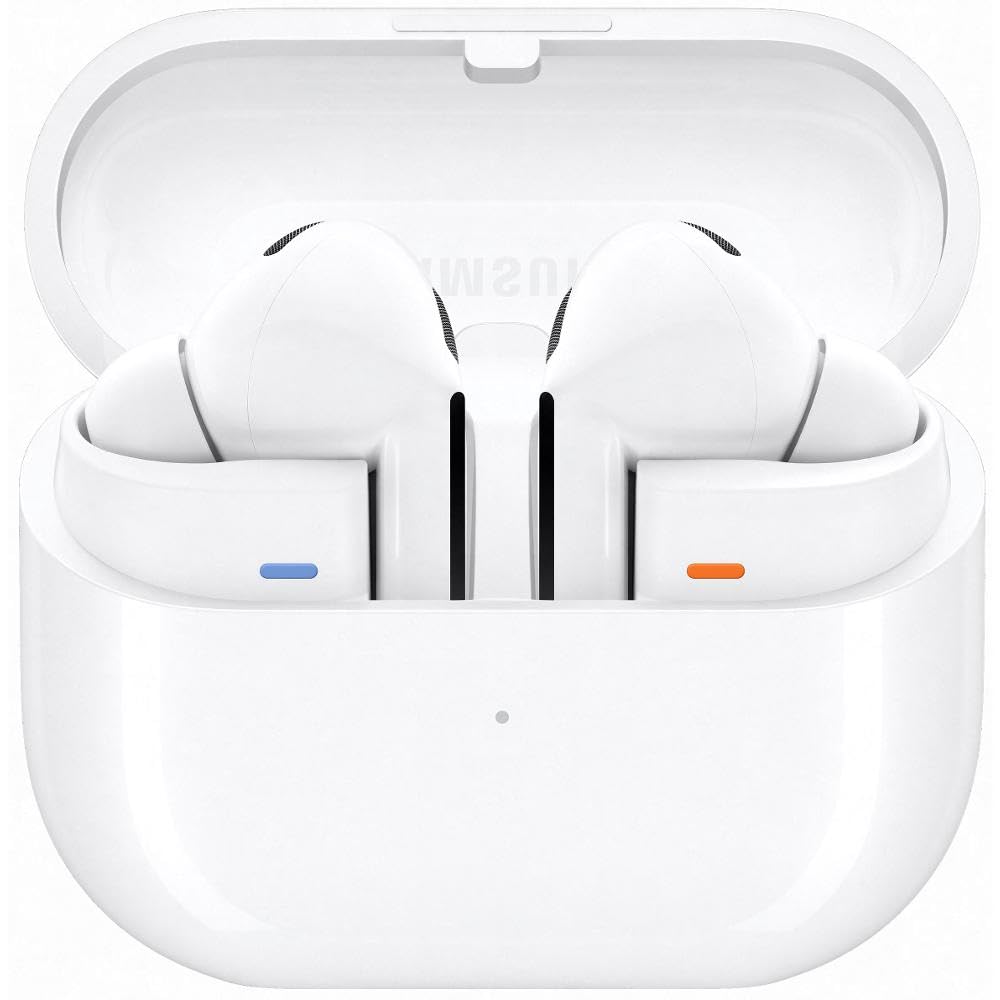
Samsung Galaxy Buds3 Pro Wireless Bluetooth Headphones Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Samsung Galaxy Buds3 Pro Wireless Bluetooth Headphones, Active Noise Canceling (ANC), Adaptive Noise Canceling, 360 Audio, in-Ear Headphones with Hi-Fi Sound, Silver, Includes Anymode Clear Cover

‘Cloud Worm ‘PCPJack’ Takes Control of TeamPCP Hacker Network’


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Cloud Worm ‘PCPJack’ Takes Over TeamPCP Hacker Network

Quick Summary

  • PCPJack is a recently identified malware aimed at cloud infrastructures.
  • It eliminates malicious scripts from TeamPCP and deploys its own.
  • PCPJack captures credentials from multiple services and seeks lateral movement.
  • Distinct from other malware, it refrains from participating in cryptocurrency mining.
  • The malware takes advantage of services like Docker, Kubernetes, and MongoDB.
PCPJack cloud worm commandeers TeamPCP hacker infrastructure

Overview of PCPJack

PCPJack, a highly advanced cloud-based worm, has been discovered by researchers at SentinelLabs. This malware exhibits a unique ability: it removes the malicious code used by the infamous TeamPCP hackers and substitutes it with its own. Detected through Google’s VirusTotal malware detection service, PCPJack sets up a Python virtual environment to extend its capabilities.

Operations and Targets

PCPJack is tailored to extract credentials from a variety of services, encompassing cloud, container, developer, productivity, and financial solutions. The malware strives to disseminate itself across exposed cloud infrastructures and performs lateral movement within targeted environments. The services PCPJack focuses on include Docker, Kubernetes, Redis, MongoDB, RayML, and susceptible web applications.

Monetization Strategies

Unlike certain malware that engages in cryptocurrency mining efforts, PCPJack pursues monetization through different methods. It partakes in the resale of compromised access, credential theft, fraud, spam, and extortion, rendering it a flexible menace in the cybercriminal ecosystem.

TeamPCP’s Ascent and Weakness

TeamPCP, a hacking collective noted for breaching the Aqua Security Trivy vulnerability scanner, has been implicated in various prominent attacks. These involve the CanisterWorm supply chain breach and a trojanized variant of the LiteLLM proxy. The rise of PCPJack suggests potential insider knowledge regarding TeamPCP’s operations, as conjectured by SentinelLabs.

Security Issues and Insights

Despite the advanced nature of PCPJack’s code, SentinelLabs uncovered several security flaws. These include the lack of encryption for the token associated with the attacker’s Telegram command and control (C2) bot, along with a credential decryption key. Such oversights reveal possible vulnerabilities that could be utilized to lessen the threat posed by PCPJack.

Conclusion

PCPJack signifies a noteworthy advancement in the malware arena, expertly targeting cloud infrastructures with accuracy and effectiveness. Its capability to eliminate pre-existing malicious code and supplant it with its own renders it a formidable foe. Although it does not partake in cryptocurrency mining, its monetization via credential theft and fraud presents considerable dangers to impacted organizations.

Frequently Asked Questions

Q: What is PCPJack?

A: PCPJack is a newly identified malware that targets cloud infrastructures by eliminating existing malicious code and inserting its own.

Q: How does PCPJack function?

A: PCPJack sets up a Python virtual environment and retrieves modules to extract credentials from various services, seeking to spread through cloud infrastructures.

Q: Which services are targeted by PCPJack?

A: PCPJack targets services such as Docker, Kubernetes, Redis, MongoDB, RayML, and other susceptible web applications.

Q: What methods does PCPJack use for monetization?

A: PCPJack monetizes through the resale of compromised access, credentials theft, fraud, spam, and extortion, instead of resorting to cryptocurrency mining.

Q: Which group was targeted by PCPJack?

A: PCPJack targeted the TeamPCP hacker network, recognized for its sophisticated assaults on diverse platforms.

Q: Did SentinelLabs discover any weaknesses in PCPJack?

A: Yes, SentinelLabs identified certain security oversights, such as the lack of encryption for specific tokens and keys, which could be exploited to diminish PCPJack’s threat.

Telstra Notifies Australians About LEO Satellite 000 Calls


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Challenges with Telstra and LEO Satellite 000 Calls

Brief Overview

  • Telstra alerts that LEO satellite constellations are unprepared for 000 calls.
  • LEO satellites require a “critical mass” for dependable emergency communication.
  • The UOMO commitments might need to be postponed until at least late 2028.
  • Telstra has noted a rise in outages tied to LEOsat backhaul.
  • The absence of LEOsat caused major community effects on the availability of emergency calls.

Telstra’s Apprehensions Regarding LEO Satellite Abilities

Telstra has expressed apprehensions about the preparedness of low earth orbit (LEO) satellite constellations to facilitate trustworthy 000 emergency calls. The telecommunications leader has notified the federal government that these systems must attain a “critical mass” to ensure sufficient support for emergency services.

The challenges faced by Telstra for LEO satellite 000 calls

The Importance of Achieving a Critical Mass

Telstra’s alert corresponds with its earlier guidance that 5G non-terrestrial network standards are still under development. The merger of terrestrial and non-terrestrial networks is crucial for delivering reliable SMS, voice, and data services. Until LEOsat densities reach necessary levels, consistent emergency communication will continue to be difficult.

Postponements in UOMO Commitments

The telecommunications provider recommends pushing back the Universal Outdoor Mobile Obligation (UOMO) until a complete ecosystem, which includes adequate LEO satellites and infrastructure, is established. Telstra foresees that this may not be realized until late 2028.

Effects of LEOsat Services on Emergency Communication

Telstra’s dealings with Eutelsat’s OneWeb LEOsat constellation reveal the obstacles encountered. Transitioning from geostationary to LEOsat backhaul resulted in a 43% rise in mobile tower outages. These outages brought considerable disruptions to the availability of 000 calls, with certain base stations unable to manage emergency calls for up to 35 minutes each day.

Conclusion

Telstra’s cautious outlook on the preparedness of LEO satellites for emergency services highlights the necessity for a well-rounded infrastructure before depending on them for crucial communication. As Australia advances its telecommunications capabilities, ensuring sturdy and dependable emergency call systems remains a principal concern.

Q&A

Q: What concerns does Telstra have regarding LEO satellites?

A: Telstra contends that LEO satellites have not achieved the “critical mass” crucial for reliable 000 emergency calls.

Q: What does the Universal Outdoor Mobile Obligation (UOMO) entail?

A: UOMO is a governmental initiative aimed at ensuring mobile network availability in outdoor environments, including for emergency services.

Q: When does Telstra forecast the complete ecosystem for LEO satellites will be ready?

A: Telstra expects that the essential infrastructure might not become available until late 2028.

Q: How have LEO satellites influenced Telstra’s services?

A: The transition to LEO satellites led to increased mobile tower outages, affecting the availability of emergency calls.

Q: What actions has Telstra taken to address these issues?

A: Telstra has halted further rollout of LEOsat backhaul until additional satellites are deployed.

Q: What are the consequences of postponed UOMO obligations?

A: Delays indicate that enhancements in outdoor mobile coverage and the reliability of emergency calls may take longer to realize.

Microsoft may forsake its 2030 clean energy objective


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Microsoft’s Clean Energy Goals: Confronting New Challenges

Microsoft's clean energy ambitions under review

Brief Overview

  • Microsoft is reassessing its clean energy target for 2030 in light of surging AI infrastructure needs.
  • The technology leader is investigating various energy alternatives, including nuclear and natural gas options.
  • No definitive resolution has been reached regarding the clean energy objective.
  • Microsoft aims to persist in its sustainability initiatives with new developments in Wisconsin.
  • AI-powered data centre growth is transforming energy strategies across the sector.

Data Centres and Energy Needs

The rapid growth of data centres, fueled by the increasing demands of AI technologies, is putting pressure on Microsoft’s capability to fulfill its clean energy commitment for 2030. The firm’s once ambitious goal, established prior to the AI surge, now confronts logistical and financial obstacles.

Adapting to the AI Landscape

Microsoft, along with rivals such as Amazon and Alphabet, is making substantial investments in AI infrastructure, including offerings like Copilot and Azure cloud services. These developments require considerable energy resources, prompting a reassessment of clean energy timelines.

Exploring Alternative Energy Sources

In response to the rising energy demands, Microsoft is investigating various energy alternatives. The company has formed partnerships with We Energies to implement 1.2 gigawatts of carbon-free energy projects by 2028, while also looking into nuclear energy options such as the Three Mile Island facility in Pennsylvania.

Industry Developments and Challenges

The increase in data centre construction has led to a rise in natural gas consumption due to its faster implementation compared to renewable energy sources. This trend underscores a larger industry challenge of reconciling rapid technological progress with sustainability goals.

Conclusion

Microsoft is currently in the process of reassessing its 2030 clean energy objectives due to the substantial energy requirements stemming from AI infrastructure expansion. While the organization remains dedicated to sustainability, it is exploring a blend of energy solutions, including renewables and nuclear power, to address future needs.

Q&A

Q: What was Microsoft’s initial 2030 clean energy target?

A: Microsoft’s initial target was to align its entire hourly electricity consumption with renewable energy acquisitions by 2030.

Q: What is prompting Microsoft to reconsider its clean energy objectives?

A: The swift development of AI technologies and the resulting energy requirements are causing Microsoft to reevaluate the practicality of its 2030 target.

Q: Are there current projects in place to advance Microsoft’s clean energy goals?

A: Yes, Microsoft has commitments to establish 1.2 gigawatts of carbon-free energy initiatives in Wisconsin by 2028.

Q: What alternative energy sources is Microsoft looking into?

A: Microsoft is considering nuclear energy, as shown by its power agreement with Constellation Energy, while also increasing its reliance on natural gas.

Q: How does Microsoft’s situation stack up against other tech corporations?

A: Similar to Microsoft, other major tech companies like Amazon and Alphabet are also making significant investments in AI infrastructure, which influences their energy policies.

Q: What role does the Three Mile Island nuclear facility play in Microsoft’s energy strategy?

A: Microsoft has entered a power agreement to aid in the revival of a unit at the Three Mile Island nuclear plant, reflecting its interest in nuclear energy initiatives.

Defence Prepared to Unveil Secret Space Data Archive


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Concise Overview

  • Defence has finalized a $37 million agreement with Bluestaq to create a classified space data repository.
  • The Unified Data Library (UDL) is aimed at enhancing space situational awareness.
  • This initiative builds on a successful non-classified trial held in 2023.
  • The UDL will monitor and categorize artificial objects in space, including satellites and debris.
  • The contract is effective until mid-2028 and is a component of the SPACE 9360 initiative.

Defence’s Tactical Step into Space Situational Awareness

The Defence Department of Australia is significantly advancing its space capabilities with the creation of a classified Unified Data Library (UDL). This project, valued at $37 million and in partnership with Bluestaq, seeks to strengthen the nation’s space situational awareness, which is essential as the space environment becomes more intricate.

Advancing Proven Technology

The UDL, a concept first tested on a non-classified basis in 2023, utilizes technology pioneered by Bluestaq. This system, already operational with US agencies, has shown its ability to effectively manage extensive volumes of space data. The shift to a classified version represents a major enhancement in Australia’s capacity for space data management.

The Significance of Space Situational Awareness

Considering space is increasingly perceived as congested and competitive, the capacity to monitor and classify artificial objects like satellites and space debris is vital. The UDL will equip Defence with extensive data, including launch alerts, tracking and position information, and conjunction evaluations. These abilities are crucial for upholding national security and ensuring operational preparedness.

Successful Non-Classified Trials

The trial of the non-classified UDL by the Australian Defence Department commenced in December 2023. The success of this trial has opened avenues for a secure, Australian-managed system that can process large data volumes. This system is now fully sanctioned and incorporated into long-term operations within the SPACE 9360 initiative, boosting Australia’s comprehension of space-based activities.

Future Opportunities and Collaborations

The agreement with Bluestaq, Defence’s largest engagement with the vendor, lasts until mid-2028. This collaboration aims to provide continuous project support services for implementing the classified UDL within Defence’s secure networks. This initiative not only builds upon the achievements of the non-classified UDL but also indicates a strengthening partnership between Defence and Bluestaq.

Conclusion

The Australian Defence Department is progressing its capabilities in space situational awareness through a $37 million project for a classified data repository in collaboration with Bluestaq. This initiative is part of a larger strategy to bolster national security and operational efficiency in an increasingly competitive space landscape.

Q: What is the aim of the Unified Data Library (UDL)?

A: The UDL is intended to enhance space situational awareness by cataloguing and tracking artificial entities in space, such as satellites and debris.

Q: Why is space situational awareness crucial for Defence?

A: Space situational awareness is essential as space becomes more crowded and competitive. It safeguards national security and supports operational readiness.

Q: What does the $37 million agreement with Bluestaq entail?

A: The agreement encompasses the implementation of a classified version of the UDL, project support services, and the system’s integration into Defence’s secure networks.

Q: In what way does this project build on previous efforts?

A: The classified UDL is based on a successful non-classified trial conducted in 2023, which highlighted the system’s capability to manage large quantities of space data.

Q: What are the long-term objectives of the SPACE 9360 initiative?

A: The SPACE 9360 initiative aims to enhance how Australia’s Space Command perceives and oversees space-related activities, improving national security capabilities.

Google’s Leading Scientist Cautions That EU Data Regulations May Endanger User Privacy


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Google Scientist Raises Alarm on EU Data Regulations

Quick Overview

  • Google cautions that EU data-sharing legislation might threaten user privacy.
  • The EU seeks to ensure equitable competition within the digital marketplace.
  • Google’s AI team reveals possible privacy weaknesses.
  • The EU is set to finalize data-sharing protocols soon.
  • Google risks facing fines for failing to comply.

Context on EU’s Data-Sharing Initiative

The European Commission has been imposing stricter rules on major tech companies to enhance competition and offer consumers additional options. However, this approach has drawn criticism from the US authorities. A major proposal on the table mandates that tech giants like Google share search engine data with rivals like OpenAI. Such data encompasses search rankings, queries, clicks, and impressions.

Google’s Privacy and Security Apprehensions

Google scientist warns of privacy risks from EU regulations

Sergei Vassilvitskii, a prominent scientist from Google, voiced substantial concerns regarding the Commission’s strategy for data anonymization, indicating that it may not adequately safeguard user privacy. The AI red team at Google, responsible for pinpointing vulnerabilities, was able to re-identify individuals in under two hours, revealing notable risks.

Consequences for Major Tech Companies

If Google does not adhere to the upcoming regulations by July 27, it may incur fines as stipulated by the Digital Markets Act, aimed at diminishing the dominance of large tech firms. Non-compliance could lead to penalties of up to 10% of Google’s total annual revenue, posing a considerable financial threat to the organization.

Conclusion

As the EU prepares to finalize its data-sharing regulations, Google’s apprehensions underscore the fragile equilibrium between encouraging competition and ensuring user privacy. The results of these negotiations will significantly impact both technology firms and consumers.

Questions & Answers

Q: What are the EU’s intentions regarding the data-sharing proposal?

A:

The EU aspires to promote fair competition and provide consumers with increased options by mandating that dominant tech firms share data with smaller competitors.

Q: What worries Google about the proposal?

A:

Google is concerned that the anonymization techniques suggested by the EU might not be sufficiently effective, potentially enabling personal information to be traced back to specific individuals.

Q: What could occur if Google disregards the new regulations?

A:

If Google does not execute the necessary protocols, it may face significant penalties under the Digital Markets Act, amounting to up to 10% of its global revenue.

Q: In what way has Google’s AI team influenced the conversation?

A:

Google’s AI red team illustrated that the proposed data anonymization could be circumvented, successfully re-identifying users in under two hours, which raises serious concerns regarding privacy.

Q: When is the EU expected to finalize the data-sharing regulations?

A:

The EU is anticipated to finalize the regulations on data-sharing in the near future, after considering input from stakeholders.

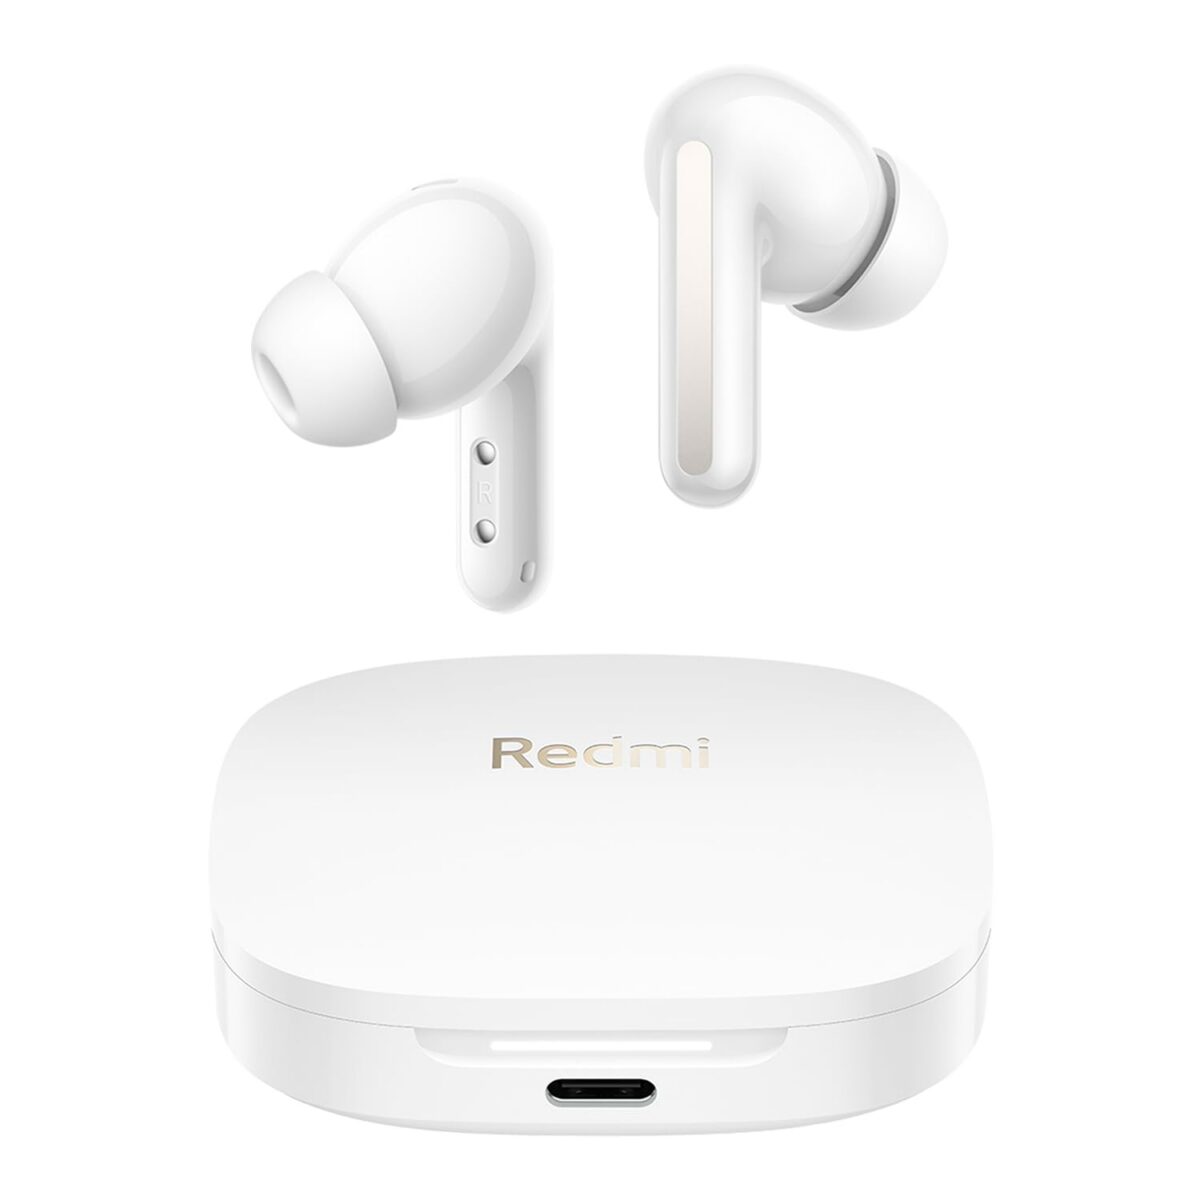
Xiaomi Redmi Buds 6-Cloud White Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Xiaomi Redmi Buds 6-Cloud White

Victorian Government Designates $106M for IT Revamp to Assist Communities and Families


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Victoria Gov’s Ambitious IT Investment for Community and Family Assistance

Victoria Gov’s Ambitious IT Investment for Community and Family Assistance

Overview

  • Victoria designates $106 million for the transformation of IT systems in community and family services.
  • Notable investments in technology for emergency services, including Victoria Police.
  • The education sector will gain from cloud transitions and upgrades to technology platforms.
  • Extensive enhancements are planned for Victoria’s Triple Zero telephony system.
  • Extra funding allocated for cyber security across multiple departments.

Revamping Community and Family Services

In a significant initiative to upgrade its digital resources, Victoria’s Department of Families, Fairness and Housing is slated to receive a $106 million infusion over the coming three years. This effort is part of a larger $126 million funding aimed at improving services for vulnerable children, youth, and families.

The transformation will follow a phased strategy to modernise digital infrastructures, beginning with the replacement of antiquated reporting and information systems. This initial step will establish a strong foundation for a future-ready case management system, chiefly in child protection services.

Vic gov invests $106m in IT transformation for communities and families

Enhancements for Emergency Services

The state budget details substantial investments in technology for emergency services. Victoria Police will benefit from upgrades, with $14 million set aside for 3000 mobile devices and improved evidence recording tools. This ensures vital information is easily accessible in the field, enhancing police operational capabilities.

Additional financial commitments include $25.9 million for assets and $15 million for operational costs related to refreshing IT infrastructure and advancing cyber security, protecting sensitive data and supporting frontline initiatives.

Upgrades in Education and Public Services

The education sector is poised for benefits, with a budget of $17.2 million allocated for transitioning IT infrastructure to the cloud, facilitating smoother operations and minimizing cyber security threats. Educational institutions will switch to centrally managed technology platforms to boost security and productivity.

Moreover, $5 million is designated for Service Victoria to innovate new products and services, which includes establishing an AI advisory body to responsibly leverage cutting-edge technology trends.

Conclusion

Victoria’s current budget highlights a strong pledge towards enhancing digital infrastructure across multiple sectors. With an emphasis on community and family services, emergency services, and education, the state intends to modernise and secure its IT frameworks, ensuring readiness to tackle future challenges effectively.

FAQs

Q: What is the objective of the $106 million funding?

A: The funding aims to upgrade IT systems in community and family services, improving case management, especially for child protection.

Q: What impact will the budget have on emergency services?

A: Emergency services, notably Victoria Police, will acquire new mobile devices, enhanced evidence recording technology, and improved cyber security frameworks.

Q: What transformations are planned for the education sector?

A: The education sector will migrate IT infrastructure to the cloud, with schools transitioning to centrally managed technology platforms for increased security and efficiency.

Q: How will the budget tackle cyber security?

A: Investments will enhance cyber security measures for public health services, Victoria Police, and educational establishments, ensuring data protection and operational continuity.

Q: Why is upgrading the Triple Zero telephony system important?

A: Upgrading the Triple Zero telephony system guarantees effective and reliable emergency communication, vital for public safety.

Melbourne Airport Implements AI Agents for Incident Management


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Melbourne Airport Improves Incident Management with AI Agents

Quick Overview

  • Melbourne Airport employs AI agents for swift incident management.
  • AI works alongside SharePoint to adhere to standard operating procedures (SOPs).
  • Preparation of reports for executive leaders is now AI-supported.
  • Challenges involve handling access to sensitive data.

Transforming Incident Management with AI

Melbourne Airport has adopted agent-based AI to enhance incident management throughout its airport and terminals. This progressive method enables quick responses to various situations, improving operational effectiveness and safety.

AI agents utilized for incident management at Melbourne Airport

AI Integration with SharePoint

Irfan Khan, the head of data analytics, states that the airport has connected AI agents with its SharePoint databases. This integration enables personnel to swiftly comply with standard operating procedures (SOPs) for incidents ranging from runway issues to health emergencies.

Streamlining Report Creation

AI is further optimizing the creation of shift incident reports for submission to the airport’s senior leadership. Previously, this was a demanding task, especially for exhausted staff after extended shifts. Now, AI agents facilitate the generation of comprehensive reports tailored to specific leadership requirements.

Tackling Data Privacy Challenges

Despite the overall success of the AI implementation, challenges have emerged, particularly concerning data privacy. Agents unintentionally accessed sensitive personal data from OneDrive accounts, prompting the airport to reassess access controls and governance policies.

Conclusion

The implementation of AI agents at Melbourne Airport represents a pivotal advancement in modernizing operational strategies. By merging AI with established systems, the airport improves incident management efficiency while tackling data privacy concerns.

FAQs

Q: What motivated Melbourne Airport to implement AI for incident management?

A: The requirement for rapid and effective responses to incidents across the airport and terminals drove the adoption of AI.

Q: In what ways does AI enhance the creation of incident reports?

A: AI agents aid in crafting comprehensive and customized reports, reducing staff workload and enhancing precision.

Q: What challenges has Melbourne Airport encountered with AI implementation?

A: Challenges include managing data privacy and ensuring sensitive information is not mistakenly accessed by AI agents.

Q: How is Melbourne Airport addressing data privacy concerns with AI?

A: The airport is reevaluating agent access rights and reinforcing governance to avert unauthorized data access.