Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 38 of 187

NAB Utilizes Databricks’ Genie AI to Unleash Enhanced Data Worth


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
NAB Elevates Data Analytics with Databricks’ Genie AI

Overview

  • NAB adopts Databricks’ Genie AI tools to maximize data utility.
  • Genie Spaces and Genie Code simplify data querying and programming.
  • This initiative seeks to enhance customer experience and relationship management.
  • Insights powered by AI facilitate quicker dispute resolution and customer engagement.

NAB’s Strategic Application of Databricks’ Genie AI

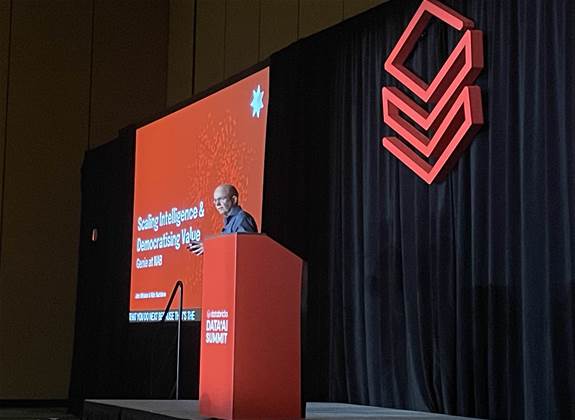
NAB utilizes Databricks' Genie AI tools to extract greater value from its data

John Whiston from NAB.

The National Australia Bank (NAB) has embraced Databricks’ Genie AI tools to enhance its data analytics capabilities. These tools are now operational within NAB’s analytics community, supporting natural language querying and the efficient creation of datasets, which bolster the bank’s decision-making functions.

Accelerating Data-Driven Insights

John Whiston, NAB’s executive in charge of data and analytics, states that the use of Genie tools is a logical advancement as the bank’s Ada platform already utilizes a Databricks foundation. NAB employs 180 data sources through Ada to integrate data insights into its operations.

The Genie AI tools empower NAB to swiftly obtain insights that previously took weeks or even months to generate. The implementation of Genie Spaces facilitates dataset curation and overlays them with an intuitive natural language chat interface, thereby democratizing data access for internal teams.

Improving Customer Engagement

NAB’s use of Genie AI is in line with its overall strategy to prioritize relationships and deliver outstanding customer experiences. By grasping customer needs during pivotal moments, NAB strives to enhance interactions and resolve disputes in a more efficient manner.

The analysis of call center transcripts with Genie Spaces has unveiled valuable insights into customer behavior and actual needs, enabling more informed and proactive engagement. This forward-thinking approach has lessened the frequency of repeated calls from customers during dispute resolution.

Conclusion

NAB’s implementation of Databricks’ Genie AI tools represents a major advancement in enhancing data-driven decision-making and customer experience. Through AI-enhanced analytics, NAB seeks to streamline operations, foster better customer interaction, and uphold a secure data environment.
Q&A Section

Q: What are Genie Spaces and Genie Code?

A: Genie Spaces consist of curated datasets featuring a natural language interface for easy querying, while Genie Code serves as an AI coding assistant that supports developers in efficiently crafting queries.

Q: How do Genie tools enhance customer experience?

A: By providing insights into customer behavior and requirements, Genie tools enable NAB to conduct more proactive and informed customer engagements, especially during dispute resolution.

Q: Why did NAB opt for Databricks’ AI tools?

A: The adoption is a natural evolution since NAB’s data platform, Ada, primarily operates on a Databricks infrastructure, allowing for smooth integration and data-driven decision-making.

Q: What effects has the integration of Genie AI had on NAB’s operations?

A: NAB has seen expedited delivery of data insights, improved access to internal data, and enhanced customer service through more informed and proactive engagements.

Q: How does NAB maintain data security with these tools?

A: NAB ensures a secure environment by strictly regulating data access, safeguarding sensitive information while enabling efficient utilization of data.

ASD Takes Action Against Developers Lacking Security Knowledge


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

New Security Directives from ASD for Software Developers

Quick Summary

  • ASD revises Information Security Manual to prioritize secure software development.
  • Developers without security expertise are discouraged from leading software projects.
  • Focus on education, skill enhancement, and maintaining a skills inventory for developers.
  • Increased use of AI in threat analysis and penetration evaluations.
  • Instructions on protecting personal data on platforms such as LinkedIn.
  • ASD’s 261-page ISM is compulsory for Australian governmental bodies.

New Security Directives from ASD for Software Developers

ASD establishes strict standards for developers lacking security expertise

The Australian Signals Directorate (ASD) has adopted a steadfast position on the importance of security proficiency in software development. The latest revision of the Information Security Manual (ISM) implements guidelines that dissuade employing developers who do not possess adequate cybersecurity knowledge. This initiative aligns with ASD’s goal of a “secure by default” philosophy, ensuring the integrity of software from its inception.

Significance of Developer Training and Skill Enhancement

To facilitate this program, the ISM encourages developers to pursue specialized training or skill enhancement in secure coding and programming techniques. Organizations are urged to keep a record detailing the cybersecurity competencies and knowledge of their developers, ensuring responsibility and ongoing advancement.

Enhancements in AI and Threat Intelligence

ASD also promotes the adoption of AI technologies in threat intelligence services to boost event detection capabilities. These technologies are additionally recommended for penetration testing and security evaluations of software, highlighting the role of technology in strengthening cybersecurity protocols.

Standards for Professional Conduct on LinkedIn

In a time when adversaries utilize open-source intelligence, ASD has implemented guidelines advising personnel against disclosing sensitive work-related information on platforms like LinkedIn. The ISM recommends using privacy controls to manage the visibility of personal posts, reducing the risks tied to espionage.

Compulsory Compliance for Government Agencies

The 261-page ISM is aimed at security professionals in organizations and vendors. While compliance is obligatory for Australian government agencies and any entity handling government data, other organizations are not legally required to comply unless specific laws or directives are enacted.

Overview

ASD’s revised Information Security Manual emphasizes the imperative of cybersecurity expertise in software development. By mandating training, advocating AI-enhanced security strategies, and recommending cautious online behavior, ASD seeks to bolster the security posture of Australian organizations and safeguard national interests.

Questions and Answers

Q: Why is ASD emphasizing the security capabilities of developers?

A: ASD’s objective is to ensure that software is secure from the beginning, minimizing vulnerabilities and safeguarding against cyber threats.

Q: What training is advisable for developers?

A: ASD recommends that developers participate in secure coding and programming practice training to improve their cybersecurity expertise.

Q: What role does AI play in security according to ASD?

A: AI technologies are endorsed for threat intelligence applications, event detection, penetration testing, and software security evaluations.

Q: Are organizations outside the government obligated to adhere to the ISM?

A: Compliance is required only if specific legislation or directives are issued; otherwise, it is not obligatory for non-government organizations.

Q: What dangers are associated with sharing work-related information online?

A: Open-source intelligence can be misused for espionage, resulting in risks to national security and financial harm.

LMG Selects Slack for Organizational Transformation


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • LMG, a prominent mortgage aggregator, has implemented Slack Enterprise to enhance internal communication.
  • The organisation’s goal is to replace more than 200 separate systems with Slack as the main platform.
  • Slack Enterprise works alongside LMG’s existing Salesforce CRM, boosting productivity and teamwork.
  • Efforts are underway to integrate Slack with the CRM, aimed at refining sales and support workflows.
  • LMG has observed a notable drop in internal emails, thereby increasing workflow effectiveness.

LMG’s Move to Slack Enterprise

Mortgage aggregator LMG has made a significant advancement by implementing Slack Enterprise to unify and enhance its internal communications. With a vast network of over 5000 brokers, the largest in the trans-Tasman area, LMG encountered issues with fragmented communication. The introduction of Slack Enterprise is intended to streamline these channels and replace an overwhelming array of tools that had surpassed 200 in their operations.

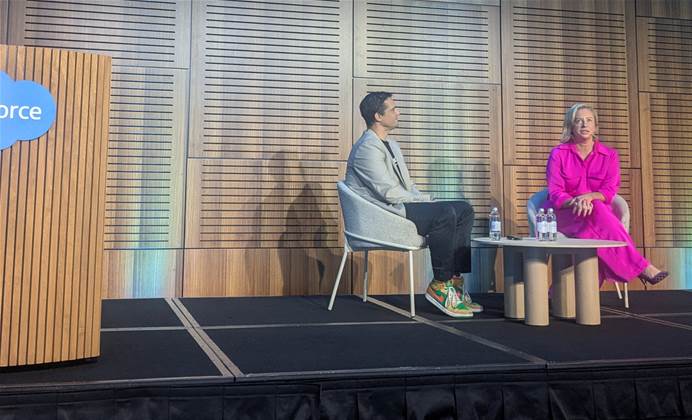
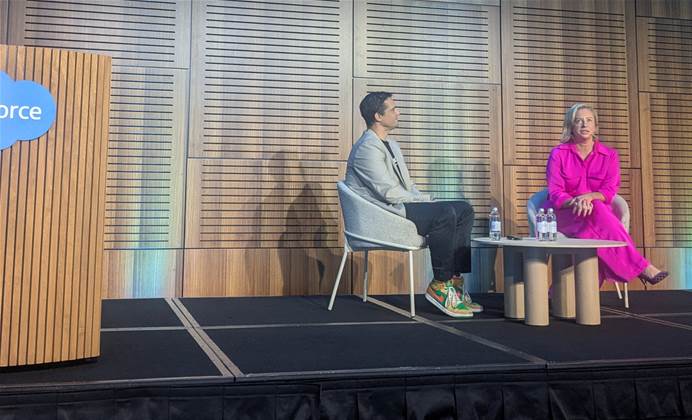
LMG bets on Slack as an enterprise platform

The Issue of Isolated Systems

Prior to Slack’s implementation, LMG’s internal communication was dispersed among various platforms such as email, Google Chat, WhatsApp, and SMS. This fragmentation not only obstructed productivity but also required frequent context switching and ineffective communication channels.

Boosting Collaboration with Slack

Karina Egan, LMG’s general manager of business enablement, emphasized the change during Salesforce’s Financial Summit in Sydney. The transition from a basic version of Slack to its enterprise variant has been crucial. Teams that previously depended on various tools are now equipped to utilize Slack’s extensive features.

“We aimed to establish Slack as more than merely a messaging application. It’s about leveraging Slack’s potential as an enterprise solution,” Egan remarked. The transition has resulted in fewer meetings, more efficient update sessions, and a considerable decrease in internal emails.

CRM Integration and Future Plans

LMG is moving beyond the basic functionalities of Slack. The organisation is currently focused on integrating Slack with its Salesforce CRM. This integration is in the user acceptance testing stage, with an emphasis on enabling sales teams to seamlessly update contacts and log activities through Slack.

Additionally, LMG is investigating the possibility of transferring its IT support ticketing system to Slack, which could transform the internal handling of support requests.

Conclusion

LMG’s move to adopt Slack Enterprise represents a pivotal progress in enhancing internal communication and improving operational efficiency. By centralizing communication and minimizing email dependency, LMG is establishing a benchmark for how large organisations can successfully manage their communication systems.

Q: What motivated LMG to switch to Slack Enterprise?

A: LMG sought to unify its fragmented communication tools and optimise internal communication across its operations.

Q: What effects has Slack Enterprise had on LMG’s email use?

A: The organisation has significantly curtailed internal email traffic, centralising communication in Slack to enhance workflow efficiency.

Q: What integrations are LMG exploring between Slack and its CRM?

A: LMG is evaluating integrations that will allow sales teams to modify contacts and log activities directly via Slack, improving CRM functionalities.

Q: What future initiatives does LMG envision for Slack?

A: LMG is contemplating the migration of its IT support ticketing system to Slack, potentially managing requests solely through the platform.

Why Are Two Tesla Cybercabs Located 12,000 km from Their Home in New Zealand?


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

What Are Two Tesla Cybercabs Doing 12,000 km from Their Base in New Zealand?

Brief Overview

  • Tesla Cybercabs sighted in New Zealand, a long way from Texas.
  • Potential cold weather testing as New Zealand experiences winter.
  • Cybercabs are self-driving, built for driverless function.
  • Production is increasing with more than 100 units observed in recent visuals.
  • Opportunity for deployment as robotaxis.
  • Australia is set for similar trials utilizing FSD V14 software.

The Voyage of Tesla Cybercabs to New Zealand

Today, a video circulated on social media has uncovered an interesting scene: Tesla Cybercabs being delivered in New Zealand. These advanced vehicles, placed on a Mercedes Benz double-decker car carrier from PTSL Auto Logistics NZ, are nearly 12,000 kilometers distant from their production home at Tesla’s Gigafactory in Texas.

Cold Weather Trials in New Zealand

The arrival of Tesla Cybercabs in New Zealand prompts inquiries about their intended function so far from their origin. Tesla, similar to numerous automakers, frequently tests vehicles prior to release in varying climates, and New Zealand’s winter provides an ideal environment for cold weather assessments. This aligns with the approach of exposing these cars to various climatic challenges before their worldwide launch.

Initial Prototypes with Conventional Controls?

Though the Cybercabs are intended to function independently without human operators, the existing prototypes may retain conventional features like a steering wheel and pedals. This would make transport and testing procedures more manageable. The finalized production model of the Cybercabs is anticipated to be entirely driverless.

Upcoming Production and Implementation

Recent aerial footage has displayed over 100 Cybercabs at Tesla’s manufacturing site, signifying a considerable increase in production capacity. Tesla revealed plans for the release of the initial production model in April, indicating that the hardware is set for action. With appropriate software, these cars could quickly become active as autonomous robotaxis, transforming urban transportation.

Importance of Winter Testing

Although hardware development is completed, winter testing remains essential. It gives engineers the chance to evaluate and refine the vehicle’s performance in demanding conditions. This could be the first instance where a Cybercab has been operated outside the US, marking a pivotal moment in its development timeline.

The Possibility of Testing in Australia

If Tesla is leveraging New Zealand for testing purposes, it is plausible they may turn to Australia next. As Australians eagerly await the launch of Full Self-Driving (FSD) V14, evaluating the Cybercab with this software on Australian roads is a sensible progression. Such evaluations would further ready the vehicle for various international markets.

Excitement Down Under

Australians are enthusiastic about witnessing Tesla’s cutting-edge Cybercab on their routes, offering a budget-friendly and eco-friendly transport solution. The technology promises to revolutionize personal mobility, and a local presence would yield invaluable insights on its adaptation to Australian laws and road conditions.

Conclusion

To sum up, the sighting of Tesla Cybercabs in New Zealand represents a strategic initiative for cold weather evaluation. It underscores Tesla’s dedication to thorough vehicle development and hints at prospective future implementation in Australia. As the company progresses toward mass production, global audiences are keenly observing how these autonomous vehicles will transform transportation.

FAQ: Essential Information

Q: Why are Tesla Cybercabs present in New Zealand?

A: They are probably there for cold weather trials, utilizing New Zealand’s winter environment.

Q: Are the Cybercabs completely autonomous?

A: The final versions are anticipated to be fully autonomous, but the current prototypes may still include traditional controls.

Q: What does the recent production footage signify?

A: It indicates a notable increase in Cybercab production, gearing up for global rollout as autonomous robotaxis.

Q: Will the Cybercabs undergo testing in Australia?

A: While not firmly established, it is a logical progression, especially with the forthcoming FSD V14 software requiring testing on Australian routes.

Q: What effect might Cybercabs have on transport in Australia?

A: They could offer a cost-effective, sustainable transport alternative, changing personal mobility in urban settings.

G7 Leaders Pledge to Enhance AI Cooperation


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

G7 Leaders Emphasize AI Collaboration

Brief Overview

  • G7 leaders pledged to strengthen AI collaboration during the 2023 summit.
  • The “trusted partners” initiative aims to facilitate access to advanced AI models.
  • Concerns over cyber security related to AI model misuse were highlighted.
  • Europe aims for enhanced tech sovereignty amidst reliance on US technology.
  • The European Commission is planning AI “gigafactories” to ensure sovereign computing capabilities.

AI Collaboration at the G7 Summit

At the recent summit in Evian-les-Bains, G7 leaders from the Group of Seven countries pledged to strengthen their cooperation in tackling both the challenges and possibilities inherent in advanced AI technologies. The event underscored the critical need for a unified strategy on AI, with conversations centered around creating a “trusted partners” initiative aimed at providing non-US countries with access to advanced US AI models, including offerings from firms like Anthropic.

G7 leaders emphasize AI partnerships

Concerns Over Security and AI Models

The summit also brought up cyber security issues, particularly concerning Anthropic’s AI model, Mythos. While its design focuses on identifying coding vulnerabilities and boosting cyber defences, fears remain that it might be weaponized to augment cyber attacks. Due to these worries, US President Donald Trump had earlier limited foreign access to such advanced models, citing national security concerns.

The “Trusted Partners” Initiative

The suggested “trusted partners” initiative could bypass these limitations, permitting nations or companies considered reliable to utilize AI models to strengthen their cyber security against potential threats such as China. This progression is perceived as a strategic effort to advance global AI capabilities while prioritizing security.

Europe’s Challenge for Tech Sovereignty

Europe is grappling with the challenge of pursuing its ambitions for tech sovereignty while remaining competitive against a backdrop of US technology dominance. European leaders increasingly recognize AI as a pivotal element in their economic and national security agendas. The European Commission has unveiled plans for AI “gigafactories” and significant computing infrastructure aimed at ensuring autonomous access to computing resources.

Conclusion

The G7 summit highlighted the significance of global collaboration in the development and regulation of AI. With cyber security issues at the forefront, the “trusted partners” initiative presents a route for non-US nations to gain access to premier AI technologies while enhancing their defences. Europe’s pursuit of technological independence further underscores the global interplay of AI innovation and security.

Q: What was the primary focus of the G7 summit relating to AI?

A: The focus was on promoting international collaboration to address the challenges and opportunities posed by advanced AI technologies.

Q: What does the “trusted partners” initiative entail?

A: It is a proposed effort to provide access to advanced US AI models for trustworthy non-US countries to improve their cyber security.

Q: What security issues are associated with AI models like Mythos?

A: Although intended to identify coding weaknesses, these models might be misused to execute cyber attacks.

Q: How is Europe addressing US supremacy in AI and technology?

A: Europe is working toward increased tech sovereignty by investing in AI “gigafactories” and reducing its dependency on US technology.

Q: What are the consequences of US restrictions on AI models?

A: The restrictions emphasize national security concerns but have also sparked discussions on the need for a more inclusive access model.

Toll Group Enhances Network to Remove Reliance on Data Centres


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

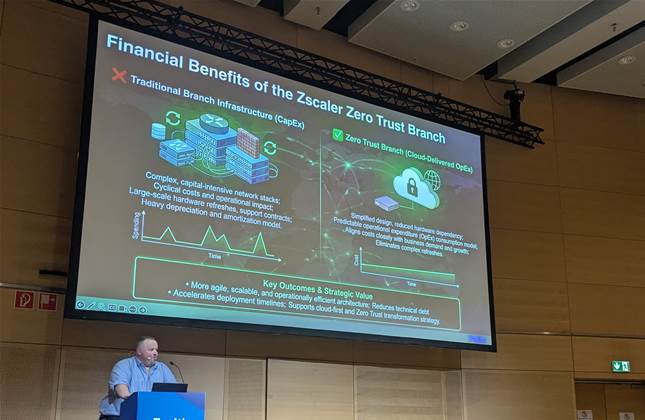
  • Toll Group is enhancing its network by shutting down data centres and utilising cloud platforms such as Azure and AWS.
  • The initiative includes the rollout of Zscaler’s Zero Trust Exchange framework to boost security and connectivity.
  • Deployment of Zscaler’s hardware gateways and access protocols is taking place at 250 sites worldwide.
  • Modernising the network is designed to cut costs and reduce dependence on conventional data centre structures.
  • The updated model transitions from capex to opex, aiming for estimated yearly savings of 20%.
  • Deployment simplifies and hastens the process of setting up new locations, reducing setup time to about two weeks.

Network Modernisation and Transition to Cloud

Toll Group has initiated a significant network modernisation project focused on shutting down its data centres and maximising the use of Azure and AWS cloud platforms. This undertaking represents a key evolution in the company’s tech strategy, employing Zscaler’s Zero Trust Exchange (ZTE) cloud platform to securely link its global locations.

Adopting Zero Trust Architecture

The effort entails the deployment of Zscaler’s Zero Trust Branch (ZTB) hardware gateways alongside its Zero Trust Networking Access offerings, which include Zscaler Internet Access (ZIA) and Zscaler Private Access (ZPA). This approach empowers Toll Group to establish precise access controls and shift connectivity closer to the network edge, circumventing traditional SD-WAN nodes and firewalls.

Optimising Global Operations

Launched nine months ago, the modernisation project has already finalised network enhancements for Toll’s two Australian data centres, affecting 23 domestic locations. With two delivery partners selected, the company intends to broaden these improvements to its remaining four data centres and 250 international sites, ultimately aiming to close all its data centres.

Cost Savings and Operational Advantages

By moving from a capital expenditure framework to an operational expenditure model, Toll Group foresees yearly savings of 20%. This change has been a vital component in reassessing its network management approach, favouring smarter, cloud-centric solutions over traditional SD-WAN systems.

Speeding Up Time-to-Market

This new network strategy drastically cuts the time needed to set up new locations. Previously, establishment required a managed service provider and could extend from six to eight weeks. Now, with the option to select an internet provider and set up ZTB gateways, Toll can launch new sites in about two weeks.

Cloud Incorporation and Future Directions

This modernisation aligns with a broader corporate strategy to lessen reliance on data centres. Toll has already transitioned around 70% of its application workloads to AWS and Azure, reinforcing its dedication to a cloud-first methodology.

Conclusion

Toll Group’s current network modernisation initiative represents a strategic shift towards cloud integration, utilising Zscaler’s Zero Trust solutions to move away from traditional data centre dependency. This effort promises notable cost reductions, enhanced operational efficiency, and faster new site deployments, marking a crucial transition in the company’s technological framework.

Q: What is the main aim of Toll Group’s network modernisation?

A: The primary aim is to close current data centres and improve network security and connectivity through Zscaler’s cloud services.

Q: What impact does the new model have on Toll Group’s expenditures?

A: The conversion from capex to opex is projected to generate a 20% annual savings, enhancing cost efficiencies.

Q: Which technological solutions are being introduced in the project?

A: Toll Group is implementing Zscaler’s Zero Trust Branch (ZTB) gateways, Zscaler Internet Access (ZIA), and Zscaler Private Access (ZPA).

Q: What is the effect of the project on the initiation of new sites?

A: The redesigned approach reduces the setup duration for new sites from six to eight weeks to roughly two weeks.

Q: What proportion of Toll Group’s application workloads have already transitioned to the cloud?

A: Approximately 70% of application workloads have been shifted to AWS and Azure.

Q: What are the long-term intentions once the data centres are retired?

A: Toll Group aims to perform a thorough assessment and modernise any outstanding infrastructure into the cloud.

Access Control Weakness Revealed FIFA World Cup Match Streams to Unrestricted Access


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Significant access control vulnerability permitted unrestricted access to FIFA World Cup streams.
  • Researcher BobDaHacker identified the flaw via FIFA’s agent registration site.
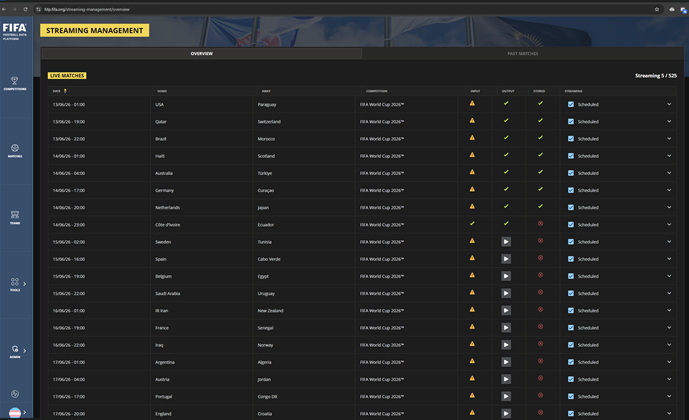
  • The vulnerability granted access to stream keys, camera feeds, and match data.
  • Inadequate backend verification enabled unauthorized access for any authenticated user.
  • The researcher notified U.S. authorities after efforts to reach FIFA went unanswered.
  • FIFA has yet to reply to the researcher but swiftly addressed the issue.

Uncovering the Flaw

An inquisitive researcher, referred to as BobDaHacker, discovered a critical access control vulnerability on one of FIFA’s public platforms. This flaw made live broadcast stream keys, camera feed access, and match statistics available to anyone who passed a straightforward identity verification process at an agent registration portal.

Access control vulnerability left FIFA World Cup match streams easily accessible

Source: BobDaHacker

Technical Insights and Consequences

After finalizing registration for prospective football agents, the researcher discovered that her account was incorporated into FIFA’s Microsoft Entra tenant, the identity and access management (IAM) system for FIFA’s internal operations. The backend did not enforce role verification, allowing any authenticated member of the Entra tenant to access data. This flaw enabled BobDaHacker to reach the streaming management dashboard and Real-Time Messaging Protocol (RTMP) ingest links for all FIFA World Cup 2026 matches.

Each game utilized a singular stream key across five different camera views, including the main broadcast feed. This situation allowed potential attackers to seize all camera feeds simultaneously and disrupt live broadcasts worldwide. Additionally, the researcher’s account had access to the Commentator Information System, which included editorial comments, team information, and other vital match details.

Obstacles in Reporting

BobDaHacker encountered considerable difficulties in reporting the vulnerability, characterizing it as an “absolute nightmare” due to FIFA’s absence of a bug bounty program or designated security contacts. After unsuccessful attempts to reach out to FIFA, she informed U.S. authorities, such as the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI), and received feedback from them. Despite a quick resolution to the problem, FIFA has not acknowledged the researcher’s contributions.

Conclusion

The identification of an access control flaw in FIFA’s frameworks illustrates the crucial need for effective backend verification to avert unauthorized access. Although the issue was promptly resolved, the lack of engagement from FIFA emphasizes the necessity for improved communication channels for reporting vulnerabilities.

Question & Answer Segment

Q: What type of vulnerability did BobDaHacker find?

A: The vulnerability was a misconfiguration in access control that left FIFA World Cup match streams, camera feed access, and match data exposed to unauthorized individuals.

Q: How did the researcher gain entry to FIFA’s systems?

A: By completing the registration for prospective football agents, the researcher was incorporated into FIFA’s Microsoft Entra tenant, which did not have sufficient backend role validation.

Q: What possible consequences could this vulnerability have led to?

A: Potential attackers could take control of camera feeds, modify live broadcasts, and alter match statistics and other essential information.

Q: How was the vulnerability reported by the researcher?

A: Following unsuccessful attempts to connect with FIFA, the researcher reported the problem to U.S. agencies like CISA and the FBI, receiving feedback from them.

Q: Has FIFA replied regarding the vulnerability report?

A: Even though the problem was resolved quickly, FIFA has not yet responded to the researcher.

Q: Is there information on how long the vulnerability existed?

A: The duration of the vulnerability’s presence on FIFA’s platform remains unclear.

PAX Aus 2026 Storytime Presenter Revealed: A Significant Attraction for MMO Fans


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

PAX Aus 2026: A Significant Attraction for MMO Fans

Quick Overview

  • Holly Longdale, the Executive Producer of World of Warcraft, designated as the Storytime speaker for PAX Aus 2026.
  • Longdale’s professional journey includes legendary franchises such as World of Warcraft, Diablo, and EverQuest.
  • PAX Aus Storytime provides exclusive perspectives on the gaming sector through personal narratives.
  • Longdale’s background aligns perfectly with PAX Aus’s community-oriented approach.
  • PAX Aus 2026 is scheduled for 9–11 October at the Melbourne Convention and Exhibition Centre.

A Renowned Career in Virtual Realms

Holly Longdale, a key player in MMORPG creation, has been selected as the Storytime speaker at PAX Aus 2026. With over two decades in the field, she has been instrumental in shaping games like World of Warcraft, Diablo, Overwatch, and EverQuest. She currently serves as the Executive Producer for World of Warcraft, including its latest expansion, World of Warcraft: Midnight.

Holly Longdale to speak at PAX Aus 2026 Storytime

Prior to her tenure at Blizzard, Longdale held significant positions at Sony Online Entertainment and Disney, contributing to projects related to EverQuest expansions, TRON, and Pirates of the Caribbean. Her vast experience renders her an exceptional speaker for PAX Aus Storytime.

The Importance of Storytime at PAX Aus

Storytime is one of the most eagerly awaited segments at PAX Aus each year, offering participants the opportunity to hear from notable figures in the gaming industry. In contrast to conventional keynote sessions, Storytime presents a more personal look at the anecdotes, challenges, and lessons that have defined the careers of some of the most impactful personalities in gaming. Past Storytime segments have consistently drawn large crowds, keen for behind-the-scenes revelations.

A Perfect Match for the PAX Aus Platform

Longdale’s impact on the MMO genre makes her an outstanding selection for the PAX Aus platform. Massively multiplayer online games are fundamentally community-oriented, and Longdale’s contributions have profoundly impacted these communities. Her emphasis on creativity and connection underscores the core values of PAX Aus.

In her announcement, Longdale shared her enthusiasm for celebrating the influence of games and their communities. Her theme of creativity and connection perfectly resonates with the essence of PAX Aus.

PAX Aus 2026

PAX Aus has long functioned as a tribute to community in gaming, featuring panels, cosplay, indie showcases, and a vibrant expo floor. Longdale’s career, focused on nurturing gaming communities, captures this spirit, making her Storytime appearance highly awaited.

PAX Aus 2026 will unfold at the Melbourne Convention and Exhibition Centre from 9–11 October. With Holly Longdale confirmed as the Storytime speaker, the event promises an unforgettable experience for gamers and industry fans alike. Be sure to grab your tickets promptly, as they are selling fast!

PAX Aus 2026 event with Holly Longdale

Recap

Holly Longdale’s forthcoming Storytime segment at PAX Aus 2026 is poised to deliver invaluable insights into the realm of MMORPGs. Her extensive experience and impact on gaming render her an ideal fit for this community-oriented event, granting participants a unique chance to learn from one of the leading figures in the industry.

Q&A Segment

Q: Who is Holly Longdale?

A: Holly Longdale is the Executive Producer of World of Warcraft at Blizzard Entertainment, recognized for her substantial contributions to the MMORPG genre.

Q: What is PAX Aus Storytime?

A: PAX Aus Storytime is a session wherein prominent figures in the gaming industry share personal narratives and insights, giving a behind-the-scenes look at game development.

Q: When and where will PAX Aus 2026 occur?

A: PAX Aus 2026 will take place at the Melbourne Convention and Exhibition Centre from 9–11 October.

Q: Why is Holly Longdale a notable choice for PAX Aus Storytime?

A: Holly Longdale’s career in MMORPGs and her commitment to community-centered game development make her an exceptional speaker for PAX Aus, which focuses on the community aspect of gaming.

Security Leaders Support Loosening Export Restrictions for Anthropic’s Mythos-Class Models


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Security Executives Support the Release of Anthropic’s Mythos-Class Models

Remove Export Restrictions for Anthropic’s Mythos-Class Models

Brief Overview

  • Cybersecurity professionals request the removal of export restrictions on Mythos-class AI models.
  • Mythos-class models assist in identifying software vulnerabilities.
  • Similar abilities are found in other AI models such as GPT-5.5 and Opus.
  • Concerns about unilateral disarmament impacting Western cyber defenders.
  • Advocacy for a transparent, inclusive rule-making procedure.
Security executives support the removal of export controls on Anthropic's Mythos-class

Katie Moussouris.

Mythos-Class Models and Cyber Security

Leaders in the security field have submitted an open letter to the US Department of Commerce requesting the elimination of export restrictions on Anthropic’s Fable and Mythos-class AI models. These restrictions were imposed suddenly, resulting in Anthropic disabling global access shortly after their launch.

The Case for Availability

The signers recognize the Mythos-class models’ capacity to uncover software vulnerabilities and produce exploits. Nonetheless, they contend that these capabilities are not unique, as other models like GPT-5.5 and Opus possess similar features. The letter highlights that Chinese models are advancing in parity with US AI technology, possibly having undisclosed sophisticated abilities.

Consequences for Cyber Security

According to them, restricting access to the Mythos-class models takes crucial resources away from defenders, comparing the export restrictions to a unilateral disarmament of Western cyber assets. While the group holds differing opinions on AI regulation, they share consensus on the necessity for controls rooted in scientific and democratic values.

Research Paper Controversy

The enforcement of these restrictions was based on a third-party research study. Katie Moussouris, who initiated Microsoft’s bug bounty program, reviewed the study. She clarifies that while the research indicated possible vulnerabilities, the defensive properties of the models were purposely evaluated and not innately dangerous.

Conclusion

The push to revoke export restrictions on Anthropic’s Mythos-class models emphasizes the ongoing discourse between innovation and regulation within AI technology. Industry leaders urge for a balanced strategy that maintains security while fostering technological progress.

Q: What are Mythos-class models?

A: Mythos-class models are sophisticated AI systems developed by Anthropic that focus on identifying software vulnerabilities and crafting solutions.

Q: Why were export restrictions placed on these models?

A: Export restrictions were placed after a research report raised alarms regarding the potential for misuse of these models in producing software exploits.

Q: What is the principal argument against these restrictions?

A: The restrictions are said to undermine Western cyber defence by limiting access to powerful security resources, even though similar functions are available elsewhere.

Q: How do other AI models compare to the Mythos-class?

A: Models such as GPT-5.5, Opus, Sonnet, and Kimi 2.7 have similar functionalities, making the restrictions on Mythos-class models appear less warranted.

Q: Who endorsed the open letter to the US Department of Commerce?

A: The letter was supported by 42 industry leaders, including CISOs and executives from organizations like Sophos, Adobe, and NVIDIA.

Amex Required to Strengthen Access Controls After Insider Privacy Breaches


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Amex Privacy Measures Strengthened After Insider Breaches

Quick Overview

  • Amex instructed to improve access controls following insider privacy breaches.
  • OAIC inquiry was initiated after a complaint regarding personal data access.
  • Amex must introduce account-level access and activity logging within six months.
  • Just-in-time access controls were advised but initially opposed by Amex.
  • Amex must apologize and provide compensation to the affected party.
Amex instructed to enforce access controls after insider privacy breaches

Amex Facing Scrutiny Over Privacy Breaches

The Office of the Australian Information Commissioner (OAIC) has mandated American Express (Amex) to reinforce its data access protocols following an investigation into privacy breaches by insiders. This directive follows a complaint from a former customer, which disclosed that an Amex employee accessed their sensitive information across five internal systems during and after a personal relationship.

Required Enhancements in Access Protocols

Amex is obligated to implement standardized account-level access and action logging within a six-month timeframe. This involves generating a timestamped record every time an employee accesses or alters a customer record. Moreover, technical measures must be established to restrict employee access to particular customer information, especially for at-risk or high-profile cardholders.

Just-in-Time Access Protocols

The OAIC recommended the adoption of just-in-time (JIT) access controls to further protect customer data. JIT would limit staff access to customer records without time-sensitive triggers, such as active customer authentication. While Amex initially opposed this suggestion, the commissioner found it essential due to the sensitive nature of the data held by the firm.

Past Incidents and Increased Expectations

Previous incidents involving Amex, including a 2019 situation where customer data was fraudulently accessed, have alerted the company. As a result, Amex is subject to higher expectations concerning preventative measures to reduce insider threats. The OAIC identified Amex as being in violation of Australian Privacy Principle 11.1, necessitating a written apology and compensation to the complainant.

Conclusion

Amex has been directed by the OAIC to strengthen its data access measures following privacy breaches involving insider access. Within six months, Amex must establish comprehensive logging systems and limit access to sensitive customer data. Despite earlier resistance, Amex is expected to implement just-in-time access controls to improve data safeguarding.

Q&A

Q: What led to the OAIC investigation into Amex?

A: The investigation was initiated by a complaint from a former customer whose sensitive information was accessed by an Amex employee during and after a personal relationship.

Q: What are account-level access and action logging?

A: These systems generate timestamped records any time an employee accesses or modifies a customer record, improving transparency and responsibility.

Q: What is the objective of just-in-time (JIT) access controls?

A: JIT access controls are intended to restrict staff access to customer records, requiring time-sensitive triggers like customer authentication to avoid unnecessary data exposure.

Q: How has Amex reacted to the order?

A: Amex initially resisted the JIT requirement due to practical concerns but is now mandated to comply with the OAIC’s directives to strengthen data protection measures.

Q: What compensation must Amex provide?

A: Amex is required to issue a written apology and provide compensation for both economic and non-economic damages, along with covering the complainant’s expenses related to the case.