Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 20 of 187

Onelogon Vulnerability Circumvents Microsoft’s Zerologon Security Patch


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Brief Overview

  • A newly found Onelogon exploit circumvents Microsoft’s Zerologon security update.
  • This vulnerability impacts Microsoft’s Active Directory, enabling attackers to take control of domains.
  • Onelogon employs a 24-bit brute force attack, securing access in an average of 32 minutes.
  • An alternative attack method necessitates no initial account access and can succeed in around 37 minutes.
  • Microsoft recommends the use of secure RPCs to guard against these vulnerabilities, although not all organizations can enforce them.
  • Research indicates a considerable number of systems still remain susceptible to these exploits.

The Onelogon Exploit

German security experts Alexander Neff, Tobias Holl, and Kevin Borgolte from Ruhr University have uncovered a new vulnerability termed Onelogon. This exploit is reminiscent of the notorious Zerologon from 2020, which enabled attackers to fully breach Active Directory management domains.

Onelogon attack defeats Microsoft's Zerologon update

Mechanism of Onelogon

The researchers have devised a 24-bit brute force attack that necessitates a compromised, low-privilege computer account. This strategy can reset a server-side challenge cache and achieve access in about 32 minutes on average. Moreover, a meet-in-the-middle attack, which does not require previous account access, can breach a domain controller in roughly 37 minutes.

Microsoft’s Reaction

In spite of the seriousness, Microsoft has not intended to directly rectify the Onelogon problem. The company suggests employing secure Remote Procedure Calls (RPCs) to alleviate the threat posed by both Onelogon and Zerologon vulnerabilities. Nevertheless, not all organizations can utilize secure RPCs, leaving numerous systems vulnerable.

Current Vulnerability Status

Recent studies reveal a concerning number of organizations continue to be at risk. A 2025 audit uncovered that nearly a quarter of 44 Active Directory environments permitted vulnerable Netlogon secure channel connections. A 2026 examination across 270 organizations identified six systems directly at risk from Onelogon.

Technical Insights

The Netlogon protocol from Microsoft, which is part of Active Directory, authenticates a computer’s identity by scrambling a code using a confidential key. Regrettably, the scrambling begins from a fixed, predictable starting point, which attackers can take advantage of. This predictability allows them to eventually circumvent security checks without needing to know the secret key.

Patching Limitations

The update Microsoft released for Zerologon only verifies if the first five bytes of a challenge are the same. It overlooks other patterns that generate predictable ciphertext, making the patch incomplete and evadable. A comprehensive fix would need to break backward compatibility to properly implement the cryptographic protocol.

Conclusion

The Onelogon vulnerability underscores persistent security issues with Microsoft’s Active Directory, especially the shortcomings in the Zerologon patch. While secure RPCs could provide a solution, their application is not widespread, leaving many systems vulnerable. Organizations need to remain alert and consider alternative security strategies to safeguard their networks.

Q: What is the Onelogon vulnerability?

A: Onelogon is a security exploit that bypasses Microsoft’s Zerologon patch, enabling attackers to take control of Active Directory domains.

Q: How does Onelogon function?

A: Onelogon utilizes a 24-bit brute force attack and a meet-in-the-middle technique to gain access to systems in 32 to 37 minutes.

Q: Why hasn’t Microsoft resolved Onelogon?

A: Microsoft suggests secure RPCs to address Onelogon but hasn’t released a patch due to the significance of backward compatibility.

Q: Are numerous systems still at risk from Onelogon?

A: Yes, studies indicate many systems are still vulnerable due to the lack of universal secure RPC implementation.

Q: What should organizations do to defend themselves?

A: Organizations should employ secure RPCs wherever possible and remain informed about alternative security options.

Q: How did researchers uncover Onelogon?

A: Researchers at Ruhr University identified the vulnerability through an examination of Microsoft’s Active Directory and the limitations of the Zerologon patch.

South Australia Launches Royal Commission into AI After Premier’s Trip to Silicon Valley


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

South Australia’s Royal Commission on AI

South Australia Launches Royal Commission on AI After Premier’s Visit to Silicon Valley

South Australia Launches AI Investigation

Quick Overview

  • South Australia initiates a Royal Commission focused on Artificial Intelligence.
  • Emphasis on proactive policy measures instead of assigning legal liability.
  • Five primary focus areas: regulation, education, public services, workforce, and infrastructure.
  • AI’s consumption of energy and water is being examined.
  • Adelaide capitalizes on its technological ecosystem for AI advancement.

South Australia’s Pioneering Step in AI Regulation

After a strategic trip to Silicon Valley, South Australian Premier Peter Malinauskas has revealed a Royal Commission on Artificial Intelligence (AI). This groundbreaking initiative seeks to investigate the systemic influences of AI, establishing South Australia as the first state in Australia to utilize such a powerful legal mechanism for technology evaluation.

Emphasis on Proactive Policy Development

The Royal Commission will prioritize forward-thinking policies over retrospective blame. It intends to develop a roadmap based on evidence to enhance economic opportunities while protecting against social challenges. A panel of distinguished commissioners will guide the inquiry, gathering input from a variety of stakeholders.

Five Main Focus Areas

Regulatory and Policy Framework

The commission will investigate policy and regulatory frameworks at both the state and national levels, tackling the disjointed AI regulatory system in Australia.

Impact on Education

The role of AI in education will be analyzed, emphasizing improvement in learning outcomes without sacrificing academic integrity.

Delivery of Public Services

The potential of AI to enhance healthcare and other public services will be examined, with a focus on secure and effective implementations.

Transition of the Workforce

The commission will consider the effects of AI on the job market and create retraining initiatives for impacted industries.

Technical Infrastructure Assessment

The inquiry will evaluate AI’s energy and water requirements, especially with regard to South Australia’s renewable energy strategies.

Considerations for Energy and Water

AI’s demand for substantial electricity and water resources stands as a central issue. South Australia’s renewable energy scenario offers both challenges and opportunities for integrating AI data centers.

Adelaide’s Role in Technological Leadership

Adelaide’s well-established technology ecosystem, which includes entities like the Australian Institute for Machine Learning, positions South Australia as a frontrunner in AI policy. The Royal Commission utilizes these strengths to shape national technology directions.

Participation of Global Tech Giants

The Royal Commission will include multinational technology companies, such as Microsoft and Google, to share insights on data security and infrastructure needs. The public nature of the inquiry will shine a light on the operations of these firms.

Upcoming Steps for the Commission

With sessions scheduled to commence on 1 October 2026, the government will finalize the panel of commissioners and the terms of reference. Public contributions will be solicited, with a final report expected by 1 July 2027.

Conclusion

South Australia’s Royal Commission into AI represents a proactive strategy for addressing the technology’s systemic effects. By emphasizing policy advancement and leveraging its technological ecosystem, Adelaide is set to shape national AI policies.

Q&A

Q: What is the reason behind South Australia’s Royal Commission into AI?

A: The Commission seeks to proactively investigate AI’s systemic influences and create policy frameworks instead of assigning guilt.

Q: What are the main focus areas for the Commission?

A: The Commission will target regulation, education, public service, workforce transition, and technical infrastructure.

Q: How is the Commission addressing AI’s energy requirements?

A: It will analyze AI’s resource consumption within the scope of South Australia’s renewable energy policies.

Q: What role will international tech companies play in the Commission?

A: Companies like Microsoft and Google will offer insights on data security and infrastructure during public hearings.

Q: How does Adelaide’s tech landscape support the Commission’s work?

A: Adelaide’s prominent tech organizations provide knowledge, establishing South Australia as a leader in AI regulation.

Q: What is the schedule for the Royal Commission?

A: The proceedings will start on 1 October 2026, with a final report scheduled for 1 July 2027.

Australian Super Funds to Test Unified Cyber Attack Reaction


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Fast Overview

  • Operation Honey Bee assesses the cyber-attack response of the Australian superannuation industry.
  • More than 50 participants, including 15 superannuation funds, are taking part this year.
  • The aim of the exercise is to uncover capability weaknesses and improve information exchange.
  • GNGB encourages funds to consider third parties as key players in their response strategies.
  • Australia’s superannuation system boasts $4.5 trillion and is swiftly expanding.

Operation Honey Bee: Fortifying Cyber Defenses

Super funds to test coordinated cyber attack response

The Gateway Network Governance Body (GNGB) is once again leading efforts to enhance the cyber resilience of Australia’s superannuation sector. Through its annual Operation Honey Bee, GNGB is implementing a thorough exercise to mimic a coordinated cyber-attack. Now entering its fourth year, this exercise acts as an essential platform for assessing and refining the sector’s response tactics.

Unprecedented Participation in 2023

This year’s Operation Honey Bee is set to be the largest to date, featuring over 50 participants, inclusive of 15 superannuation funds and various service providers. The exercise will also bring together industry regulators and a variety of government stakeholders. Michelle Bower, the chief executive of GNGB, emphasized that this collective endeavor is crucial for understanding realistic cyber threats and training for coordinated responses.

Aims and Tactics

The principal objectives of Operation Honey Bee encompass assessing shared incident response plans, pinpointing capability deficiencies, and enhancing information exchange. The exercise acts as a litmus test for how well organizations can communicate and collaborate in real time during a cyber emergency. GNGB’s resilience checklist for 2024 underscores the necessity of including third parties as essential stakeholders in response strategies, instead of just being recipients of notifications.

An Essential Role in Cyber Preparedness

Founded in 2016, GNGB is a not-for-profit organization owned by the industry that assumed the network stewardship role from the Australian Taxation Office. It oversees the Superannuation Transaction Network (STN) and the SuperStream messaging data network. While the ATO continues to act as an observer, GNGB plays a key role in ensuring the securities and efficiencies of networks managing over $4.5 trillion in assets, establishing Australia’s superannuation system as one of the fastest-growing in the world.

Conclusion

Operation Honey Bee is a vital exercise orchestrated by GNGB to assess and strengthen the cyber resilience of Australia’s superannuation industry. With growing participation each year, the exercise focuses on improving incident response strategies, addressing capability gaps, and fostering enhanced information sharing among stakeholders. As the sector continues its expansion, these coordinated initiatives are critical to protecting the financial future of Australians.

Q: What is Operation Honey Bee?

A: Operation Honey Bee is an annual exercise carried out by GNGB to evaluate the Australian superannuation sector’s reaction to coordinated cyber-attacks.

Q: Who takes part in Operation Honey Bee?

A: This year, the exercise features over 50 participants, including 15 superannuation funds, service providers, regulators, and government stakeholders.

Q: What are the key goals of the exercise?

A: The exercise aims to assess incident response plans, identify capability gaps, and enhance information sharing during cyber incidents.

Q: Why is GNGB involved in this exercise?

A: GNGB is responsible for managing the Superannuation Transaction Network and SuperStream, ensuring the cyber resilience and safety of the sector.

Q: How significant is Australia’s superannuation system?

A: The system manages more than $4.5 trillion in assets and is among the fastest-growing pension systems globally.

Q: What is the role of the Australian Taxation Office in GNGB?

A: The ATO is not a member of GNGB but takes part as an observer in the network.

Budget-Friendly GAC AION EV Poised to Launch in Australian Market Below $30,000


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

  • GAC plans to launch a budget-friendly EV in Australia, priced at less than A$30,000.
  • The EV will be equipped with a 44kWh Magazine Battery 2.0, offering a range of 320km.
  • This vehicle is aimed at city drivers and those new to EVs.
  • GAC intends to rival conventional petrol cars in terms of price.
  • Charging at home is easy with a smaller battery designed for urban usage.

Overview of GAC’s Latest EV Introduction

The electric vehicle market in Australia has transformed rapidly, moving away from premium-priced options towards a competitive space prioritizing affordability. Chinese manufacturers have played a pivotal role in this shift, with GAC spearheading the most recent efforts.

Specifications for Battery and Performance

  • Battery Technology: This new EV features a 44kWh Magazine Battery 2.0, recognized for its safety standards.
  • Range: Provides a WLTP estimated driving distance of 320km.
  • Urban Optimization: Built for everyday urban transportation needs.

Insights on the 44kWh Battery

The 44kWh Magazine Battery 2.0 balances performance with cost-effectiveness. With a driving range of 320km, it is ideal for daily travels in Australian urban centers where the average distance covered is below 50km daily, offering a practical cushion for drivers.

Pricing Perspectives for the Australian Market

While the exact price remains unconfirmed, this new version is anticipated to be below A$30,000, positioning it as one of the more economical EVs in Australia, rivaling traditional petrol vehicles on cost.

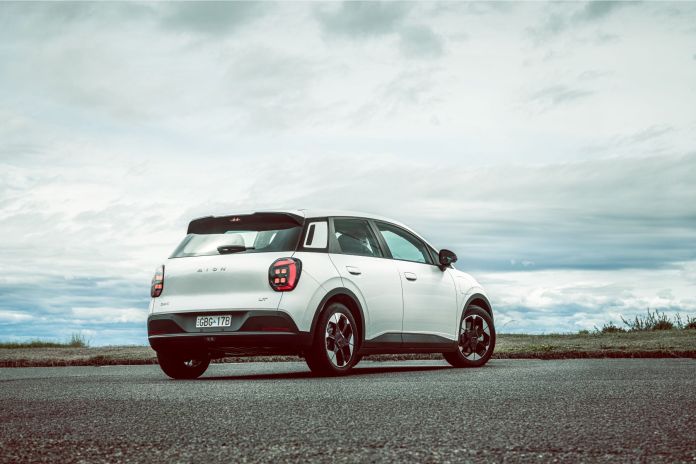
GAC AION EV affordable Australian market

Target Market: New EV Enthusiasts

GAC is targeting this model towards novice EV buyers and city-based families, providing an approachable entry into electric driving. The design and roomy interior appeal to younger drivers and students.

Benefits of Home Charging

Home charging is straightforward, with the 44kWh battery capable of charging overnight efficiently. This fast charging advantage is beneficial for city residents with garage or driveway access, and rapid chargers can quickly replenish the battery as needed.

Concluding Observations on GAC’s Growth

GAC’s new model represents the growing availability of EVs in Australia. If it maintains competitive pricing, it could play an essential role in the nation’s electric vehicle industry, offering affordable solutions tailored to consumer preferences.

Recap

GAC is ready to change the Australian EV landscape with an economical model aimed at city driving. With an emphasis on cost-efficient battery technology and practical range, this upcoming EV presents an attractive option for price-sensitive consumers compared to petrol vehicles.

Q: What will the new GAC EV’s price be in Australia?

A: The anticipated price for the new GAC EV is below A$30,000.

Q: What kind of driving range does the GAC AION EV provide?

A: The GAC AION EV is estimated to offer a driving range of 320km.

Q: Who is the intended audience for the new GAC EV?

A: The intended audience includes novice EV buyers, younger individuals, students, and urban commuters.

Q: What charging methods are available for the GAC AION EV?

A: The EV can be charged at home using a typical wall outlet or AC wallbox and also supports fast charging at DC charging stations.

Q: How does the GAC AION EV stack up against conventional petrol vehicles?

A: The GAC AION EV offers competitive pricing with petrol vehicles and provides the distinct advantages of electric driving.

Q: What are the key features of the 44kWh Magazine Battery 2.0?

A: It is distinguished by its safety features and cost-effective performance tailored for city driving.

NBN Co’s SaaS Implementation Increases IT Costs


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

NBN Co’s IT Expenses Escalate with SaaS Implementation

Quick Summary

  • NBN Co’s IT and software expenditures rose by six percent in FY26 due to the adoption of SaaS.
  • The utilization of AI has not substantially influenced NBN Co’s technology budget.
  • NBN Co’s revenue for FY26 reached $5.92 billion, reflecting a three percent year-over-year increase.
  • The shift from copper to fibre is propelling the introduction of faster, costlier plans.
  • NBN Co intends to transition customer groups to full fibre beginning in 2028.

Escalating IT and Software Expenses

During the 2026 financial year, NBN Co noted a six percent increase in “other” operating expenses, mainly due to heightened investments in IT and software. This rise corresponds with the company’s move towards cloud services, although cost mitigation strategies and lowered discretionary spending have lessened the overall effect.

NBN Co's SaaS implementation increases its IT expenses

Software Licensing Issues

The overall rise in software licensing expenses has particularly impacted government organizations, with NBN Co being among them. The firm, recognized for its use of VMware products, has encountered possible price increases, though specific details regarding contracts remain private.

AI’s Contribution to NBN Co’s Functioning

Even though artificial intelligence is being increasingly implemented within NBN Co, CEO Ellie Sweeney affirmed that AI has not substantially affected the IT budget. Currently, AI is employed to create post-incident reports and prepare teams for infrastructure repairs, thereby enhancing operational productivity without significantly raising costs.

Financial Results and Strategic Changes

For FY26, NBN Co reported revenues of $5.92 billion, indicating a three percent growth compared to the preceding year. This increase was fueled by the transition of customers from copper-based services to full fibre, which led to the uptake of faster and more expensive plans.

The organization is determined to decrease Australia’s reliance on outdated copper infrastructure. Beginning in 2028, NBN Co intends to actively transition customer groups to full fibre, with the goal of improving customer satisfaction and achieving resilience and reliability objectives.

Conclusion

The shift to software as a service by NBN Co has resulted in increased IT and software costs, while AI has not greatly influenced the budget. The company continues to progress in moving customers from copper to fibre, aiding revenue growth and enhancing service offerings.

Questions & Answers

Q: What factors have led to the growth in NBN Co’s IT and software expenses?

A: The increase primarily results from the adoption of cloud-based services, leading to elevated IT and software expenditures.

Q: Has AI implementation had a significant effect on NBN Co’s technology budget?

A: No, the use of AI has not materially influenced the company’s technology budget.

Q: What was NBN Co’s revenue for the FY26 financial year?

A: NBN Co recorded a revenue of $5.92 billion for FY26, a three percent increase compared to the previous year.

Q: How is NBN Co addressing its dependence on copper infrastructure?

A: NBN Co is gradually moving customers to full fibre, with plans to start proactively transitioning customer groups from 2028.

Q: What function does AI serve in NBN Co’s operations?

A: AI is utilized to draft post-incident reports and prepare teams for infrastructure repairs, contributing to more efficient network operations.

CBA’s AI Assistant Prepared to Confront Challenging Questions


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Commonwealth Bank’s AI Assistant “Companion” Faces New Challenges

Quick Overview

  • The AI assistant “Companion” by Commonwealth Bank is crafted to respond to inquiries regarding spending and saving.
  • Companion employs dedicated safeguards for delicate matters such as gambling and financial exploitation.
  • Due to regulatory restrictions, the AI is unable to dispense financial advice.
  • Companion operates on a multi-agent framework involving various CBA teams alongside AWS collaboration.
Commonwealth Bank's AI assistant addresses new challenges

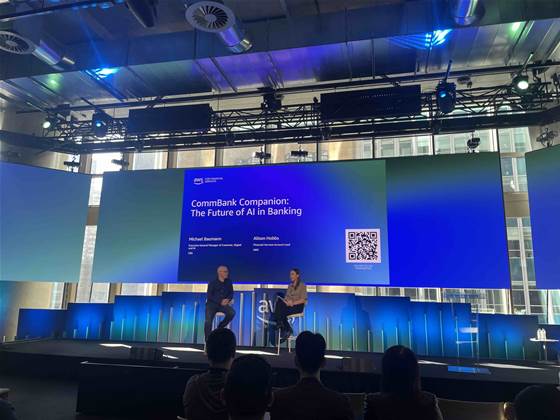
(L-R) Michael Baumann (CBA) and Alison Hobbs (AWS).

Overview of Companion

Commonwealth Bank has launched its AI assistant “Companion” to manage inquiries that clients generally do not pursue through traditional means. This initiative signifies a wider commitment to incorporating AI into banking services, offering a tailored experience in financial management.

Customer Engagement and Duties

Companion emphasizes inquiries related to spending and saving, with half of current questions concentrated in these domains. Created as a personal finance tool, it allows clients to examine their financial situations in ways that conventional bank personnel may not accommodate. This evolution highlights the AI’s ability to enhance rather than replace human interaction.

Handling Sensitive Issues and Safeguards

The AI is equipped with safeguards to recognize sensitive topics such as gambling concerns and financial exploitation. These systems steer users toward specialized human teams, guaranteeing that intricate issues receive the necessary support.

Limitations on Financial Guidance

Even with its potential, Companion is prohibited from providing financial advice due to regulatory policies. The ability of AI to offer such recommendations is still a matter of debate, necessitating changes in legislation to permit this capability.

Architectural Framework and Partnerships

Companion’s structural design is multi-agent, incorporating collaboration among various CBA teams and partners like AWS. This distributed model ensures that every element conforms to the overarching design and quality benchmarks, reflecting the bank’s dedication to innovation.

Conclusion

The AI assistant “Companion” from Commonwealth Bank showcases the fusion of technology in contemporary banking, addressing customer inquiries and improving financial management. While it currently contends with regulatory limitations, its development signifies a notable progression towards more engaging and personalized banking services.

Q&A

Q: What is the main role of CBA’s AI assistant “Companion”?

A: Companion primarily focuses on spending and saving inquiries, offering a personal financial management resource for clients.

Q: How does Companion handle delicate matters?

A: It utilizes safeguards to identify sensitive topics and directs clients to specialized human teams for proper assistance.

Q: Is Companion able to give financial advice?

A: No, Companion is not permitted to provide financial advice due to regulatory constraints.

Q: What type of architecture does Companion utilize?

A: Companion employs a multi-agent architecture with contributions from various CBA teams and collaborations with AWS.

Mark Zuckerberg Reveals Innovative AI Vision, Aims for Global Superintelligence


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Mark Zuckerberg Reveals Innovative AI Vision

Quick Insights

  • Mark Zuckerberg champions personal superintelligence instead of centralized authority.
  • Meta concentrates on personal AI agents and intelligent eyewear for everyday application.
  • Superintelligence to enhance creativity and entrepreneurship, beyond mere automation.
  • AI to deliver customized education and expedite medical innovations.
  • Zuckerberg advocates for power equilibrium through universal access to AI resources.
  • Meta intends to provide complimentary AI tools to billions, with economical access to advanced functionalities.
  • Potential advantages for Australian users encompass affordable enterprise-level tools.

Countering the AI Catastrophe Rhetoric

Mark Zuckerberg has recently taken a stand against the prevailing fear-driven discourse surrounding artificial intelligence. Contrary to the assumption that AI could result in job displacement or human obsolescence, Zuckerberg endorses the democratization of AI. He asserts that genuine advancement derives from equipping individuals as opposed to centralized powers.

Personal AI Assistants and Smart Eyewear

Meta envisions personal AI assistants incorporated within smart eyewear to support users in their daily activities. These assistants will function continuously, helping users with tasks like organizing schedules, managing finances, and even pursuing hobbies. Privacy is a top concern, backed by robust security measures similar to WhatsApp’s encryption.

Creation Over Automation

Meta frames AI as a catalyst for human creativity rather than merely a tool for automation. Zuckerberg envisions a future where individuals can independently develop software, media, and businesses, which in turn diminishes the necessity for large teams. This transformation aims to elevate entrepreneurship and economic prospects.

Customized Educators and Medical Innovations

In the realm of education, Meta seeks to offer accessible personalized educators, promoting individualized learning experiences for students. In healthcare, AI is set to hasten discoveries, with projects like the Chan Zuckerberg Biohub leading to swift progress in treating uncommon ailments.

Power Equilibrium, Not Mythical Harmony

Zuckerberg critiques the idea of a singular, perfectly harmonized superintelligent system. Rather, he promotes the widespread distribution of AI tools, allowing various systems to establish checks and balances. This strategy aspires to democratize power and avoid central authority.

Complimentary Access and Practical Economics

Meta plans to provide fundamental AI tools at no cost to billions, with affordable alternatives for supplementary computing capacity. This open approach contrasts with closed ecosystems that limit advanced functionalities, aiming to guarantee broad access to AI technologies.

Potential Ramifications in Australia

For Australians, Meta’s vision holds substantial promise. With forthcoming software updates and innovations like Ray-Ban Meta smart glasses, local entrepreneurs could utilize powerful resources without significant financial commitments. Nonetheless, privacy and data sovereignty are critical factors for both users and policymakers.

Conclusion

Mark Zuckerberg’s AI vision underscores individual empowerment, advocating for the extensive distribution of superintelligence resources. By centering on personal AI agents and promoting a balanced distribution of power, Meta aims to improve creativity, education, and healthcare. The open-access approach could favor Australians by delivering affordable, enterprise-grade technology to small enterprises and individuals.

Questions & Answers

Q: What is Mark Zuckerberg’s primary stance concerning AI?

A: Zuckerberg contends that personal superintelligence should be available to all, rather than being monopolized by a select few elite organizations.

Q: How does Meta propose to weave AI into everyday life?

A: Meta intends to employ personal AI assistants and smart eyewear to support users with daily tasks, while ensuring stringent privacy measures.

Q: What influence could this vision have on employment opportunities?

A: By promoting creativity and entrepreneurship, Meta’s vision could generate new business ventures, lessening the dependence on large teams and encouraging economic development.

Q: How does Meta plan to tackle AI safety issues?

A: Meta advocates for a power balance through widespread AI access, enabling different systems to offer checks and safeguards.

Q: Are these tools going to be complimentary?

A: Basic versions of AI tools will be available for free, with cost-effective options for users requiring additional computational resources.

Q: What are the repercussions for Australian users?

A: Australians might gain from low-cost, advanced technology, empowering small enterprises and individuals to embark on ambitious projects.

Komatsu Australia Transitions 4000 Users to Groundbreaking Zero Trust Cloud Security


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Komatsu Australia Adopts Zero Trust Cloud Security

Quick Read

  • Komatsu Australia is integrating a zero trust network framework to tackle advancing cybersecurity challenges.
  • A pilot initiative utilizing Zscaler’s cloud-based security will commence with 100 users, with plans to scale up to over 4000 users.
  • This initiative addresses worries about AI-fueled cyber threats and internal security vulnerabilities.
  • Zero trust exchange will take the place of conventional network security infrastructure, shifting from a capex to an opex approach.

Why Choose Zero Trust?

In a time when cyber threats are rapidly changing, Komatsu Australia has acknowledged the necessity to enhance its cybersecurity strategies. By embracing a zero trust network architecture, the organization seeks to safeguard its corporate network against potential incursions, especially those driven by sophisticated AI systems.

Transition to Zero Trust Cloud Security

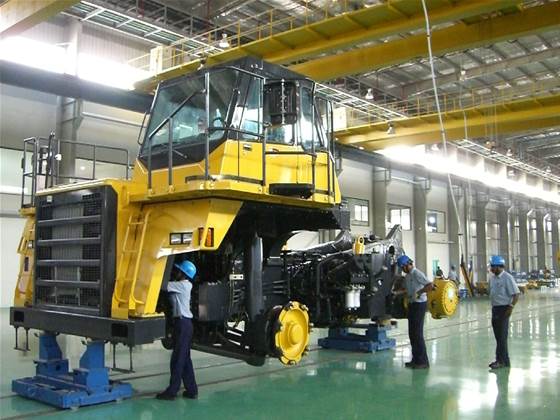
Komatsu Australia plans to initiate a pilot of Zscaler’s cloud-based zero trust exchange by the end of this month. Starting with 100 users, the pilot intends to grow to over 4000 users across Australia, New Zealand, New Caledonia, and Papua New Guinea. The zero trust model examines every device accessing the network with equal scrutiny, irrespective of whether it is used by a remote worker or an on-site employee.

Tackling AI-Fueled Threats

Henry Wright, cybersecurity manager at Komatsu Australia, underscored the main concern: the emergence of AI-powered cyber threats. New AI agents could independently initiate cyber-attacks, presenting a considerable danger. Wright pointed out particular worry regarding AI systems like Claude Mythos, which can rapidly analyze environments for weaknesses.

How Zscaler’s Zero Trust Functions

Zscaler’s zero trust network access (ZTNA) framework utilizes a switchboard concept linking end users, applications, and the internet. It incorporates client connectors on devices and lightweight virtual machines within data centers to enforce security controls through Zscaler’s global Zero Trust Exchange platform. This configuration guarantees stringent management of application and internet access.

Transition from Capex to Opex Model

The implementation of zero trust security signifies a transition for Komatsu from a capital expenditure (capex) model to an operational expenditure (opex) model. This change reflects trends in other sectors, where businesses favor more adaptable and cost-efficient security solutions.

Summary

Komatsu Australia’s shift to a zero trust cloud security model signifies a proactive measure in strengthening its cybersecurity framework. By utilizing Zscaler’s cutting-edge solutions, the company seeks to reduce risks related to AI-driven cyber threats and enhance its security operations.

Q&A Section

Q: What is zero trust network architecture?

A: Zero trust network architecture is a security paradigm that necessitates rigorous verification for any device attempting to access a network, no matter its location.

Q: Why is Komatsu Australia implementing this framework?

A: The organization aims to defend against evolving cybersecurity threats, particularly those prompted by advanced AI systems, and enhance its internal security measures.

Q: How does Zscaler’s Zero Trust Exchange function?

A: It employs client connectors and virtual machines to govern and secure access among end users, applications, and the internet via a cloud infrastructure.

Q: What are the advantages of transitioning from capex to opex in security?

A: This change enables businesses to minimize upfront expenditures, enhance adaptability, and concentrate on operational efficiencies within their security approaches.

Q: How does this transition aid in combating AI-driven threats?

A: By limiting the attack surface and enforcing strict access controls, Komatsu can improve its defenses against autonomous AI cyber assaults.

Mitsubishi Reintroduces Electric ASX VR-e for Australia Utilizing Foxconn’s Cutting-Edge Technology


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Mitsubishi has unveiled the ASX VR-e electric vehicle for the Australian market, scheduled to debut in late 2026.
  • The ASX VR-e features the Foxtron Bria platform from Foxconn, offering a contemporary EV experience.
  • It will be offered in LS, XLS, Exceed, and high-performance GSR variants.
  • Equipped with a 57.7 kWh lithium iron phosphate battery, it boasts a range of up to 516 km (NEDC).
  • Fast charging capability allows for an 80% charge in less than 30 minutes.
  • Designed with a drag coefficient of Cd 0.26 for enhanced aerodynamics.
  • The interior includes a 15.6-inch touchscreen and a 9.2-inch digital instrument cluster.
  • Expected pricing will start at A$40,000 for the base model.

Mitsubishi’s Electric Comeback

Mitsubishi Motors is making a renewed entry into the Australian electric vehicle sector with the ASX VR-e, set to launch in late 2026. Although it’s not the anticipated EVO electric variant, this new offering reflects Mitsubishi’s dedication to electrification, marking its return to all-electric vehicles since the i-MiEV.

Collaboration with Foxconn and Platform

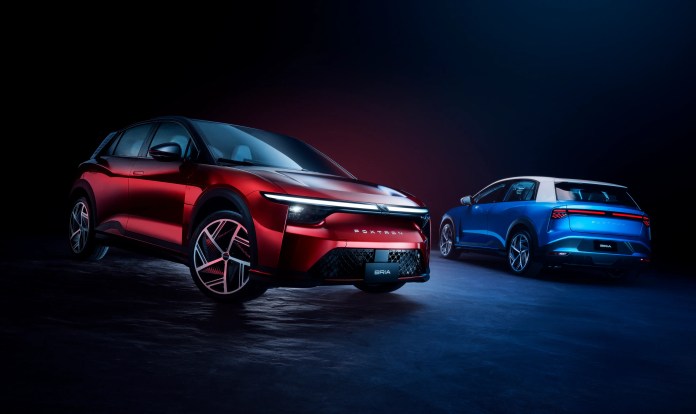
The ASX VR-e is built on the Foxtron Bria platform by Foxconn, highlighting a strategic alliance that enables Mitsubishi to introduce an advanced EV swiftly. This innovative electric crossover benefits from Foxconn’s extensive electronics know-how, featuring a software-defined architecture with ongoing updates.

Mitsubishi ASX VR-e Electric Vehicle Collaboration with Foxconn

Trims and Performance Metrics

The ASX VR-e will come in four trim levels: LS, XLS, Exceed, and the performance-oriented GSR. The GSR variant features a dual-motor configuration, enabling it to accelerate from 0-100 km/h in a mere 3.9 seconds.

Battery Capacity and Range

With a 57.7 kWh lithium iron phosphate battery, the ASX VR-e can achieve a range of up to 516 km on the NEDC cycle. Under real-world Australian driving conditions, the WLTP range is anticipated to be between 380-410 km.

Charging Features

Fast charging features allow the ASX VR-e to charge from 10% to 80% in under 30 minutes with a 134 kW DC charger. Additionally, a standard 7 kW AC charger is offered for home charging overnight.

Aesthetic and Aerodynamic Design

The ASX VR-e presents a stylish, aerodynamic profile with a drag coefficient of Cd 0.26. Its futuristic design is complemented by a full-width lightbar and sculpted shapes to improve efficiency.

Mitsubishi ASX VR-e Electric Vehicle Interior and Technology

Advanced Interior Features

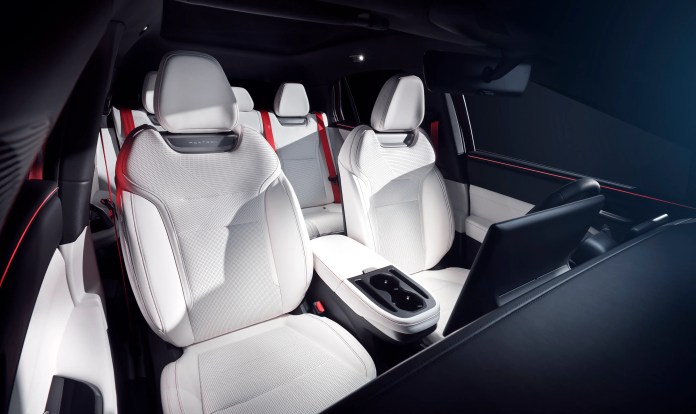
The cabin is equipped with a 15.6-inch touchscreen interface and a 9.2-inch digital instrument panel. The minimalist aesthetic offers a spacious environment, enhanced by advanced digital features for over-the-air updates.

Measurements and Usability

With a length of 4,315 mm, width of 1,885 mm, and height of 1,535 mm, the ASX VR-e is a compact crossover that boasts a tight turning radius of 5.59 metres. It provides 320 litres of cargo capacity, which expands to 1,043 litres when the rear seats are down.

Estimated Pricing and Market Strategy

Pricing information is forthcoming, but it’s anticipated that the base LS will begin around A$40,000. The GSR model may surpass A$60,000, allowing Mitsubishi to position itself competitively within the electric vehicle market.

Conclusion

Mitsubishi is poised to re-establish itself in the Australian electric vehicle sector with the ASX VR-e, capitalizing on its partnership with Foxconn. The vehicle’s modern tech, performance capabilities, and appealing design are expected to meet a variety of consumer requirements. With an anticipated launch in late 2026, excitement is mounting for this groundbreaking electric crossover.

FAQs

Q: When will the Mitsubishi ASX VR-e be available in Australia?

A: The ASX VR-e is projected to arrive in Australian dealerships in the fourth quarter of 2026.

Q: On what platform is the ASX VR-e built?

A: The ASX VR-e utilizes Foxconn’s Foxtron Bria platform, engineered for an innovative electric crossover experience.

Q: What are the anticipated range and charging capabilities?

A: The ASX VR-e provides a range of up to 516 km (NEDC) and features fast charging, reaching 80% in under 30 minutes.

Q: What trim levels can be expected for the ASX VR-e?

A: The vehicle will be offered in LS, XLS, Exceed, and high-performance GSR trims.

Q: How does the ASX VR-e perform?

A: The GSR variant features a dual-motor configuration that accelerates from 0-100 km/h in 3.9 seconds, placing it in the performance vehicle category.

Q: What is the expected starting price for the ASX VR-e?

A: The base LS model is anticipated to start around A$40,000, with upper trims potentially exceeding A$60,000.

Eightcap Integrates AI to Improve Compliance Throughout Global Markets


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Eightcap Employs AI to Enhance Compliance Across Global Markets

Quick Overview

  • Eightcap, a prominent Australian fintech, is advancing compliance through AI technologies.
  • Role-specific access controls are established to fulfill varying regulatory requirements globally.
  • AI streamlines compliance tasks, including call transcript creation and analysis of customer sentiment.
  • The company leverages Salesforce to optimize operations and maintain data privacy.
  • Eightcap is researching AI to bolster internal security and anticipate regulatory demands.

Eightcap’s Cutting-Edge Compliance Strategy

Rapidly expanding Australian fintech Eightcap is harnessing artificial intelligence (AI) to handle its growing compliance responsibilities. The firm ensures that customer data aligns with privacy, access, and data sovereignty standards across diverse jurisdictions, underscoring its focus on innovation and security.

Eightcap utilizes AI to enhance compliance across global markets

Role-Specific Access Controls

Eightcap has incorporated role-specific access controls within its customer relationship management platform. This enables globally dispersed teams, such as sales, onboarding, support, and compliance, to access customer data while limiting access to sensitive information based on their designated roles. This approach guarantees that all teams operate with uniform information, enhancing customer interactions and compliance oversight.

Using Salesforce for Data Protection

Salesforce forms the backbone of Eightcap’s operations. The platform’s built-in security features bolster the company’s objective of safeguarding customer information. By utilizing Salesforce, Eightcap ensures that its data access is protected and fulfills the stringent requirements of various regulatory frameworks.

AI’s Role in Compliance Operations

Eightcap employs AI to automate repetitive compliance processes, such as generating call transcripts, summarizing discussions, and flagging duplicate entries. AI also identifies key phrases and analyzes customer sentiment for further examination. This automation allows human agents to concentrate on more intricate matters, significantly lessening the manual effort once necessary in compliance duties.

Improving Security and Forecasting Compliance Needs

While the initial emphasis on AI was for compliance, Eightcap is now investigating how AI can reinforce internal security. By detecting atypical permissions and insider threats, AI aids in forecasting and addressing potential security vulnerabilities. Furthermore, as Eightcap ventures into new markets, AI is anticipated to shift compliance from a reactive to a proactive stance, predicting regulatory inquiries and efficiently compiling needed evidence.

Conclusion

Eightcap stands at the forefront of integrating AI to streamline compliance and data governance throughout its worldwide operations. By adopting role-specific access controls, utilizing Salesforce, and automating compliance tasks, the firm ensures strong data privacy and security. As Eightcap continues to advance, AI will be pivotal in enhancing security and forecasting compliance requirements.

Q: What is Eightcap’s main objective in integrating AI?

A: The main objective is to efficiently manage compliance tasks while ensuring customer data privacy and security across different jurisdictions.

Q: How do role-specific access controls support Eightcap?

A: They enable various teams to access essential customer records while limiting access to sensitive data, thus ensuring consistent information dissemination and improved compliance administration.

Q: What importance does Salesforce hold in Eightcap’s operations?

A: Salesforce acts as the foundational platform, offering embedded data security features that uphold Eightcap’s data privacy and compliance obligations.

Q: In what way does AI enhance compliance operations at Eightcap?

A: AI automates duties like call transcript creation and conversation summarization, allowing human agents to focus on more complex challenges and minimizing manual workloads.

Q: What are Eightcap’s future intentions regarding AI in compliance?

A: Eightcap aims to leverage AI for anticipating regulatory demands and enhancing internal security by detecting potential insider threats and suspicious permissions.

Q: How does Eightcap maintain customer data privacy?

A: Eightcap fulfills privacy commitments by giving customers the option to have their personal information deleted or provided upon request, in line with applicable privacy regulations.