Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 141 of 187

TPG Telecom Revamps Organization to Integrate Cloud and Cybersecurity Services


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
Quick Read

  • TPG Telecom combines its cloud and cybersecurity teams into a new unit known as: Technology Security, Cloud & End to End Architecture.
  • After the reorganization, General Manager of Technology Security, Lee Barney, will be leaving the company.
  • This restructure is designed to enhance secure-by-design practices and promote the adoption of cloud security throughout the organization.
  • This new unit is in line with the Australian Government’s cybersecurity strategy for essential infrastructure.
  • The Cyber Centre of Excellence (CCoE) located in Sydney will maintain its collaborative efforts with industry and academic institutions.

TPG Telecom Restructures to Integrate Cloud and Cybersecurity Services
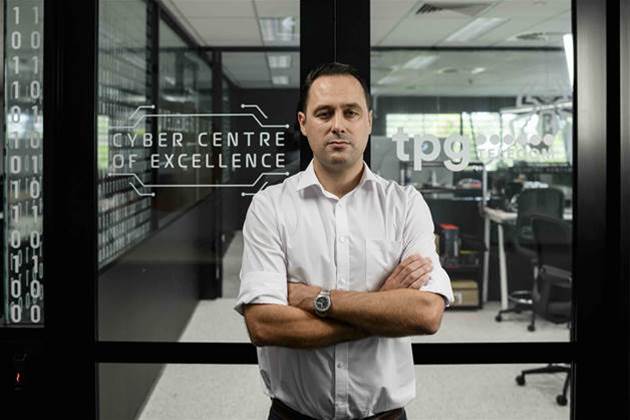
TPG Telecom restructure combines cybersecurity and cloud services

Lee Barney.

Leadership Change and Departure of Lee Barney

TPG Telecom has implemented a major organizational overhaul, merging its cloud infrastructure with its cybersecurity functions into a single entity named Technology Security, Cloud & End to End Architecture. This shift resulted in the exit of Lee Barney, who has been TPG’s General Manager of Technology Security for almost three years.

Barney announced his departure on LinkedIn, saying, “As the organization reshapes its leadership focus, I depart with the assurance that the team is well-equipped for the upcoming challenges.” Although TPG Telecom has yet to appoint a leader for the new unit, there are currently no plans in place to find a direct successor.

Strategic Consolidation of Cloud and Security Teams

The merger of TPG’s cloud and security teams is driven by the imperative to cultivate secure-by-design principles, a strategy strongly advocated by the Australian Government’s cybersecurity policies. By integrating these divisions, TPG seeks to enhance coherence between development and security, guaranteeing that new platforms and services are secure from the outset.

A representative from TPG Telecom informed TechBest, “We are uniting security and cloud to design and construct security-native cloud solutions and enhance security capability adoption throughout the organization.”

Alignment with the National Cybersecurity Agenda

This integration aligns closely with the government’s Cyber Security Strategy 2023–2030, which urges organizations in critical infrastructure sectors, such as telecommunications, to adopt layered defensive strategies and secure-by-design methodologies.

This strategy features initiatives such as six “Cyber Shields” aimed at safeguarding Australia’s digital infrastructure, emphasizing collaboration between the public and private sectors, making TPG’s strategic move both timely and well-executed.

The Function of the Cyber Centre of Excellence (CCoE)

During Barney’s stewardship, TPG’s Cyber Centre of Excellence (CCoE) was launched in Sydney and began operations in late 2023. The CCoE aims to identify and address vulnerabilities in telecommunication and IT systems through both offensive and defensive cybersecurity methods.

This facility hosts TPG’s red and blue cybersecurity teams and includes representatives from industry leaders like Ericsson, Nokia, and Tata Consultancy Services (TCS) on rotating 90-day assignments. In collaboration with the University of New South Wales (UNSW), the center also promotes academic partnerships focused on threat research and innovation.

TPG’s Forward-Looking Cybersecurity Strategy

Even though Barney’s departure signifies a pivotal moment, TPG Telecom’s commitment to cybersecurity continues to strengthen. The amalgamation of cloud and security functions is anticipated to enhance workflows, diminish silos, and bolster resilience against new threats. The future of this unit will likely place greater emphasis on automation, AI-driven threat detection, and comprehensive cloud-native security solutions.

Summary

TPG Telecom has redesigned its technology division to merge cloud and cybersecurity services into a unified, cohesive unit. This strategic initiative follows the exit of General Manager Lee Barney and mirrors wider trends in Australia’s critical infrastructure sectors towards adopting secure-by-design methodologies. With its Cyber Centre of Excellence and alignment with national cybersecurity objectives, TPG Telecom is positioning itself as a more agile and security-focused telecommunications provider in an increasingly complex digital environment.

Q: Why did TPG Telecom restructure its technology division?

A:

The restructure is meant to integrate cloud and cybersecurity teams to develop security-native solutions and enhance security adoption throughout the organization, in line with Australia’s secure-by-design strategy.

Q: What is the name of the new function?

A:

The newly formed organizational unit is referred to as Technology Security, Cloud & End to End Architecture.

Q: Who is in charge of the new function?

A:

Currently, TPG Telecom has not appointed a leader for the new function and has no immediate plans to replace Lee Barney.

Q: What impact did Lee Barney have on TPG Telecom?

A:

Barney was instrumental in establishing the Cyber Centre of Excellence, strengthening TPG’s overall security posture, and enhancing in-house cybersecurity capabilities during his time.

Q: What is the Cyber Centre of Excellence (CCoE)?

A:

Situated in Sydney, the CCoE is a facility focused on detecting vulnerabilities within telecom and IT systems. It hosts both red and blue teams, industry collaborators, and academic researchers working together to enhance cybersecurity outcomes.

Q: How does this restructuring connect with national policy?

A:

This restructure aligns with the Australian Government’s cybersecurity strategy, which promotes secure-by-design development and facilitates cooperation between public institutions and private enterprises.

Q: What are red and blue teams in cybersecurity?

A:

Red teams simulate actual cyberattacks to evaluate security systems, while blue teams protect against these threats to reinforce the organization’s defenses. Together, they elevate the security maturity of an organization.

Q: Will customers experience any changes due to this transition?

A:

No significant disruptions to customer services are anticipated. In the long run, customers may enjoy enhanced security and reliability in cloud-based offerings resulting from this integration.
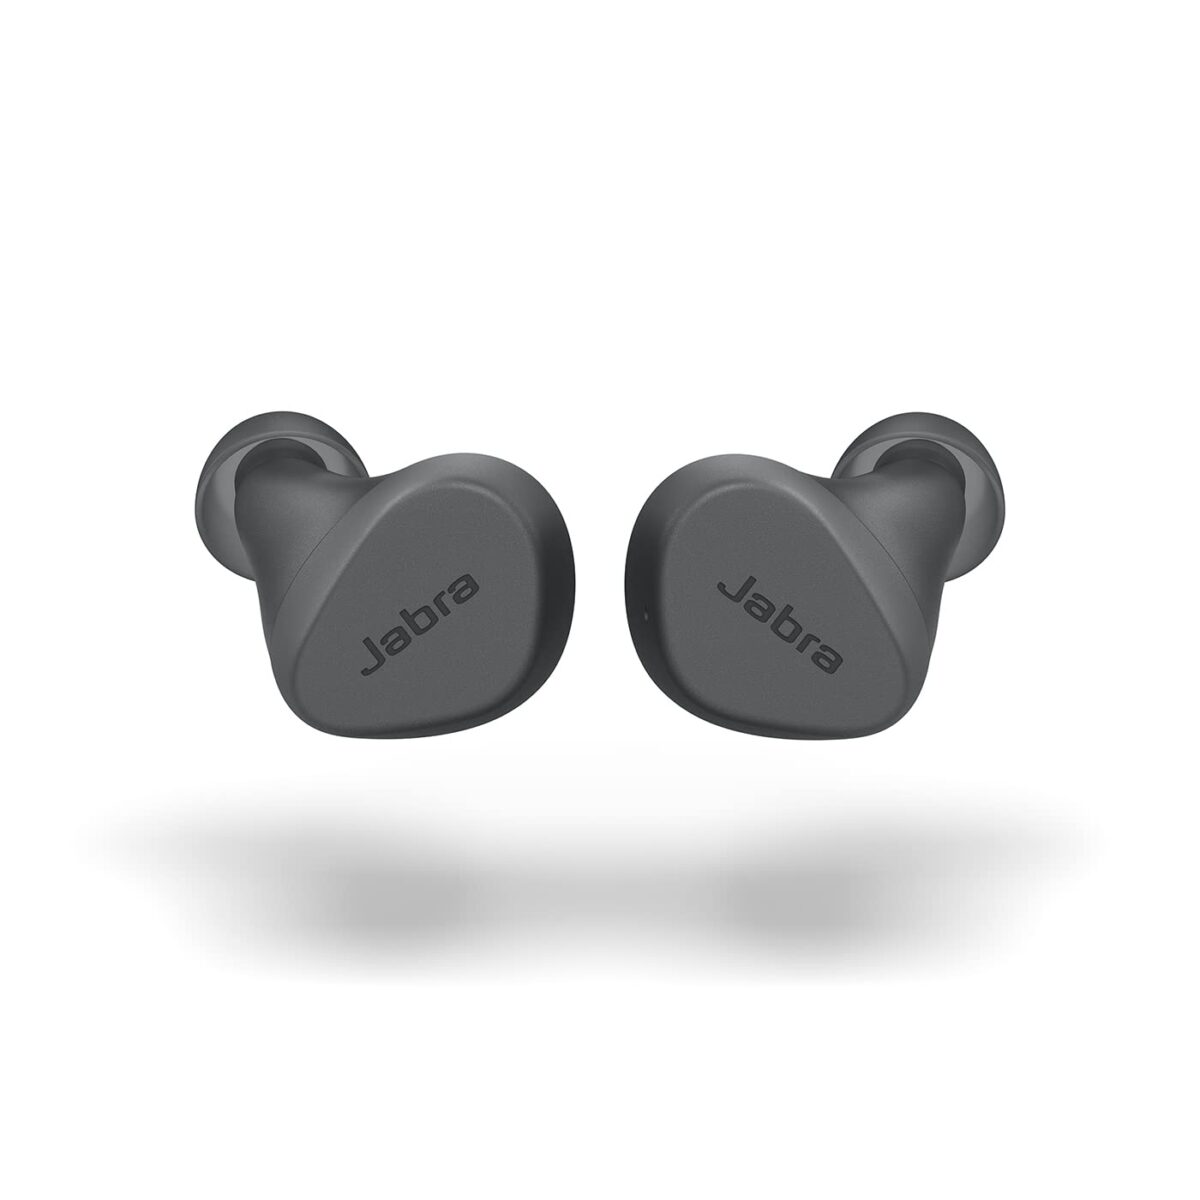
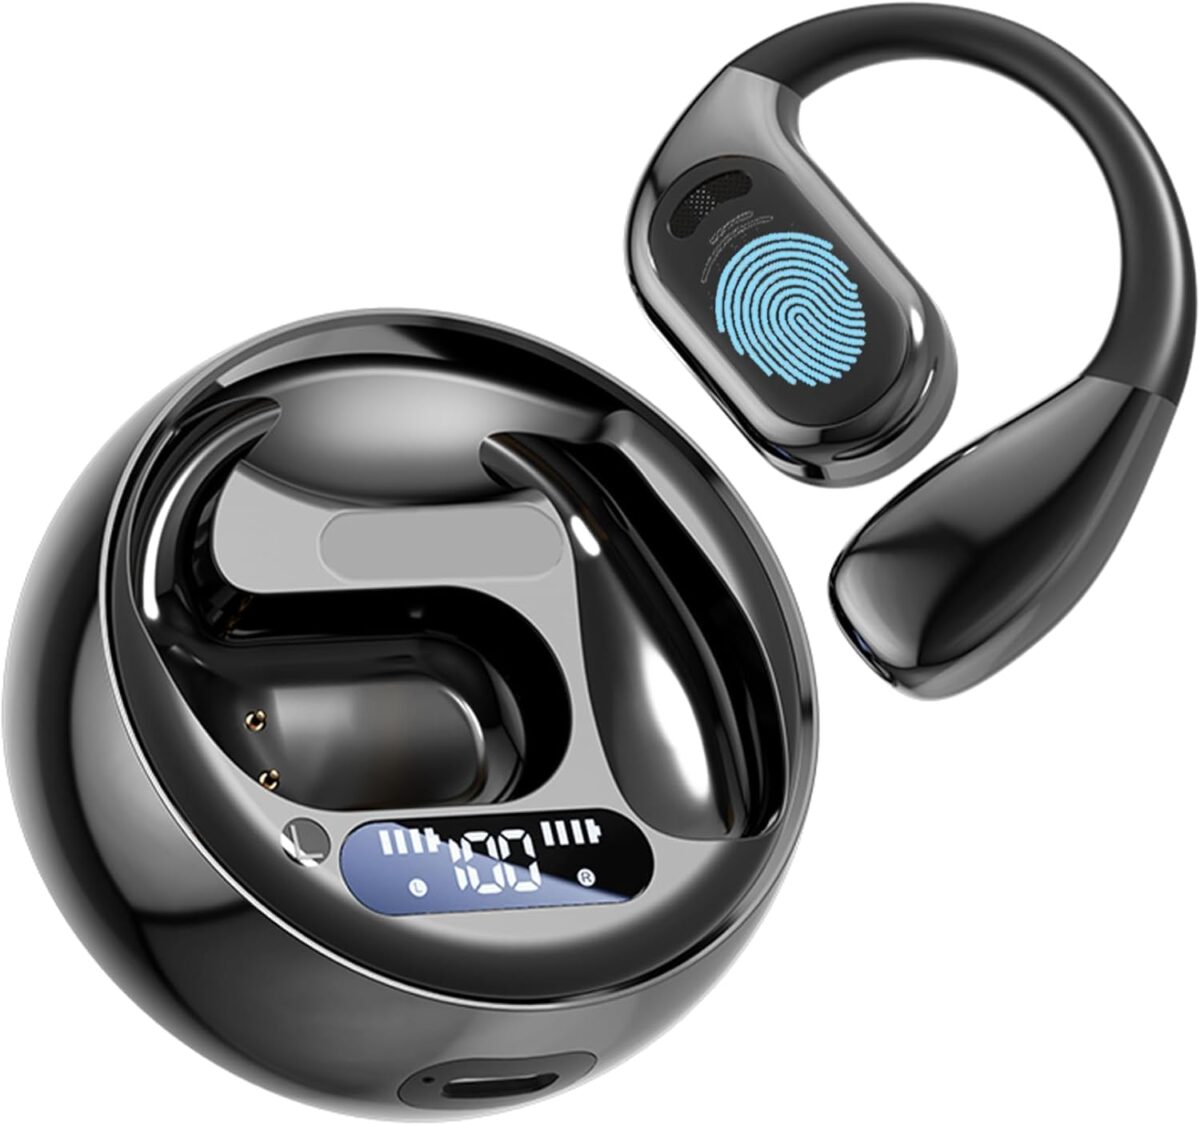
JABRA Elite 2 Wireless Earbuds Dark Gray EU Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

JABRA Elite 2 Wireless Earbuds Dark Gray EU

M76 Ai Translator Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

M76 Ai Translator Earbuds,Ai Headphones Language Translation,Wireless Bluetooth Translation Earbuds,Translation Headset for Business, Study and Travel,Black

Vodafone Raises Concerns About Telstra with ACCC Regarding Mobile Coverage Conflict


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Swift Overview

  • Vodafone has lodged a complaint against Telstra with the ACCC, accusing the latter of potentially deceptive mobile coverage assertions.
  • Reports indicate that Telstra’s coverage relies on external antennas typically not used by the general public.
  • Vodafone suggests that recent updates to Telstra’s website indicate a prior lack of clarity in representation.
  • The ACCC is contemplating a regulatory inquiry; Vodafone is considering legal action as well.
  • ACCAN is advocating for a formal investigation, citing significant consequences for consumers in regional areas.
  • The conflict arises from enduring disputes surrounding regional roaming and access to networks.
Vodafone refers Telstra to ACCC over misleading mobile coverage claims

Vodafone Targets Telstra’s Coverage Statements

Vodafone, a part of TPG Telecom, has officially submitted a grievance to the Australian Competition and Consumer Commission (ACCC), claiming that Telstra has misled consumers regarding its mobile coverage assertions. The telecommunications company is also contemplating legal measures, emphasizing that Telstra’s touted network range relies on equipment that is generally not utilized by ordinary mobile users.

The Core of the Issue: Coverage vs. Reality

The central issue in this debate is the methodology for measuring mobile coverage. Vodafone argues that Telstra’s 3 million square kilometre coverage assertion depends on the availability of “external antennas and powered repeaters”—devices often situated on buildings or vehicles, as opposed to being carried by consumers.

This claim is corroborated by the ACCC’s 2026 Mobile Infrastructure Report, highlighting how coverage claims can be inflated with the use of signal-enhancing technology. Vodafone argues that Telstra’s public maps and promotional content didn’t initially clarify this distinction.

Telstra’s Take: Rejection and Rationale

Telstra has acknowledged that it utilizes external antennas in its coverage assessments but refutes any intention to mislead. A Telstra representative stated, “Customers in regional and remote locations benefit from utilizing external antennas… our maps allow users to view coverage with and without these devices.”

Telstra asserts that it has consistently been transparent through its online resources, claiming that the recent enhancements to its website were aimed at better informing the public post-discussion with Vodafone—not an admission of misleading behavior.

Vodafone Calls for Action

Vodafone asserts that its ongoing appeals for Telstra to rectify or clarify the contested coverage claims were disregarded until recent modifications were made on Telstra’s site. Vodafone contends that these alterations are a tacit acknowledgment that the previous assertions were misleading.

Regardless, Vodafone insists that Telstra’s updates fail to resolve the issue adequately and has formally requested the ACCC to investigate. Legal routes are also being contemplated to compel Telstra to terminate its practices and possibly offer compensation.

Wider Industry Ramifications and MVNO Concerns

Vodafone emphasizes that mobile virtual network operators (MVNOs) utilizing Telstra’s infrastructure may have gained advantages from the purportedly exaggerated claims, implying that the matter transcends the two primary telecoms, affecting the broader industry.

Access to Telstra’s regional infrastructure has long been contentious. Vodafone previously sought roaming privileges via the ACCC, which were denied in 2022. A subsequent network-sharing agreement between TPG Telecom and Telstra was also turned down by the Competition Tribunal due to potential anti-competitive effects. Following these setbacks, TPG has allied with Optus for a regional network collaboration.

ACCAN Urges ACCC to Intervene

The Australian Communications Consumer Action Network (ACCAN) has lent its support to Vodafone’s appeal for regulatory action. CEO Carol Bennett termed the allegation that Telstra has exaggerated its network coverage for over a decade as “grave and harmful.”

“Many Australians in remote locales depend on Telstra under the assumption that it’s the sole provider with dependable service,” she remarked. “If the coverage benefits have been overstated, then consumers are being misled into paying higher prices for potentially illusory advantages.”

ACCAN is urging the ACCC to take decisive measures if the allegations hold true, asserting that “misleading and deceptive practices are unacceptable in any market, particularly one dealing with essential services.”

Conclusion

Vodafone has placed Telstra under scrutiny, accusing its competitor of misleading Australians—especially those in rural and remote areas—by inflating its mobile coverage claims. The debate revolves around whether Telstra’s network assertions accurately reflect actual device functionality or depend on specialized signal-enhancing equipment. With the ACCC now contemplating an inquiry and ACCAN backing the initiative, the eventual outcome could significantly impact mobile competition and consumer confidence throughout Australia.

Q: What is the main issue between Vodafone and Telstra?

A:

Vodafone contends that Telstra misrepresented its mobile coverage by encompassing areas only accessible via external antennas, which are not normally utilized by regular mobile users. This, they claim, misleads individuals about the practical usability of Telstra’s network.

Q: Has Telstra responded to the accusations?

A:

Yes. Telstra refutes any accusations of misconduct and argues that its maps and marketing materials have consistently enabled users to view coverage with and without the use of external antennas. It states that the recent adjustments to its website were made to clarify this distinction further after discussions with Vodafone.

Q: What action is Vodafone pursuing?

A:

Vodafone is advocating for a regulatory inquiry by the ACCC and is exploring legal options to compel Telstra to halt its practices and potentially provide restitution for any misleading statements.

Q: What is the ACCC’s position so far?

A:

The ACCC has confirmed it is “considering” Vodafone’s referral but has not yet declared a formal investigation.

Q: What role does ACCAN play in this dispute?

A:

ACCAN, Australia’s foremost consumer advocacy organization for communications, backs Vodafone’s call for an examination. It has highlighted the possible detriment to regional consumers and called for stringent regulatory measures should Telstra’s actions be found misleading.

Q: How does this impact regional customers?

A:

If Telstra’s coverage assertions are proven to be overstated, regional Australians may have been misled into selecting Telstra over more cost-effective or comparable options under the false impression that it was the only trustworthy alternative.

Q: Has Vodafone previously attempted to access Telstra’s regional network?

A:

Yes. Vodafone has previously approached the ACCC to obtain access to Telstra’s regional network for roaming, but that request was rejected. Additionally, a later network-sharing proposal between TPG Telecom and Telstra was also blocked by the Competition Tribunal.

Q: What steps follow?

A:

The ACCC is assessing the complaint. Should it find substance in Vodafone’s allegations, it may initiate a formal inquiry, which could lead to penalties, required clarifications from Telstra, or more extensive modifications in how mobile coverage marketing is conducted across the sector.

Xiaomi Redmi Buds 6 Lite Hybrid ANC Wireless Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Xiaomi Redmi Buds 6 Lite Hybrid ANC Wireless Earbuds, Active Noise Cancellation up to 40 dB, 38 Hours Music Playback, Custom EQ Mode, Google Fast Pair Compatible, Fast Charging, USB, Type-C Small,

Telegram Closes Two Significant Black Market Activities


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Telegram Takes Action Against $54.6 Billion Black Market Activities

Brief Overview

  • Telegram has closed down two prominent black markets: Xinbi Guarantee and Huione Guarantee.
  • These platforms were responsible for facilitating more than AU$54.6 billion in illegal transactions since 2021.
  • They were recognized as central locations for cybercriminals, fraudsters, and money laundering activities.
  • Huione Guarantee is associated with the Cambodia-based Huione Group, which is also connected to North Korean cybercrime.
  • The U.S. authorities have blacklisted Huione Group for its support of malicious cyber actors.
  • This closure represents a major setback for global online fraud and digital crime networks.
Telegram shuts down two significant black market platforms

Telegram’s Fight Against Cybercrime Networks

Telegram, the cloud-based messaging service, has taken significant steps by shutting down two infamous black markets—Xinbi Guarantee and Huione Guarantee—both of which were operating openly on its platform. These Chinese-language services were notorious for enabling cybercrime, providing opportunities for stolen data trading, money laundering, and even telecom infrastructure for scammers.

Telegram asserted that such unlawful activities breach its terms of service and are eliminated as soon as they are detected. This action underscores an increasing commitment by technology platforms to combat illegal activities that occur in plain sight.

AU$54.6 Billion in Illegal Transactions

As per the blockchain analytics company Elliptic, Xinbi Guarantee and Huione Guarantee jointly facilitated over US$35 billion (approximately AU$54.6 billion) in transactions since 2021. This far exceeds the volume of the infamous dark web marketplace Silk Road, which was shut down by the FBI in 2013 after facilitating around US$1.2 billion in drug-related transactions.

“This is a significant setback for online fraudsters who depended on these markets for stolen data, laundering services, and telecom infrastructure,” commented Elliptic.

What Were Xinbi and Huione Guarantee?

Xinbi Guarantee and Huione Guarantee functioned as escrow services and transaction intermediaries within illicit Telegram groups. These offerings were utilized by cybercriminals to conduct large-scale fraudulent schemes, including investment scams and identity theft. Their closure has disrupted a vital segment of the underground digital economy.

Huione Guarantee had recently undergone a rebranding as “Haowang Guarantee” before its termination. It confirmed on its official website that it had been blocked by Telegram and announced the cessation of its operations.

Connections to the North Korean Lazarus Group

Huione Guarantee is a division of the Cambodia-based Huione Group, which also runs Huione Pay and Huione Crypto. These organizations have drawn attention from international law enforcement. In 2023, Huione Pay was linked to a cryptocurrency wallet tied to the notorious North Korean Lazarus Group, a state-sponsored hacking entity responsible for some of the globe’s most remarkable cyberattacks.

This discovery, along with subsequent financial connections, resulted in the United States government placing the entire Huione Group on a sanctions list, restricting its access to the U.S. financial system. Treasury Secretary Scott Bessent referred to the group as “the preferred marketplace for malicious cyber actors.”

Global Consequences and Australia’s Cybersecurity Scenario

Australia, similar to many other countries, is increasingly influenced by international cybercrime organizations. The dismantling of Xinbi and Huione could assist in decreasing the number of scams and fraudulent investment operations aimed at Australians. In 2023 alone, Australians fell victim to over $3 billion in scams, according to Scamwatch. Eliminating communication pathways utilized by scammers may help mitigate this escalating problem.

Cybersecurity professionals in Australia have praised Telegram’s actions but caution that more measures need to be implemented. Criminal enterprises are highly adaptable, and new avenues may appear to replace those that have been dismantled.

Conclusion

Telegram’s action against Xinbi Guarantee and Huione Guarantee has delivered a severe setback to the cybercriminal ecosystem. These platforms had handled over AU$54.6 billion in illegal transactions, facilitated scams, and supposedly supported operations linked to North Korean hackers. With mounting pressure from international regulators and escalating public scrutiny, technology companies are intensifying their enforcement against illicit activities on their platforms. Nonetheless, the battle against cybercrime is ongoing, and ongoing vigilance will be crucial to safeguarding users and financial systems around the world.

Q: What were Xinbi Guarantee and Huione Guarantee?

A:

These were Chinese-language black market services operating on Telegram. They acted as escrow services for cybercriminals, providing money laundering, stolen data trading, and various illicit fintech services.

Q: Why did Telegram dismantle these platforms?

A:

Telegram pointed to violations of its service terms, especially regarding criminal activities such as scams and money laundering. The platforms were taken down upon discovery.

Q: How much money flowed through these markets?

A:

Blockchain analytics firm Elliptic estimated that Xinbi and Huione processed over US$35 billion (AU$54.6 billion) in illegal transactions since 2021.

Q: What is the Huione Group?

A:

Huione Group is a conglomerate based in Cambodia behind Huione Guarantee. It also oversees Huione Pay and Huione Crypto and has been linked to the North Korean Lazarus hacking group, resulting in U.S. sanctions.

Q: What are the repercussions for Australia?

A:

Australians are common targets for online scams. Disrupting these global black markets may lessen financial losses and shield consumers from fraud originating from overseas.

Q: Is this the end of such black markets on Telegram?

A:

Not necessarily. While this disruption is substantial, cybercriminals can regroup and identify alternative platforms. Continuous oversight and enforcement are critical.

Q: How can users safeguard against online scams?

A:

Australians should stay updated on scam strategies, employ two-factor authentication, avoid dubious links, and report any fraudulent actions to Scamwatch or the Australian Cyber Security Centre (ACSC).

Q: What role do messaging platforms play in cybercrime?

A:

Messaging services like Telegram can be exploited by criminals for secure communication, trading illegal goods, and managing scams. However, with proactive moderation and enforcement, platforms can also contribute to the solution.

“Wireless Earbuds Bluetooth 5.3 Headphones Review”


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Wireless Earbuds Bluetooth 5.3 Headphones with 4 Mic HiFi Stereo Sound, Wireless Headphones with Dual LED Display Touch Control, 40H Playtime Bluetooth Earphones IP7 Waterproof, Purple

Tyro Payments Seeks New Chief Information Security Officer


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Tyro Payments is in the process of hiring a new Chief Information Security Officer (CISO) after Manasseh Paradesi’s exit.
  • The incoming CISO will answer to Chief Risk Officer Steven Chapman and will manage the company’s comprehensive cybersecurity initiatives.
  • Main duties involve ensuring adherence to Australian regulatory requirements and protecting confidential data and systems.
  • Paradesi has resigned after a two-year period, previously holding positions at Omniscient Neurotechnology, AGL, Cover-More Group, and GE Energy Connections.
  • This decision comes as the regulatory and cyber threat environment in Australia’s fintech industry intensifies.
Tyro Payments is searching for a new Chief Information Security Officer

Leadership Shift at Tyro Payments

Listed on the ASX, Tyro Payments is actively searching for a new Chief Information Security Officer (CISO) following the announcement of Manasseh Paradesi’s resignation. The organization has already begun its recruitment effort to find an appropriate successor.

The new CISO will report to Chief Risk Officer Steven Chapman and will be responsible for overseeing Tyro’s information security infrastructure. This includes putting key cybersecurity protocols in place to secure customer information, financial systems, and stakeholder confidence.

Significance of This Change

As cyberattacks on financial sectors grow more sophisticated, the importance of a CISO is greater than ever. For Tyro Payments, which caters to over 68,000 Australian businesses with EFTPOS and banking solutions, upholding strong cybersecurity measures is essential.

Recent statistics from the Australian Cyber Security Centre (ACSC) indicate that the financial industry continues to be one of the most targeted sectors for cybercrime. The average financial impact of a cyberattack on medium-sized businesses in Australia has escalated to over $88,000 per incident.

This leadership shift arrives amid increasing regulatory oversight. Financial entities are required to comply with standards such as APRA CPS 234, which demands strict compliance with information security governance and incident response strategies.

New CISO Responsibilities

As detailed in the LinkedIn job post, the new CISO at Tyro will be accountable for:

  • Creating and implementing a unified information security plan.
  • Ensuring adherence to both local and international regulatory demands.
  • Overseeing the integration of advanced cybersecurity solutions.
  • Working with internal teams to carry out risk evaluations and audits.
  • Managing security incidents and breaches effectively.

The position will also require leading a team of cybersecurity experts and collaborating with Tyro’s executive leadership to foster a security-centric culture.

Overview of Manasseh Paradesi’s Tenure and Experience

Manasseh Paradesi joined Tyro Payments in 2021, bringing a wealth of knowledge from the cybersecurity and risk management fields. Before his time at Tyro, he was the CISO at Omniscient Neurotechnology, a medical device company utilizing AI to map brain function.

Paradesi’s previous roles include senior security positions at prominent organizations like Cover-More Group, energy company AGL, and GE Energy Connections. His departure marks the beginning of a new era for Tyro as it aims to align its security strategy with ongoing threats and business goals.

Cybersecurity Challenges in Australia’s Fintech Sector

The fintech landscape in Australia is rapidly expanding, bringing with it increased exposure to cyber dangers. From ransomware incidents to phishing attacks, companies like Tyro must constantly fend off threats that can compromise customer confidence and financial security.

As reported by TechBest, Australian fintechs are investing significantly in cybersecurity, with over 70% planning to boost their security budgets in 2026. Appointing a strong, forward-thinking CISO is not only a regulatory requirement but also a competitive edge.

Conclusion

Tyro Payments is experiencing a pivotal leadership transition as it searches for a new Chief Information Security Officer to navigate the increasingly intricate cybersecurity terrain. With the departure of Manasseh Paradesi, the new CISO will play a crucial role in protecting the firm’s digital infrastructure, ensuring regulatory compliance, and maintaining customer trust in one of Australia’s leading fintech companies. This recruitment process unfolds amid escalating threats and growing regulatory responsibilities.

Q: Why is Tyro Payments in need of a new CISO?

A:

Tyro Payments is looking for a new CISO to take over from Manasseh Paradesi, who is leaving after over two years in the position. The firm wishes to enhance its cybersecurity and compliance framework in light of increasing threats and regulatory demands.

Q: What responsibilities will the new CISO at Tyro hold?

A:

The new CISO will supervise Tyro’s complete information security framework, incorporating policy formulation, risk management, incident response, and adherence to regulations like APRA CPS 234.

Q: Who will the new CISO report to at Tyro?

A:

The CISO will report directly to Tyro’s Chief Risk Officer, Steven Chapman, underscoring the strategic importance of this role within the organization.

Q: What are the major cybersecurity risks faced by Tyro and other fintechs in Australia?

A:

Fintech companies like Tyro contend with risks such as ransomware, data breaches, phishing, and supply chain attacks. The ACSC notes a rise in incidents targeting financial entities, highlighting the urgent need for robust security strategies.

Q: What background did Manasseh Paradesi contribute to Tyro?

A:

Paradesi contributed significant experience from his prior roles at Omniscient Neurotechnology, Cover-More Group, AGL, and GE Energy Connections. His expertise covers both private sector and essential infrastructure cybersecurity.

Q: How will this transition impact Tyro’s clientele?

A:

The transition is anticipated to proceed smoothly, with Tyro reaffirming its dedication to providing secure and dependable financial services. The company is actively seeking a successor to maintain its cybersecurity standards.

Q: Where can potential candidates apply for the CISO position?

A:

Qualified candidates can apply for the role through LinkedIn or Tyro’s careers site. The job listing is publicly available and details the required qualifications and responsibilities.

Soundcore Space A40 Earbuds Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

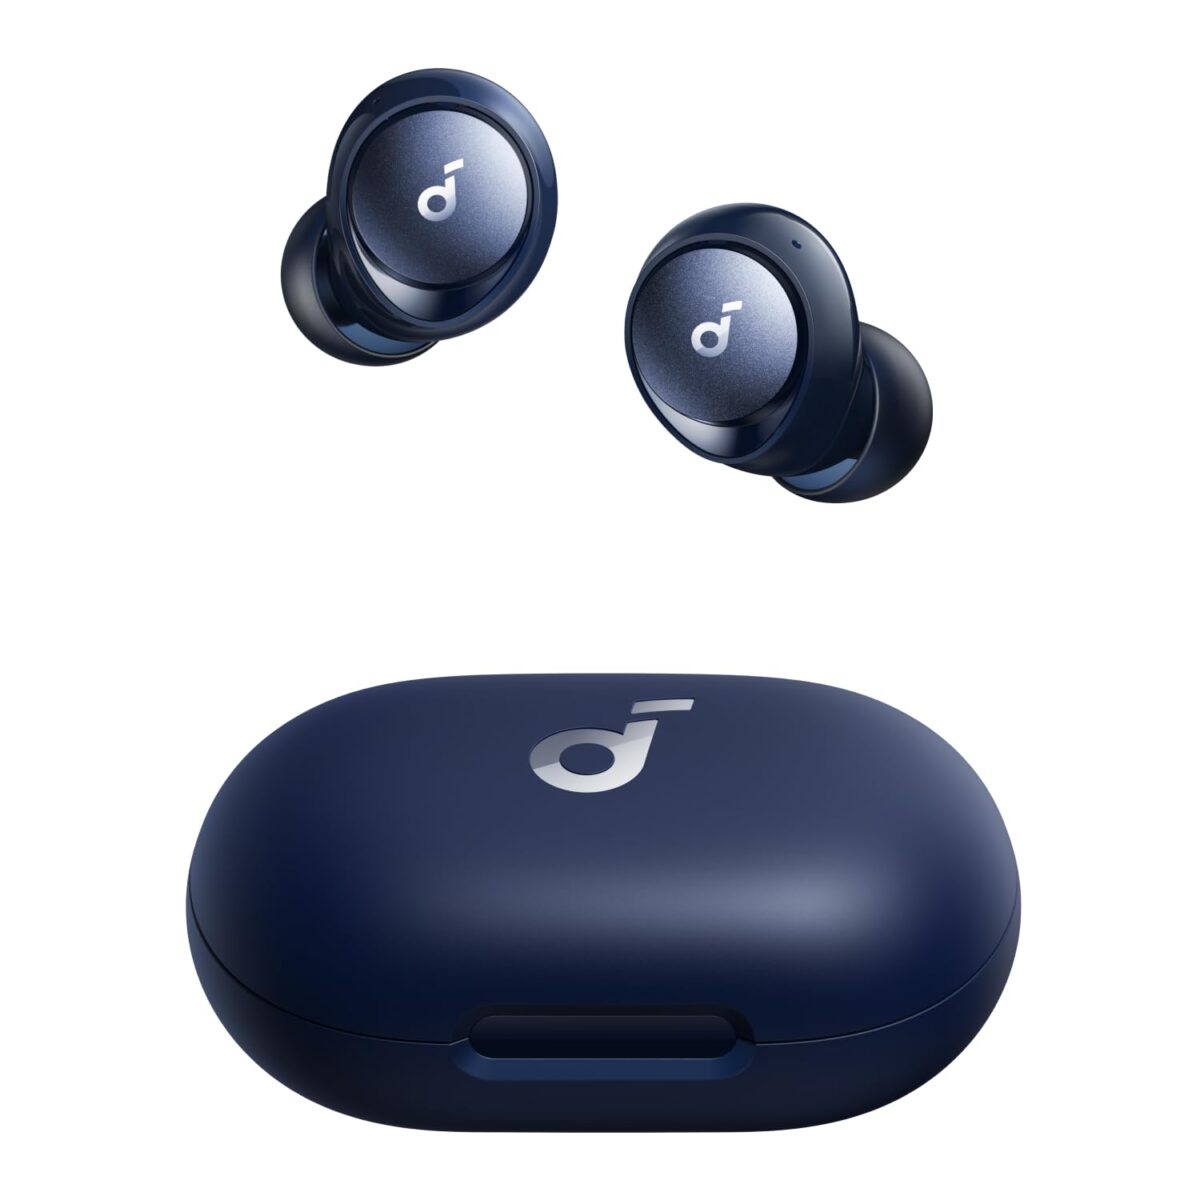
soundcore by Anker Space A40 Adaptive Active Noise Cancelling Wireless Earbuds, Reduce Noise by Up to 98%, Ultra Long 50H Playtime, 10H Single Playtime, Hi-Res Sound, Comfortable Fit, Wireless Charge

Safeguarding Your Information in the Era of AI: Essential Insights for Every Aussie


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • In 2026, 95% of companies experienced difficulties when implementing AI, largely due to issues related to data preparedness and concerns surrounding security.
  • Australia and New Zealand are enhancing their privacy legislation, which includes tougher breach reporting requirements and increased penalties.
  • Data breaches are escalating in ANZ, with 527 incidents documented in the first half of 2026 alone.
  • Effective Data Security Posture Management (DSPM) is vital for protecting against cyber threats in AI-enabled environments.
  • Automation and data governance are critical for scaling security measures and boosting operational productivity.
  • New AI-driven positions and policies are emerging to address changing threats and ensure compliance.
Data Protection Strategies in the Era of AI for Australians

The Essential Connection Between Data Security and Information Management

With the rapid increase in AI integration across sectors, organisations are becoming more reliant on systems governed by data. Nonetheless, initiatives can struggle without robust data management practices in place. According to Forrester, companies in the Asia Pacific with strong information management strategies are 1.5 times more inclined to succeed in AI endeavors.

This aspect is especially significant in Australia and New Zealand, where regulators are intensifying their scrutiny of data privacy infringements. The Office of the Australian Information Commissioner (OAIC) alongside the Australian Cyber Security Centre (ACSC) revealed 527 data breaches in only the first six months of 2026, marking the highest figure in over three years. Malicious attacks comprised 67% of these occurrences, illustrating that cybercriminals are capitalizing on trends in digital transformation.

Privacy Law Amendments in Australia

  • Penalties for significant privacy violations can now go up to 10% of yearly revenue.
  • Definitions of personal data now encompass technical identifiers such as IP addresses.
  • Consent protocols have become stricter, requiring explicit approval from users in a timely manner.
  • Individuals are granted broader rights to access, amend, and erase their personal data.
  • Notification of breaches is mandatory within stricter deadlines.
  • ‘Privacy by design’ is now a requisite from the inception of all systems and processes.

New Zealand’s Strengthened Privacy Regulations

  • Tighter international data transfer regulations are now instituted.
  • The Privacy Commissioner has been endowed with extended powers.
  • Formal risk assessments are required for high-risk data processing activities.
  • Organisations are obliged to keep meticulous records pertaining to data management.

In light of these updates, organisations in ANZ are reassessing their data strategies to assure compliance with regulations and lessen vulnerability to cyber threats.

Managing Data Sensitivity in AI Frameworks

AI technologies depend on data, yet risks significantly increase when that data contains personal, medical, or proprietary information. The 2026 data breach at MediSecure, affecting nearly 50% of Australia’s populace, emphasizes the severe repercussions that inadequate data security can lead to, particularly within sectors like healthcare where continuity of service is crucial.

To alleviate these dangers, organisations should implement Data Security Posture Management (DSPM) to:

  • Recognize and categorize sensitive data throughout all environments.
  • Employ controls commensurate with data sensitivity levels.
  • Track usage patterns and identify unusual behaviors.
  • Ensure adherence to privacy statutes.
  • Automate responses to threats related to data security.

New Security Positions and Continuous Engagement

The emergence of AI has given rise to new security roles dedicated to AI-specific risks. These specialists assess vulnerabilities in AI frameworks, establish customized security measures, and coordinate responses to incidents.

Organisations are also fostering an environment of ongoing discussions about security, where risk tolerance levels are established, resources are reallocated as necessary, and compliance efforts are consistently evaluated. This thoughtful strategy guarantees that AI adoption corresponds with both business and security objectives.

Automating Data Security for Enhanced Scalability and Effectiveness

Traditional methods of data protection are unable to keep pace with the scale and intricacy of contemporary data. Automation has shifted from being optional to essential.

According to reports from Cybersecurity Ventures, there has been a 35% increase in the adoption of sophisticated threat detection tools, while Gartner projects that by 2026, 70% of enterprises will have integrated AI-driven threat intelligence systems.

Key automated capabilities encompass:

  • Risk evaluations to oversee access and permissions.
  • Heatmaps that pinpoint high-risk areas for data exposure.
  • Instant alerts designed to thwart and address threats.

These technologies enable security teams to focus on strategic initiatives, enhancing efficiency while boosting resilience against threats.

Boosting Data Security Through Quality Management and Governance

AI systems depend on superior data quality to generate precise insights. Poor data quality can not only detract from results but also elevate security risks. Gartner estimates that subpar data may cost companies about A$21 million yearly.

To maintain both data quality and security, organisations should:

  • Utilize automated solutions to identify outdated or inconsequential content.
  • Establish robust data governance frameworks.
  • Create metadata systems for enhanced data tracking.
  • Develop policies for the lifecycle management of outdated data, such as archiving or deletion.

When implemented alongside AI systems, these governance strategies minimize potential attack vectors and assure adherence to developing regulations.

A Holistic Strategy for AI Data Security

As AI becomes increasingly ingrained within business functions, the associated data security risks are bound to escalate. A comprehensive strategy—addressing data governance, risk management, and automation—is pivotal for achieving success.

Entities that invest in proactive data security measures not only adhere to compliance standards but also secure a competitive advantage in responsibly and effectively implementing AI.

Learn how recommended solutions such as AvePoint’s AI Security and Confidence platform can aid your organisation in protecting sensitive data while unlocking the full potential of AI.

For additional information, visit AvePoint’s AI Security and Confidence Solutions.

Modern Data Protection Practices for Australians in AI Contexts

Conclusion

The safeguarding of data in the age of artificial intelligence is a pressing issue for organisations in Australia and New Zealand. With stricter privacy regulations and increasingly sophisticated cyber threats, businesses are compelled to adopt a proactive and strategic framework to protect their information resources. This includes establishing DSPM, automating threat identification, and enhancing data governance. Such initiatives ensure that organisations remain compliant, resilient, and prepared to safely leverage AI technology.

Q: Why does AI elevate data security risks?

A:

AI systems necessitate large volumes of data, much of which is sensitive. This makes them prime targets for cybercriminals. Furthermore, attackers can leverage AI tools to identify and exploit vulnerabilities at a pace that outstrips traditional techniques.

Q: What constitutes Data Security Posture Management (DSPM)?

A:

DSPM represents a proactive methodology for protecting and managing sensitive data. It entails locating where data is held, classifying its sensitivity, implementing security protocols, supervising access, and automating responses to threats.

Q: How are Australia and New Zealand revising their privacy regulations?

A:

Both