Matthew Miller, Author at Techbest - Top Tech Reviews In Australia - Page 12 of 187

USDA Introduces Satellite and AI Program to Improve Crop Prediction


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!
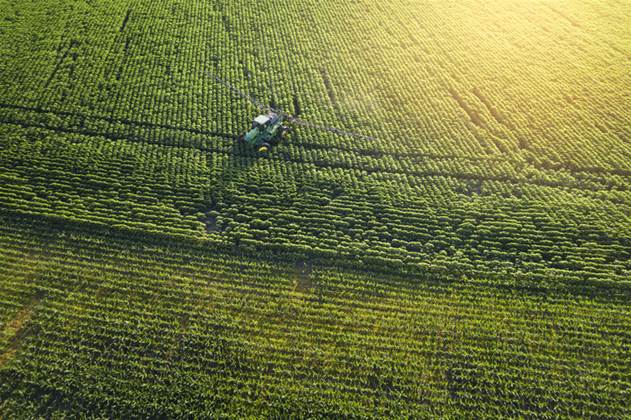
USDA Satellite and AI Project to Improve Crop Forecasting

Quick Overview

  • USDA initiates a pilot program aimed at improving crop forecasting through satellite imagery and AI.
  • The project seeks to tackle criticisms related to the dependability of agricultural data.
  • Partnership with NASA and federal organizations to enhance reporting precision.
  • Initiatives include the use of geospatial tools, crop modeling, and farmer surveys.
  • USDA committed to increasing transparency regarding methodologies and data limitations.
  • Farmers voice concerns over the trustworthiness of data and recent policy shifts.
  • Political repercussions as the Iowa Senate race heats up.

USDA Initiates Satellite and AI Project
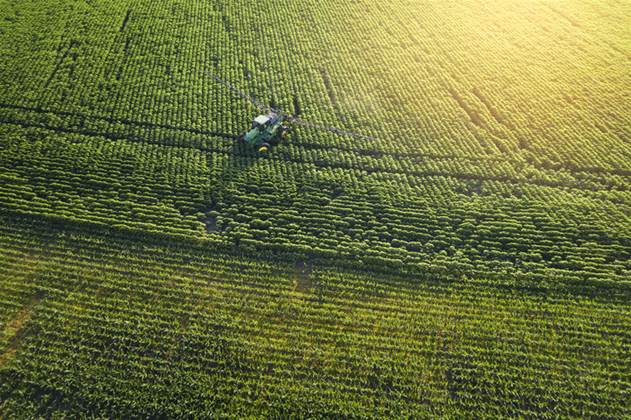
USDA to evaluate satellites and AI to enhance crop predictions

The United States Department of Agriculture (USDA) is launching a pilot program to refine its crop acreage and yield assessments by utilizing cutting-edge technology. The initiative, proposed by Secretary Brooke Rollins, aims to confront critiques regarding the dependability of government agricultural statistics.

Innovations in Agriculture

Announced at the Farm Progress Show in Boone, Iowa, the USDA’s data modernization initiative involves cooperation with NASA and other federal entities to leverage enhanced satellite imagery. This endeavor will use geospatial tools, crop models, and farmer surveys for more precise estimation of crop acreage and yield. Moreover, artificial intelligence and machine learning are set to significantly contribute to improving data collection methodologies.

Tackling Data Reliability Challenges

The USDA’s initiative emerges in response to feedback from farmers, grain traders, and economists regarding the trustworthiness of its data. These issues were magnified by major staff cuts and inconsistencies between the initial and final figures of planted and harvested corn acres in 2025. The USDA intends to minimize redundant information requests from farmers while enhancing the promptness and precision of its statistics.

Political and Economic Repercussions

The USDA’s initiatives are taking place in a politically charged context in Iowa, where the US Senate race has been designated as a “toss-up” by Cook Political Report. Iowa’s agriculture-centric economy has faced challenges from tariffs and increasing diesel and fertilizer prices, further complicated by geopolitical strife. The USDA’s listening sessions, initiated at Minnesota Farmfest, have made evident farmers’ frustrations regarding data reliability and policy implications for the agricultural economy.

Conclusion

The USDA’s latest initiative to improve crop forecasting via satellite and AI technology signifies a major progress towards updating agricultural data collection practices. By addressing reliability concerns and enhancing transparency, the USDA aims to restore farmers’ confidence and adapt to the changing agricultural landscape.
Q&A Section

Q: What is the main objective of the USDA’s new initiative?

A: The initiative aims to enhance the accuracy of crop forecasting through the use of satellite imagery and AI technology.

Q: How will the USDA improve its data gathering methods?

A: By partnering with NASA, utilizing geospatial tools, crop models, and integrating AI and machine learning.

Q: What criticisms has the USDA encountered regarding its data?

A: Farmers and traders have raised concerns about the reliability of USDA’s agricultural data.

Q: How does this initiative influence political dynamics in Iowa?

A: The initiative aligns with a competitive Senate race, emphasizing the significance of agricultural policies.

Q: Will farmers gain easier access to USDA methodologies?

A: Yes, the USDA intends to furnish farmers with more information regarding its methodologies and data limitations.

Q: What effect do listening sessions have on the USDA’s methodology?

A: Listening sessions have surfaced farmers’ grievances and shaped the USDA’s data modernization initiatives.

Telstra’s 2020 Choices Result in Significant Mobile Disruption Six Years On


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Read

  • Decisions made by Telstra in 2020 resulted in a significant mobile outage in 2026.
  • A technical assessment disclosed deficiencies in the maintenance of network timing equipment.
  • Telstra could face fines in the range of tens of millions.
  • A complicated series of errors involved financial limitations and inadequate documentation.
  • Brady admitted to the shortcomings and committed to adding more resources and expert advice.

The Technical Audit Reveals Deficiencies

Telstra's 2020 decisions led to a 2026 mobile outage.

On July 8, 2026, Telstra’s mobile network suffered a nationwide failure that heavily impacted services, including the triple zero emergency contact line. An assessment conducted by Technology Audit Partners (TAP) revealed that the issues originated from decisions made back in 2020. While initially reliable and suitable, cuts to costs and neglected maintenance transformed the network timing apparatus into a potential disaster.

Tracing the Sequence of Events

In 2020, Telstra initiated essential alterations to its primary timing setup, aiming to renovate an outdated server chassis. However, this upgrade included limitations that prohibited stratum-2 and stratum-3 servers from being housed together in the same chassis. Consequently, this resulted in dependence on external servers, causing instability in time sources.

Ignored Indicators and Alerts

Signs of distress began to emerge shortly thereafter. The Melbourne time server operated by Telstra demonstrated looping behaviors upon failing to connect to the Sydney server. Although the issue was recognized, it was not thoroughly investigated, resulting in the installation of a GPS card as a temporary fix. Unfortunately, the card was not updated for an existing GPS defect, which ultimately led to the outage.

The Outage and Its Repercussions

On July 8, a malfunction in the power supply necessitated the replacement of the chassis in Melbourne. This triggered the reset issue with the GPS card, consequently making other servers adopt incorrect dates and resulting in widespread network failures. This incident underscored significant oversight and documentation shortcomings.

Dealing with the Aftermath

Vicki Brady, the CEO of Telstra, accepted accountability, recognizing the failures while dismissing accusations of a flawed design. The telco has since implemented more alarms, enhanced monitoring procedures, and invested in additional resources and external expertise for its engineering divisions.

Conclusion

The 2026 outage experienced by Telstra was a result of ignored risks, deficient documentation, and financial constraints dating back to 2020. This incident highlights the necessity for strong maintenance and documentation protocols, particularly within essential network infrastructures. Looking ahead, Telstra is focused on fortifying its systems through better monitoring and expert contributions.

Q: What caused the Telstra outage in 2026?

A: The outage was a result of a series of errors starting in 2020, including inadequate documentation, financial limitations, and failure to update crucial timing systems.

Q: How did Telstra’s decisions in 2020 affect the network?

A: The modifications made in 2020 imposed operational restrictions and uncertainties concerning time sources, which went unaddressed until resulting in a significant outage.

Q: What steps is Telstra taking to avert future outages?

A: Telstra is upgrading its monitoring systems, refining documentation practices, and bringing in additional resources and outside expertise to enhance its network setup.

Q: Were there any indicators prior to the outage?

A: Indeed, there were warning signs such as looping behaviors and alerts, but they were not adequately investigated or acted upon, leading to the eventual failure.

Q: What impact did budgetary limitations have on this situation?

A: Financial constraints were highlighted as a factor shaping decision-making processes, influencing the prioritization of essential network operations and upkeep.

Q: How is Telstra addressing the staffing and expertise challenges identified in the audit?

A: Telstra intends to evaluate staffing within its engineering division and allocate additional resources to ensure comprehensive control of network capabilities.

Sonos MCP Server Incorporates ChatGPT, Gemini, Grok for Music Management; Launches Beam Ultra Soundbar and Ace Ultra Headphones


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • Sonos launches the Sonos 27 operating system featuring open AI integration.
  • The new Beam Ultra soundbar supports 7.1.2 Dolby Atmos and enhanced vocal clarity.
  • Ace Ultra headphones offer adaptive ANC and smooth integration with the Sonos system.
  • Software updates encompass Sonos Fabric and Positioning Technology.
  • Products are set for pre-order on September 2, 2026, with general release on September 29.

Acoustic Features of the Beam Ultra

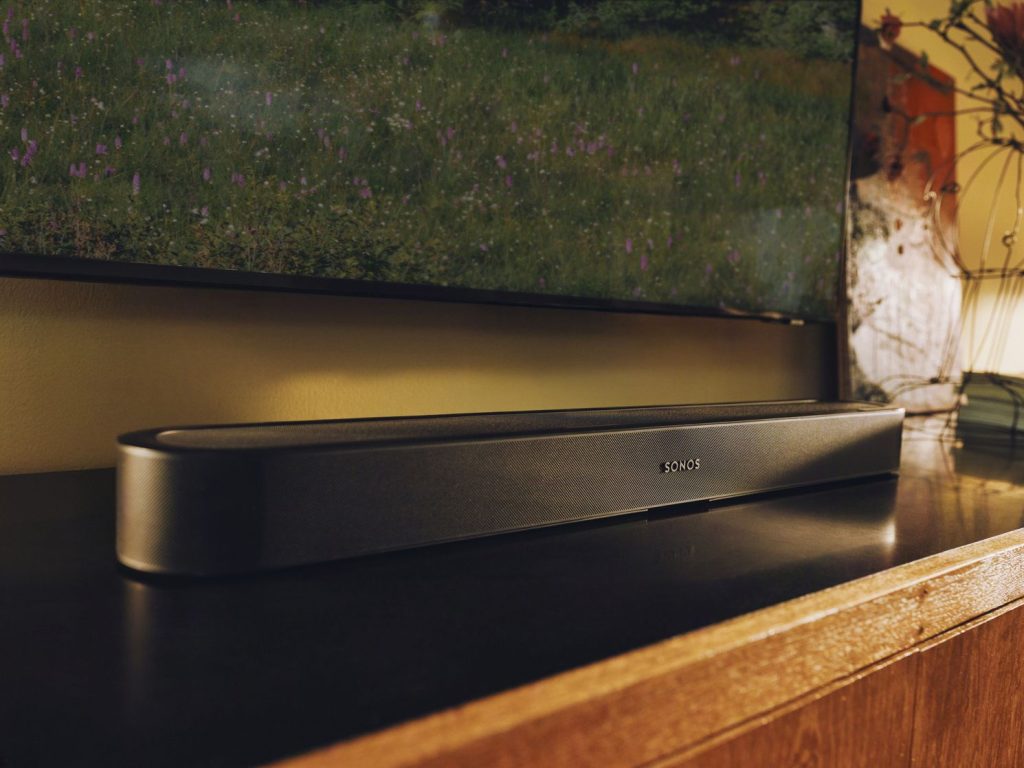
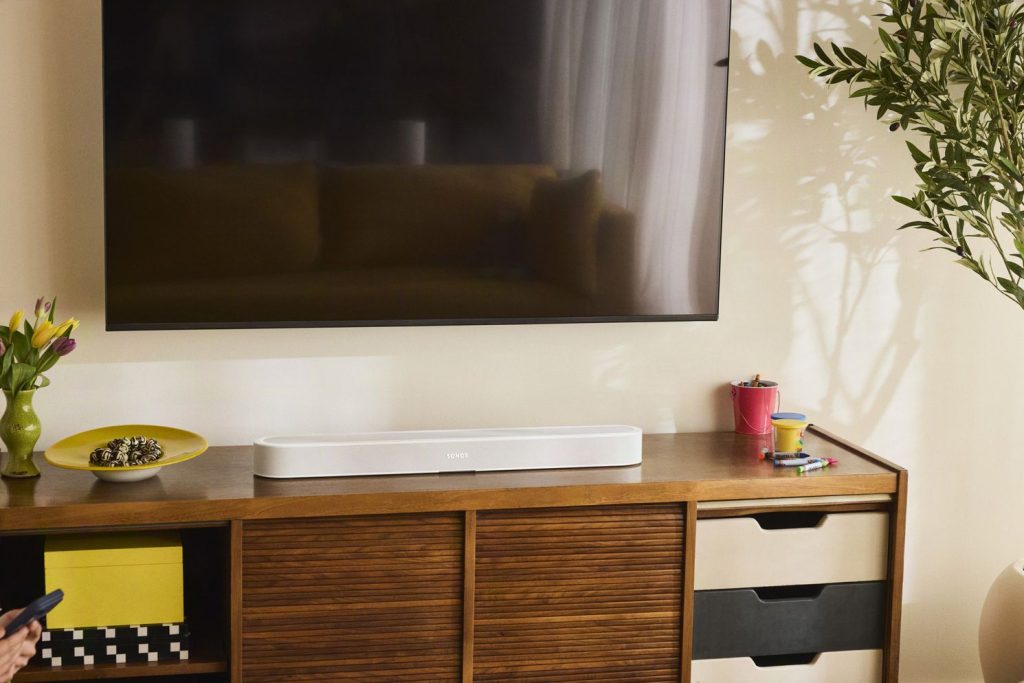
The Sonos Beam Ultra stands out in the latest platform update, delivering authentic 7.1.2 Dolby Atmos in a sleek design. It incorporates nine custom drivers, including two upward-firing ones for immersive audio and bass enhancement. The revamped centre channel enhances vocal clarity, tackling frequent issues of unclear dialogue in home theaters. Equipped with AI Speech Enhancement and Night Sound mode, the Beam Ultra promises an exceptional audio experience at A$1,099, supporting WiFi, Bluetooth, and HDMI eARC connections.

Sonos Beam Ultra Soundbar with advanced audio features

Mobilizing the Ecosystem with Ace Ultra

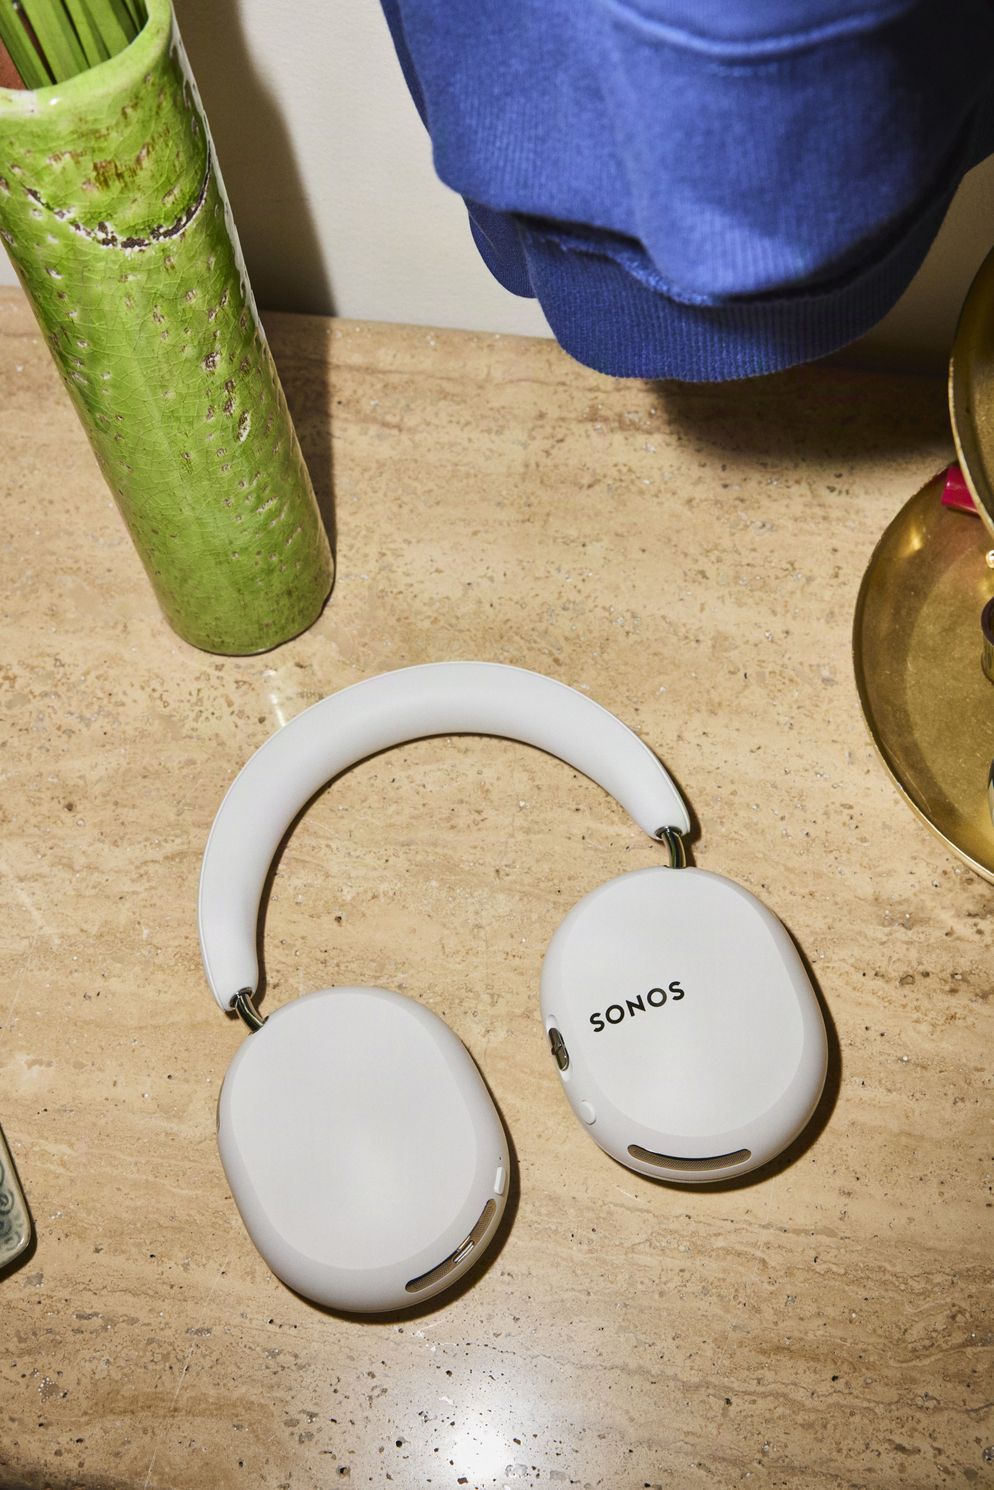
Priced at A$699, the Sonos Ace Ultra headphones are equipped with a custom 40mm driver and adaptive noise cancellation through a 10-microphone array. With a battery life of 35 hours, they are perfect for travel. This model uniquely features the Headphone Engine 2, allowing immediate integration with the Sonos system without the need for a smartphone. This function, debuting in Early Access, transforms personal audio connectivity.

Sonos Ace Ultra Headphones with Adaptive ANC

Sonos 27 and Transition to Open AI

The Sonos 27 OS presents an open platform for AI integration, accommodating external AI agents such as OpenAI’s ChatGPT via the Model Context Protocol (MCP). This feature lets users control audio settings through AI without the Sonos app, enhancing flexibility in smart home setups. Upcoming updates will permit users to create custom AI agents with distinct models and voices.

Sonos 27 OS with Open AI Integration

Dynamic Positioning Solves the Rear Surround Dilemma

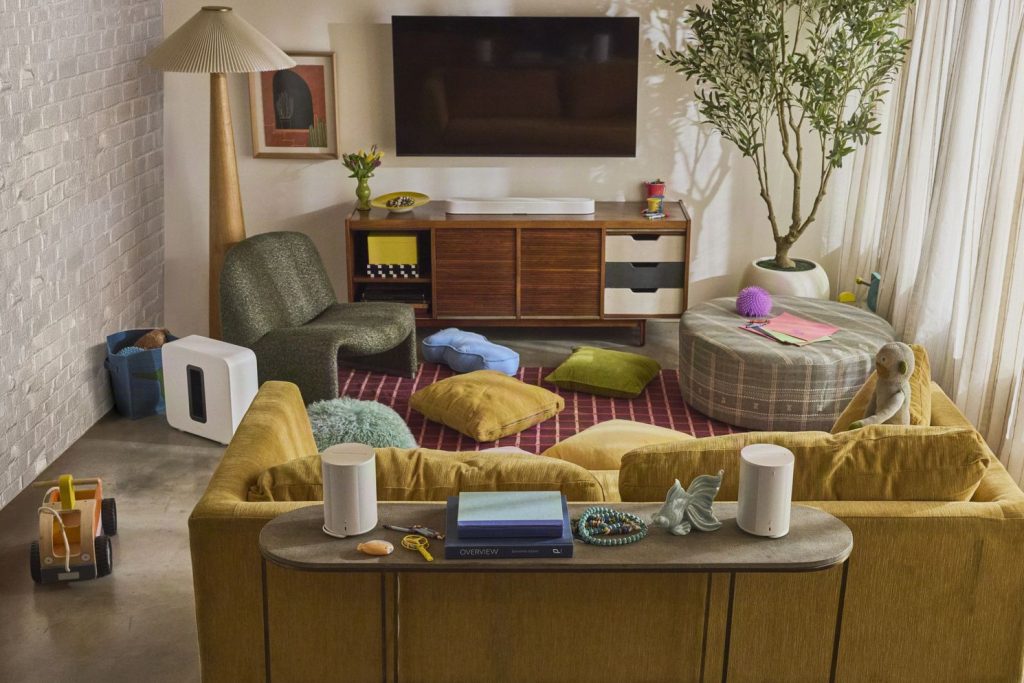
Sonos Fabric and Positioning Technology empowers speakers to adapt their functionalities based on physical arrangement, facilitating temporary rear surround sound configurations. This capability is especially advantageous for renters or individuals seeking tidy audio solutions.

Sonos Dynamic Positioning Technology for Surround Sound

Australian Launch and Rollout Information

The Sonos 27 app, offering community-driven features, will begin rolling out on September 8. The Beam Ultra and Ace Ultra will be available for pre-order starting September 2, 2026, with general availability on September 29. For further information, visit Sonos.

Conclusion

The latest products from Sonos, including the Beam Ultra soundbar and Ace Ultra headphones, utilize the new Sonos 27 operating system to provide unparalleled audio management and integration with open AI platforms. With features such as dynamic speaker positioning and seamless system connectivity, Sonos is establishing a new benchmark in home audio technology.

Q: What key feature does the Sonos Beam Ultra offer?

A: The Sonos Beam Ultra features authentic 7.1.2 Dolby Atmos sound with improved vocal clarity through its redesigned centre channel and AI Speech Enhancement.

Q: In what way do the Ace Ultra headphones integrate with the Sonos system?

A: The Ace Ultra headphones come with Headphone Engine 2, enabling straightforward audio control from the Sonos system without utilizing a smartphone.

Q: What is the importance of the Sonos 27 operating system?

A: The Sonos 27 OS offers an open framework for the incorporation of third-party AI agents, allowing adaptable management of the audio space.

Q: How does Sonos Fabric and Positioning Technology assist users?

A: It enables speakers to dynamically adapt their roles based on their placement, allowing for temporary surround configurations without the need for permanent setups.

Q: When can Australians expect the new Sonos products to launch?

A: The Beam Ultra and Ace Ultra will be available for pre-order from September 2, 2026, with general availability occurring on September 29.

Privacy Act Overhaul to Strengthen 72-Hour Breach Notification Deadline


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Rapid Overview

  • Under new legislation, Australian organisations might soon be required to inform the Information Commissioner of data breaches within a 72-hour timeframe.
  • The limited erasure right will apply solely to major digital platforms that satisfy certain revenue or user criteria.
  • Smart glasses pose privacy risks but are not included in the proposed legislative alterations regarding personal use.
Privacy Act reform: 72-hour breach notification requirement

Proposed 72-Hour Breach Notification Obligation

Under draft legislation introduced by the Attorney-General’s department, Australian organisations are mandated to notify the Information Commissioner of an eligible data breach within 72 hours. The Privacy Amendment (Personal Data Protection) Bill 2026 intends to replace the existing “as soon as practicable” criterion with a definitive deadline. This corresponds with current cyber regulation timelines outlined in the Security of Critical Infrastructure Act 2018 and the Cyber Security Act 2024.

Retention of the Two-Stage Breach Evaluation

The proposed bill keeps the current 30-day period for evaluating suspected breaches. Once there are reasonable grounds for suspecting a breach, the 72-hour notification countdown starts. Organisations may file an incomplete report with a rationale if a complete statement cannot be presented within the specified timeframe. Not reporting may result in infringement or compliance notices.

Introduction of a Restricted Erasure Right

The proposed legislation brings forth a restricted erasure right that applies exclusively to large digital platforms as outlined by the Online Safety Act 2021. To qualify, platforms must achieve a gross revenue of $500m or have 2.5 million Australian users monthly. They are required to remove personal information upon request unless certain exceptions are applicable.

Smart Glasses and Privacy Issues

Although the proposed legislation recognizes the privacy risks linked with smart glasses, it does not intend to prohibit them for personal use. The Privacy Act does not apply to individuals using these devices for personal purposes. When regulated entities gather data via wearables, compliance with privacy laws is necessary, which includes acquiring consent for sensitive data collection.

Conclusion

The suggested amendments to the Privacy Act seek to bolster data breach reporting obligations, introduce a restricted erasure right for major digital platforms, and address privacy concerns associated with smart glasses without enforcing additional restrictions on personal use. These modifications reflect continual efforts to modernize Australia’s privacy framework in light of technological developments.

Q: What is the updated reporting time for data breaches?

A: The proposed legislation mandates organisations to report eligible data breaches to the Information Commissioner within 72 hours.

Q: Is the new erasure right applicable to all companies?

A: No, the erasure right is limited to large digital platforms that meet specific revenue or user criteria.

Q: Are smart glasses prohibited under the new rules?

A: No, the legislation does not recommend banning smart glasses for personal use, although it acknowledges related privacy issues.

Q: What is the process for the two-stage breach notification?

A: Organisations have a 30-day window to evaluate a suspected breach, followed by 72 hours to notify the Information Commissioner if a breach is verified.

Q: What consequences arise for failing to report a breach within 72 hours?

A: Not reporting within the 72-hour timeframe may lead to an infringement or compliance notice.

Q: What exceptions are in place for the erasure right?

A: Exceptions include law enforcement, legal retention obligations, technical impossibility, trivial requests, and ongoing service requirements.

QCY MeloBuds N70 Review


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

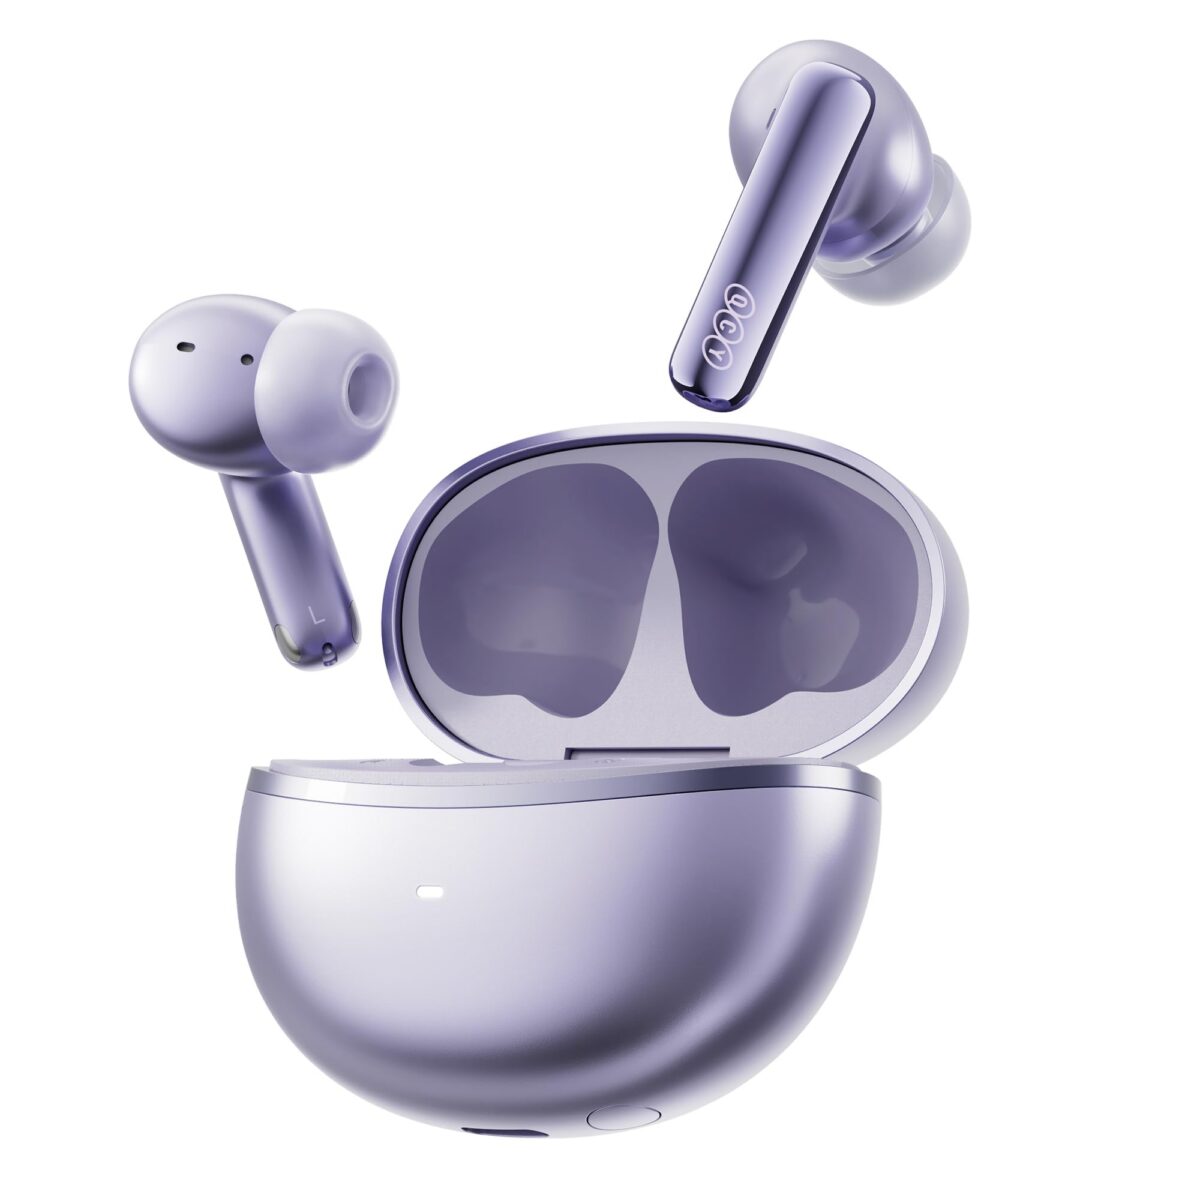
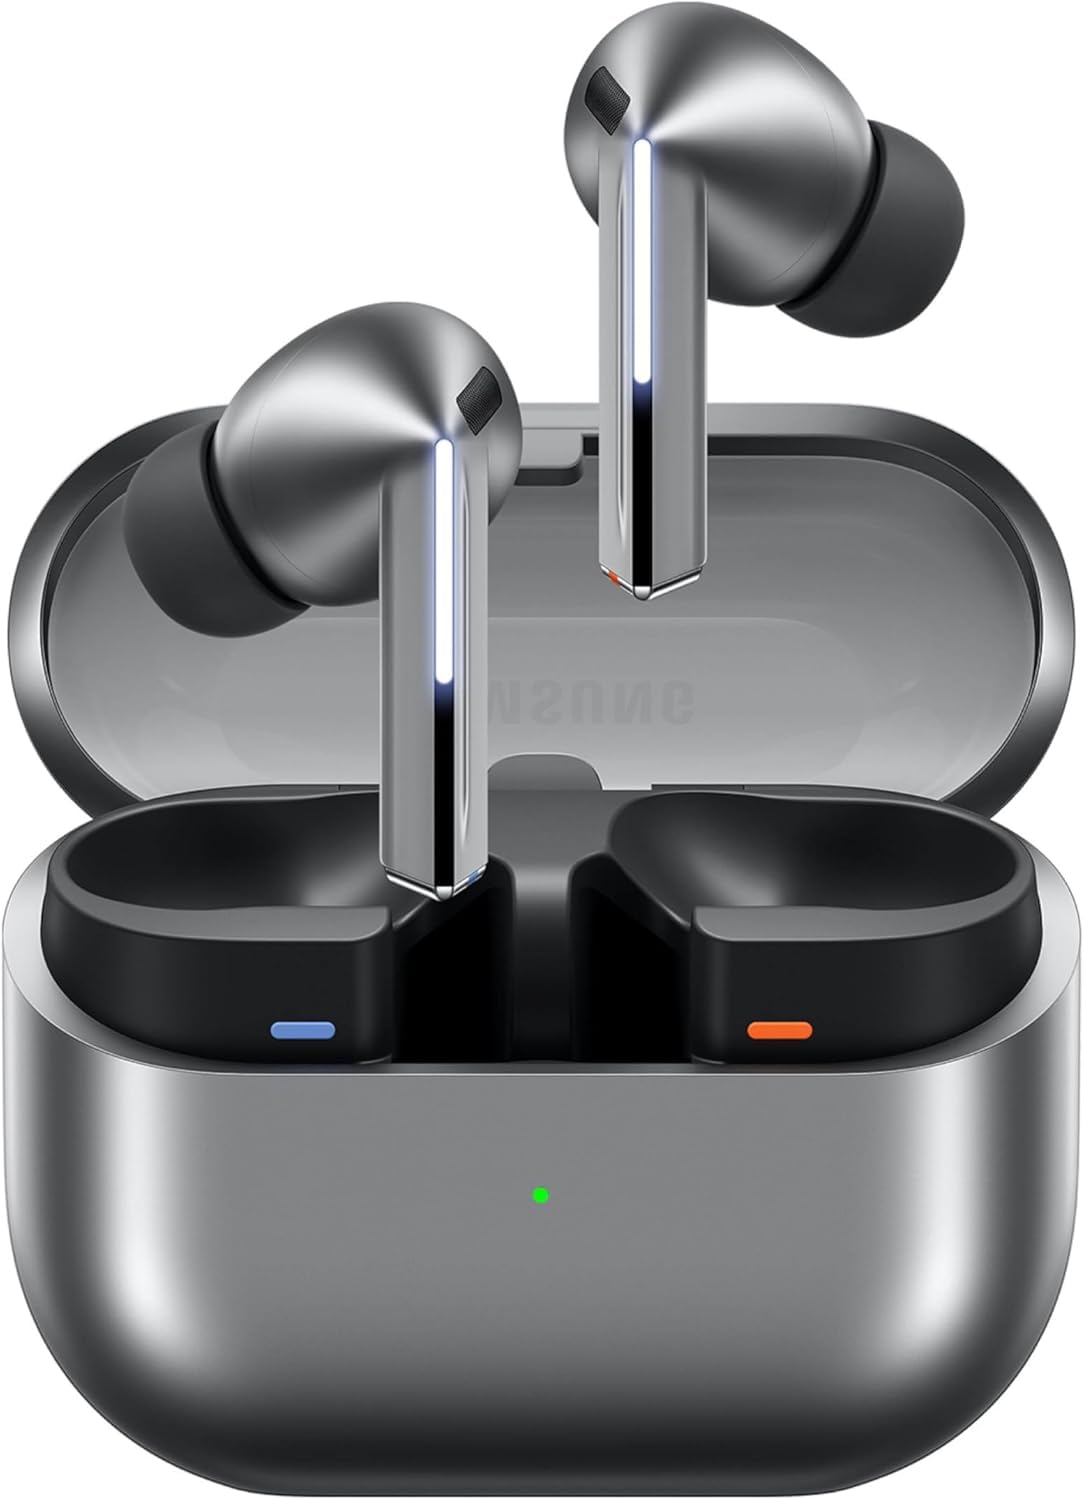
QCY MeloBuds N70 Aadptive Hybrid Active Noise Cancelling Wireless Earbuds, Bluetooth 6.0 with 6 Mics Clear Call, LDAC Hi-Res Audio, 50H Playtime, Wireless Charging, IPX5 Waterproof

Expired Anti-Spam Domain Leads to Email Mayhem at NZ’s Eden Park Stadium


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Eden Park’s email configuration included a lapsed domain, presenting possible email security threats.
  • Consultant Alex Shakhov collected DMARC reports for a year as a result of this configuration error.
  • Reports disclosed Eden Park’s interactions with 600 organizations, such as sponsors and representatives.
  • The stadium asserts that no data breach occurred and has revised its DNS settings.
  • Fujitsu verified that the expired domain was associated with a discontinued anti-spam service.
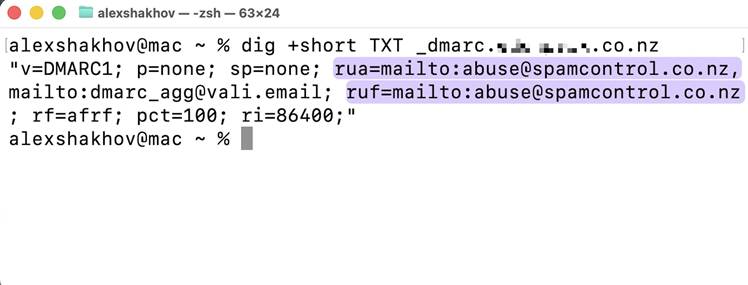
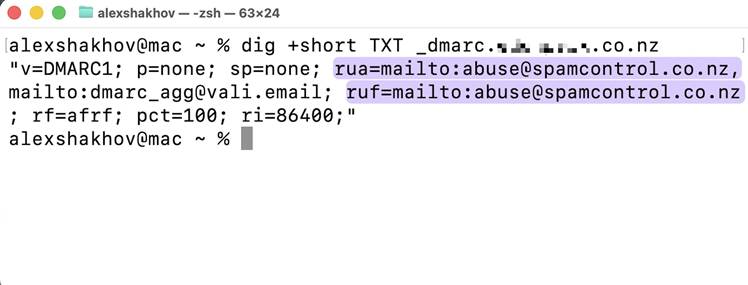
Eden Park Stadium in NZ experiences email security challenges due to lapsed domain

Email Issues at Eden Park

Eden Park, New Zealand’s principal stadium, neglected a vital email configuration flaw for several years. This error involved the inclusion of a lapsed anti-spam domain, enabling the potential interception of sensitive message authentication reports.

Email consultant Alex Shakhov, based in the US, uncovered that the DMARC record in Eden Park’s DNS pointed to spamcontrol.co.nz, a defunct domain. By acquiring this domain, Shakhov was able to receive DMARC reports, providing quick insight into Eden Park’s email system.

Findings from Collected Reports

In just one month, Shakhov analyzed Eden Park’s communication with 600 organizations, including sponsors and event management firms. This exposure had the potential to facilitate targeted phishing attempts if exploited by malicious entities.

Despite multiple efforts to inform Eden Park about the issue, Shakhov’s alerts went ignored for more than a year. His research underscored the considerable security vulnerabilities stemming from the lapsed domain reference.

Response and Reassurances from the Stadium

Eden Park acknowledged the problem and claimed that no data breaches occurred. The stadium has since revised its DNS configuration to remove the expired domain reference. Eden Park reassured that comprehensive cybersecurity measures are in place, actively monitored by their IT team.

However, the stadium did not explain the delay in responding to Shakhov’s warnings.

Understanding DMARC Configuration Errors

DMARC, which stands for domain-based message authentication, reporting, and conformance, aids in safeguarding domains against email spoofing. However, misconfigurations like those at Eden Park can inadvertently expose sensitive information.

DMARC records designate email addresses for receiving reports, but outdated or incorrect configurations may lead to data vulnerabilities. Shakhov’s findings serve as a cautionary example of the necessity for updated and accurate DMARC settings.

Fujitsu’s Involvement and Domain Background

The lapsed domain, spamcontrol.co.nz, was linked to Fujitsu’s operations in Australia and New Zealand. Fujitsu confirmed that it was part of an anti-spam service that was discontinued in June 2021.

Despite this setback, Fujitsu reported no evidence of negative impacts on existing customer systems due to the domain’s discontinuation.

Broader Implications and Research Insights

Shakhov’s evaluations found similar DMARC configuration errors across other organizations. A 2023 study revealed that 26% of domains with external DMARC reporting addresses failed verification checks, highlighting the common occurrence of such security failures.

Shakhov expressed his willingness to return the spamcontrol.co.nz domain to Fujitsu.

Conclusion

The failure to address an expired domain in Eden Park’s email configuration emphasizes the need for regular DNS audits. While there was no data breach, the risk for misuse was considerable, illustrating the necessity for vigilant cybersecurity practices.

Q: What led to the email security problem at Eden Park?

A: The email settings at Eden Park referenced an expired domain, enabling the capture of DMARC reports.

Q: Who identified the configuration error?

A: The error was identified by US-based email consultant Alex Shakhov.

Q: Was there any data breach at Eden Park?

A: Eden Park indicated that no data was compromised despite the oversight.

Q: What steps did Eden Park take post-discovery?

A: Eden Park updated its DNS configuration to remove the lapsed domain reference and assured strong cybersecurity measures are in place.

Q: How was Fujitsu connected to the expired domain?

A: The domain was part of a defunct anti-spam service formerly managed by Fujitsu in Australia and New Zealand.

Q: Are similar DMARC configuration issues prevalent?

A: A study indicated that 26% of domains with external DMARC reporting addresses failed verification, pointing to the commonality of such misconfigurations.

NT Government Begins Path to Digital Driver’s Licence


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Fast Overview

  • The Northern Territory government intends to provide digital driver’s licences by the year’s conclusion, in line with globally acknowledged standards.
  • The Motor Vehicles Amendment (Digital Licences) Bill 2026 establishes the legal basis for Territorians to possess a secure digital licence on their smartphones.
  • Minister Joshua Burgoyne emphasized that these digital licences will authenticate driving privileges, age, and identification in applicable scenarios.
NT government launches digital driver's licence initiative

Digital Licences: Advancing in the Northern Territory

The Northern Territory is poised for a digital shift with the impending release of digital driver’s licences. Expected to be launched by the end of the year, these licences aim to meet internationally accepted standards, offering a contemporary substitute for the conventional physical format.

Legal Structure

The enactment of the Motor Vehicles Amendment (Digital Licences) Bill 2026 sets up the foundation for this initiative, enabling qualified Territorians to have a digital representation of their driver’s licence on their smartphones. This action reflects a wider movement towards digitisation in governmental services.

Advantages of Digital Licences

As stated by Minister for Corporate and Digital Development Joshua Burgoyne, the digital licence will fulfill various roles: confirming an individual’s right to drive, verifying their age as over 18, and establishing identity in specific contexts. This move contributes to a broader initiative for digital government services designed to enhance convenience and security for citizens.

Considerations for Interstate and International Travel

Although the digital licence provides many advantages, the government recommends that Territorians keep their physical driver’s licence on hand when traveling interstate or abroad. This advice stems from the ongoing development of national and global recognition standards for digital licences.

Conclusion

The Northern Territory’s initiative to launch digital driver’s licences represents a pivotal advancement in its digital transformation efforts. By establishing a legal framework that endorses the use of digital licences, the territory is positioning itself as a leader in innovative governmental services.

Q: What are the primary advantages of having a digital driver’s licence?

A: The digital driver’s licence provides convenience, security, and multifunctionality by confirming driving authority, age, and identity in relevant situations.

Q: Is it compulsory to convert to a digital driver’s licence in the Northern Territory?

A: No, choosing to adopt a digital driver’s licence is optional for residents of the territory.

Q: Can the digital licence function without mobile data coverage?

A: Yes, the digital licence will operate even without mobile data coverage.

Q: Should I still retain my physical driver’s licence while traveling?

A: Yes, carrying your physical driver’s licence is advisable when traveling interstate or internationally due to ongoing recognition developments.

Q: What legislation supports the implementation of digital driver’s licences?

A: The Motor Vehicles Amendment (Digital Licences) Bill 2026 provides the legal framework for digital driver’s licences.

REA Group Names First Chief AI Officer


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Read

  • REA Group designates Thyago Liberalli as its inaugural Chief AI Officer.
  • He comes with more than 20 years of expertise in AI and technological transformation.
  • This position is aimed at improving AI functionalities and providing scalable solutions.
  • Liberalli formerly served in senior AI positions at Seek.
  • The role reports directly to REA’s Chief Technology Officer, Steve Maidment.

REA Group’s Bold Step into AI Leadership

REA Group has made a major advancement in its AI strategy by appointing Thyago Liberalli to the newly created Chief AI Officer role. This choice highlights the organization’s dedication to incorporating sophisticated AI capabilities into its processes, with the intention of enhancing experiences for customers and consumers alike.

Thyago Liberalli’s Outstanding Record

Thyago Liberalli joins REA Group with a robust background in AI after a 13-year stint at Seek, where he held key positions such as Asia Pacific Director of AI and Global Director of AI and Machine Learning. His experience spans regions including Australia, Latin America, and Asia-Pacific, rendering him an essential asset to REA’s international aspirations.

The Vision for AI at REA Group

The establishment of the Chief AI Officer role represents a strategic initiative to connect existing AI capabilities with future advancements. Liberalli’s mission is to expedite the transition from AI trials to the formulation of effective, scalable products. This ambition aligns with REA’s extensive AI plan, which emphasizes delivering tangible value for clients and improving operational effectiveness.

Reporting Structure and Strategic Alignment

In his new capacity, Liberalli will report to Steve Maidment, Chief Technology Officer at REA Group. This connection ensures that AI initiatives are closely linked with the company’s broader technological vision, promoting a unified approach to AI-driven evolution.

REA Group names its first Chief AI Officer

Image credit: REA Group/LinkedIn

Summary

Thyago Liberalli’s appointment as Chief AI Officer for REA Group represents a critical advancement in its technological growth. With his skills, the organization is set to utilize AI to generate significant value throughout its operations, aligning with its mission to innovate and excel in the proptech sector.

Q: Who is Thyago Liberalli?

A: Thyago Liberalli is the newly appointed Chief AI Officer at REA Group, boasting over 20 years of experience in AI and technology transformation, previously employed at Seek.

Q: What is the purpose of the Chief AI Officer role at REA Group?

A: The role aims to enhance AI functionalities and advance the development of scalable AI solutions, in line with REA’s overarching AI strategy.

Q: What experience does Thyago Liberalli bring to REA Group?

A: Liberalli has significant experience in AI, having worked as Asia Pacific Director of AI and Global Director of AI and Machine Learning at Seek.

Q: How does this appointment fit into REA Group’s overall strategy?

A: This appointment aligns with REA Group’s strategy to integrate advanced AI capabilities into its processes, aiming to improve customer experiences and operational efficiency.

Q: Who will Thyago Liberalli report to in his new role?

A: Thyago Liberalli will report to Steve Maidment, the Chief Technology Officer at REA Group.

Q: What regions does Thyago Liberalli have experience working in?

A: His expertise covers Australia, Latin America, and the Asia-Pacific region.

Q: What is REA Group’s broader AI agenda?

A: REA Group’s AI agenda concentrates on moving from AI trials to practical applications, providing measurable value to clients and enhancing the company’s proptech ventures.