Australia Tech News - Page 6 of 231 - Techbest - Top Tech Reviews In Australia

Security Specialist Cautions Against Installing Meta’s Muse AI Assistant


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Security specialist Patrick Wardle advises against using Meta’s Muse AI assistant due to a zero-day vulnerability.
  • The issue, termed “not-a-mused”, permits the redirection of dictated audio to an attacker’s domain.
  • Muse AI’s significant access to system resources renders it a prime target for potential threats.
Security researcher cautions against Meta's Muse AI assistant

Security Risks Associated with Meta’s Muse AI Assistant

Renowned macOS security expert, Patrick Wardle, has alerted Mac users regarding Meta’s recently released Muse AI assistant. His warning follows the release of proof-of-concept code for a zero-day vulnerability, which he asserts can easily convert the app into a backdoor for cybercriminals.

Wardle, founder of the Objective-See Foundation and writer of The Art of Mac Malware, revealed the vulnerability, labeled “not-a-mused”, via an X thread and a functioning exploit on GitHub. He pointed out that this vulnerability enables any local process to modify an undocumented setting, endo_voyager_dictation_endpoint, without needing elevated permissions.

Risk Factors of Muse AI

The main danger involves rerouting the audio dictated to Muse to an attacker’s server instead of Meta’s. This redirection can facilitate capturing prompts, introducing harmful commands into the assistant, and stealing authentication data. The exploit only requires the user to click the microphone and dictate as they usually would.

Wardle noted that this proof of concept presumes an attacker can already execute code on the user’s machine. He stressed that Muse AI presents a uniquely attractive target due to its extensive access to system resources, which significantly exceeds the standard scope of malware.

Consequences for Connected Devices

Wardle’s discoveries also apply to devices connected to a compromised Mac using Muse. An attacker could potentially execute commands such as retrieving an iPhone’s location, scanning for nearby Bluetooth devices, and accessing personal data like contacts and calendars. Conversely, using the assistant for messaging would merely result in draft creation rather than covert message sending.

Meta’s Reaction and Security Protocols

Meta has been marketing Muse as a secure personal assistant, with Mark Zuckerberg emphasizing its round-the-clock capabilities. The company asserts that the system employs isolated execution, least-privilege access, and a dedicated security layer known as Sentinel to oversee connector actions and network egress.

Nevertheless, past incidents like the OpenClaw malware, previously referred to as Clawdbot, have raised alarms regarding AI agents having extensive access to user systems.

Conclusion

Patrick Wardle’s alert regarding Meta’s Muse AI assistant underscores critical security vulnerabilities that could be exploited by malicious actors. The zero-day flaw, “not-a-mused”, highlights the dangers associated with AI applications that enjoy extensive access to system resources. While Meta continues to endorse Muse’s security features, users must stay vigilant and aware of potential risks.

Q: What is the primary security issue with Meta’s Muse AI assistant?

A: The main issue is a zero-day vulnerability that enables the redirection of dictated audio to an attacker’s server, potentially turning the app into a backdoor.

Q: How does the “not-a-mused” vulnerability operate?

A: It exploits an undocumented setting that can be changed by any local process without elevated permissions, facilitating audio redirection and possible data breaches.

Q: What makes Muse AI a key target for cybercriminals?

A: Muse AI’s extensive access to system resources, including files, microphone, camera, location, and calendar, makes it a prime target for those seeking wide-ranging access.

Q: Can this vulnerability impact connected devices?

A: Yes, the exploit can reach linked devices, enabling attackers to request actions such as obtaining an iPhone’s location and accessing personal information.

Q: What protective measures has Meta put in place for Muse?

A: Meta claims to implement isolated execution, least-privilege access, and a security layer called Sentinel to manage actions and network egress for Muse.

Q: Are there any significant past incidents related to AI security?

A: Yes, the OpenClaw malware raised concerns regarding AI agents’ broad access to user systems, emphasizing the risks tied to such applications.

Insufficient Data Exchange Undermining EU Cybersecurity Measures


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Brief Overview

  • Efforts for cyber defence in the European Union are hindered by insufficient data exchange among member nations.
  • The EU has allocated €1.4 billion ($2.25 billion) towards enhancing cybersecurity.
  • The deficit in information exchange is referred to as the “Achilles heel” of EU cybersecurity.
  • A major ransomware incident in 2025 went unreported by the impacted countries.
  • National security regulations are obstructing cross-border information exchange.
  • No significant cybersecurity event has been documented since 2016.
  • France, Ireland, the Netherlands, and Spain are facing legal measures due to non-adherence to EU information-sharing regulations.

EU’s Cybersecurity Funding and Obstacles

The European Union is making substantial investments in its cybersecurity framework, with a current budget of €1.4 billion aimed at bolstering its cyber defences. Nevertheless, a report from the European Court of Auditors indicates that these initiatives are being weakened by a pronounced lack of information sharing among the member states.

The Critical Weakness: Insufficient Information Exchange

The report points out that poor data sharing is the “Achilles heel” of the EU’s cybersecurity framework. A prompt and actionable flow of information is essential for an effective response to cyber threats, which is currently lacking. This shortcoming diminishes the overall effectiveness of the EU’s cybersecurity systems and protocols.

Unreported Cyber Events

In September 2025, a ransomware attack struck a technology provider servicing the aviation sector, disrupting major airports throughout Europe, such as those in London, Brussels, Berlin, and Dublin. Alarmingly, none of the impacted nations informed the EU cybersecurity agency or other member states, showcasing the gaping hole in information exchange.

Obstacles to Information Exchange

Legislation pertaining to national security in individual nations is identified as a major hindrance to effective cross-border information sharing. This legal backdrop frequently obstructs the necessary communication between countries when incidents arise.

Legal Proceedings and Non-compliance

In spite of EU regulations demanding information sharing, no EU country has reported a “large-scale” cybersecurity event since 2016. The European Commission has recently referred France, Ireland, the Netherlands, and Spain to the EU Court of Justice for not aligning their national legislation with EU directives regarding cybersecurity information sharing.

Conclusion

The European Union’s commitment to cybersecurity is laudable, yet ineffective information exchange among member states undermines its cyber defences. The absence of timely and actionable information jeopardizes the EU’s capacity to address cyber threats, presenting a significant danger to its collective security.

Q: Why is exchanging information essential for EU cybersecurity?

A: Information exchange is crucial as it enables timely reactions to cyber challenges, thereby improving the overall efficiency of cybersecurity strategies.

Q: What are the repercussions of failing to share information about cyber events?

A: The lack of information sharing can result in disjointed responses, heightened vulnerability, and extended recovery from cyber issues.

Q: In what way are national security laws impacting information sharing?

A: National security laws frequently limit the flow of information across borders, obstructing collaborative efforts to counter cyber threats.

Q: What measures is the EU implementing against non-compliant member nations?

A: The EU has initiated legal actions against states that have not modified their legislation to align with EU directives on cybersecurity information sharing.

Q: Have there been any enhancements in EU cybersecurity measures?

A: Although significant investments and some improvement in cooperation have been made, the lack of information sharing continues to be a pressing concern.

Q: What was the consequence of the ransomware incident in 2025?

A: The incident caused disruptions at major European airports, underlining the repercussions of insufficient information sharing.

Suncorp Group Incorporates AI to Improve Risk Management


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Suncorp Group Utilizes AI for Superior Risk Management

Brief Overview

  • Suncorp Group is adopting AI within its risk management frameworks.
  • AI improves data acquisition for operational issues.
  • AI facilitates the interpretation of intricate risk policies.
  • Proof-of-concepts (POCs) showcase AI’s capability to enhance processes.
  • AI supports both specialists and novices in submitting incidents.
  • AI-driven chatbots efficiently answer policy-related questions.

Overview

Suncorp Group is leveraging artificial intelligence (AI) to strengthen its risk management functions. The major Australian insurance player aims to transform data acquisition methods and improve the accessibility of vital risk policies through AI-powered initiatives.

Suncorp Group advances risk management with AI implementation

Cutting-Edge Application of AI in Risk Systems

At a gathering organized by IBM during Gartner’s IT Symposium/Xpo, Jonathon Rutter, Suncorp’s Executive Manager of Programs and Systems, emphasized the company’s strategic direction toward AI. By executing proof-of-concepts (POCs), Suncorp has successfully validated AI’s ability to optimize risk-related operations.

Enhancing Data Acquisition

A key use of AI lies in refining the incident lodgement process. AI technologies are employed to guarantee thorough and precise data capture, essential for effective incident management. Whether it be a risk professional or a frontline employee registering an incident, AI assists in gathering the necessary details and streamlines the process.

Simplifying Policy Navigation

AI significantly contributes to making complex risk documents more accessible. These policies are crucial for Suncorp’s functioning but may be difficult to decipher. AI technologies clarify language, minimize redundancy, and offer swift access to pertinent information through chatbot solutions, thereby boosting overall efficiency.

Conclusion

Suncorp Group’s deployment of AI in its risk management structure exemplifies a proactive strategy to improve operational effectiveness. By focusing on data acquisition and policy navigation, AI not only elevates reporting quality but also guarantees that essential information is available to all team members, regardless of their level of expertise.

Q: What is the main objective of Suncorp Group’s AI implementation?

A: The main objective is to enhance risk management practices by refining data acquisition and simplifying policy navigation.

Q: In what way does AI enhance the incident lodgement procedure?

A: AI guarantees comprehensive data capture, prompts for any incomplete information, and enables a smooth incident management experience.

Q: What function does AI serve in navigating risk policies?

A: AI simplifies the complicated language within risk documents, cuts down on redundancies, and employs chatbots to grant immediate access to specific details.

Q: How has Suncorp confirmed AI’s potential for enhancing processes?

A: Suncorp has utilized proof-of-concepts (POCs) to assess and demonstrate AI’s effectiveness in refining risk-related operations.

SEC launches 1.3MW rooftop solar panel system at MSAC to reduce operational energy costs by as much as $80,000


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

  • MSAC has launched a 1.3MW solar system on its rooftop to lower energy expenses.
  • This solar array is anticipated to produce more than one million kilowatt hours each year.
  • The facility is expected to save as much as A$80,000 annually on electricity bills.
  • SEC oversees the installation, ownership, and upkeep of the solar system.
  • Rooftop solar supplies 24% of MSAC’s electricity requirements, helping to reduce costs.
  • SEC’s efforts benefit over 4,400 government locations with renewable energy resources.

The Drive for Renewable Energy in Public Spaces

In a step that reflects the worldwide transition toward sustainable energy, the Melbourne Sports and Aquatic Centre (MSAC) has energized a 1.3 megawatt solar array atop its roof. This endeavor, initiated by the State Electricity Commission (SEC), aims to decrease operational electricity expenses and enhance the use of renewable energy in public establishments. As substantial venues generally encounter high energy demands, this initiative serves as a model for prospective sustainable advancements.

Rooftop solar array at MSAC to lower operational costs

Behind the Meter: A Model for Savings

The SEC’s creative strategy enables the State Sport Centres Trust to enjoy lower energy expenses without the burden of initial capital outlays. By managing the installation and upkeep, the SEC maintains ownership of the solar facilities. MSAC purchases the produced energy at a reduced pre-agreed price, avoiding conventional grid expenses and network fees.

Infrastructure and Energy Synergy

MSAC, a large sports complex located in Albert Park, houses numerous facilities including competitive pools and basketball courts, all of which have significant energy requirements. The output of the solar array aligns with peak daytime usage, promoting effective energy consumption and savings. This undertaking not only lowers electricity costs but also showcases the practicality of solar energy in large-scale implementations.

Widening the Scope of Renewable Energy

The SEC’s pledge to renewable energy encompasses over 4,400 government facilities, underscoring its commitment to diminishing dependence on conventional electricity systems. By embracing rooftop solar and other renewable programs, the SEC establishes a model for both public and private sectors to achieve more reliable and economical energy options.

Conclusion

The deployment of a 1.3MW rooftop solar array at MSAC represents a calculated initiative by the SEC and State Sport Centres Trust to cut energy costs and adopt renewable approaches. Providing 24% of the facility’s energy demand, this project illustrates how solar power can be utilized efficiently and sustainably to satisfy high-demand needs.

Q&A

Q: What is the annual electricity generation expected from the solar array?

A: The solar array is projected to produce more than one million kilowatt hours each year.

Q: What financial advantages does the solar system present for MSAC?

A: MSAC is expected to save up to A$80,000 each year on electricity expenses.

Q: Who is responsible for the solar array’s installation and maintenance?

A: The SEC handles the installation, ownership, and maintenance of the solar system.

Q: What share of MSAC’s energy demand will the solar array satisfy?

A: The solar array will provide about 24% of the overall electricity use for MSAC.

Q: What is the wider impact of the SEC’s renewable projects?

A: The SEC aids over 4,400 government facilities with renewable energy, advocating for sustainable energy solutions throughout Victoria.

ASD Cautions that AI Prompt Injection Threats Are Permanent


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Risks of AI Prompt Injection: Guidance from ASD

Summary Overview

  • ASD indicates that risks linked to AI prompt injection are inherent and can’t be entirely rectified within the model.
  • Appropriate measures should be executed at the software layer, referred to as the “harness,” that envelops AI models.
  • Vulnerabilities due to prompt injection are similar to past issues encountered with phone phreaking.
  • ASD recommends maintaining least privilege access and verifying outputs from AI.
  • This guidance is currently advisory in nature, aimed at bolstering security for enterprises.

Security Issues in AI: The Significance of the Harness

Risks of AI prompt injection and strategies for mitigation

The Australian Signals Directorate (ASD) has issued guidance that addresses the ongoing security threats linked to agentic artificial intelligence (AI). The primary concern is that these threats cannot be completely diminished within the models themselves. Instead, attention should be directed to the software layer, or “harness,” that surrounds and manages the models.

Grasping Prompt Injection Vulnerabilities

Prompt injection poses a major obstacle because language models interpret commands and information within the same contextual window. The ASD emphasizes that there is currently no dependable technical solution for this vulnerability, likening it to historical problems with phone phreaking.

The UK’s National Cyber Security Centre (NCSC) indicates that prompt injection may never be fully resolved like some other security vulnerabilities. Mitigation efforts must take place within the harness by regulating what agents can access and execute.

Recommended Practices: Reducing Risks in AI Systems

ASD’s recommendations urge businesses to implement least privilege access, require human consent for critical actions, and validate AI outputs prior to operational deployment. Additionally, it is vital to treat multi-agent systems as a singular entity to avert compromises through shared contexts.

Moreover, ASD advises purging outdated agent context instead of summarizing it to sidestep the introduction of errors. A persistent rules file should be utilized for initiating sessions.

Concluding Remarks

The advisory from the ASD regarding AI prompt injection vulnerabilities highlights the necessity of instituting controls at the harness level. Although these vulnerabilities cannot be completely eliminated, organizations can alleviate risks through strategic software governance and operational methods. This guidance represents a crucial advancement in the security of AI technologies within Australian enterprises.

Q: What does prompt injection mean in AI?

A: Prompt injection happens when AI models misinterpret inputs as commands, resulting in possible security vulnerabilities.

Q: Why is it impossible to rectify prompt injection within AI models?

A: The models handle commands and information concurrently, making it challenging to identify and resolve the issue internally.

Q: What function does the “harness” serve in AI security?

A: The harness is the software layer that encompasses AI models, where control measures and mitigations are applied to bolster security.

Q: How does ASD recommend addressing AI prompt injection risks?

A: ASD recommends enforcing least privilege access, obtaining human consent for substantial actions, and maintaining logs to manage and reduce risks.

Q: Is the ASD guidance obligatory for businesses?

A: At present, the guidance is advisory, designed to educate and assist businesses in enhancing their AI security protocols.

Australian Mobile Carriers to Introduce Automatic Reimbursement for Service Disruptions


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Automated Compensation for Service Interruptions

Australian mobile carriers to face 'automated' compensation for service interruptions

Brief Overview

  • Senate committee advises automated compensation for service interruptions.
  • Proposed standards for performance and dependability for telcos.
  • Stakeholder consultations are essential prior to rollout.
  • Political factions have differing opinions on the proposal.
  • Demands for clarity in network funding initiatives.

Recommendations from the Senate Committee

A recent assessment by a senate committee has proposed that Australian telecommunications operators should comply with obligatory performance and reliability standards, automatically compensating customers adversely impacted during outages. This suggestion arises in response to several network failures affecting emergency services, leading to a comprehensive investigation.

Political Responses and Recommendations

Although the committee regards this initiative as overdue, major political factions are split. Labor senators express cautious support, advocating for further investigation and discussions. Conversely, Coalition senators show skepticism, preferring voluntary compensation options rather than compulsory payouts. They also emphasize the importance of transparency in upcoming network investment strategies, particularly regarding rural regions.

Consequences for Telecommunications

The committee’s findings underscore the need for enhanced standards in the telecommunications industry. It recommends an automated compensation system and a penalty structure for service interruptions, urging the government to act resolutely. The report advocates for extensive stakeholder engagement to ensure that any compensation system is equitable and feasible.

Further Recommendations

  • Updating laws governing emergency services, potentially nationalizing the service for enhanced accountability.
  • Independent validation of unsuccessful emergency call welfare checks.
  • Examination of the Australian Communications and Media Authority’s regulatory authority.
  • Introducing text messaging options for emergency services alongside voice calls, with mobile roaming during significant outages.
  • Establishing a public registry of devices for network compatibility.

Conclusion

The senate committee’s proposals aim to improve network reliability and customer satisfaction within the Australian telecommunications sector. By instituting automated compensation for service interruptions and defining clear performance benchmarks, the initiative seeks to safeguard consumers and ensure accountability.

Q: What is the key recommendation from the senate committee?

A: The committee recommends instituting mandatory performance and reliability standards for telecommunications providers, with automated compensation for customers affected by service interruptions.

Q: How have the political parties responded to the proposal?

A: Labor senators advocate for further assessment and dialogue, while Coalition senators favor voluntary compensation models and highlight the necessity for transparency in network investments.

Q: What other measures does the committee propose?

A: They propose modernizing emergency service laws, reviewing regulatory authorities, enabling text messaging for emergencies, and keeping a public registry of devices for network compatibility.

Q: What is the rationale for transparency in network investments?

A: Transparency is essential for developing effective policies for regional connectivity and resilience, particularly in rural and remote locations.

Foreign Hackers Aimed at Colorado Water Systems in August


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Cybersecurity Challenges for Water Systems: An Escalating Issue

Cybersecurity Challenges for Water Systems: An Escalating Issue

Cyber incursion on Colorado water infrastructure in August

Quick Overview

  • International hackers targeted two water systems in Colorado during August.
  • There were no effects on public safety or water services.
  • Alleged involvement of a group supported by Iran.
  • Cyber assaults involved disabling remote access and changing pump cycles.
  • Part of a larger trend of attacks on U.S. water infrastructure.

Context of the Recent Incidents

In late August, two privately operated water utilities in Colorado, serving fewer than 200 residents each, were attacked by foreign hackers. Although these incursions did not threaten public safety or water services, they revealed weaknesses in critical infrastructure. The office of Governor Jared Polis indicated that these events are indicative of a broader pattern of cyberattacks on water infrastructure in the U.S., suspected to be associated with an Iranian-affiliated group.

Details of the Cyber Attack

The attackers were able to change equipment settings, which included disabling remote access and alarms, and altering pumping schedules. Thankfully, these events were short-lived, and the risks were quickly countered by the water suppliers, who alerted state officials. Despite the breach, the processes for treatment and water quality remained intact.

Wider Context of Cyber Attacks on Water Systems

This event follows a concerning trend of cyber assaults on water systems throughout the United States. A notice from the Cybersecurity and Infrastructure Security Agency (CISA) pointed out similar intrusions taking place in numerous states, affecting around 100 water entities. Previous attacks were consistent with methods employed by Iranian-related hackers, often utilizing programmable logic controllers to interfere with operations.

Conclusion

The cyber incidents in August involving Colorado water systems highlight the escalating threats to vital infrastructure posed by foreign hackers. While there was no immediate effect on public safety, these occurrences expose considerable vulnerabilities and the pressing need for strengthened security measures. The pattern of assaults points to a coordinated initiative by state-supported groups, demanding heightened vigilance and readiness across the industry.

Q&A Section

Q: What effects did the attacks have on Colorado’s water systems?

A:

The attacks did not affect public safety or water services, and the quality of water was not impaired.

Q: Who is believed to be responsible for these cyberattacks?

A:

The attacks are thought to be connected to an Iranian-backed group targeting U.S. water infrastructure.

Q: In what way did the attackers modify the water systems?

A:

The hackers changed equipment settings, which included disabling remote access, alarms, and modifying pumping cycles.

Q: What actions were taken to reduce the risk?

A:

The water providers swiftly mitigated the risks and notified state authorities to avert further harm.

Q: What implications does this have for the future of water system security?

A:

These occurrences emphasize the necessity for enhanced cybersecurity protocols and vigilance to safeguard critical infrastructure.

Anthropic Quietly Sets Up New Biology Laboratory


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Anthropic’s New Biology Laboratory: The Intersection of AI and Drug Science

Quick Overview

  • Anthropic launches a new biology lab in San Francisco to push drug science forward with AI.
  • The facility emphasizes rare diseases and merges physical experiments with AI innovation.
  • Anthropic seeks to hasten drug development and address ailments labeled as “undruggable.”
  • The lab does not directly engage in drug discovery but backs wider drug development initiatives.
  • The organization is in the preliminary phases of automating laboratory tasks with AI while ensuring human supervision.
  • Anthropic plans a notable IPO to support further advancements in AI.

Anthropic Ventures into Biological Sciences

Anthropic has quietly set up a new lab in the San Francisco Bay Area that focuses on physical biology research. This initiative represents a broadening of their artificial intelligence aspirations into drug science, concentrating on creating treatments for rare diseases. Unlike conventional drug discovery processes that often depend on computer modeling, Anthropic’s strategy integrates tangible laboratory experiments.

Anthropic's newly established biology lab in San Francisco

Balancing Aspirations with Concerns

Anthropic is harnessing the potential of AI to streamline lab processes, aiming to decrease human involvement whenever feasible. The company’s Claude AI is crafted to guide robotic systems in conducting experiments, although human supervision is essential to guarantee safety. This effort arises at a pivotal moment as the company manages both the opportunities and possible dangers of AI, with some experts raising alarm over its effects on society.

Acquisitions and Investments

Anthropic is intensifying its focus in the life sciences domain, regarded as a key area for AI utilization. The company has recently introduced Claude Science software and acquired Coefficient Bio to enhance its drug development capabilities. With intentions to expand operations, Anthropic is actively seeking professionals in biochemical fields to strengthen its internal expertise.

Tackling ‘Undruggable’ Ailments

Anthropic’s AI solutions aim to expedite the development of therapies for diseases previously labeled “undruggable.” Their initiatives involve uncovering intricate molecules like bispecific and trispecific antibodies, capable of targeting various sites on a protein or cell. While the exact conditions being targeted are not publicly disclosed, Anthropic’s endeavors represent a significant move towards transforming drug development.

Conclusion

Anthropic’s new biology lab signifies an important advancement in merging AI with drug science, with an emphasis on rare diseases and speeding up drug development workflows. Although the company’s initiatives aim to push medical science forward, they also underscore the importance of responsibly addressing AI’s potential hazards. As Anthropic gears up for a major IPO, its endeavors in life sciences continue to progress, aspiring to provide ground-breaking solutions for unmet medical requirements.

Common Questions

Q: What is the primary aim of Anthropic’s new biology lab?

A: The lab is intended to carry out physical biology experiments, enhancing AI applications in drug science, especially for rare and overlooked diseases.

Q: In what manner does Anthropic plan to implement AI in their new lab?

A: Anthropic plans to utilize AI to automate lab experiments while ensuring human supervision to maintain safety and reliability.

Q: Is Anthropic engaged in direct drug discovery?

A: No, the lab is not solely focused on drug discovery but aids Anthropic’s wider drug development strategies.

Q: What challenges does Anthropic encounter with its AI initiatives?

A: While AI has the ability to accelerate drug development, there are concerns regarding safety, ethical implications, and the necessity to reconcile technological advancements with potential dangers.

Q: How is Anthropic addressing worries regarding AI’s influence on the pharmaceutical sector?

A: Anthropic concentrates on addressing unmet medical needs and ensuring its AI solutions do not compete directly with established pharmaceutical and biotech organizations.

MG U9 EV Launched: Dual-Motor Electric Ute Debuts in Australia Priced from A$78,990, Featuring 3.5-Tonne Towing Capability


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

Quick Overview

  • The MG U9 EV, a dual-motor electric pickup, debuts in Australia priced from A$78,990.
  • Offers a robust towing capability of 3.5 tonnes, perfect for demanding tasks.
  • Equipped with a durable 102.2kWh LFP battery that delivers a range of up to 430km.
  • Incorporates cutting-edge features such as air suspension and Vehicle-to-Load functionality.
  • Includes contemporary comforts and safety technologies.

MG U9 EV: A Revolutionary Addition to Australia’s Dual-Cab Ute Market

Dual-cab utes have been a long-standing favorite among Australians due to their adaptability and toughness,
suited for both professional and recreational use. However, options for electrification in this area have been notably
limited. Introducing the MG U9 EV, revealed at the Everything Electric expo in Sydney,
signifying a major move towards electrifying this popular vehicle category.

Impressive Dual-Motor Power and Reliable Towing Capacity

Powered by a dual-motor all-wheel-drive system, the MG U9 EV generates an impressive
325kW of power and 700Nm of torque. This configuration allows the pickup to sprint
from 0 to 100km/h in just 5.8 seconds, competing closely with performance-oriented petrol variants. More
importantly, it retains a towing ability of 3,500kg, adhering to the segment’s benchmark.

Battery Power, Highway Performance, and Charging Speeds

Fitted with a 102.2kWh LFP battery, the U9 EV provides a WLTP range of 430km. Actual
conditions might decrease this range, particularly with towing. The pickup supports 115kW DC
fast-charging, reaching 20-80% battery in around 42 minutes, minimizing downtime
during extended journeys.

Secure Storage and On-the-Go Power

The U9 EV features a 236-litre front compartment, perfect for the safe storage of tools or
groceries. Its Vehicle-to-Load (V2L) capability allows the pickup to power devices and
appliances, transforming it into a mobile worksite powerhouse.

Electronic Air Suspension and Interior Comforts

The U9 EV is equipped with electronic air suspension, improving ride comfort while adapting to
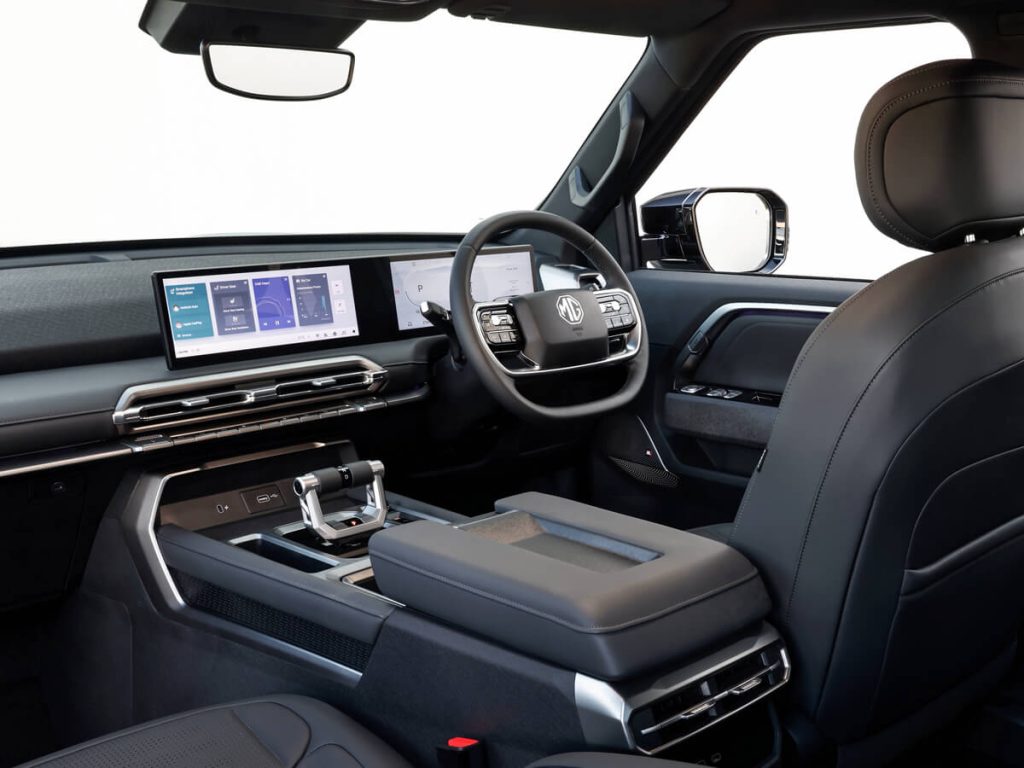
various terrains. Inside, it boasts a collection of modern amenities, ranging from digital screens and
wireless connectivity to advanced safety technologies, ensuring a high-quality driving experience.

The Initial Impression

With a starting price of A$78,990, the MG U9 EV might appear pricey but offers an impressive value when benchmarked against its diesel rivals. For individuals in need of a
powerful, practical, and environmentally friendly ute, the U9 EV stands out as a significant player in
Australia’s automotive landscape.

Overview

The MG U9 EV signals a transformative era for dual-cab utes in Australia, merging electric
efficiency with traditional ute functionalities. With its robust performance, considerable
towing capacity, and state-of-the-art features, it aims to reshape what drivers can expect from
an electric ute.

Q: What is the initial price of the MG U9 EV in Australia?

A: The MG U9 EV has a starting price of A$78,990, excluding on-road expenses.

Q: What is the towing capability of the MG U9 EV?

A: It boasts a braked towing capacity of 3,500kg, aligning with segment expectations.

Q: How swiftly can the MG U9 EV charge using a DC fast charger?

A: The U9 EV can achieve a 20-80% charge in roughly 42 minutes with a 115kW DC fast charger.

Q: What is the electric driving range of the MG U9 EV?

A: The vehicle is capable of a WLTP range of up to 430km, although real-world driving scenarios may differ.

Q: What special storage feature does the MG U9 EV provide?

A: The U9 EV is equipped with a 236-litre front storage compartment, offering secure and weather-resistant storage.

Q: Are advanced safety features included in the MG U9 EV?

A: Yes, it comes with features such as adaptive cruise control, autonomous emergency braking, lane-keeping assistance, and more.

Helix 2.5 AI Model Introduced as Humanoid Robots Manage Household Tasks in 30 Unseen Residences


We independently review everything we recommend. When you buy through our links, we may earn a commission which is paid directly to our Australia-based writers, editors, and support staff. Thank you for your support!

  • Figure reveals the Helix 2.5 AI model with notable advancements in household generalization.
  • Helix 2.5 was evaluated in 30 unfamiliar residences, achieving a 56% success rate.
  • Physical Intelligence’s pi 0.5 model employs multimodal data for generalizing household tasks.
  • Robotic foundation models demonstrate promising advancements, yet practical implementation is still years away.

How Helix 2.5 addresses unfamiliar homes

Figure describes Helix 2.5 as its most advanced neural network to date. Rather than obtaining demonstrations within the specific homes where the robot would operate, Figure pre-trained the base model on Index, its global dataset of human behavior videos.

From that foundational model, Figure adapted three full-body actions: tidying a living room, folding towels, and making beds. The team then deployed its humanoid across 30 residential locations throughout the San Francisco Bay Area.

  • No training data was collected from any of the 30 test residences.
  • None of the evaluation items, towels, or bedding were present in the training data.
  • The robot utilized the existing beds, couches, and tables that each home had.
  • Grading was strictly binary, requiring complete end-to-end execution with no partial credit.

The contrast in performance between policies with and without foundational pre-training was pronounced. When Figure tested a control policy trained from scratch without Index pre-training, it achieved a zero-shot success rate of merely 9 percent across the homes. However, when employing the Index pre-trained Helix 2.5 model, that success rate rose to 56 percent.

Figure also showcased an empirical human-to-robot transfer scaling law. By training four models with an eightfold increase in pre-training data while keeping downstream tuning constant, the action prediction error consistently decreased with every doubling of data. Figure asserts that the trend was consistent enough to predict the validation loss of its largest model run to four decimal points before training.

The Airbnb tactic and the divide to active family life

Viewing the footage released by Figure founder Brett Adcock reveals insightful details about the execution of these tests. Figure conducted evaluations across 30 properties, which appear to be holiday rentals and Airbnbs rather than occupied family homes.

Utilizing short-term rentals is an ingenious engineering shortcut. It provides the team with immediate access to diverse floor plans, varying mattress heights, and multiple surface textures without upending employee households.

This approach also underscores the disparity between an empty rental and true domestic life. The homes displayed in the demonstration videos are tidy, well-lit, and unoccupied. In several clips, company engineers can be seen closely observing the robot as it maneuvers around furniture.

Navigating static furniture in an empty rental without prior mapping is a significant accomplishment in autonomous spatial reasoning. However, an active Australian family household presents a considerably more chaotic setting.

In reality, dogs may dart through the kitchen, children can leave school bags scattered in entryways, and family members walk about. While static spatial generalization is a crucial first step, safely coexisting with people in dynamic environments remains a challenge yet to be addressed.

Physical Intelligence adopts a multimodal approach with pi 0.5

While Figure prioritizes human video pre-training for humanoid platforms, Physical Intelligence approaches generalization from a complementary perspective with pi 0.5.

Physical Intelligence constructs vision-language-action foundation models. The central concept behind pi 0.5 is heterogeneous co-training. Instead of training solely on actuator telemetry from a single robot platform, the model incorporates a mix of multimodal web data such as image captioning and visual question answering, along with action data from static dual-arm setups and mobile manipulators.

This dual-path strategy fosters semantic understanding alongside low-level actuator control. When given an instruction like “clean the bedroom,” pi 0.5 generates a high-level subtask in text, effectively communicating with itself to break the task into manageable steps. It subsequently funnels that step into a continuous flow of 300 million parameters, directing physical joints in one-second action segments.

Physical Intelligence evaluated pi 0.5 across unseen homes on domestic tasks, including placing dirty dishes in sinks, loading clothes into hampers, and wiping countertop surfaces with sponges.

Their ablation tests indicated that web-scale multimodal data was the primary contributor to the robot’s ability to recognize unfamiliar household items. Incorporating data from other robotic designs offered physical baseline stability. After training in around 100 diverse environments, pi 0.5 achieved generalization performance in new homes that closely matched baseline models trained directly within the target test rooms.

Maintaining perspective on progress

These announcements affirm that robotic foundation models are advancing swiftly, but it’s vital to keep timelines realistic. We are likely still years away from entering stores like JB Hi-Fi or Harvey Norman to purchase a domestic humanoid for A$15,000 to handle our Saturday cleaning, yet this suggests it isn’t a decade off.

A 56% zero-shot success rate in unfamiliar homes indicates a significant increase from 9 percent, yet it also signifies the robot fails more than four times out of ten. If a household appliance showed that failure rate, it would remain unused in storage. Humanoid hardware continues to be expensive, power-intensive, and mechanically intricate.

The significance of these technological updates lies in validating the software roadmap. For years, the industry contemplated whether physical manipulation could benefit from the foundational model scaling laws that propelled large language models.

The data from Figure and Physical Intelligence substantiate that physical intelligence scales with data. Training foundation models on a wide array of human activities and multimodal data equips machines with a fundamental intuitive comprehension of the physical world prior to entering a room.

We are still in the early stages of this journey, but the era of hand-coding every single room is finally nearing its end.

Summary

Figure’s Helix 2.5 and Physical Intelligence’s pi 0.5 models signify substantial advancements in AI robots managing household chores. While promising strides have been made, obstacles persist regarding practical implementation and attaining higher success rates in real-world scenarios.

Q: What is Helix 2.5?

A: Helix 2.5 is the newest AI model from Figure aimed at enabling humanoid robots to carry out household tasks without prior mapping.

Q: How was Helix 2.5 assessed?

A: It was tested in 30 unfamiliar residences, achieving a 56% success rate in tasks such as tidying, folding, and making beds.

Q: What is the pi 0.5 model?

A: The pi 0.5 model from Physical Intelligence employs multimodal data to understand and execute household tasks, presenting a different methodology for task generalization.

Q: What challenges do AI robots face in homes?

A: Challenges consist of achieving higher success rates, adapting to dynamic environments, and lowering costs and complexity.